1/ Today we’re launching the HOL Partner Program.
Cohort One brings together 30+ signed partners, including XMTP, GoDaddy, and DSR, to help shape open infrastructure for AI agents.
Registries. Payments. Privacy. Security. Communication. Standards.
The agent stack is forming now.
An email can carry instructions your AI assistant can read, even when you can't see them.
Now give that assistant access to your accounts.
This is what prompt injection looks like in practice.
Your AI Agent Writes Code. Who's Auditing Its Commits?
The Conventional Commits Framework sets a commit contract for AI-written changes, including atomic commits and explicit breaking-change notes.
https://t.co/oYZxOPRvEd
HOL x AI is the best show on X to catch up on everything AI.
This week, NVIDIA's AI Robot Ducks, Anthropic Historic IPO, and so much more...
JOIN US LIVE. https://t.co/7T73l6EgFN
Running Langflow where others can reach it? Every release through 1.12.8 lets a stranger skip the login or run code on the server. One of the bugs, CVE-2026-93680, already has a Metasploit module.
Upgrade to 1.13.0. Set a superuser password first.
https://t.co/rKPGNJMAjg
A declaration buys fewer stages, never fewer boundaries.
When opted in, the ai-native-sdlc plugin’s PreToolUse hook checks source-code write paths against the active plan’s file list.
Read the implementation and its boundaries: https://t.co/s9Na6KfdMy
Your agent should never be handed a shell.
SysKnife accepts typed actions. The daemon needs a one-time approval from a separate terminal.
The article covers this boundary and the audit-chain limits.
https://t.co/oEHr1IWjGZ
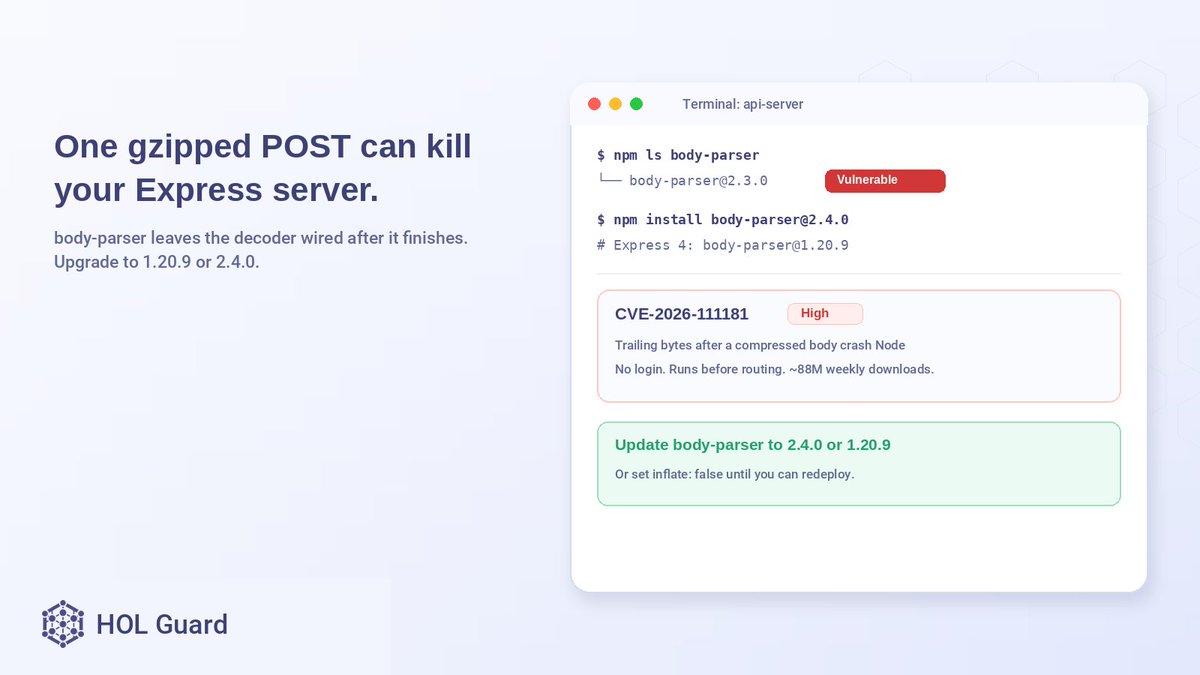
One gzipped POST crashes every Express app still on body-parser below 1.20.9 or 2.4.0. CVE-2026-111181 needs no login and runs before routing.
Upgrade body-parser. Or set inflate: false until you redeploy.
https://t.co/CYTJjwL3x9
Kept API keys or wallet keys in Railway? An intruder got into Railway's store of customer environment variables, and wallets with keys there were drained of about $371K before the notice.
Rotate every Railway variable. Move funds off old wallet keys.
https://t.co/aBcg0cWuQO
A stranger's server corrupts memory inside your Node.js app with one malformed compressed reply to fetch(). CVE-2026-111497 hits every supported Node.js line. Express 5 uploads reach the same Brotli bug.
Update to 22.23.4, 24.22.1 or 26.12.1.
https://t.co/en808wmV0d
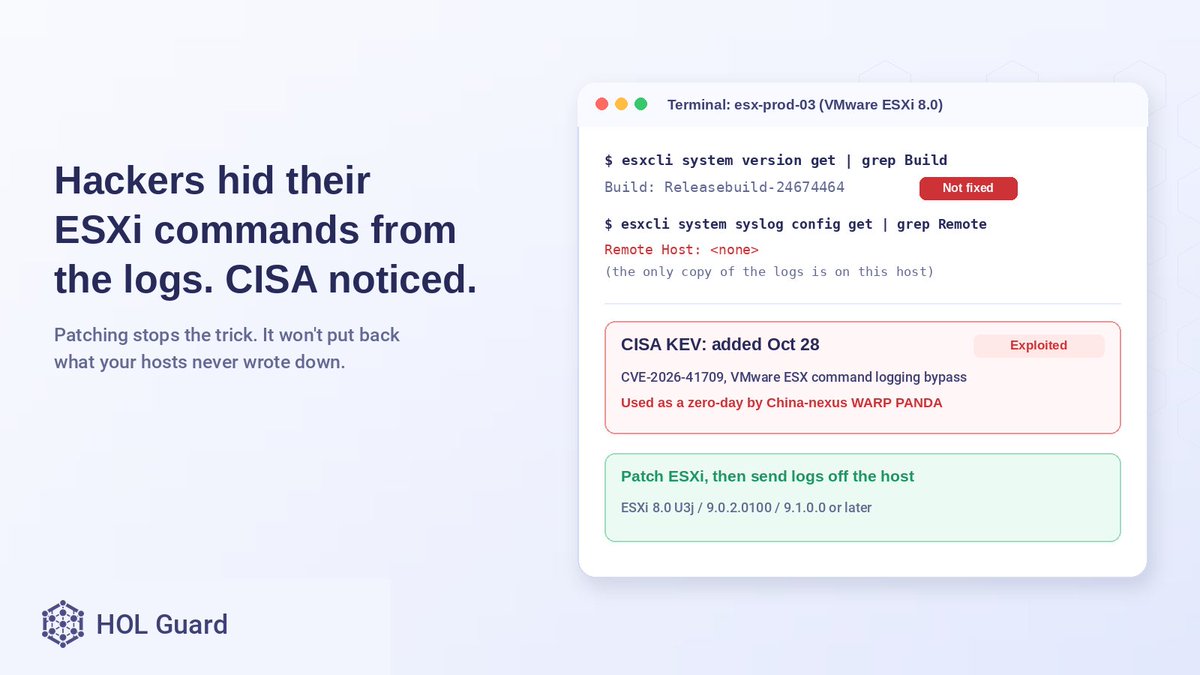
China-linked hackers ran commands on VMware ESXi hosts that never reached the logs, using a zero-day. CISA added the bug, CVE-2026-41709 in VMware ESX, to its exploited list today.
Patch to 8.0 U3j or later and forward ESXi logs off the host.
https://t.co/OsaSoqlkAz
Run Tailscale SSH? One hacked laptop on your tailnet can forward a socket and get root on every server its SSH rules reach. Tailworm (TS-2026-014) is fixed in Tailscale 1.104.4.
Upgrade every SSH node, or set TS_SSH_DISABLE_FORWARDING=1 until you can.
https://t.co/VxhvibOnyf
Got Linux appliances online? Attackers turned web shells into root on 25 of them and reached a US government network. The bug: CVE-2026-46300 in the Linux kernel (Fragnesia), now on CISA's exploited list.
Check /etc/pam.d/su before rebooting, then patch.
https://t.co/qckf8H85gW
Anyone who requests the right URL while a WordPress site is updating can reach the unpacked copy's installer and plant their own config. WordPress 7.1.4 closes that window. Auto-updates open it too.
Update, then block web access to wp-content/upgrade/.
https://t.co/GTAvTqqDRm
Browser Harness has 18,425 GitHub stars and a Caution label on HOL. All four findings behind that label are packaging gaps: no website, privacy or terms link in the manifest, and no lockfile.
10 Claude Code plugins by adoption, each label explained:
https://t.co/V8FuelznEm
Strangers are dropping webshells into Magento stores via the guest cart, no account needed. CISA added PolyShell (CVE-2026-48356) in Adobe Commerce and Magento Open Source to its exploited list.
Patch with APSB26-73, then hunt for files you didn't add.
https://t.co/TWHl0jQadt
Paying for LiteLLM Enterprise? A request with no API key can make your proxy send its master key and every model provider key to an attacker's server.
Upgrade to 1.106.5 (or 1.105.6/1.104.8/1.103.10) and rotate that key. Open source installs are safe.
https://t.co/1IHzi0xm5x