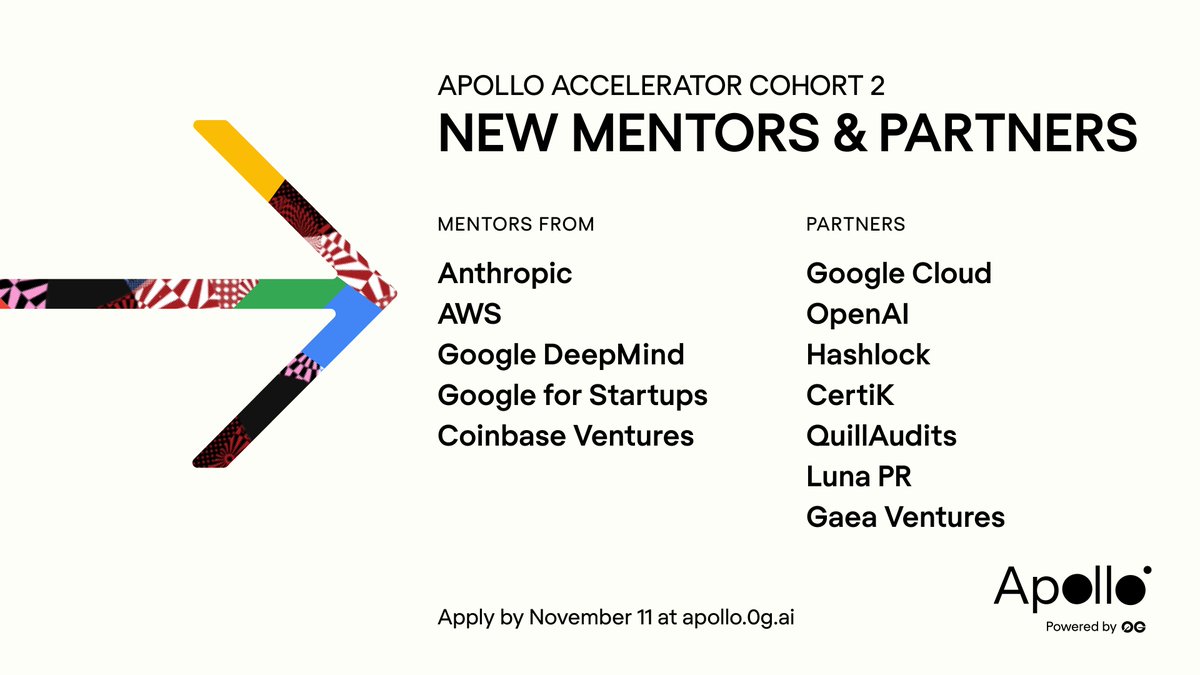
Proud to be a trusted security partner of the Apollo AI Accelerator by @0G_labs, run with @xBuildersVC
We are here to help the Cohort 2 teams build and ship securely
Applications close 11 Nov: https://t.co/UwJqa5pKcm
“Security is a loop: re-review on change, monitoring after launch, a bounty, and a drill now and then.”
The audit is one step in the loop, not the finish line. The checklist we built with @InspiraLabsHQ covers the rest, from the first commit to Day Zero.
Teams hear the same four pieces of security advice: get an audit, set up a multisig, plan the launch, prepare for the worst
Each of those controls works inside its own boundary. Losses happen between them: a commit that changed after the report, a key that stayed on a personal wallet, a launch plan with a date and no code freeze, an incident with nobody authorized to pause the contracts 🌱
We mapped five of these gaps with Hashlock:
- before the audit
- the audit and its edges
- launch
- the AI layer
- Day Zero, the first 24 hours of an incident
A project is ready when its controls connect. The audited commit is the deployed commit, the keys sit where the plan says they sit and someone is authorized to act in the first hour of an incident 🍃
Full piece 🔗
By @InspiraLabsHQ x @Hashlock_
Co-written with @InspiraLabsHQ: a security playbook for founders preparing to launch or raise, and the investors who assess them
An audit covers one commit on one date. Losses happen in the gaps around it: deployment, keys, launch, incident response
“A bug on either side is a consensus bug.”
That is how the @X1_EcoChain CTO explains why they audited both halves of their Layer 1: the Go node and the Solidity contracts.
The case study, including the High a fix created and our fix review caught:
https://t.co/1nratfmu8w
Good read from @xccy_finance and Schema Research on what fixed rates on lending do for treasuries, vaults and borrowers
What caught our eye: pricing the hedge into a vault’s share price. That is where vault security gets tested!
Borrow $500K on Aave for six months, and the interest bill could be $7,500 or $25,000, depending on where rates go
Fix the rate at 6% and the bill is $15,250, fees included
We worked through cases like this in a new piece 👇 https://t.co/Cux5grarxp
Applications for Apollo Cohort 2 by @0G_labs close today
We are a security partner of the program: Cohort 2 teams get 30% off Hashlock security audits.
AI founders building real products, this is your last call
Apollo Cohort 2 mentors now include leaders from Anthropic, AWS, Google DeepMind, Google for Startups and Coinbase Ventures.
Partners include Google Cloud and OpenAI.
Up to 10 AI startups, up to $2M each, run with @xBuildersVC.
Applications close Nov 11.
Building on @X1_EcoChain?
As security partner for the X1 EcoChain ecosystem, we review what teams launch on it: token contracts, DeFi and staking, bridges, dApps and games.
Get your code reviewed before you ship:
https://t.co/jhw2bSRNhM
Proud to keep building with @X1_EcoChain after auditing their Layer 1.
We know the base layer inside out: the Go node and the system contracts. That gives every team launching on X1 EcoChain a head start on security
X1 EcoChain 🤝 Hashlock: Elevating Ecosystem Security and Unlocking Exclusive Perks for Builders!
We are thrilled to highlight our successful partnership with @Hashlock_ — a premier Australian smart contract and decentralized systems auditor with an impeccable global reputation for blockchain security.
Having already completed the comprehensive audit of our Layer 1 blockchain, Hashlock's security experts possess an intimate, hands-on understanding of our underlying architecture and codebase. This gives projects building within the X1 EcoChain ecosystem a massive advantage.
Thanks to this established technical baseline, upcoming ecosystem projects can undergo security audits with Hashlock much faster, more smoothly, and on exclusive, highly favorable terms.
Empowering the next generation of secure, scalable Web3 projects — together with the industry's best!
Introducing Space and Time Enterprise: a new data privacy platform for AI and finance.
Deploy Proof of SQL in your enterprise environment, keep your underlying business data private, and share verifiable results with your AI agents, auditors, and stakeholders.
Audit complete: @X1_EcoChain
Hashlock reviewed both halves of the chain: the Go node client that runs the network and the Solidity contracts that run on it
Full report: https://t.co/ACuy9DlUdN
Today in Rome, Hashlock team joins the SiGMA World panel "Trust but Verify: Audits, Transaction Monitoring and the Practical Work of Keeping Crypto Safe"
AIBC World 2026 opens today at Fiera Roma, and Hashlock is exhibiting.
Hashlock team is at the Hashlock booth until 5 Nov
Come and ask us what we would fix first in your code
@AIBC_World
Hashlock now has a project page on @SolanaCompass, the Solana ecosystem directory.
Worked with us? A short review there helps other builders find a security partner they can trust.
https://t.co/FYclKjrGmX
The lesson for every team, not only exchanges: perfect code is not enough if one laptop can reach the system that moves your money.
Security covers people, devices and access too
Binance lost about $6.3B on 29 Oct, by its own estimate. Early reports said $5.6B before the full count. TRM Labs calls it the largest crypto theft on record.
Binance's first findings point to one hacked staff laptop. In plain words:
4. Most of the money left in about 20 minutes, across 10 blockchains (TRM Labs).
About $3B is already frozen, and Binance says it will cover all losses. TRM links the attack to North Korea's TraderTraitor group.
1. An attacker got into the laptop of a Binance engineer.
2. From it, they reached the internal system that sends withdrawals.
3. That system signed the attacker's withdrawals as if they were real.
Binance says it found no sign of a private key leak.
Proud to see our Founder & CEO @jockhaslam among the 19 new supporters backing @ethlabs_org, the non-profit R&D lab for Ethereum and ETH.
Security is on their short list of what makes Ethereum special. It is on ours too