

Top Tweets for #qakBot

(Unverified) Qakbot Found
C2: 24[.]158[.]33[.]41:443
Country: United States (AS20115)
ASN: CHARTER-20115
#c2 #Qakbot #unverified
(Unverified) Qakbot Found
C2: 74[.]118[.]80[.]74:443
Country: Afghanistan (AS45178)
ASN: ROSHAN-AF Main Stree...
#c2 #Qakbot #unverified
(Unverified) Qakbot Found
C2: 5[.]163[.]120[.]247:995
Country: Saudi Arabia (AS25019)
ASN: SAUDINETSTC-AS
#c2 #Qakbot #unverified
(Unverified) Qakbot Found
C2: 51[.]211[.]212[.]16:995
Country: Saudi Arabia (AS25019)
ASN: SAUDINETSTC-AS
#c2 #Qakbot #unverified
(Unverified) Qakbot Found
C2: 62[.]1[.]22[.]212:995
Country: Greece (AS1241)
ASN: FORTHNET-GR Forthnet
#c2 #Qakbot #unverified


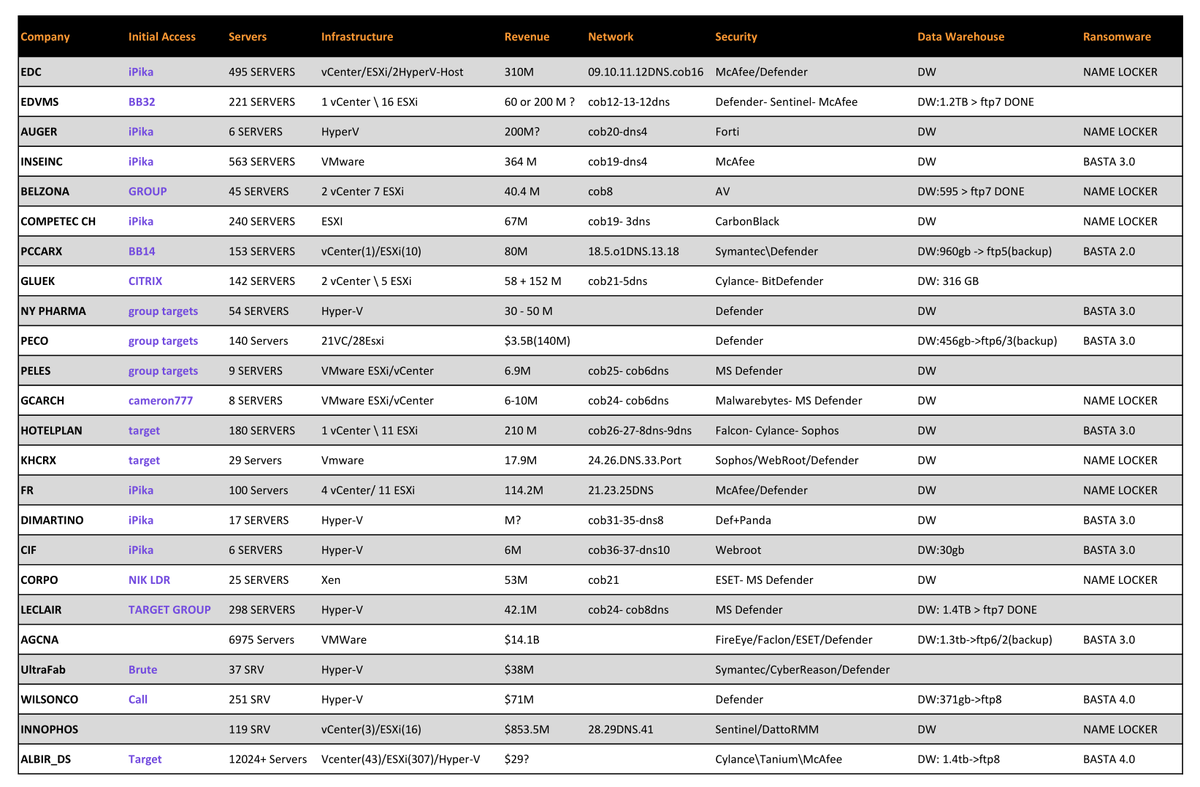
📌 While analyzing the #BlackBasta ransomware leak, I identified a pattern that allowed me to compile a list of organizations that were attacked or compromised between 2023 and 2024.
They documented details such as the initial access vector, which included:
- #Qakbot
- #PikaBot
- NIK LDR (?)
- CITRIX (vulnerabilities)
- Call (social engineering / vishing)
- Brute Force (probably the #BRUTED framework)
- "Cameron777" (IAB) and others.
* #CobaltStrike was also a component that was used in almost all attacks. Let's not forget #IcedID, #DarkGate and #Latrodectus among others.
A worrying and interesting fact is that many of these organizations never made the incident public, which could suggest that they paid the ransom to avoid other repercussions (?) 🤔
All my respect to the community that has always been reporting and warning about each of these malicious campaigns, including the current ones.
[+] https://t.co/PfW9i3cfCf
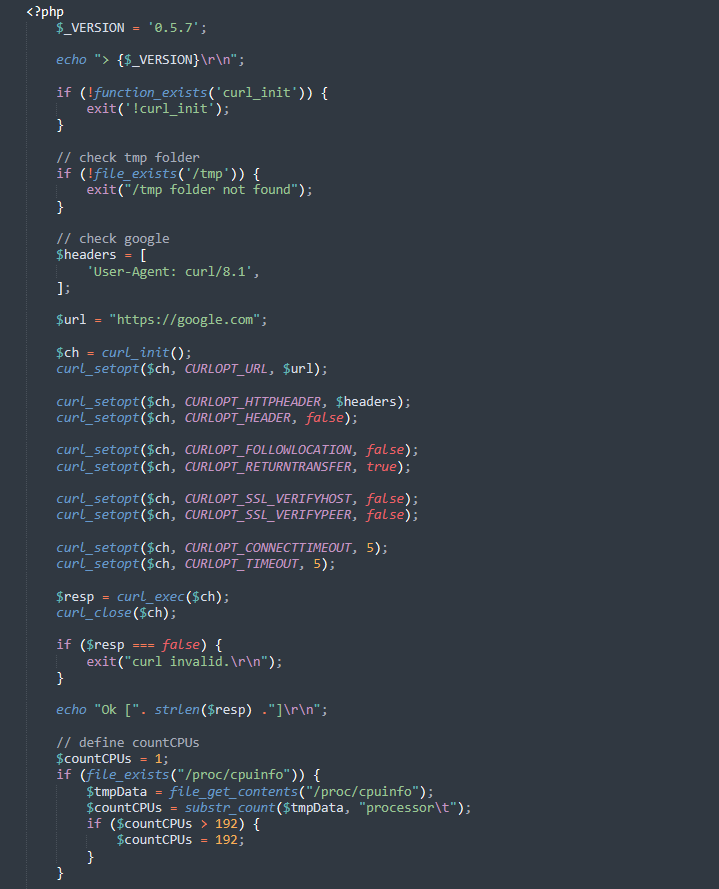
📌 In March 2024 I found a very interesting opendir on IP 2.57.149.237 (mentioned in the EclecticIQ report). An opsec error allowed me to see part of the PHP source code and that's when I realized two things:
1.- It was a tool or framework to perform brute force attacks on VPN devices.
2.- The code had fragments very similar to the PHP proxy scripts used by #TA577 (aka Tramp aka GG) for the distribution of Emotet, Qakbot, Pikabot, etc.
Now, thanks to @EclecticIQ's research, everything fits and I can confirm that what I saw a year ago, was a preliminary or in-development version of #BRUTED. Good work @WhichbufferArda and team! 🦾
/ @Cryptolaemus1


(Unverified) Qakbot Found
C2: 2[.]50[.]54[.]1:443
Country: United Arab Emirates (AS5384)
ASN: EMIRATES-INTERNET Emirates Internet
#c2 #Qakbot #unverified
(Unverified) Qakbot Found
C2: 86[.]98[.]219[.]194:443
Country: United Arab Emirates (AS5384)
ASN: EMIRATES-INTERNET Emirates Internet
#c2 #Qakbot #unverified
(Unverified) Qakbot Found
C2: 2[.]49[.]173[.]1:443
Country: United Arab Emirates (AS5384)
ASN: EMIRATES-INTERNET Emirates Internet
#c2 #Qakbot #unverified

The US just seized $24M in crypto from a Qakbot hacker 👀
Cyber heists ain't what they used to be — feds are getting good at this game 🔒💰
#Crypto #CyberCrime #Qakbot
(Unverified) Qakbot Found
C2: 2[.]50[.]53[.]41:443
Country: United Arab Emirates (AS5384)
ASN: EMIRATES-INTERNET Emirates Internet
#c2 #Qakbot #unverified

U.S. authorities have indicted Rustam Gallyamov for leading the Qakbot botnet, which infected over 700,000 devices and facilitated ransomware attacks, alongside a civil forfeiture complaint for $24M in seized cryptocurrency. #Cybercrime #Qakbot https://t.co/4Fun9ajMdx

🚨 JUST IN: The DOJ is going after $24M in crypto from Russian malware dev Rustam Gallyamov, the alleged mastermind behind the Qakbot botnet. Despite the botnet's takedown, he kept pushing malware. 💰💻 #CryptoCrime #Qakbot $BTC $USDT


After over a decade of chasing him, the U.S. has indicted the mastermind behind the Qakbot botnet—linked to ransomware giants and hundreds of global victims.
#Cybercrime #Qakbot #Ransomware #Cybersecurity #FBI
https://t.co/6X42mxmCrq
Last Seen Hashtags on Sotwe
bokep #ometv
Seen from Switzerland
unstoppablesierra
Seen from United States
brosis
Seen from United States
CircoenPrimavera
Seen from United States
toystory
Seen from Mexico
R18G
ديوت_بدوي
부커만남
Seen from Korea
findesemanadelaleche
Seen from United States
teenageee filter:videos
Seen from United States
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers