

Top Tweets for #workloadid

Learn how to implement #ConditionalAccess for #WorkloadID and automate Incident Response:
🔗 https://t.co/phoT3Y6aop
Apply restriction of credentials by App Management Policies in #MicrosoftEntra and #Azure Policies for MSIs:
🔗 https://t.co/NyEyJCVBKO
🔗 https://t.co/hDeHkA25lW

I've published a #KQL function ("WorkloadIdentityInfoXDR") for #MicrosoftDefender to enhance details of #MicrosoftEntra #WorkloadID from various sources, incl. the new table "OAuthAppInfo" but also IdentityInfo table and #ExposureManagement. (1/2)
🔗 https://t.co/1L9ZnwCVBB

[New blog post] Identify and prevent abuse of 🤖 #ManagedIdentities by #FederatedCredentials from ⚡ unauthorized entities. This will include how to detect and avoid #WorkloadID compromise in #Azure by using #AzADSPI, #MicrosoftSentinel and #AzurePolicy.
https://t.co/SDi4N95l37
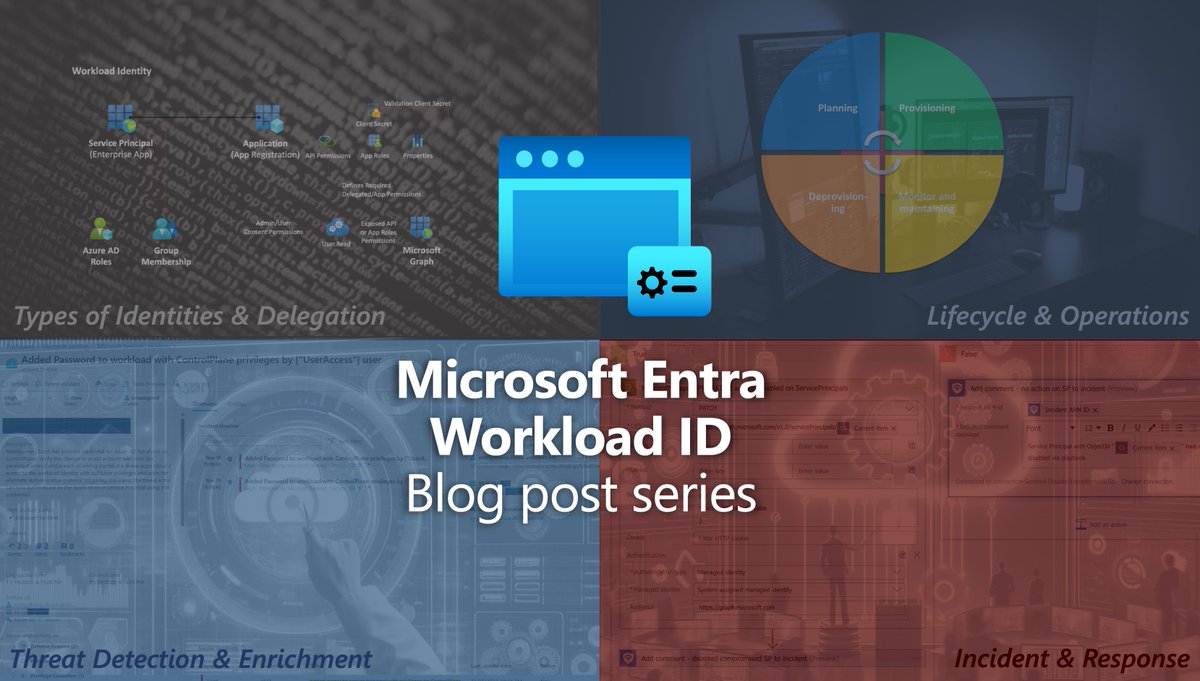
In the previous month, I’ve written a blog post series about #MicrosoftEntra #WorkloadId: https://t.co/WOYkUKGsNz
In this thread, I like to give you a summary about a few key aspects about managing non-human identities in #EntraID which has been also described in the articles.
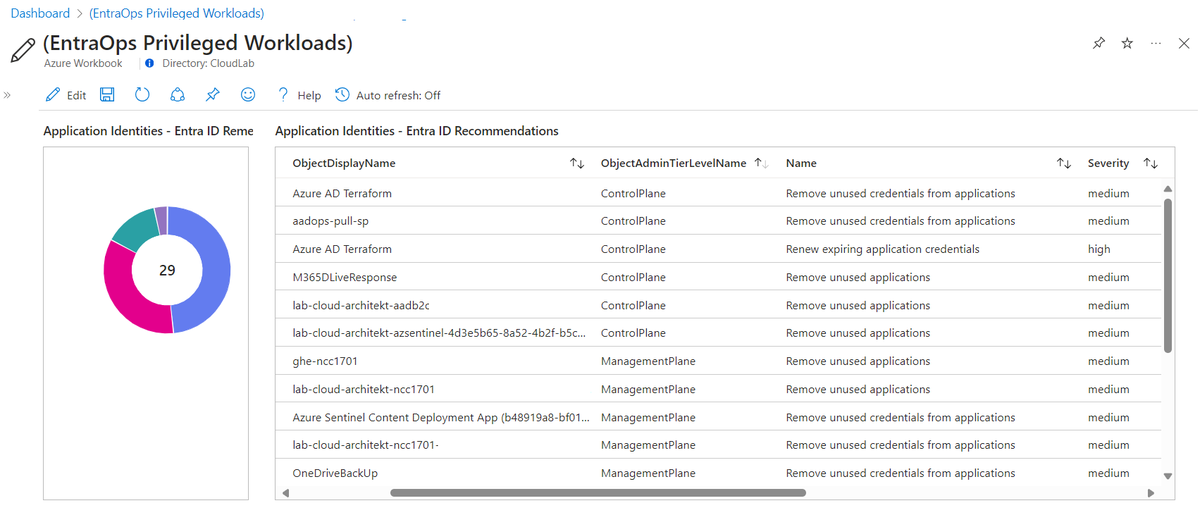
Ingestion of results from #EntraID Recommendations to Microsoft Sentinel is a great use case. It can be used for entity enrichment or workbooks. For example, I've integrated them to my #EntraOps #WorkloadID Workbook to show privilege classification of stale apps and credentials.
[New blog post] #MicrosoftEntra #WorkloadID - Incident Response with #MicrosoftSentinel Playbooks and #ConditionalAccess 🤖 🛡
In this part of the blog post series, I will cover the implementation of incident response to the enriched threat detections.
https://t.co/z1r22VmvcY
[New blog post] #MicrosoftEntra #WorkloadID - Advanced Detections and Enrichment in #MicrosoftSentinel: Implementing #AzADSPI and #WatchList solution to enrich incidents (e.g., with privileged classification based on Tiering Model) and enhanced detections.
https://t.co/Z280O0GWmS
[New blog post] #MicrosoftEntra #WorkloadID - Threat Detection with #MicrosoftDefenderXDR and #MicrosoftSentinel: Overview of integrated threat intelligence, detection and UEBA capabilities across the various products to monitor non-human identities. https://t.co/vnBkkqc5UY

Working on the last finishing touches for the second part of my blog post series about #Entra #WorkloadId which will be published early next week. Stay tuned!


Last Seen Hashtags on Sotwe
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
118.9M followers

Cristiano Ronaldo
@cristiano
114.6M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90.1M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers