Impersonation scams effectively convince employees to give away credentials. Marathon Health was hit and is now notifying 5.7 million people that their data was stolen. https://t.co/7LBVJziu1u
A February 2026 Notice of Privacy Practices Update deadline quietly required most covered entities to update their NPP. Most missed it. https://t.co/o6YkQf68AQ
So many healthcare data breaches are preventable with the right training. The latest ShinyHunters attack on McKesson stemmed from voice phishing (vishing), not a sophisticated back-end software manipulation. https://t.co/21cKbotzuE
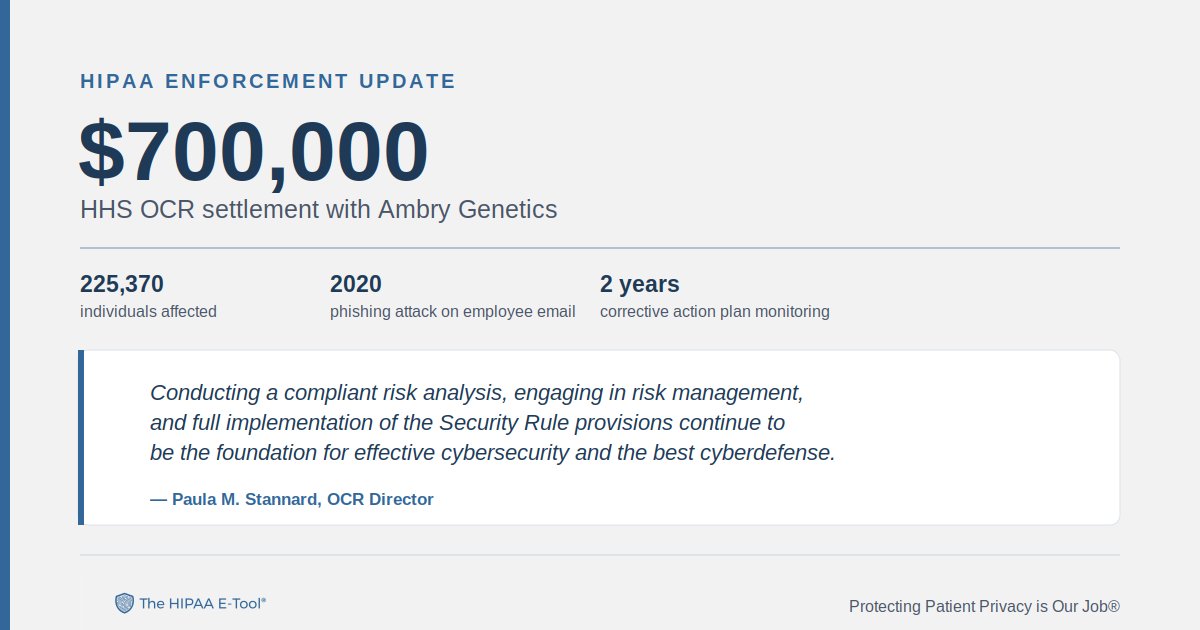
Genetic testing co. Ambry Genetics just settled with HHS OCR for $700K after a 2020 phishing attack exposed PHI of 225K+ people. No risk analysis, no access termination procedures, no unique user IDs. The basics still matter most.
Yes, AI risks sound dire this week, but let's stay focused on what's in front of us and reduce the healthcare risks we can see and control. https://t.co/yxf4n2gkcB
Risk Analysis is the Main Security Rule Requirement, the "foundational step" per OCR Director Paula Stannard at the OCR NIST Cybersecurity Conference on September 2.
My feed is full of healthcare professionals touting the benefits of AI in healthcare. Hope they're all using guardrails to ensure preservation of patient privacy and safety. https://t.co/ue5hH2hrfZ
Effectively managing third-party vendor security risks is both challenging and crucial, as these vendors are responsible for a disproportionate number of data breaches. https://t.co/xMu61J8CMm