Our online course is finally up. This one is a banger... 14 hours of video content alone, long and hard exercises (that's what she said). It was difficult to put together, but worth it!
Reverse engineering and security analysis of a smart home device based on the ESP32 SoC
https://t.co/cNosfyrJy6
Blog post by James Warner (@jmswrnr)
#esp32#infosec
In case you aren't aware...
@zseano has shared his bug bounty methodology to help you find security vulnerabilities in web application targets! 🤠
Check it out!👇
https://t.co/vEMLY2dkGF
The community has helped me a lot, and as a way to give back, I’m giving away:
1-Month Pro Lab
1-Month VIP Subscription
How to Participate:
1️⃣ Follow @hackthebox_eu
2️⃣ Like & RT this post
🎯Winners will be picked randomly on 31st January!
#hackthebox#Giveaway#infosec
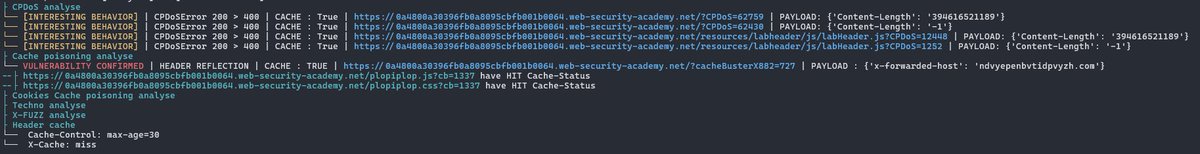
HExHTTP - Header Exploitation HTTP
HExHTTP is a tool designed to perform tests on HTTP headers and analyze the results to identify vulnerabilities and interesting behaviors.
https://t.co/d9KR9dukJi
An Open Source AI model {Deepseek r1} launched 72 hours ago.
This Chinese AI model just broke the internet.
People are running r1 model on:
- self hosted servers
- mobile phones
- raspberry pi
- mac books
Here're all the cool experiments, you check:
🧵