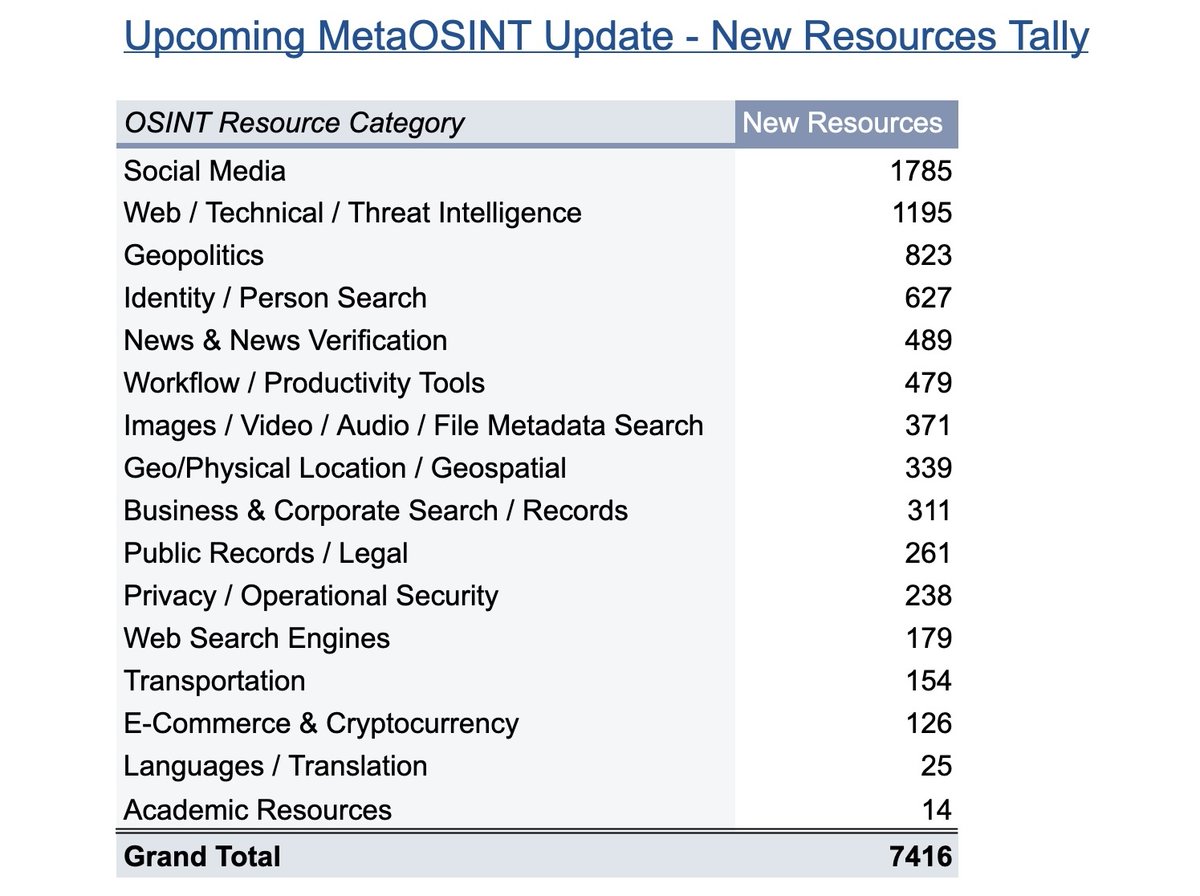
On its 1st anniversary, excited to announce the re-launch of MetaOSINT, the #OSINT tool & resource aggregator! v2 contains 900 new resources (5,700+ total) wrapped in an improved UI. The best news? A method for ongoing updates, so stay tuned for more ~weekly additions!
@BushidoToken@jamieantisocial Added here! https://t.co/FpkDrw5MWi
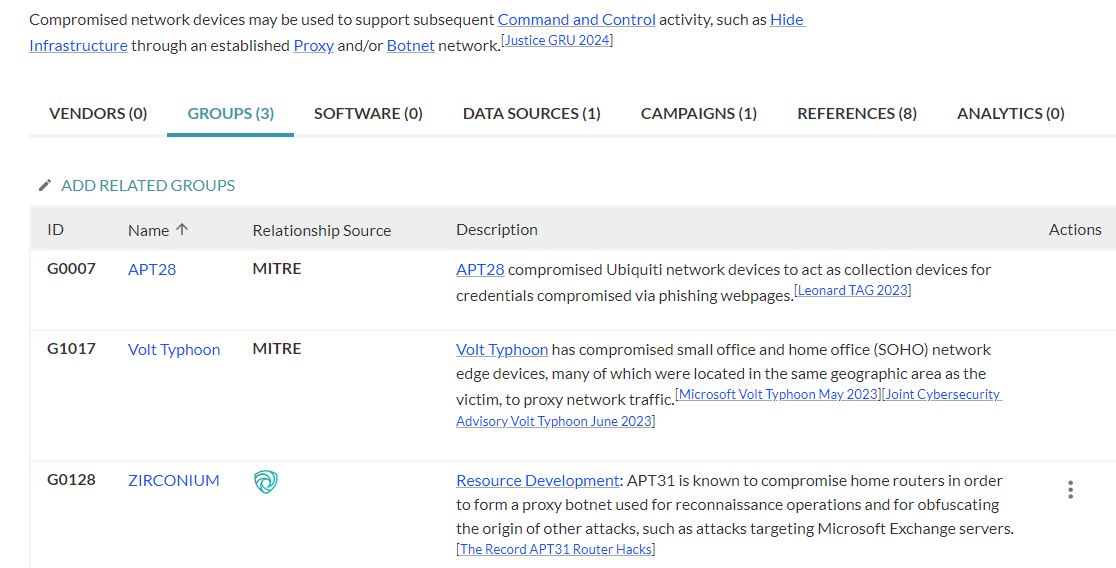
We’ll also have an ArcaneDoor Campaign added by end of the week/first of next
Really strong updates from ATT&CK this round 💪
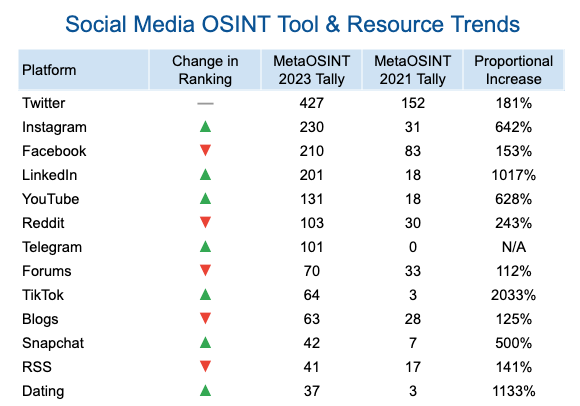
I’ve tracked thousands of #OSINT resources over a half-decade via the MetaOSINT project. Here are my thoughts on how the dataset’s evolution might reflect broader trends & changes in the underlying info landscape during a time of major global disruption: https://t.co/ZP5yRcYuFj
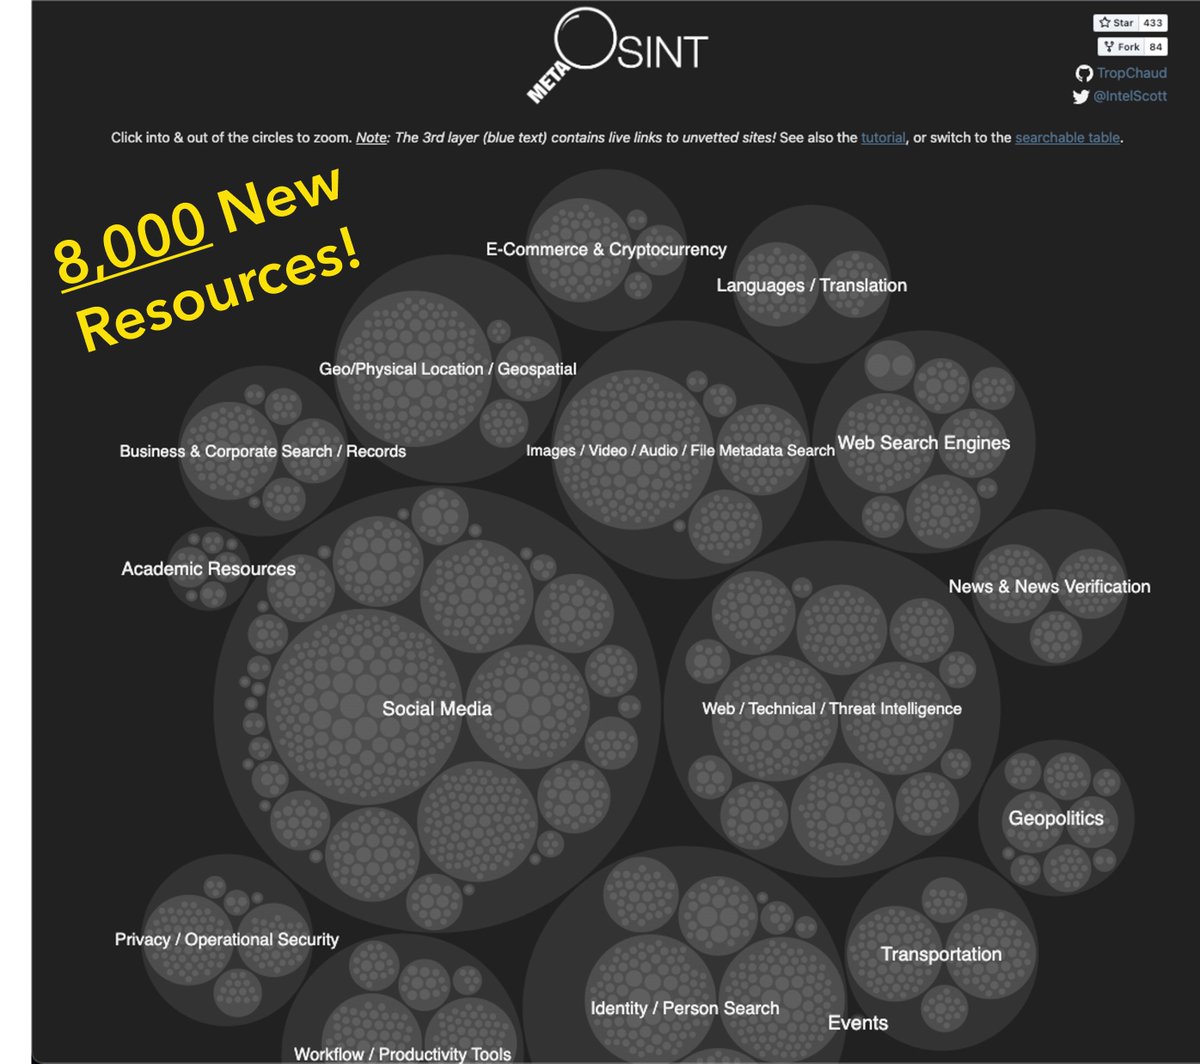
MetaOSINT v3.0 is live!
The first major update in over a year brings 8,000 new resources to the tool, more than doubling the previous tally. But structured categories & citation counts still make it easy to surface popular, relevant #OSINT resources: https://t.co/He1iwDQZfA
Long-overdue update (largest yet) to my #OSINT-focused project MetaOSINT coming soon! Adding a ton of new, timely resources to the database while maintaining its hallmark ease of use. Brush back up before the update lands in the coming days: https://t.co/srbAh35Rls
Taking a data-driven approach, @GlobalCyberAlln and @TidalCyber 's recent report validates the significant impact basic #cyberhygiene measures have in defense against the most relevant #ransomware methods of attack against #SMBs. Learn more at
https://t.co/EZXphxsN1p
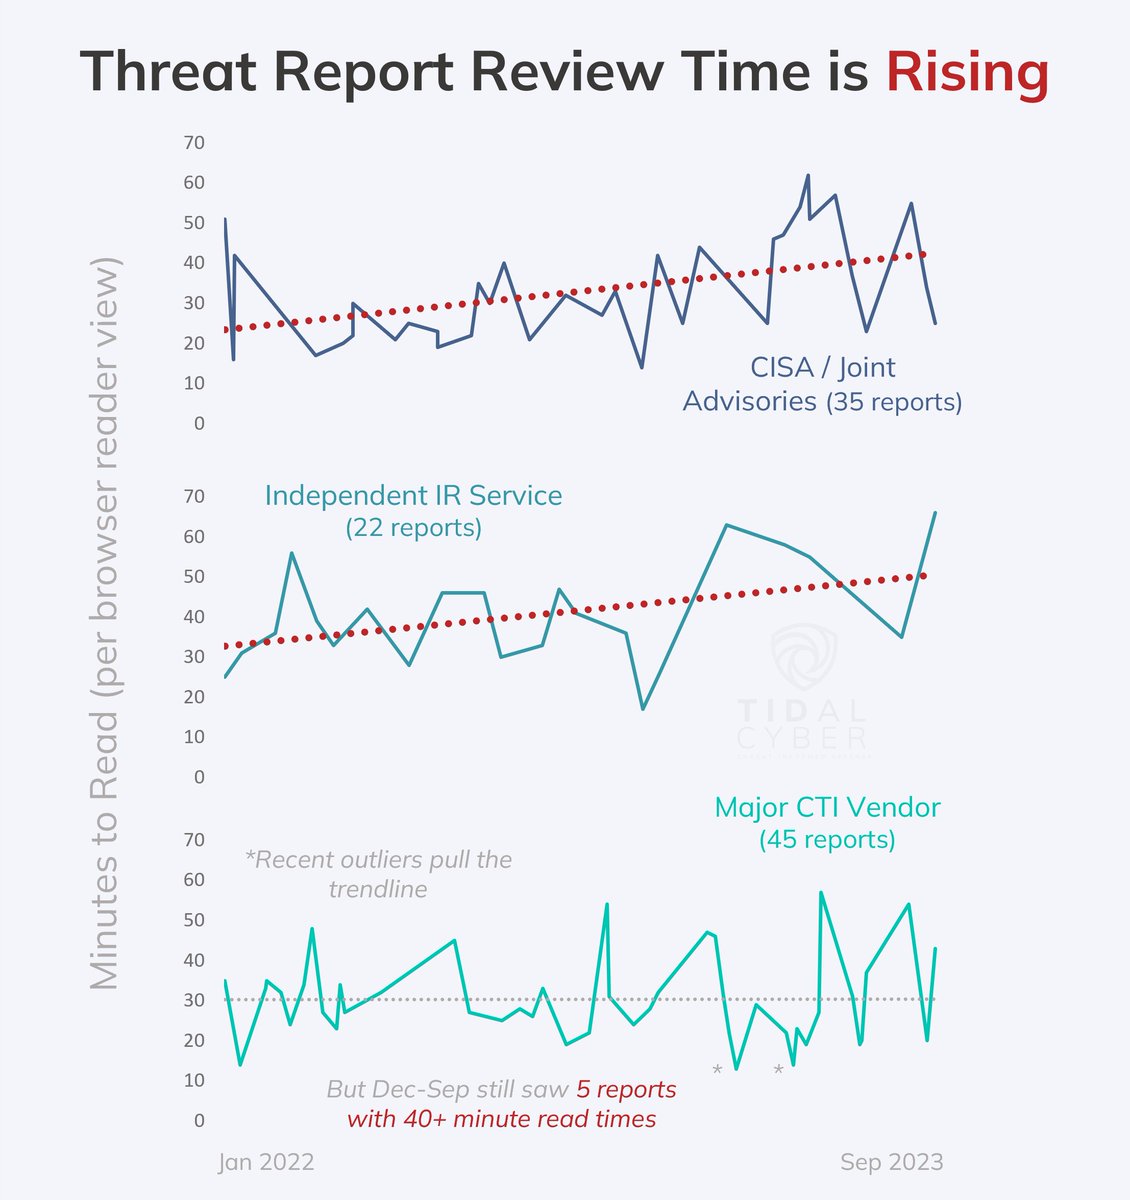
The rich detail in recent threat reporting is an extremely welcome trend. But the reality is that longer/denser reports can place more burden on teams, if they’re attempting to (or leadership expects them to) thoroughly process each one
Meet us in Iowa at the 2023 @QCCornCON on 10/5-7. @advemuian will be presenting "Using ATT&CK for Threat Profiling, Defensive Stacks, and Coverage Maps" and "Mind the Gap: From CTI to Defensive Improvements." Use code "TID25" for 25% off! https://t.co/fODEi2HJ8a #mitreattack
We added tons of content across our free Community Edition this week, including #BlackCat/#ALPHV & #ScatteredSpider tool & TTP collections and updates to @elastic & Atomic Red Team capabilities in our Product Registry: https://t.co/v0DuL5Bnhq #ThreatInformedDefense
@Cyb3rMonk Important points worth remembering. It will always be reactive by nature, but we see a lot more timely, TTP-focused CTI these days, and we've started to capture it in our knowledge base to help address the recency gap (some good examples on our homepage: https://t.co/QJDvoo70IJ)
NEW Community Edition content derives from @CISAgov's detailed new advisory. Start w/ the new Campaign object, pivot to dozens of new & updated Tools, Malware, & @MITREattack Technique relationships just added: https://t.co/N72X9jEWn9
The value here is organizing the exercise around a recent, prominent threat - recently enhanced Search in @TidalCyber Community Edition helps quickly surface relevant content, & pivoting on mapped @MITREattack techniques expands focus to include variations on observed procedures
New blog is out, walking through practical workflows for detecting & testing persistence behaviors used by #FlaxTyphoon#APT, entirely via free/community resources https://t.co/CztCi8gWvs
A set of mini purple team exercises involved a typical cast of characters including @redcanary#AtomicRedTeam tests + @sigma_hq rules run via Chainsaw on logs configured via @olafhartong's Sysmon-Modular config
Ultimately we contributed a new test aligned with an existing rule