DeepSource has been acquired by Harness.
Sanket and I started DeepSource on one bet: every line of code shipped should meet a high bar for quality and security, without a human having to review it.
Over the last eight years, we built DeepSource from the ground up: static analysis across 20+ languages, Autofix in 2020, before automated remediation was a category, code formatting, coverage, SCA and security, and eventually AI-powered code review and remediation.
The idea never changed much. Find problems before code ships, and fix as many of them automatically as we can. With agents producing code faster than humans can review it, there is a lot more of that problem to solve now.
I’m proud that everyone from open-source maintainers to enterprises relied on DeepSource to ship better code. More than anything, I’m proud of the team that built it.
Harness is building the Autonomous SDLC Platform to catch risks in software before it ships, and our vision aligns perfectly with theirs. I'm excited that DeepSource is joining forces with them and continuing our work.
https://t.co/BRzDdV9guH
GLM 5.2 nearly doubles GLM 5.1 at patching real CVEs.
We hand the model a vulnerable repo and it has to ship a patch that closes the actual exploit. A per-CVE security oracle runs the attack, confirms it no longer fires, and checks the fix didn't break the feature. No partial credit.
GLM 5.1 → 5.2: 10.2% → 18.9%. Full eval dropping soon.
320+ npm packages compromised today: timeago.js, echarts-for-react, and hundreds of packages in the @antv ecosystem.
Supply chain attacks aren't slowing down, and the triage bottleneck is getting worse.
In monorepos, one vulnerable dependency can show up across dozens of sub-projects. Same CVE, different teams, unclear ownership.
DeepSource now scopes OSS vulnerabilities per sub-repo in monorepo mode. Each sub-project gets its own Dependencies tab, with results scoped to the packages used by that sub-project.
https://t.co/aWZzuQUxQj
Everyone should save their session history, did u know all your Claude code sessions get deleted every month unless you change that in settings.json?
All that is valuable training data they’re keeping! So you should too.
I have a few repos on GH to help you do this. Share it
@prateekkathal @deepsource @arammelkoumov 👋One GitHub org install maps to one DeepSource team, so two teams can't share the same repos directly. Usual option is to split repos across two GitHub orgs.
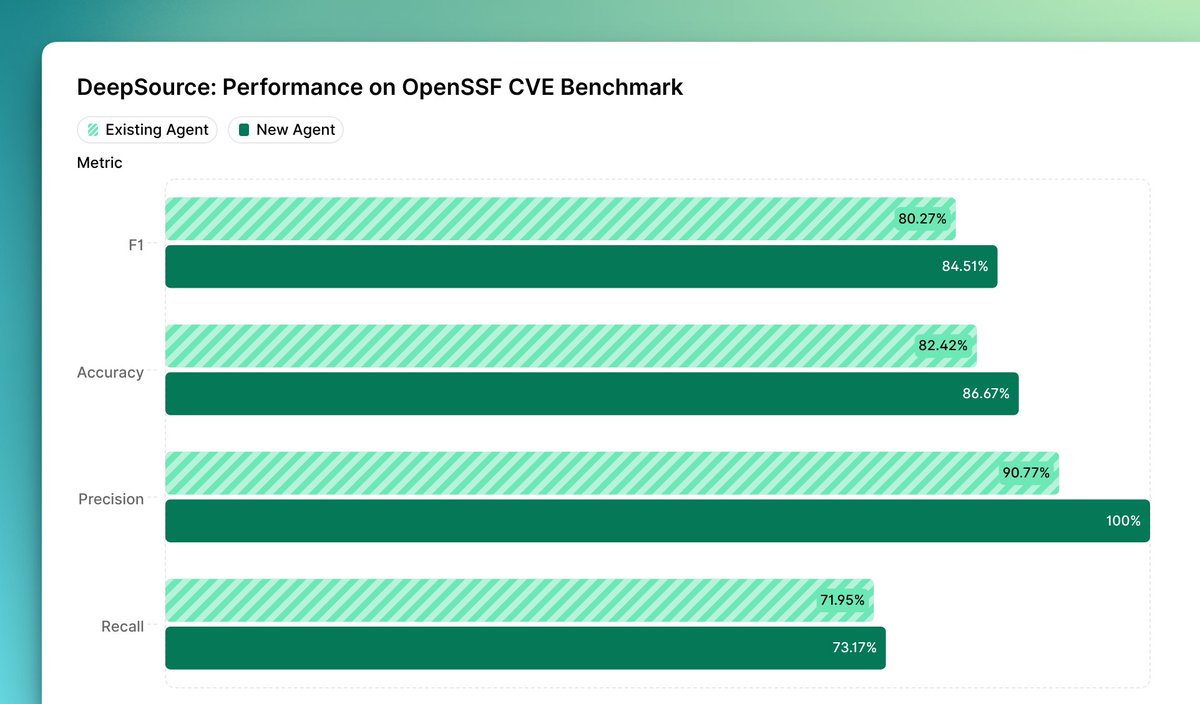
DeepSource hit 82.42% F1 on OpenSSF CVE Benchmark, in our latest run. 100% precision, 71.95% recall.
That's zero false positives across 83 real CVEs. Every alert is real.
Hybrid analysis. Static gives you the deterministic baseline, AI fills the gaps on context-dependent vulnerabilities.
DeepSource AI Review now scores higher on the OpenSSF CVE Benchmark. Most importantly, we're seeing 4%+ gain on the F1 score.
This means we're catching more real vulnerabilities without introducing a single false positive.
Our precision hit 100% (zero false positives across 83 patched diffs) while recall climbed to 73.17%.