3500+ vulnerabilities later, with a pretty decent standing on bug bounty platforms and I still can't get my CVP application approved by @AnthropicAI?
Meanwhile, some applications are getting approved within 24-48 hours. Is there actually any serious criteria for approval, or is it just random? What a joke.
IMO opus and sonnet models are enough to make everything else redundant at this point. It’s just lack of awareness with the partners but it’s only a matter of time. Most likely scenario is if they’ve got an edge or good enough contracts they will be acquired but under the hood they’re using the same AI tech… the only difference is how they’re distributing or were efficiently managing their workflow with a low cost basis, which is a problem that imho is already solved with the subscriptions we have available today.
An there it is - "Domain Intelligence": https://t.co/QSbUjS32OW (for public access)
Feel free to explore. Trial users can explore preset limited data, growth plans+ can search their own stuff!
@Jayesh25@ITSecurityguard@Th3G3nt3lman@GodfatherOrwa
Why can the https://t.co/PfEgdZF0Nj database look smaller in some cases?
Because bigger subdomain counts can just mean more wildcard noise.
This article explains why:
https://t.co/oyxPlMfQe7
I’d say each has its own strengths but personally I’ve already replaced SecurityTrails with ArgosDNS. In my testing I’ve seen better quality results probably because the data seems to refresh more frequently and the product seems to be very focused on this niche. Another big factor for me was the price point it’s realistic enough that I can actually run it every few days via the API. With SecurityTrails that gets pretty expensive very quickly. That said, the free version is a good starting point if you want to compare the results and data freshness yourself before deciding. Most people will probably end up seeing similar differences once they try both :)
I've had firsthand access to ArgosDNS and can say it’s produced quite a few solid results that I didn’t even have in my own database. Unlike many tools, the data actually feels meaningful rather than just raw volume.
I've known @damian_89_ a while and have been chasing him for ages for his recon secret sauce 😄 From what I’ve seen so far, ArgosDNS is doing a lot of smart permutations, picking up real-world naming patterns, scanning cloud certs, and doing a ton of crawling behind the scenes to get this data. It’s also nice that the dataset is already deduped so you’re not dealing with garbage.
Feel free to give it a shot at https://t.co/x6OPnFzIxd
Hey guys, I just launched https://t.co/ruxCzwsAni - if you are into IT security, bug bounty hunting, red teaming, ... this is interesting for you!
https://t.co/LdIxeQKhQw
@Omkumar_13 Not quite what I meant but during live hacking events programs have a higher bounty scale than usual and of course these are high-paying programs that one would usually shy away from unless they were specifically in an LHE and learned about their true potential.
Here’s a quick insight into how a single opportunity can dramatically change your earning potential in bug bounties.
Ever wondered what kind of difference a Live Hacking Event (LHE) can make?
Picture this:
You report 10 XSS vulnerabilities on a newly launched public program and walk away with around $5k in total bounties.
Now compare that to someone invited to a Live Hacking Event reporting those same 10 XSS bugs - they could easily walk away with $75k–$100k. Same bugs. Completely different outcome. That’s the power of getting invited to an LHE. It unlocks new scope, direct access to top programs, face-to-face interactions with HackerOne triage and security teams, networking with elite hackers, and opportunities you won’t get anywhere else.
HackerOne has outlined the eligibility criteria for invites here: https://t.co/JNCqXhSpBk
My advice? Focus your efforts on aligning with these criteria. One invite can really shift your entire growth curve, skills, learning, recognition, and bounties.
PS: Drop a comment if you feel you should’ve been invited to an LHE but haven’t yet. I’d love to hear your experience and it may help surface visibility for @Hacker0x01.
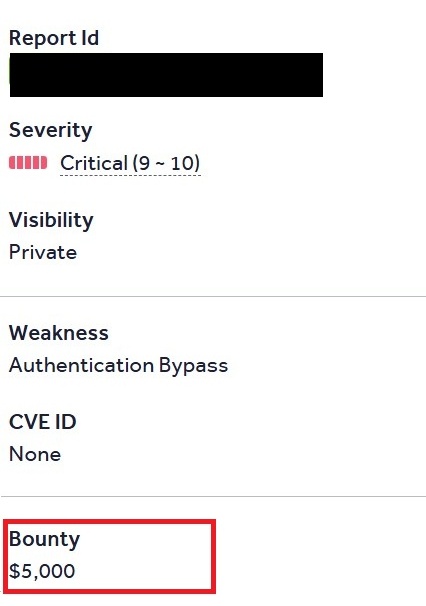
Scored a $5,000 bounty today. I’ve only started messing around with AI in my workflow THIS week. Normally I’d spend hours trying to escalate certain bugs - the kind that takes a lot of digging and escalation and I'd usually end up moving away from it considering the ROI. But this time I let AI handle some of the painful parts of the manual escalation process and it actually helped me efficiently escalate the bug. Ended up turning what would’ve been a tiny payout into a $5000 bounty.
Now I’ve basically got Burp Suite on one screen, AI on the other, and it feels like cheating (in a good way).
This might actually change how I hunt moving forward with respect to escalating stuff to avoid manual work whereever possible. 🚀