Hi, I’m Kevin Villarreal! 🤓
I created this account to continue my journey to becoming a great security professional. I may not have the years of experience as many others, but I am driven and passionate about cyber security.
Feel free to connect!
#MayTheForceBeWithYou
🛡️Not a new setting. A new look.
Authenticator's redesigned prompt puts the app and location front and center. But if your tenant says "Microsoft managed," users won't see either.
https://t.co/nikDhqby58
#EntraID#MFA
How’s my Monday going? Glad you asked.
Cracked open my afternoon energy drink (I know, I know ...I have an almost-5-month-old, cut me some slack) and my cat jumped up on my desk.
I very politely asked her to get down. Her tail responded by sending the entire drink across my desk.
Send help. Or paper towels.
🎃 Is your break-glass account excluded from EVERY Conditional Access policy? Sure about that? 👻
Microsoft's new CA policy plans (preview) let you define exclusions once and no rule can remove them.
New post:
Don't Let Your Exclusions Ghost You
https://t.co/LjX66oRgCQ
#MicrosoftEntra #ConditionalAccess
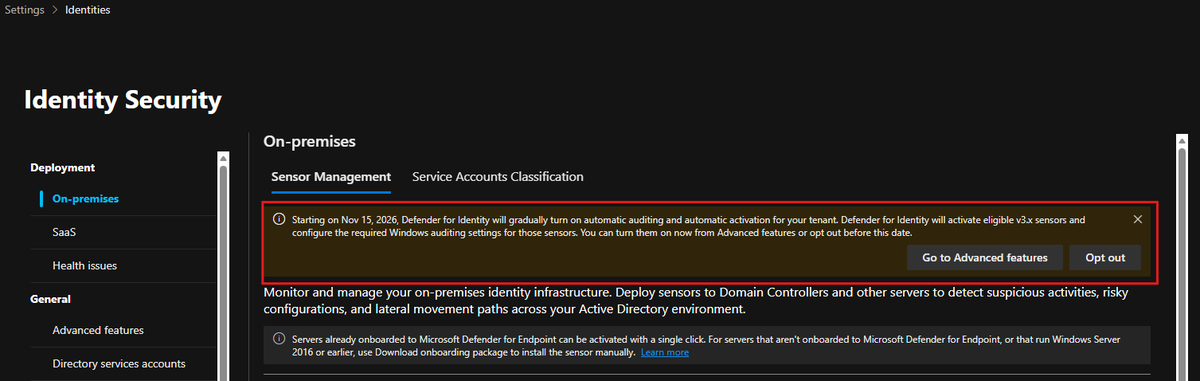
🚨Heads-up for anyone running Microsoft Defender for Identity: Microsoft is rolling out automatic activation of sensor v3.x and Windows event auditing for existing customers.
Here’s what’s changing:
🔹Eligible orgs (licensed for Defender for Identity with an active workspace) will see a 30-day notice banner on the Sensor management tab.
🔹After that 30-day window, both Automatic sensor v3.x activation and Automatic Windows auditing configuration turn on by default, including settings currently set to Off, via a gradual rollout.
🔹To keep your current configuration, select “Opt out” in the banner during the notice period.
If you manage Defender for Identity for your org or a client, this is worth checking now rather than after the rollout completes. Review your current sensor/auditing settings and decide whether the new defaults are appropriate before the opt-out window closes.
Full details: https://t.co/MiFBTJstvm
#MicrosoftSecurity #DefenderForIdentity #XDR
Heads up, Defender admins 🛡️
Noticed this today. Not sure if I've seen any announcement or anyone post this. But certainly, very interesting....
The Defender CSP now marks EngineUpdatesChannel and PlatformUpdatesChannel as [to be deprecated].
The successor looks to be DeploymentChannel: one setting for engine + platform updates...maybe
Details here:
https://t.co/tkvz09cb4h
After March 31, 2027, Microsoft Sentinel leaves the Azure portal for good.
New video: turn a plain Log Analytics workspace into Sentinel and connect it to the Defender portal.
🛡️ https://t.co/MpdUAZT0Il
#MicrosoftSentinel
The North remembers. Entra ID does not.
Entra keeps your sign-in and audit logs for 30 days. On Free, it's 7. After that, they're gone like a Stark at a wedding.
New post: The Maester's Archive, covers how to build your own Citadel before you need it:
📜: https://t.co/XkBTRMAebq
#EntraID #MicrosoftSentinel
Don't scroll past this one. Web sign-in on hybrid joined devices, with phone passkeys, FIDO2 keys, and TAP at the lock screen, and Kerberos still works for on-prem. Every hybrid org with shared devices should be watching this hit GA.
This is huge for more reasons than one!
Windows 11 Build 26340.9750 (Insider Experimental Preview) adds hybrid join support for the web sign-in provider
It also allows for use of passkeys from phones 🤯
We finally have a simple, unified login provider for shared devices!
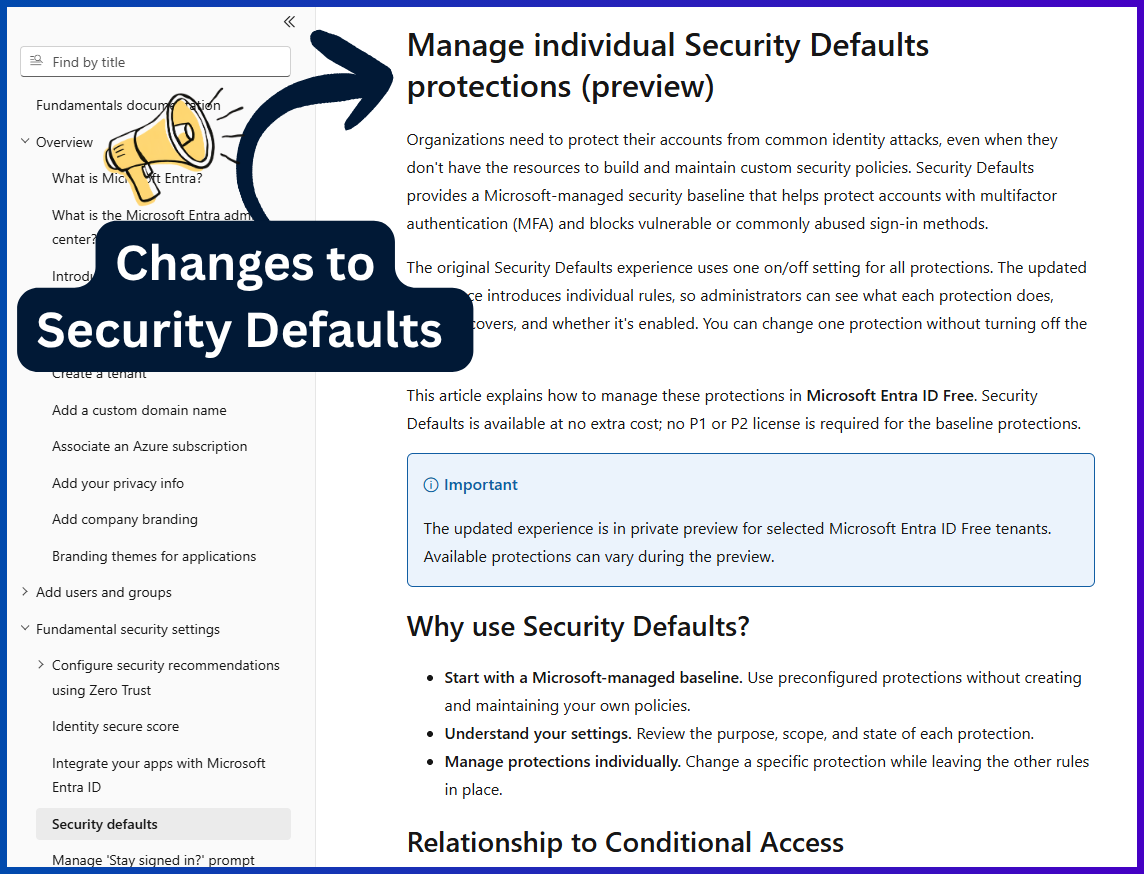
You will soon have more control over Security Defaults in Microsoft Entra! Read about it here > https://t.co/cFCCEbbYqj
Microsoft just updated their public Security Defaults documentation highlighting a current feature in Private Preview, that allows you to manage and enable individual protections within your Free Microsoft Entra tenants that use Security Defaults. Previously all protections were either On or Off.
This is an awesome new change that will help organisations roll out Security Defaults carefully, as well as support migrations to Conditional Access based controls!
#Entra #Microsoft #News
Microsoft just added 18 new security alerts to Defender for Identity in the October 2026 release, one of the bigger alert drops I’ve seen in a while. Breakdown of what matters:
🔹CVE-2025-33073 exploitation: dedicated detection for this specific Kerberos relay vulnerability. If you haven’t patched yet, this gives you a compensating detective control in the meantime.
🔹AD CS certificate abuse (3 new alerts): native coverage for ESC1, ESC8, and ESC11 misconfigured template and issuance abuse paths. These are well-worn red team techniques finally getting first-party detection.
🔹Suspicious sign-in via Temporary Access Pass: TAP is meant for MFA bootstrapping and account recovery, but it’s also a known persistence/bypass technique when abused. Good to see this covered.
🔹DPAPI master key theft + DNS-based data exfiltration: two common post-compromise techniques that signature based tools routinely miss.
🔹First real wave of Okta-specific alerts (7 total): token theft, MFA method tampering, privileged account auth anomalies, consent-grant abuse, and more. If you’re running hybrid Entra/Okta, this closes a real visibility gap MDI didn’t have before.
These roll out automatically, no config changes needed, worth checking your alert dashboard to confirm you’re seeing them.
Full list: https://t.co/d2Kp3X1WoS
#MicrosoftSecurity #DefenderForIdentity #IdentityThreatDetection
SMS MFA is leaving Entra ID. Most of what replaces it doesn't need a phone at all.
New post: passkeys, FIDO2 keys, Windows Hello for Business, a staged rollout, and a plan for users with no phone.
https://t.co/3mPQhr5nbG
#EntraID#Passkeys
I've been having an absolute blast releasing the videos and blogs I've been hammering away at.
Take the plunge. Who knows where it'll take you! At the very least, perhaps you'll enjoy the process.
...and I've been behind the scenes getting my GitHub stood up...more to come (hopefully😂)
@fabian_bader So this is my pep talk to you.
Go ahead and release that project you've been working on, the YouTube channel you've wanted to create or the blog post you've been meaning to write.
You never know where it will take you.
Create more than you consume.
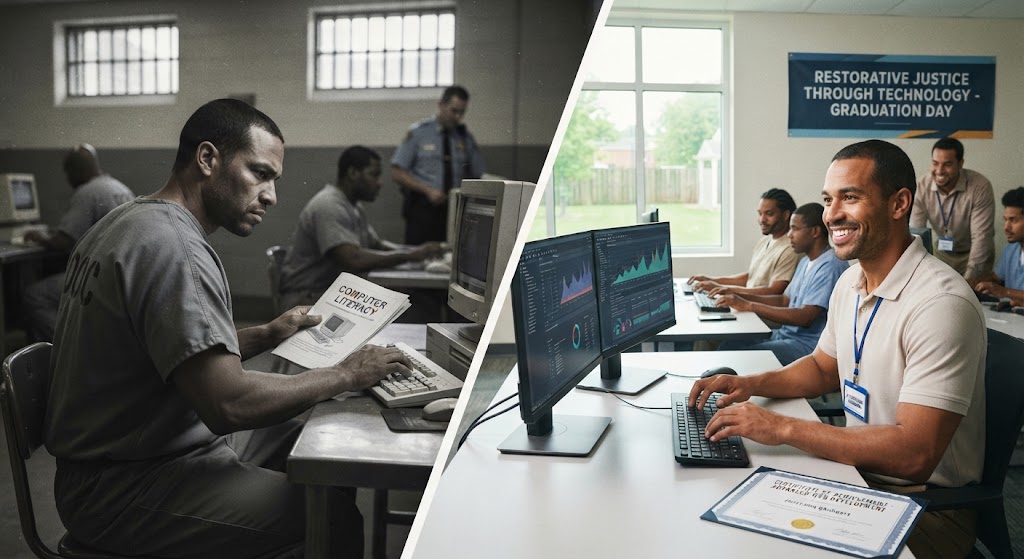
Patriot Consulting and I are matching donations to help @TLM modernize technology classrooms inside correctional facilities, giving students skills to build meaningful careers and a new life after release. Learn more & please consider donating.
https://t.co/0d7bU40r3K
Most tenants have a break-glass account. Far fewer have one that works on the worst day.
New post: emergency access accounts done right in Entra ID. FIDO2 keys, CA exclusions, SSPR side doors, alerting, drills.
https://t.co/ziXiGweetb
#EntraID#MicrosoftSecurity
Defender for Servers billing changes hit Nov 1:
🔹 Plan 1: Windows 10/11 client devices no longer billed as servers
🔹P1 + P2: machines counted individually, incl. golden-image clones sharing an Arc ID
Baseline your server counts now.
https://t.co/QGKodZdsUR
Before you flip that Conditional Access policy on, test it first.
Final part of my CA 101 series: using the What If tool to simulate a sign-in, confirm your break-glass account is excluded, and catch mistakes before they go live.
🎥 https://t.co/9ALyl9KGXb
#EntraID #ConditionalAccess