Dude uses the community reputation he has to intentionally stir drama to promote his new song.
And somehow y’all are just okay with that.
Damn.
We can talk about the issues the fandom has but getting played like a fiddle and doing exactly what they seem to want ain’t it.
So let me get this straight. One of the most controversial people in the fandom, went undercover for a while, got a second fursuit which their maker didn’t want to make, some people called out the red flags, others are mad at this.
Well I sure hope you don’t have hours of your voice freely available on the internet
In other words, we’re fucked.
This is your reminder to have a code word with every of your loved ones if you can’t otherwise verify it’s them.
New cat alert! A call from a wildlife sanctuary about a "weird cat" has led to the first new cat species discovered in over 100 years in Bolivia’s Yungas forest ecoregion. Learn more about this feline surprise: https://t.co/crffXvPqH4
@hanifbali@r_marked@cedric_dev They do but they explicitly state not to use these for „personal, protected, or sensitive data, or information restricted by law.“. And they are limited to 255 chars which might not cover the specific legal phrasing and links to ToS requirements.
@ICanAddUp@r_marked@cedric_dev The law dictates in this case that it needs explicit consent and agreement by the user from a not pre checked box with notice with specific wording that has to be shown during the checkout process. It’s the same kind of blocker as „agree with our tos“ at signup.
@r_marked@cedric_dev Currently I am facing a similar situation with Stripe in this case. Using their hosted pages there seems to be no solution for this issue provided by Stripe for this checkbox approach. 😔
🚨 BREAKING: cPanel and WHM, the control panels behind an estimated 70+ million websites, have a critical security flaw that lets anyone become root admin without a password. CVE-2026-41940 affects every supported version. It’s already being exploited in the wild.
watchTowr Labs published the full attack today, after the hosting company KnownHost confirmed the bug was already being used to break into a significant chunk of the internet.
If you've never heard of cPanel: it's the dashboard that hosting providers and millions of website owners use to manage their servers, domains, email accounts, databases, and SSL certificates. WHM is the admin version that controls the entire server. If someone gets root access to WHM, they get the keys to the kingdom and to every apartment inside it.
How the attack works, in plain English:
🔴 Step 1: The attacker sends a deliberately wrong login. cPanel still creates a temporary "you tried to log in" record on disk and gives the attacker a cookie tied to it.
🔴 Step 2: The attacker tweaks the cookie to disable cPanel's password encryption. Normally cPanel encrypts the password field on disk. With one small change to the cookie, cPanel just stores it as plain text instead.
🔴 Step 3: The attacker sends a fake login attempt where the password field secretly contains hidden line breaks. cPanel does not strip these line breaks out, so they get written straight to the session file. Each line break creates a brand new fake record. The attacker uses this to inject lines that say "this user is root" and "this user already authenticated successfully."
🔴 Step 4: The attacker visits one more random page on the site to nudge cPanel into re-reading the file. cPanel then promotes the injected fake lines into its main session memory.
🔴 Step 5: On the next request, cPanel sees a flag that says "this user already passed the password check." cPanel trusts that flag, skips checking the actual password, and lets the attacker in as root.
From start to finish, the attack takes a handful of HTTP requests.
If you run cPanel or WHM, the patched versions are:
🔴 cPanel/WHM 110.0.x → 11.110.0.97
🔴 cPanel/WHM 118.0.x → 11.118.0.63
🔴 cPanel/WHM 126.0.x → 11.126.0.54
🔴 cPanel/WHM 132.0.x → 11.132.0.29
🔴 cPanel/WHM 134.0.x → 11.134.0.20
🔴 cPanel/WHM 136.0.x → 11.136.0.5
If your version is older than these, assume someone has already broken in and act accordingly. Patch right now, then rotate every password and key the server touched: root passwords, API tokens, SSL private keys, SSH keys, mail passwords, and database passwords.
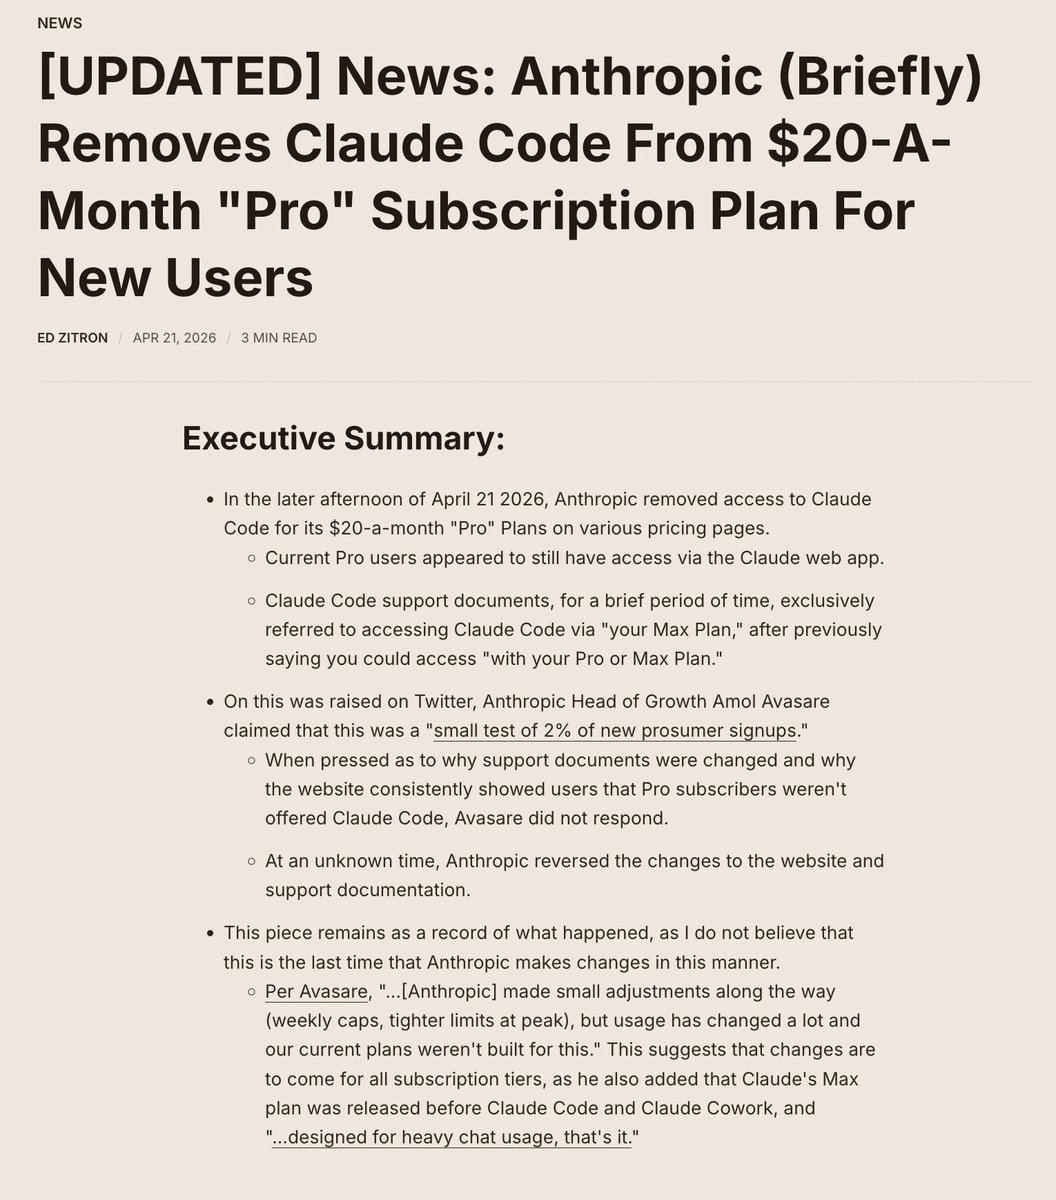
Anthropic has now reversed every change, and said that removing Claude Code from Pro was a "small test of 2% new prosumer signups." This doesn't explain why changes were made to support materials and the website, and I think we see changes to Max soon.
https://t.co/dMnjpa0YKP