Doing the best I can and learning as I go with my investments to make life better for my family. 🚒🚑 is my main gig but also selling sports and trading cards.
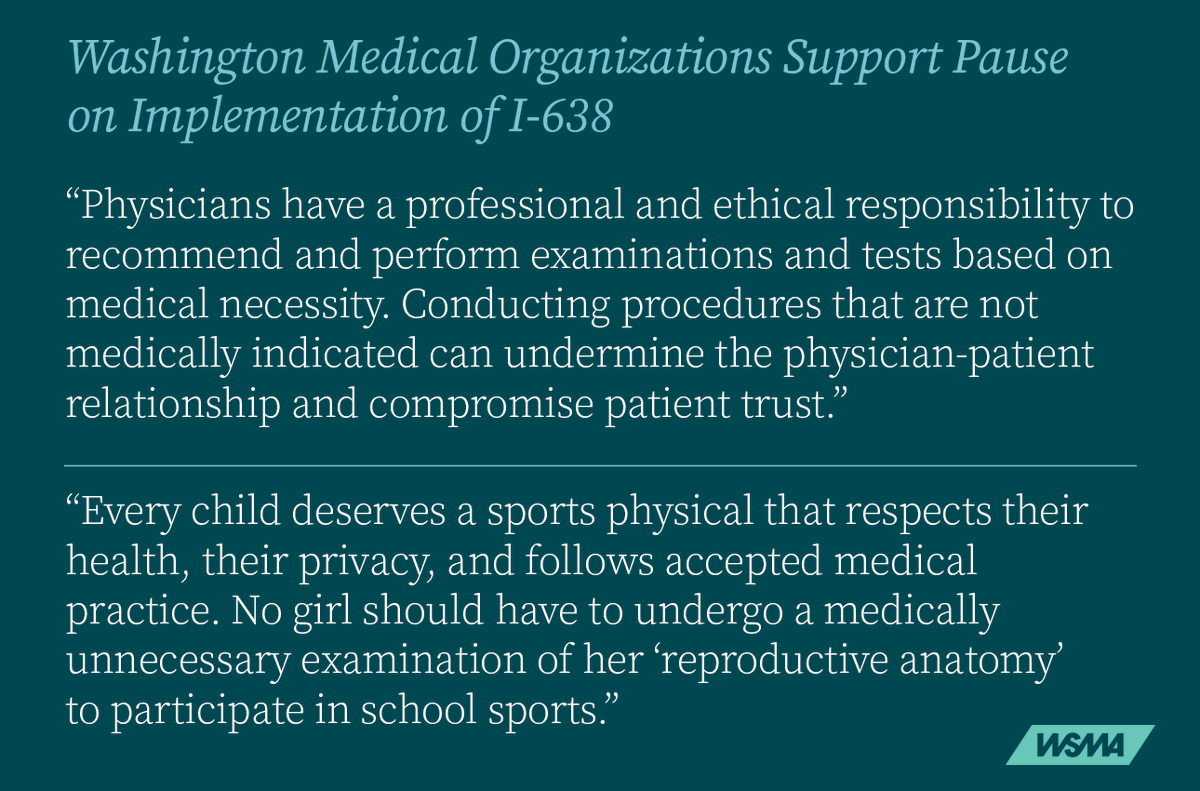
The Washington State Medical Association joins with six other statewide physician associations in support of the lawsuit brought by The ACLU of Washington, Legal Voice, and the Washington Education Association seeking to pause implementation of I-638.
While we recognize the public’s concern for fairness in sports, as statewide medical organizations we are deeply troubled by the initiative’s mandate imposing medically unnecessary examinations and verification requirements on girls participating in school sports. We believe:
- Every child deserves a sports physical that prioritizes their health, safety, and privacy; and
- Physicians should be able to follow accepted medical standards, perform examinations based on medical necessity, and ensure that all children have equitable access to the benefits of sports participation.
Together, we support the legal effort to pause Initiative 638's implementation as students, families, schools, and physicians need time and clear guidance to address these concerns before the initiative takes effect.
🔗 Read our full statement: https://t.co/Vul3ugGdd6.
#YourCareIsatOurCore
Washington State Medical Association
American College of Obstetricians and Gynecologists – Washington Section
Washington Academy of Family Physicians
Washington Academy of Physician Associates
Washington Chapter of the American Academy of Pediatrics
Washington Chapter of the American College of Physicians
Washington State Psychiatric Association
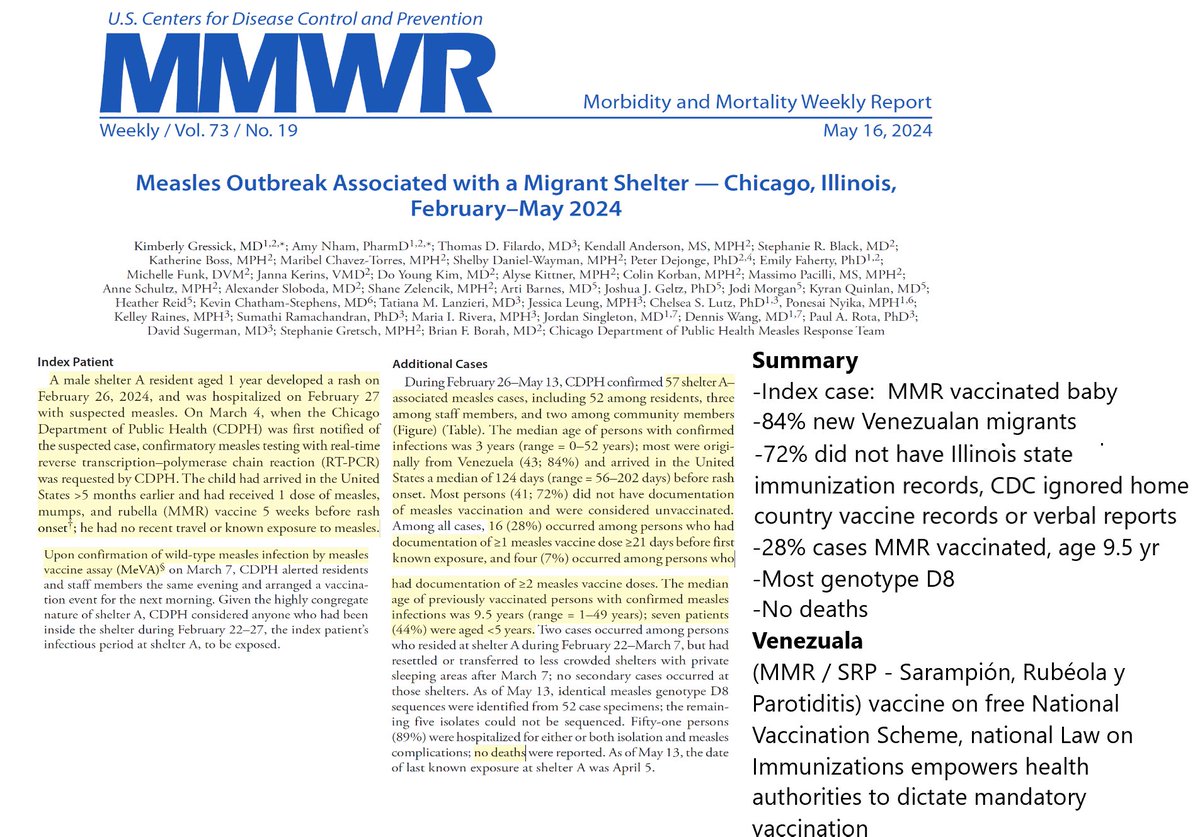
Fifty-Seven Cases, Zero Deaths, and a Vaccinated One-Year-Old at the Center of Chicago’s Measles Outbreak
Locally acquired infection in a maximally immunized toddler, a crowded shelter, ignored parentally held immunization records, unnecessary hospitalizations, all framed in CDC vaccine-promoting report. URL TheFocalPoints. @McCulloughFund
Is it me or does everyone believe we’re in the middle of a cyber attack? And don’t forget about the bomb threats (they’re quite disturbing as well).
What is happening (my analysis):
We are being “Pharmed.”
Pharming (a technical term) is planting a Trojan Horse, a backdoor, or a persistent foothold inside an organization's network NOW, allowing a foreign adversary to maintain access, observe activity, collect intelligence, and potentially exploit that access LATER (I suspect these are orchestrated test runs).
During Pharming, there will be many Phishing attempts. These phishing attempts typically trick you into following a deceptive link. Don’t fall for their tricks. Be overly cautious.
Pharming manipulates the technical routing (some of the mumbo-jumbo we’ve been hearing about), so you may not need to click a deceptive link at all. It may simply walk right in because of previously unknown or unreported Pharming efforts.
Lastly, Pharming is a technique used by nation states and sophisticated criminal organizations…so let’s see what happens next.
Until the fat lady sings, it ain’t over. And I don’t hear any singing yet.
All you cyber experts working inside of these institutions being hit, good luck!
Proverbs 1:7 🙏🏼🇺🇸
PS., don’t anyone try to tell me that our election systems are secure. Funny this didn’t happen on Election Day.
@GovBobFerguson If the companies that make them are immune from legal action no matter how many they kill then we 100% need skeptics to oversee them. The uptick is from the tens of millions of illegals and improper testing…
Seems like grok bot and grok clash when you started with grok connected and then try to have grok bots take over. Grok keeps placing trades the bots don’t approve of so they close it, but grok has been told multiple times to let the bots take point. I’m probably doing it wrong but if asked them to find any issues and fix them and it seems to be worse.
It’s not a budget shortfall though, it’s overspending and fraud. Spending has more than doubled inflation and population growth combined. Why can’t we just audit where it is all going and verify it’s getting there and a needed expense? Trying to help and helping are very different things, we throw money down the drain on every issue while doing nothing to fix any issue or actually impact the people needing the help. The answer is never more money, it’s accountability.
Breaking: When it looks like a duck, quacks like a duck, and walks like a duck, it’s probably a cyber attack.
There have simply been far too many electronic systems going down lately.
First Cox Internet, then Microsoft, then FAA, then AMTRAK, and today, it’s the banks, and being reported time now, American Airlines and United Airlines. Wow, simply breathtaking!
One thing they all have in common; the open Internet.
Seriously, this looks and smells like a massive cyber attack. If nothing else, our adversaries are getting a hard look at vulnerabilities and if there is any effective, cross talk between governmental and nongovernmental institutions. It appears there is little to none.
Keep in mind, all of these organizations have massive numbers of defensive cyber personnel and technical capabilities to protect and provide assurance to the people they serve (so there should be a lot of those people looking for new work about now).
Additionally, the CYBER Command / National Security Agency, CISA, and other USG entities have “red teams” designed to identify and then block and tackle any adversarial actions in the cyber domain of warfare. They should be, at a minimum, notifying (especially anything tied to critical infrastructure) these institutions as well as cross talking within the inter-agencies of the USG.
My guess is they’re on their a**es.
Lastly, we’re past the stage of believing these are coincidental glitches due to faulty equipment or outdated infrastructure. Also, no amount of money fixes the scale of problems we’re currently experiencing. When you are in a war, you must understand the nature of the war and you must clearly and unequivocally define the enemy you’re up against. Then and only then, you can make plans to destroy them. I don’t believe we’ve done that. This isn’t just a DOW problem, this is a national security problem.
This is past the point of being a physical war, we are in the middle of a spiritual war, one where good versus evil are the two adversaries.
I pray the good guys win.
PS., I pray this isn’t a distraction drill to keep us from demanding that our recent elections get audited. In the end, the truth always rises to the top…in this case, it eventually will because too many seriously smart people are examining every iota of data and every inch of what is happening.
PSALM 23 🙏🏼🇺🇸
I don’t know if everyone is paying attention but most of the fear mongering is coming from posts automatically translated from Turkish and Chinese writers as far as I’ve seen. I’m not dismissing everything, but I think a grain or bag of salt with each post is necessary.
@JustGrokingIt@grok This is incredibly stupid. Everyone has heightened worry and you prey on them with some exhaustingly garbage fake document. GFY, blocked
Bro, they aren't even trying to hide the corrpution anymore!!
The FAA airline stoppage story is a MUCH bigger one than the ground stop itself, and I only saw it once I started following the money and who gets paid...
Here is what I found...
The official line is that it was NOT a cyberattack and NOT a "nefarious act."
US Transportation Secretary Sean Duffy points at overloaded routers and old broken equipment. Sure we can take that at face value, because it matters for what comes next.
Because on the SAME day, the White House went to Congress for 10s of billions of dollars to rebuild air traffic control, and Duffy pushed the number EVEN higher on camera.
Both happen on the same day, a very public failure declared NOT an attack, and the argument for a VERY large cheque built straight on top of it.
Whether the outage was engineered or was just the system rotting on schedule, the political result they are after is the SAME, the breakdown becomes the justification for MORE MONEY.
The money is the whole point here, and it ends up in one place...
The "brand new" air traffic control system contracts was handed in December 2025 to a single prime contractor, Peraton, a company owned by the private equity firm Veritas Capital, and chosen despite limited FAA experience.
The full program is priced at around $31 billion dollars. Congress has so far put up only $12 billion as a "down payment." The rest is still UNFUNDED.
So Friday's breakdown arrives as the pressure to approve the rest of the SAME program already promised to the SAME private contractor; Peraton.
Most US airports are public, owned by cities and airport authorities, but the terminals and the systems get built by private firms, and that is where the billions flow, out of public failure and public money into private hands.
So who are those PRIVATE HANDS benefiting most? Who ultimately gets the money?
The prime contract went to Peraton, a private company owned by the private equity firm Veritas Capital.
And who funds Veritas? Its investors are Israeli institutions: Clal Insurance $100M, Migdal Insurance $60M, Menora Mivtachim $50M, plus ~$150M from private Israeli investors, all in its at least $15.3 billion fund.
Peraton’s lobbyist is Mark Bednar also sits on the board of the "nonprofit" that funded Sean Duffy’s TV show “The Great American Road Trip”.
This is the question, and it needs to be examined by EVERYONE.
A pressure tactic to MOVE public money into private hands, while America and Americans pay for it with 5,000 cancelled flights and the economic fallout from that many cancelled flights…
The proximity is on the public record too, lobbying and personnel links running between the contractor and the officials now asking you to fund it.
Americans ate the cancelled flights and a wrecked weekend.
The money walks the other way, into private hands, and the whole thing is dressed up as an emergency repair.
Who will investigate this corruption and conflict of interest?
See the next set of ties in the comments. Follow for more...
𝗦𝗜𝗚𝗡𝗔𝗟, 𝗡𝗢𝗧 𝗡𝗢𝗜𝗦𝗘!!