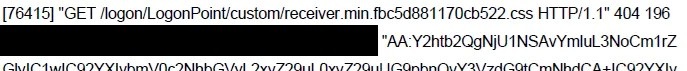
1/4 NetScaler exploitation IOCs (CVE-2026-88771 suspected) 🚨
Sharing detection info from a failed exploitation attempt seen on 22 Sep. Unauthenticated, two-stage, fully automated. Shared for detection only, so you can check your own logs.
#NetScaler#Citrix#DFIR
2/4
Staging
The attacker sends a request with a Base64 payload in the User-Agent, prefixed with "AA:". It returns a 404, but the goal is to get the payload written into the access log.
GET /logon/LogonPoint/custom/receiver.min.<hex>.css