Check out our technical analysis of #RaspberryRobin's multilayered approach to thwarting analysis and evading detection.
Read the full technical analysis here: https://t.co/Vqsqh8vHeV
My @OrangeCon_nl talk is live!
Elevate your knowledge: From COM Object Fundamentals To UAC Bypasses.
A 25-minute crash course covering Tokens, Privileges, UAC, COM, and ultimately bypassing UAC!
https://t.co/H1VZJdBzTZ
My company @ogSecConsulting has partnered with @zeropointsecltd to create some essential report writing training. It will not just boost your writing skills but also the efficiency & quality of your assessments. Check out what's covered in the course here: https://t.co/I22yGgJFEd
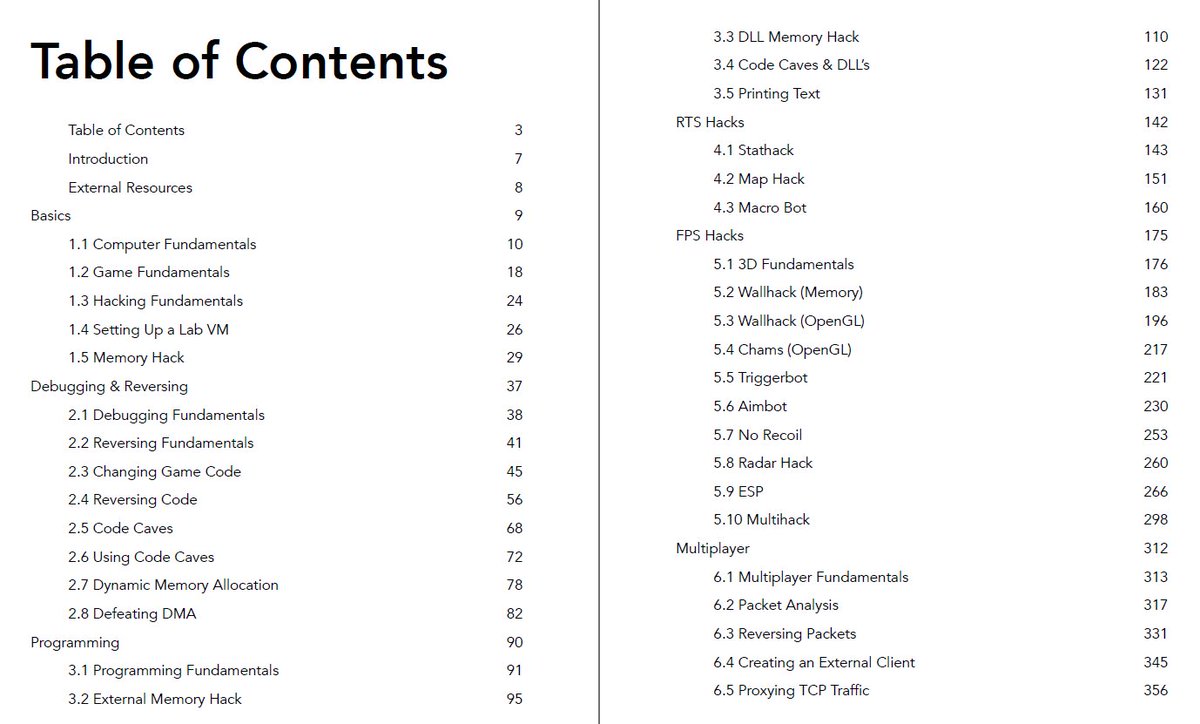
Nice to see a lot of new educational content on @GameHackingAcad 👏
They've got an interactive site (https://t.co/cayaqknVFb), but also a downloadable PDF 👇
This was extremely well written. As a red teamer if you want to bypass modern defenses like exchange online protection… just disable your phishlet for 5-8 mins after you send your email.. Then bring it back up ☠️
https://t.co/NjuYjuLHXg
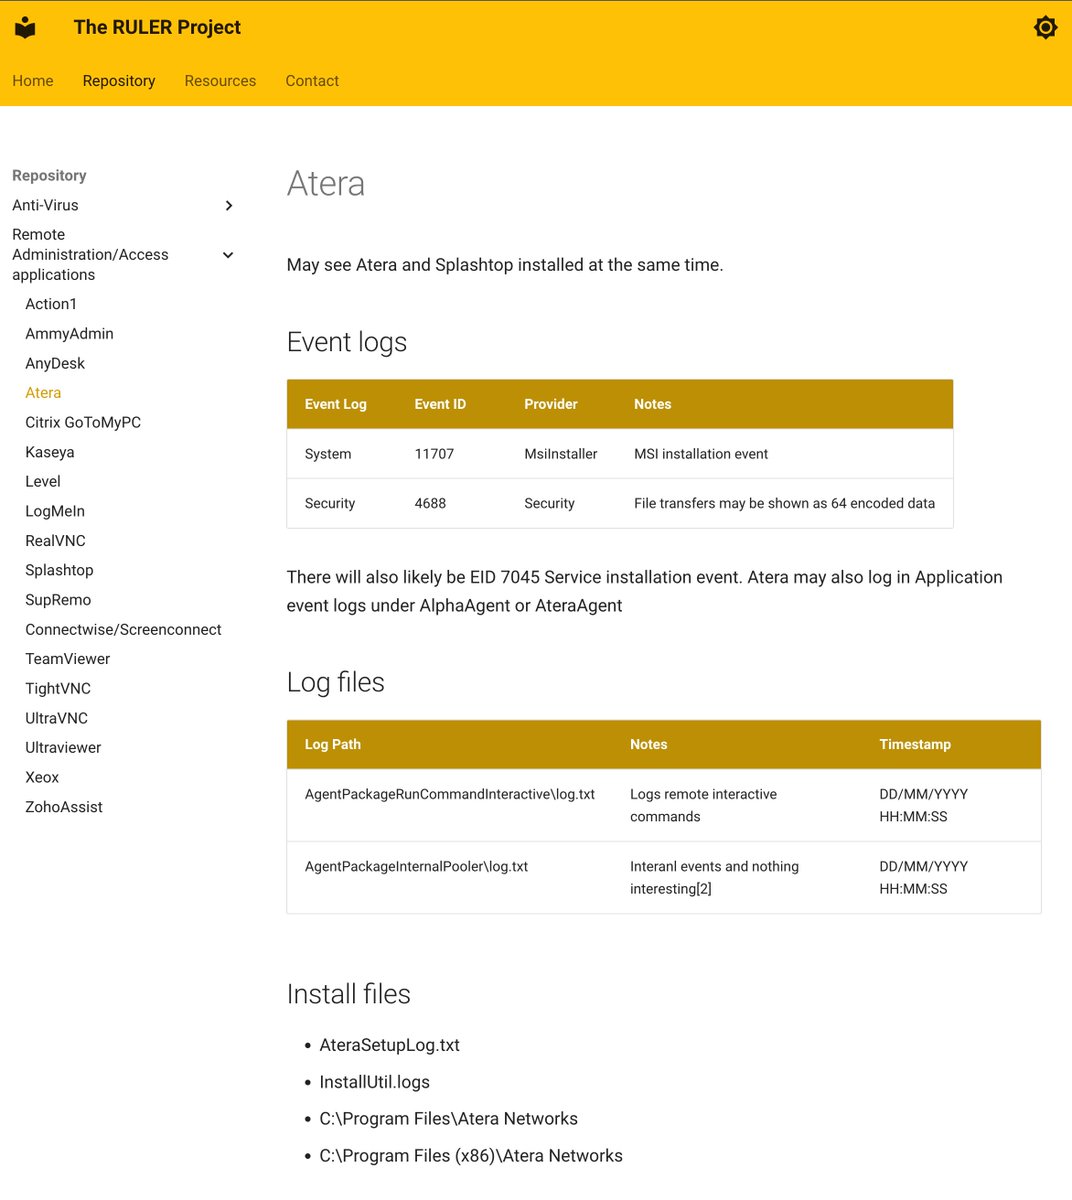
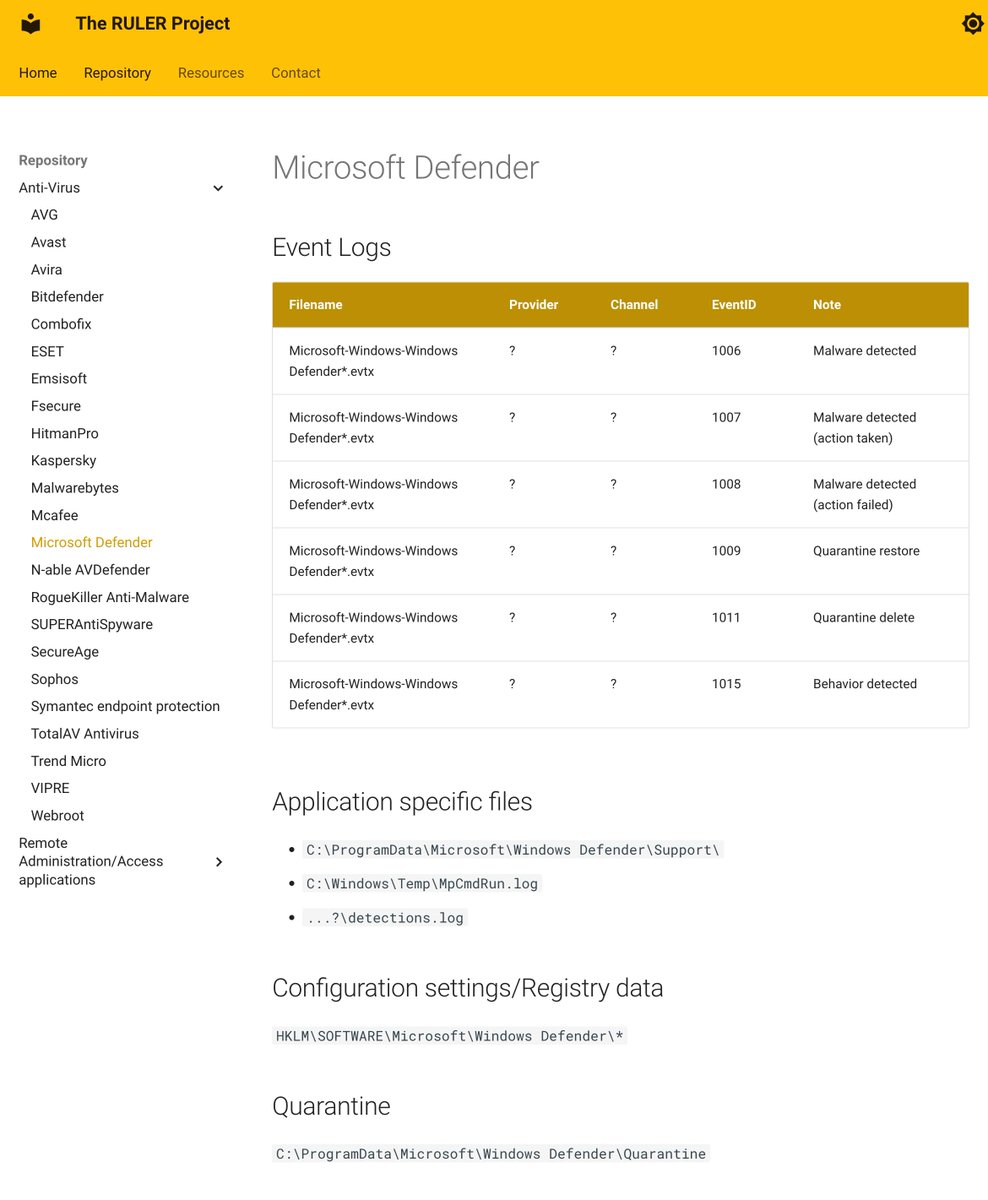
The RULER Project by @phillmoore is a centralized repository that curates and documents the types of logs and forensic details various applications generate by default to aid in digital investigations
A quick DFIR tip for the weekend
Now that notepad on Win 11 saves its states and can open tabs. It means history is saved somewhere :)
Well that somewhere is in %localappdata%\Packages\Microsoft.WindowsNotepad_8wekyb3d8bbwe\LocalState\TabState
A new location to monitor and check for unsaved files that might be used temporarily to copy things.
#dfir
#Microsoft#Sentinel incident responders, I have a bookmark for you ⤵️
My buddy @BertJanCyber
decided to go down the IR rabbit hole & write the best guide for endpoint incident response with some awesome #KQL queries.
Check out, further parts to follow.
https://t.co/JiS022ctcx
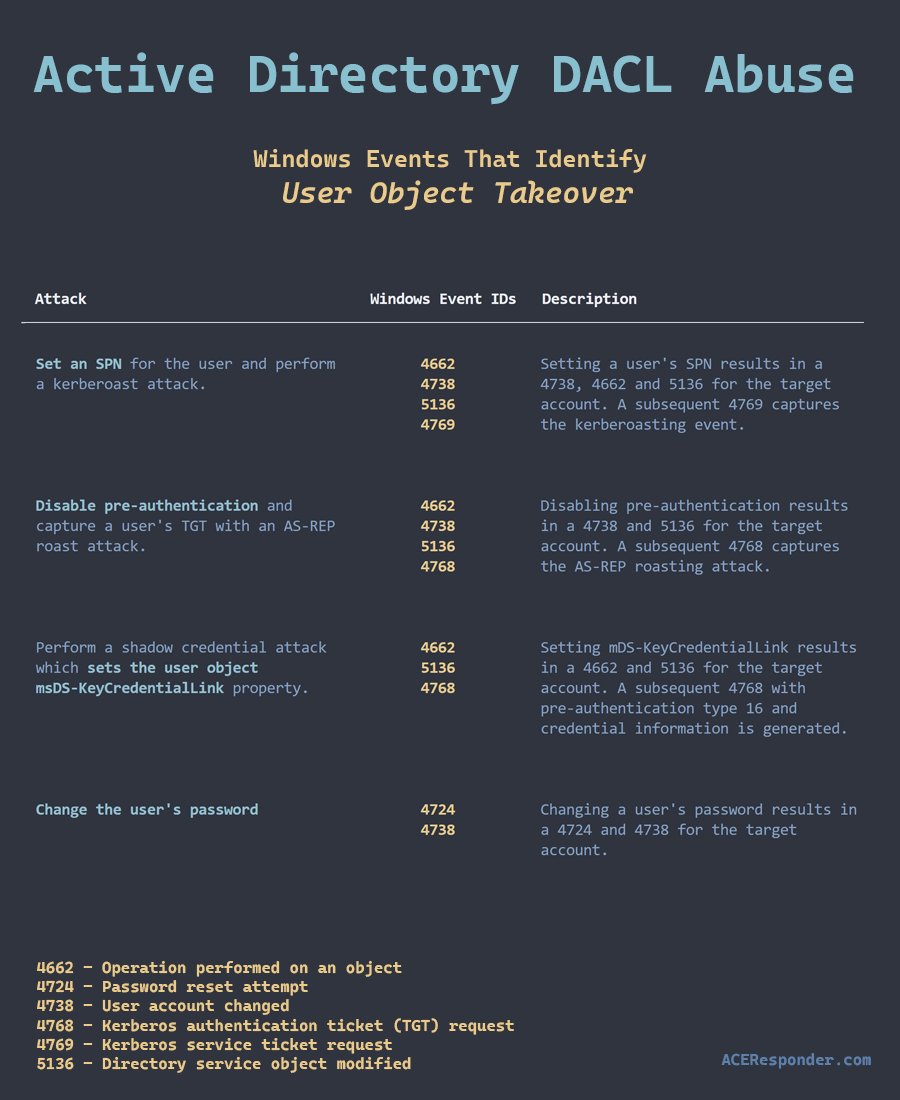
How AS-REP Roasting works. 🔐
This animation demonstrates the more secure Kerberos pre-auth and contrasts it with an AS-REP roasting attack which abuses the 'Do not require Kerberos preauthentication' setting.
#ThreatHunting#DFIR