$MOFU is live on pons.
CA: 0xf76593c1c321c2a2f77775025e9677999ce7ea8c
This is the only official contract. Before you do anything:
1. Check that the CA matches the one on https://t.co/UEpv8GHvly and in this pinned post
2. Only use the Pons link above, never one from a DM or a reply
3. Ignore anyone offering early access or support in your DMs
Thank you for being here. Back to building.
mofu-cli can now run on your own machine.
mofu --local
Uses Ollama, LM Studio or any OpenAI-compatible server. No API key, and your code never leaves your laptop.
mofu docs
Writes or updates your README from the code. Outline first, every change shown as a diff, and it only documents commands that actually exist.
mofu launch-kit
A clean fixed-supply token for Robinhood Chain: no owner, no mint, no blacklist, no fees. A Foundry project with tests and deploy steps, already checked by mofu audit.
npx mofu-cli --local
https://t.co/DPNkDzf1gC
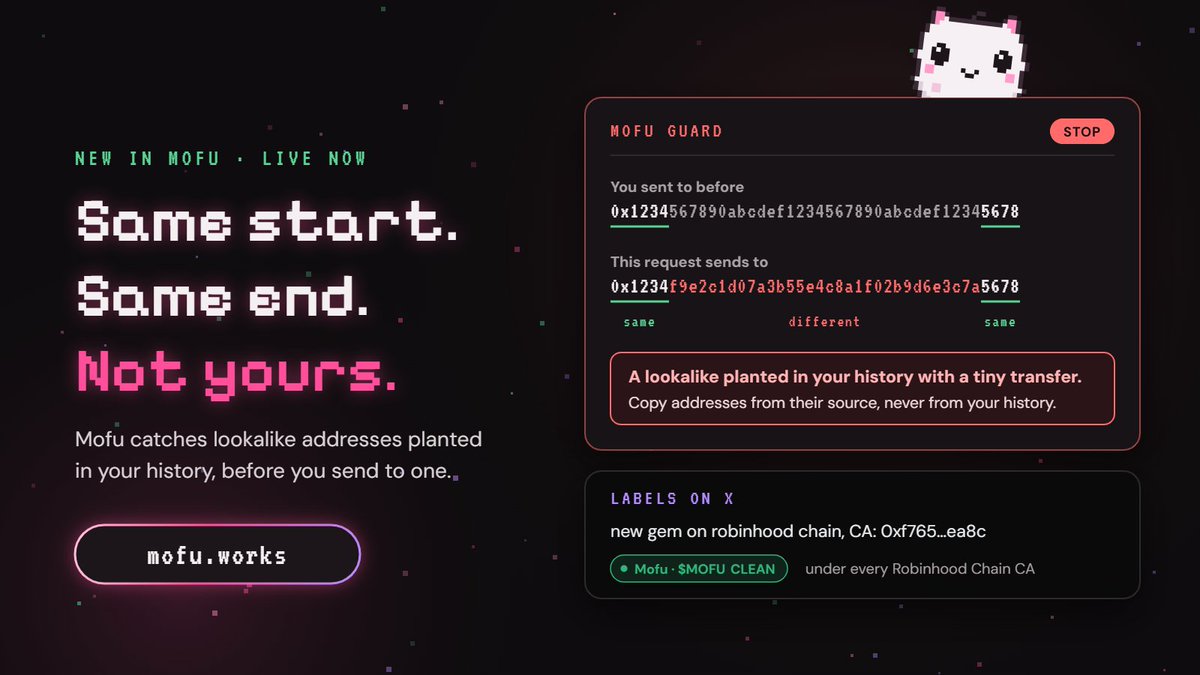
Same first characters. Same last characters. Not your address.
Scammers send you tiny transfers from addresses that start and end like one you use, hoping you copy the wrong one from your history next time.
Mofu now catches it:
- Wallet Health flags lookalike addresses planted in your recent history
- Mofu Guard stops a send to a lookalike of anyone you've sent to before, or of your own address, and shows both full addresses side by side
Also new in Mofu Guard: a small clean, caution or risky label under every Robinhood Chain contract address in posts on X.
Free. Guard never holds your keys and never signs anything.
https://t.co/j9ScpEExNr
Next up for Mofu:
1. Address poisoning alerts
Scammers send tiny transfers from addresses that start and end like yours, hoping you copy the wrong one. Mofu will flag them in Wallet Health, and Mofu Guard will stop you before you send to a lookalike.
2. Verdicts on X
Mofu Guard will put a small clean, caution or risky label next to every contract address on your X timeline.
3. mofu --local
Run the CLI on your own models with Ollama or LM Studio. No API key, and your code never leaves your machine.
4. mofu docs
README and docs written from your code. You see the diff first.
5. A safe token launch kit
A clean token contract with tests, checked by mofu audit before you deploy, plus the steps to renounce ownership.
6. Verdicts on-chain
Mofu's scan results published on Robinhood Chain, so wallets, DEXs and bots can read them directly.
https://t.co/UEpv8GHvly
Tests failing? mofu fix finds out why.
npx mofu-cli fix --run "npm test"
Mofu runs it, reads the failure, and tells you the root cause and the fix it proposes. Nothing changes until you say yes. Then it fixes it on its own branch, reruns the tests and commits. It won't weaken a test to make it pass.
mofu commit and mofu pr
The commit message and the pull request description, written from your changes. You read them first; git and gh run only after you approve.
In the browser and your AI app
Audit a Solidity contract or check a repo for leaked keys right on https://t.co/UEpv8GHvly, without your code leaving the browser. Or ask Claude or Cursor: scan_secrets and audit_solidity are on Mofu's MCP server.
https://t.co/DPNkDzf1gC
Next up for Mofu builders:
1. Secrets and contract checks in your AI app
Claude, Cursor or any MCP client will be able to ask Mofu to scan files for leaked keys and seed phrases, or check a Solidity contract. Plain code, no model on our side.
2. In the browser
Paste a contract to audit it right on https://t.co/UEpv8GHvly, without the code leaving your browser. Or paste a public GitHub repo and check it for leaked secrets.
3. mofu commit and mofu pr
Mofu writes the commit message or the pull request description from your changes. You read it, you approve it, then it runs.
4. mofu fix
Run mofu fix --run "npm test". Mofu reads what failed, finds the cause, fixes it on its own branch and runs the tests again. It asks before it touches a file.
https://t.co/UEpv8GHvly
mofu-cli now has tools for builders.
mofu secrets
Finds wallet private keys, seed phrases and API tokens in your files and your whole git history. A key you deleted last month is still in the history, and Mofu reads every commit. No AI, no API key, nothing leaves your machine.
mofu audit
Point it at a Solidity contract before you deploy and see what Mofu's Token Scanner will say once it's live: can the owner mint, block wallets, change fees without a cap. Plus common bugs like tx.origin and reentrancy, with line numbers.
mofu review
AI code review of your branch or pull request. Every comment is checked against the diff, so it only lands on lines that changed.
And a GitHub Action that runs it all on every PR.
npx mofu-cli secrets
https://t.co/DPNkDzf1gC
Next up for Mofu: tools for builders.
1. mofu secrets
Scans your repo and its whole git history for API keys, wallet private keys and seed phrases that slipped into a commit. One leaked key can empty a wallet. No AI, no API key.
2. mofu audit
Point it at a Solidity contract before you deploy and see what Mofu's Token Scanner will say once it's live: can the owner mint, block wallets, change taxes, swap the code. Plus common traps like tx.origin and unchecked calls.
3. mofu review
An AI code review of your branch or pull request: bugs, security holes and simpler ways to write it, line by line. Can post the comments straight to the PR.
4. Mofu in GitHub Actions
One workflow file runs the dependency check, the secret scan and the contract audit on every pull request and comments the results.
https://t.co/UEpv8GHvly
Mofu's token checks just got smarter.
Seen this code before?
Scammers redeploy the same honeypot under a new name and ticker. Mofu now fingerprints every contract's code and flags tokens built from the same code as a known honeypot, whatever they're called.
How deep can you sell?
When the sell test passes, Mofu now measures how big one sale can be before the price drops 10%. Simulated on the launch curve, nothing sent.
mofu-sdk
For agent builders: npm install mofu-sdk. Scan tokens, check wallets, verify webhooks, and gate every buy with a rule you can tune, including a minimum sell depth.
Free in the app, the CLI, MCP and the API.
https://t.co/UEpv8GGXw0
Next up for Mofu: smarter token checks.
1. Seen this code before
Scammers redeploy the same contract under a new name. Mofu will fingerprint the code of every token that turned out to be a honeypot or a rug, and flag new tokens built from the same code.
2. How deep can you sell
The sell test already tells you if you can sell. Next it tells you how much: how big a sell the liquidity can take before the price drops 10%.
3. mofu-sdk
A typed client for people building agents. Scan tokens, check wallets and manage webhooks in a few lines.
https://t.co/UEpv8GHvly
favorite line in the agent template:
if mofu can't be reached, the answer is no
an agent that buys while its safety check is down isn't checking anything
Mofu now works for agents.
In your terminal, no API key:
npx mofu-cli scan <token>
npx mofu-cli wallet <address>
Add --fail-on risky and a risky token stops your script.
In your trading agent: an open-source template that asks Mofu before every buy and refuses what it flags. The check lives inside buy(), so nothing can skip it. If Mofu can't be reached, the answer is no.
In your bot: webhooks that ping you when a token's owner moves, supply changes, code is upgraded, transfers pause, liquidity drops or the verdict flips.
Free. Docs at https://t.co/DPNkDzf1gC
Next up for Mofu: tools for people building agents.
1. Safety checks in the CLI
npx mofu-cli scan <token>
npx mofu-cli wallet <address>
Same scan as the web app, right in your terminal.
2. A safe trading agent template
A starter agent that asks Mofu before every buy and refuses anything flagged risk. Fork it, plug in your own strategy.
3. Webhooks
Register a URL, pick the tokens you care about, and get a ping when one changes: ownership moves, liquidity pulled, verdict flips.
If your agent trades on Robinhood Chain, it should check first.
ran my own wallet through mofu and found approvals i don't even remember giving
go check yours, it's free and you don't need to connect anything to look
$MOFU
https://t.co/aj6AF6efjp
Mofu now has a safety kit for Robinhood Chain.
Paste a wallet: see every approval it ever gave, which ones are risky, and revoke them in one click. The revoke is approve(spender, 0). Your tokens never move.
Paste a token: Mofu simulates a buy and a sell before you do. If you can't sell it, you'll know first.
Also new:
- the creator's other launches, and how many went quiet
- tokens copying another one's name or ticker
- known contracts named, not just 0x…
- a "Scanned by Mofu" badge projects can put on their site
Free, no wallet needed to check. Mofu never asks for your seed phrase, and the only transaction it ever offers is a revoke.
https://t.co/r2IzidQL4M
Next for Mofu: a safety kit for Robinhood Chain.
Building now:
- Approval Checker: see every token approval your wallet has given, which ones are risky, and revoke them in one click
- Sell Test: Mofu simulates a buy and a sell before you do, so a token that can't be sold shows up as one
- Deployer history: how many tokens the creator launched before, and how many are still alive
- Copycat alert: other tokens using the same name or ticker, and which one came first
- Wallet Health: one report for your wallet, with your tokens, their scans and your risky approvals
- Known contracts: routers, pools and launchpads named, not just 0x…
- Scanned by Mofu badge: projects can show their live scan on their own site
Mofu Guard stops a bad signature before you sign. This cleans up the ones you already did.
$MOFU holders voted on what comes next. This is the stuff that keeps wallets safe.
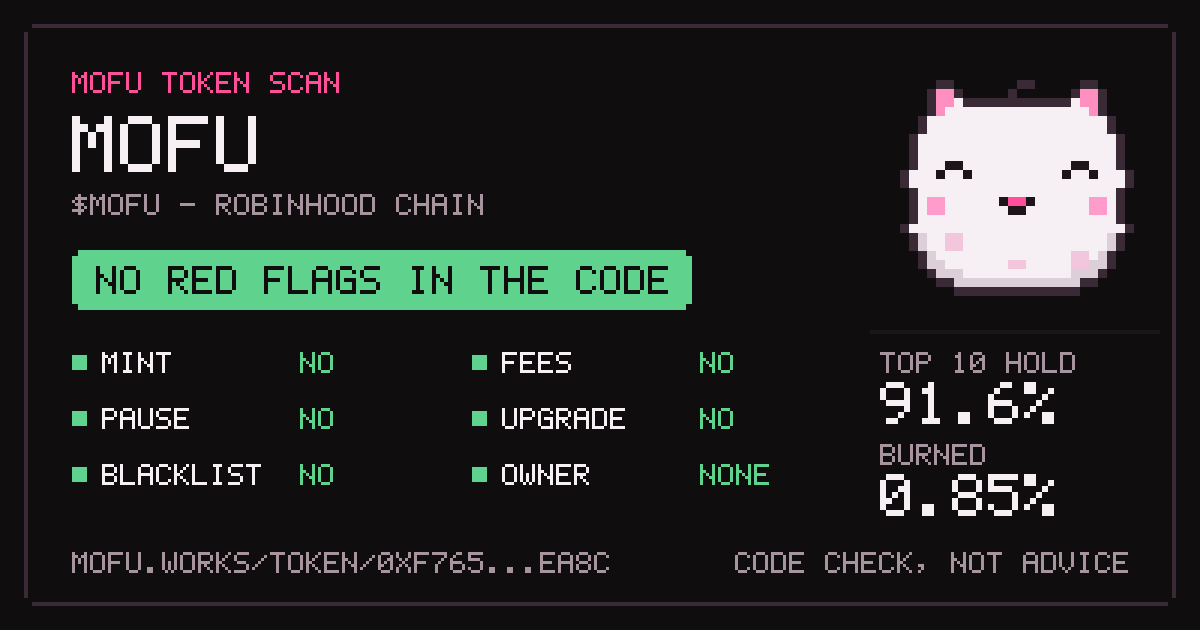
Every token on Robinhood Chain now has its own page on Mofu.
https://t.co/kihMlo38ZR + any contract address
What you get:
- what the code allows: mint, pause, blacklist, fees, upgrades, owner
- how much the top 10 wallets hold, and how much is burned
- a share card drawn for that token, ready to post
Scan a token in the app, hit Share, and the card shows up in your post. Anyone who clicks sees the same check you did.
No wallet needed. It reads the chain and tells you what the contract can do. You decide the rest.
$MOFU's own page:
https://t.co/Yc5hJTPXgS
Three new pages on https://t.co/UEpv8GHvly, all about trust.
Verify Mofu: https://t.co/GXtjwPucAq
The official $MOFU contract with a live scan, every official link, the exact message Mofu asks holders to sign, and the things Mofu will never do. If it isn't on that page, it isn't us.
Stats: https://t.co/XDYKTWNkMD
Real numbers, counted as things happen: messages, token scans, transactions explained, MCP calls, and how many risky signatures Mofu Guard has stopped. Plus holders and burned supply, read from Robinhood Chain.
Dev log: https://t.co/7pA3IDkAfx
Every update we've shipped, in one list.
Mofu Guard is here.
A free browser extension that checks what your wallet is about to sign, before you sign it.
When a site asks you to approve tokens, sign a permit or approve a whole NFT collection, Mofu Guard steps in first and shows what it really does, in plain English:
- Unlimited approvals: red warning
- Spender is a plain wallet, not an app: flagged as a likely drainer
- Permits, blind signatures and free-item orders: called out
- On Robinhood Chain, the token's contract is scanned too
Hover any contract address on any page to see its scan.
It never holds your keys, never signs and never sends anything. It only reads and warns.
Install it at https://t.co/j9ScpEExNr
Next big one: Mofu Guard.
A browser extension that checks what you're about to sign, before you sign it.
When your wallet asks you to approve or send something, Mofu Guard reads the request first and tells you in plain English what it does:
- Unlimited approvals get a red warning
- Approvals to a plain wallet instead of an app get flagged as a likely drainer
- Contracts that can mint, pause or block wallets get called out
It also labels token addresses on the pages you browse, so you can see a contract's scan without leaving the page.
It never holds your keys and never signs anything. It only reads and warns.
Building it now.