@V0iD_0daY@oluolatunjiabel My initial thought was to investigate the earliest critical-severity alert first. If it represents the starting point of a successful compromise, addressing it promptly could help prevent further damage and identify the attack's progression.
@oluolatunjiabel@V0iD_0daY If I am understanding what you mean, do you prioritize before investigation or investigation before prioritization?
Elaborate
@ireteeh Hi Dr. Iretioluwa, I'm a Cybersecurity graduate aspiring to work in SOC. I've completed several courses and TryHackMe SOC L1, but I'm struggling to land my first role. I'd appreciate a recommendation for any internship or entry-level SOC opportunity.
Free SOC lab simulation 👇🏽:
You can check out their free immersive solo labs here on : https://t.co/EzFbVnwnZH
And if you want EVEN more SOC training:
1. ☁️ Microsoft Cybersecurity Analyst Training: https://t.co/dBUMoLcCrY
2. 🤖 Splunk SIEM FREE Training Modules: https://t.co/QphIVF6xDs…
3. 💠 https://t.co/93GJZe0y4x Training Courses: https://t.co/V0mAxvsbCy
4. Cybersecurity and Cloud channel: https://t.co/Et8R7z3L3Q
📣 Know someone building a cyber portfolio? Send this to them.
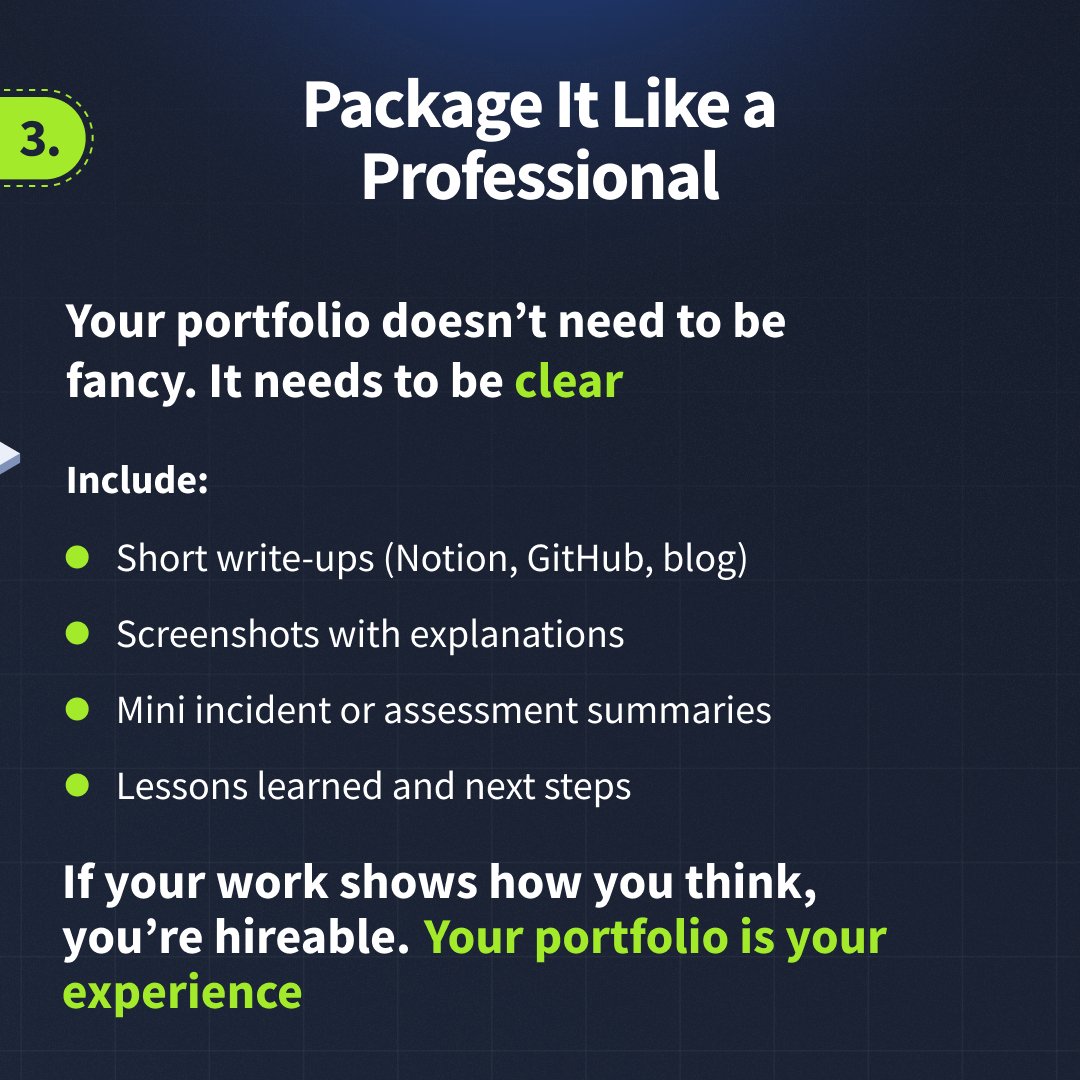
A cyber portfolio isn’t about what you’ve completed. It’s about what you can prove 🚀
Show how you think. Show your decisions. That’s what gets you hired 💼
👉 Build real, hands-on proof with TryHackMe https://t.co/dvD1sSwLEc
Cyber Security 101 (SEC1) certification is live! 🚀 a Hands-on certification built to show you actually understand the fundamentals. So stop saying you know the cyber fundamentals and start proving it.
And to launch it properly…🎁 We are giving away 500 FREE SEC1 certification attempts!
🔁 Share this post
📝 Fill in the form: https://t.co/uNaxplMD71
🏆 Get Certified
🖇️ Learn more about SEC1 here: https://t.co/hJYUyI4V9a
Sysmon is an incredibly powerful place that logs a wide range of activity types, providing a high level of visibility during analysis.
Using Sysmon logs, an analyst can observe a variety of activity types that provide deep visibility into system behaviour.
The image below illustrates how a SOAR solution can orchestrate tools, automate workflows, and enable faster, more consistent incident response across the security ecosystem.
SOAR (Security Orchestration, Automation, and Response) enables multiple security tools and technologies within an environment to work together in a coordinated way.
It automates repetitive SOC tasks, reducing manual effort and improving response time.
For example, when a SIEM generates an alert, a SOAR platform can automatically query VirusTotal for the source IP, enrich the alert with threat intelligence, and take predefined response actions, significantly reducing the SOC analyst’s workload.
HTTP/2 improves web performance by using a single connection with multiplexing and compressed headers, allowing multiple requests and responses to be handled in parallel, making websites faster, more efficient, and more reliable than HTTP/1.1.