Hands-On Hacking training course from Hacker House
- learn how attackers target and breach networks using real-world applied hacking techniques. Have you ever wanted to learn how to hack? Try our FREE sample module, crack a server & learn new skills https://t.co/SoEOv6Y6EK
picominer is a small BSD-3 C++ RandomX miner. A high-performance (XMR) mining implementation in C++ using RandomX algorithm. Optimized for modern CPUs and provides efficient mining via simple command-line interface. (src) https://t.co/euXbZayBJj - (docs) https://t.co/waqy2ML6zM
A high-performance Monero (XMR) mining implementation in C++ using the RandomX algorithm. This miner is optimized for modern CPUs and provides efficient mining capabilities with a simple command-line interface. (src) https://t.co/SDpfz3wNXU - (docs) https://t.co/zMVsOBNoGb #XMR
🚨Multiple remote OpenWrt 0days disclosed by Hacker House - pre-auth to full device compromise, command execution as root on millions of routers worldwide. Fixes shipping now. Here's how our inference-fuzzing methodology found them, via @TheHackersNews https://t.co/A20DfHKRz2
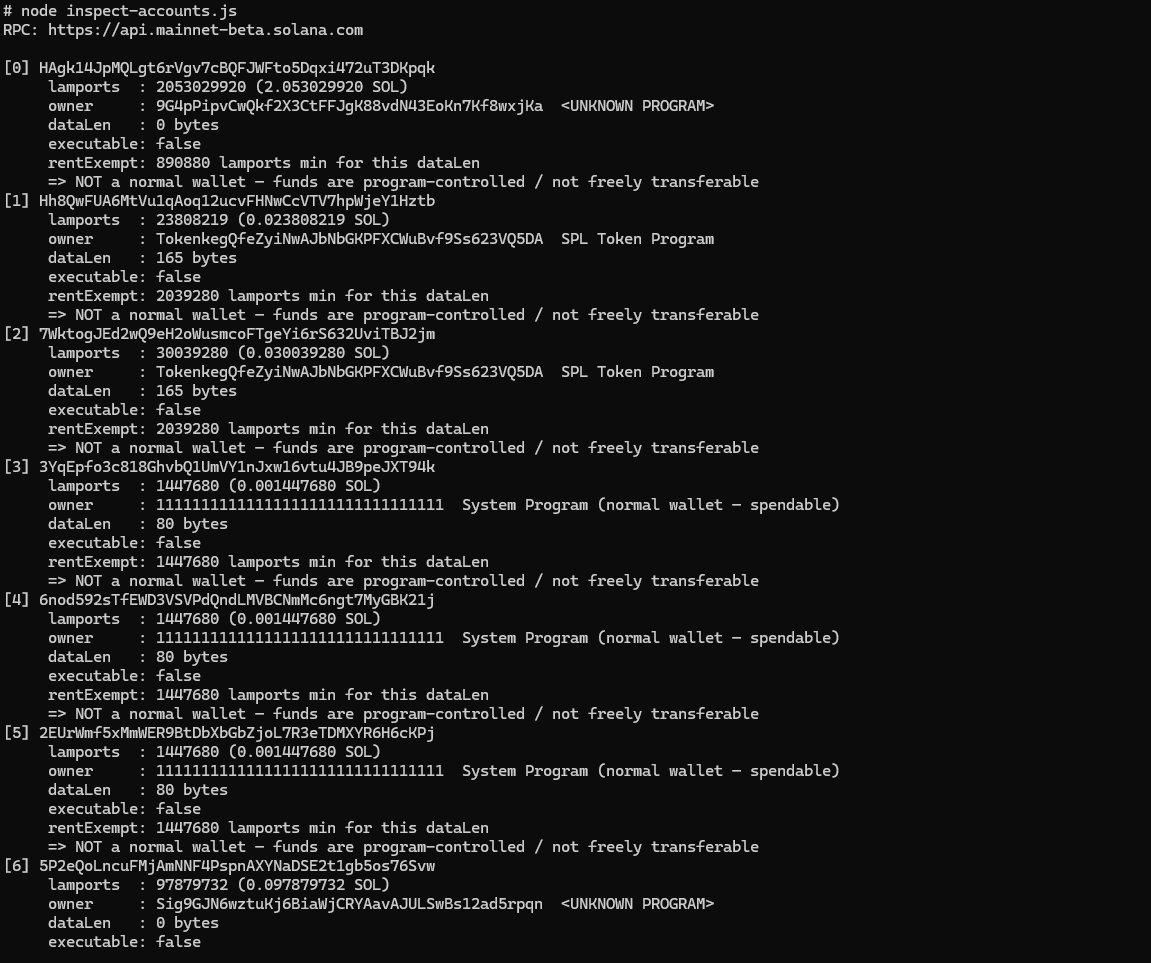
🚨PSA: If you attended the Crypto-Currency Village and completed the Badge project #defcon34. Dev firmware ships a *hardcoded* BIP39 seed. Everyone who flashes it derives *same* wallet secrets showing balances on mainnet. Never send real funds to any address from that seed.🔑
Rust Lang arraryref attack, for 90minutes impacted libsecp256k1, Blake/crypto libraries and solana-runtime. A critical supply chain attack that exposed 403 packages across the eco-system by attackers pursing core cryptocurrency developer supply chain. "cargo install" all it takes
The attacker packaged the stage2 kit in a password protected RAR file as PNG files alongside a Chrome Extension. The C2 uses a localhost port 80 communication to instruct components to automate credential theft and data exfiltration, living inside WebViews and Browser traffic.
Here is the complete attack chain executables being used by a suspected DPRK-nexus linked adversary, targeting Web3/DeFI users on Social Media incl. those who attended the Cryptocurrency Village during DEFCON34. Incl's IA ClickOnce manifests, stage1 DocSend dropper + stage2 kit.
An unauthorized Wi-Fi network appeared aboard Delta Flight 591 from Las Vegas to Atlanta on Aug. 10, prompting the crew to temporarily disable the aircraft's Wi-Fi. https://t.co/Fz54XSA1o6
🚨PSA #defcon34 - this user attempted a ClickOne malware delivery exploit and social engineering attack on me, relatively sophisticated. Be very cautious as blackhat's are actively targeting attendees with information stealers and wallet drainers.
Did you meet with @hackerfantastic - one of our founders at defcon? Are you in need of cyber-security solutions to deter attackers and reduce risk? Our team provides security audits that go deeper than anyone else. Contact the team to discuss your needs https://t.co/xN0AWYPqU5
If you attended #defcon34 and posted online about the cryptocurrency village, web3 or defi - you maybe being targeted by a sophisticated social media phishing operation by a DPRK-nexus linked adversary using nation state tradecraft. @hackerfantastic breaks it down here👇
🚨PSA #defcon34 - this user attempted a ClickOne malware delivery exploit and social engineering attack on me, relatively sophisticated. Be very cautious as blackhat's are actively targeting attendees with information stealers and wallet drainers.
Wow, not only spot a phishing attemp but does an incredible analysis.
Amazing as always @hackerfantastic
Worth the lecture for everyone, specially those in Defcon or BlackHat.
Be paranoid guys.