Ubuntu 26.10, codenamed StonkingStingray, is now available. This new Linux operating system release brings the latest updates for users. Check the announcement for details.
https://t.co/5V2uiaDgTe
#Linux#HomeLab
Breaking: PHP just flagged another unpatched REC vulnerability two days after emergency patches for the PHP2Shell flaws. It only hits rare session setups, and the team has posted urgent mitigation steps.
https://t.co/btHf9IcYmG
#HomeLab#Linux#SysAdmin
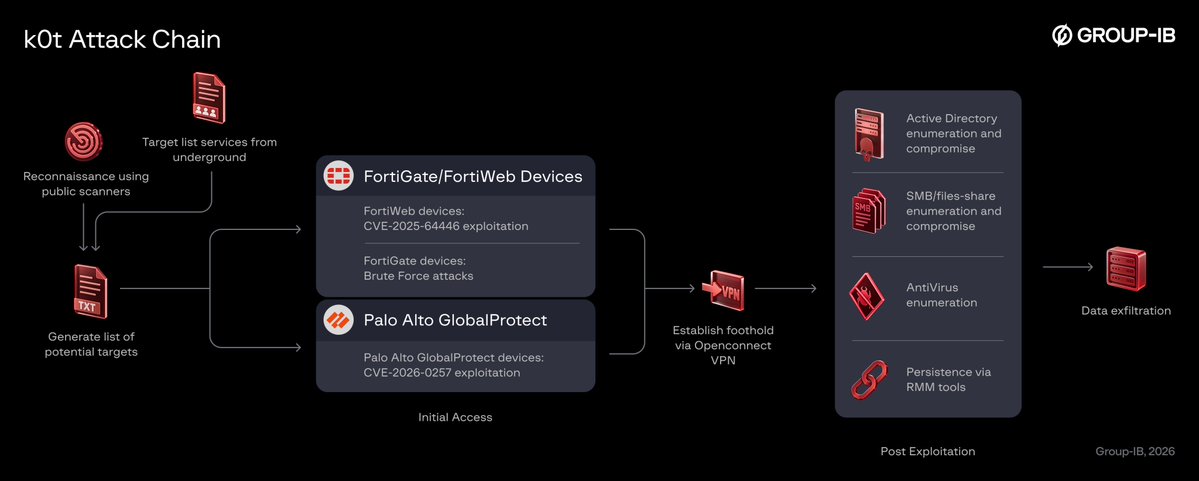
Hackers cracked Fortinet firewalls and VPNs in a k0t‑linked campaign, exposing more than 70,000 credentials. The breach lingered, letting attackers keep footholds and pull data from the network.
https://t.co/3aoMyvpXs4
#HomeLab#Linux#SysAdmin
🚨 MASSIVE ALERT: CISA just added MikroTik RouterOS zero-days to its Known Exploited vulnerabilities catalog.
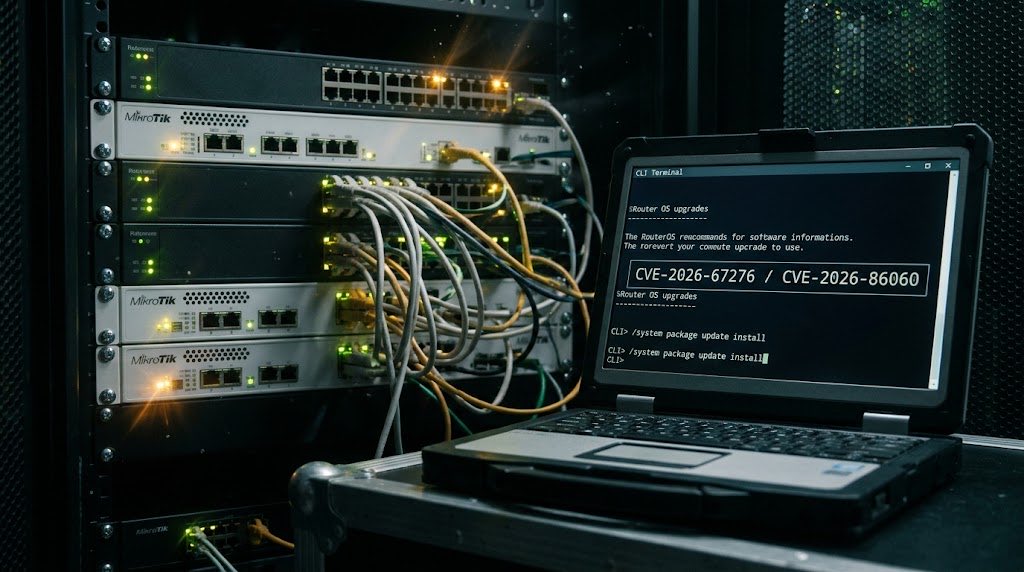
Active exploitation is happening NOW using CVE-2026-67276 (SSH Auth Bypass, CVSS 9.2) and CVE-2026-86060 (Privilege Escalation). Attackers are bypass-authenticating over SSH and escalating to full device takeover—zero trace, zero credentials needed.
If you have MikroTik routers with public-facing SSH or RouterOS containers running older versions, your entire infrastructure is at risk of lateral movement and traffic interception.
🛠️ Crucial defense steps today:
1. Upgrade to the latest RouterOS (7.24.2+ or 6.49.21+ depending on your branch).
2. Block SSH (port 22) on all WAN interfaces.
3. Change default ports, restrict /ip service access to trusted IPs only, or enforce VPN-only admin access.
Check your logs: any suspicious SSH login attempts or strange IP addresses accessing your RouterOS lately? Share your defense configs 👇
#MikroTik #RouterOS #Networking #CyberSecurity #SysAdmin
ℹ️ See details: https://t.co/dYWPlLgLqD
Critical Velocloud SQL flaw is being weaponized in the wild. CVE‑2026‑114625 scores a 9.9, letting read‑only accounts jump to full operator level, and Arista reports attacks are already happening. Keep an eye on your console.
https://t.co/HugGAd84UI
#HomeLab#Linux#SysAdmin
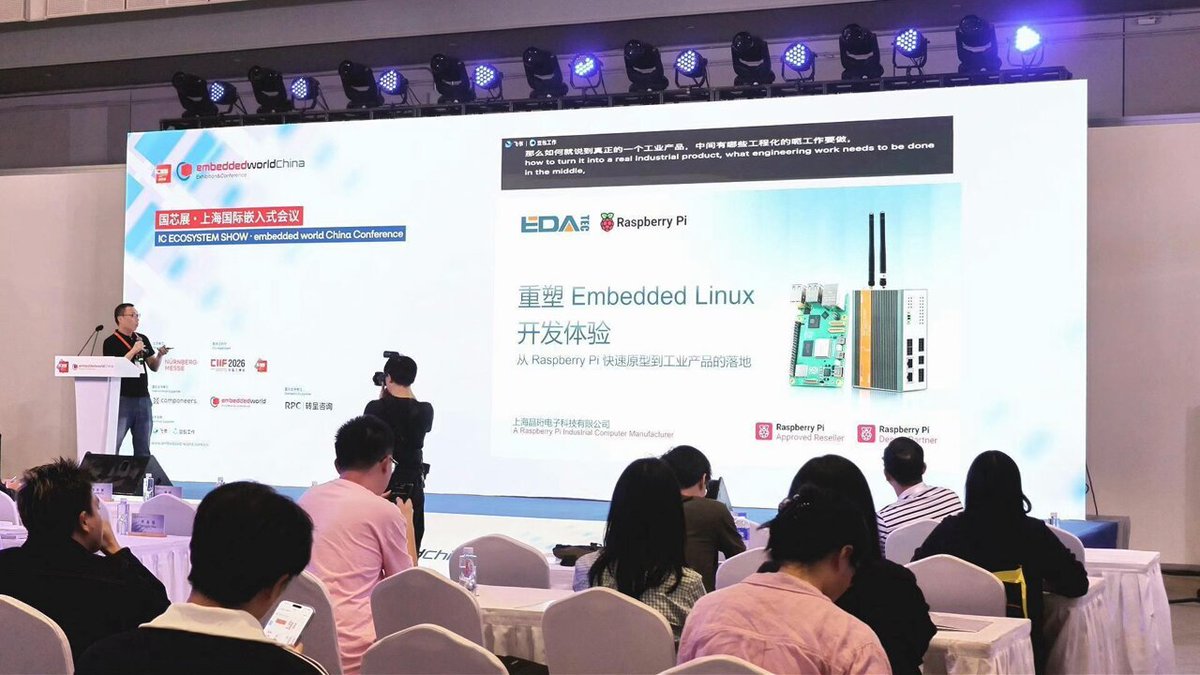
Edatec’s product director Paul Niu explains how a Raspberry Pi prototype can become an industrial computer. He highlights the technical hurdles of Embedded Linux and a building‑block kernel strategy that turns hobbyist code into a reliable operating system.
#Linux#RaspberryPi
Ubuntu just patched two critical PHP flaws that let anyone run code remotely on any PHP app. If you run PHP on your Linux server, update now before attackers exploit the unauthenticated RCE.
https://t.co/5GLTaX3RRg
#HomeLab#Linux#SysAdmin
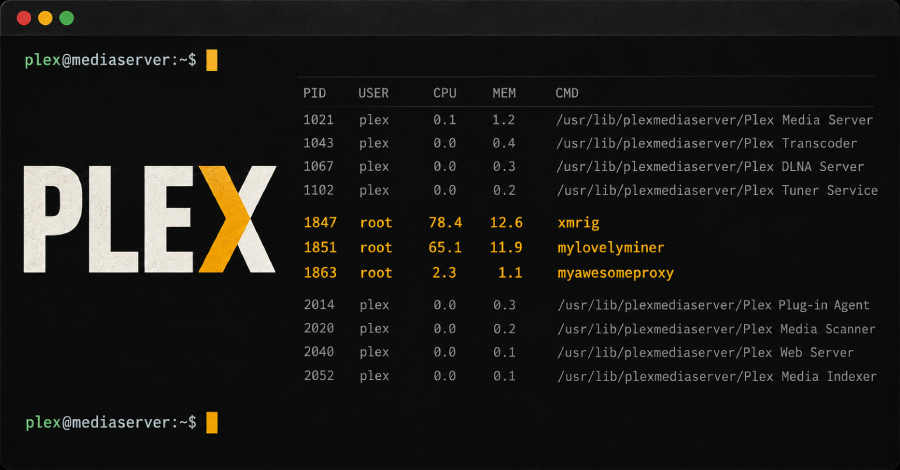
Hackers are turning Plex media servers into crypto‑miner farms by chaining four patched flaws. The Plex2Shell attack drops a Linux proxy backdoor on the operating system, so update to 1.43.3.10861 ASAP.
https://t.co/EJZ2PtdBVb
#Linux#HomeLab
Introducing a Raspberry Pi guide that turns the tiny board into a retro gaming hub. It walks you from a quick‑start handheld build to wiring old CRTs and even coding a BASIC game on a computer.
https://t.co/80su0AfFlj
#RaspberryPi#HomeLab
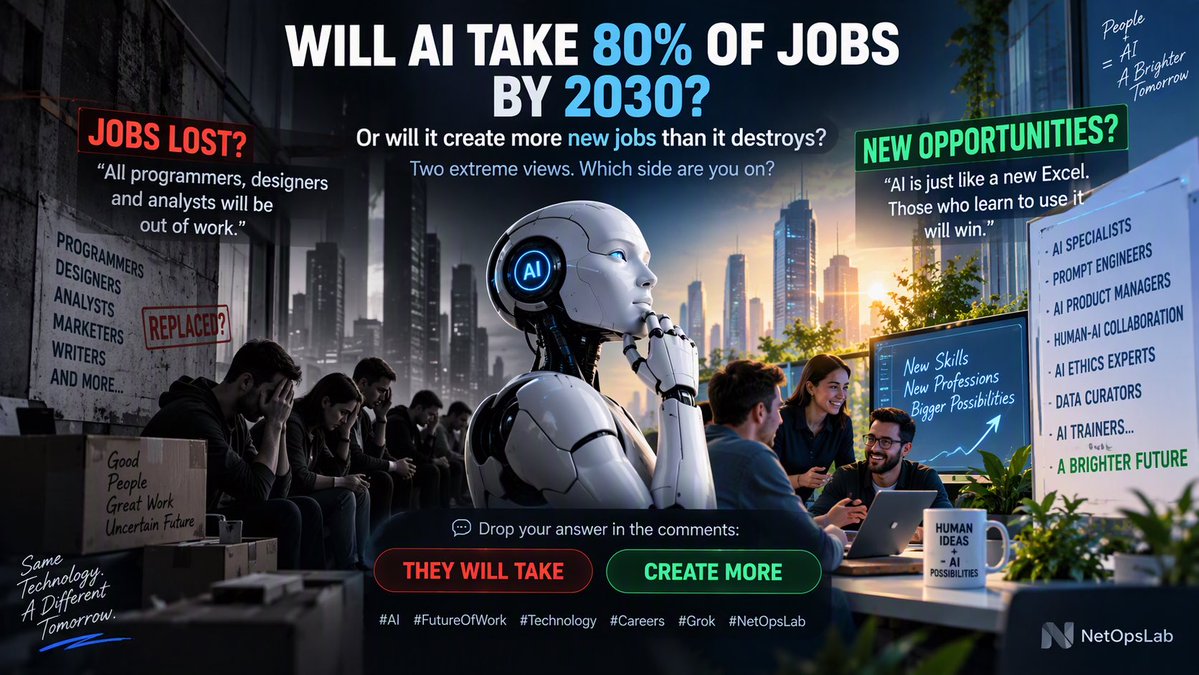
Will AI take away 80% of jobs by 2030?Or will it create more jobs than it destroys?I keep seeing two extreme camps:�� "Programmers, designers, analysts... everyone will be replaced."🟢 "AI is just the new Excel. The people who learn to use it will have a huge advantage."Personally, I think the truth is probably somewhere in between.What do you think?Comment:"Take jobs" or "Create more"
#AI #ArtificialIntelligence #FutureOfWork #AIJobs #CareerGrowth #Technology #Automation #MachineLearning #DigitalTransformation #Innovation #Grok #NetOpsLab
Malware can hide inside legitimate FortiOS processes and slip past security on VPNs that use a special tag. Attackers dropped the PEERSTITCH implant after breaching FortiManager, turning trusted firmware into a delivery vehicle.
https://t.co/87fspsT62e
#HomeLab#Linux#SysAdmin
Why waste space on a network rack when you can use the back of your TV? 😎
I 3D-printed a modular mounting system using the IKEA-style pegboard concept to mount my network gear behind the TV.
Routers, mini PCs, power supplies, cables — all organized and hidden out of sight.
Custom-fit. Modular. Easy to modify.
The best part? I can print new mounts whenever my setup changes.
Would you use a 3D-printed mounting system for your home network?
#3DPrinting #HomeLab #CableManagement #DIY
Agents, Harbor and Docker together stop clever scripts from gaming their own evaluations. Each eval runs in a microVM container with network policies, keeping runs fair and reproducible.
https://t.co/IvZBzIyttQ
#HomeLab#Linux#SysAdmin
Ubuntu’s Stonking Stingray rolls out on‑device speech‑to‑text with a tiny LLM, putting AI straight into your hands. It also brings Rust‑based coreutils and TPM‑backed full‑disk encryption to the Linux experience.
https://t.co/5V2uiaDgTe
#HomeLab#Linux#SysAdmin
Cloudflare Pages and Infoblox have uncovered over 20,000 domains tied to a long‑running tech‑support scam. The Help TDS network, linked to Hotejka, serves bogus Windows security pop‑ups that funnel users to scam call centers.
https://t.co/kaDzuWzqLm
#HomeLab#Linux#SysAdmin
Alert: Next.js just dropped an out‑of‑band patch for two unauthenticated RCE bugs and a high‑severity DoS. One flaw abuses the RSC cache, the other hits librsvg through sharp. Keep your framework up to date.
https://t.co/FPoCgVPwM0
#HomeLab#Linux#SysAdmin
Even a CFO voice can be a deepfake asking for MFA codes, and 62% of security leaders saw one last year. Run a safe tabletop drill with a fake wire transfer or admin request to teach your team the difference.
https://t.co/sHCoZYyo8p
#NetworkSecurity#HomeLab
cert in released a vulnerability note on its site about a rekey bypass in MikroTik RouterOS. The flaw lets an attacker trick the SSH pre‑authentication state on the router. If you run this firmware, update it right away.
https://t.co/hHPtZ7rgSl
#MikroTik#RouterOS