PSA: To all companies. If you send me an email and I can't respond to it because you made it a Do Not Reply then take me out of your systems and cancel any service I have with you.
It is with joy and proud the RFID hacking community see three new modes dedicated to RFID made the cut to Hashcat v8.0 thanks to the efforts of Antiklesys.
We also want to express a special thanks to @chick3nman 🙏🏻🙏🏻🙏🏻
My old wish from 2019 has been fulfilled. I can retire. 😂
If you've ever wondered why smart TVs are so cheap, this is why.
@log4j rooted his Samsung and found an always-on hot mic, automatic content recognition, geolocation, network mapping, ad targeting and user profiling, shared with Samsung's "400 partners".
A lot of it can be blocked in <15 min, wrote a basic guide below.
What your TV is doing
The main culprit is ACR (automatic content recognition). Your TV screenshots what's on screen, fingerprints it, and sends it home to build your ad profile. Samsung does it every 500ms, LG every 10ms [1].
What is insane: it happens on connected devices too.
Plug in your laptop, your console, your work machine, and your TV can fingerprint that via HDMI [1].
He also found that if your Samsung doesn't have a mic, it'll look for one from a connected soundbar or bluetooth device.
https://t.co/vNdTnIQ6KF
It's on by default, and you likely agreed to it on the setup screen you clicked through in 10 seconds.
Step 1: Turn off ACR
Samsung: Terms & Privacy → Viewing Information Services
LG: Live Plus
Vizio: Viewing Data
Roku: "Use info from TV inputs"
Sony/Google TV: Samba Interactive TV
Menus vary by model, but those are the names to look for. While you're in there, opt out of interest-based ads, reset your advertising ID, decline every optional privacy agreement, turn off voice recognition, and delete apps you never open.
Step 2: Give smart devices their own network
Put the TV, cameras, speakers and vacuum on your router's guest/IoT network. The logic is simple: these devices rarely get patched. If one gets compromised (getting drastically more frequent with AI), it shouldn't be able to see your other devices or home network.
Step 3: Block trackers for the whole house with DNS-level filtering
NextDNS (cloud-based) is easy and has a solid free plan. Pi-hole is a little bit more work if you prefer self hosting. For simplicity we'll focus on the former.
1. Sign up at https://t.co/IwhafVWVM8 (free tier is plenty)
2. Privacy tab: add a blocklist (OISD is a good bet) and turn on Native Tracking Protection for Samsung, LG, Roku, Amazon (see attached image)
3. Setup tab: copy your endpoint
4. Paste it into your router's DNS settings as DNS-over-HTTPS/TLS (or use the IPs + "Link IP" if your router only does plain DNS)
5. Bonus: block outbound port 53 except to your router. Some devices hardcode their own DNS to get around you
Then open the NextDNS logs and watch how often your TV phones home. It's eye-opening. If an app or update breaks, find the domain in the logs and allowlist it.
Why they do this
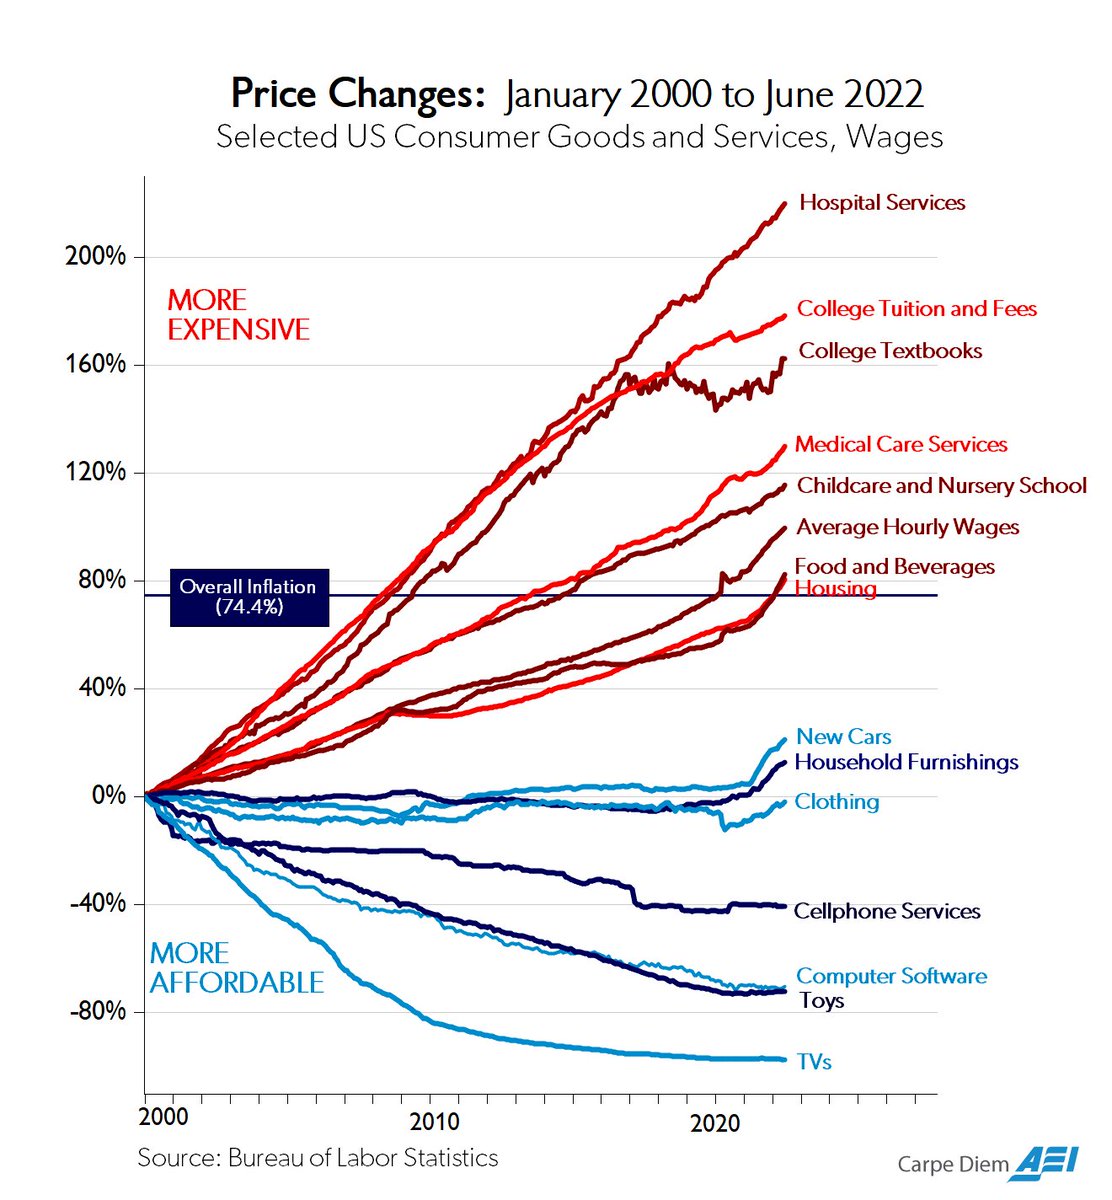
TV prices are down 97% since 2000 [2]. Most of that is better manufacturing and brutal competition. But once margins on the hardware hit zero, the cost moved to you.
In Q3 2024, Vizio lost $6.7M selling TVs and made $115.8M in gross profit from ads and viewing data [3]. They've said on earnings calls that they keep TV prices low to grow the audience they sell to advertisers. Walmart bought them in 2024.
This isn't a conspiracy theory either. Vizio paid $2.2M to the FTC in 2017 for tracking 11 million TVs without consent. Last December, Texas sued Samsung, LG, Sony, Hisense and TCL over ACR. Samsung and LG have since agreed to stop collecting that data without explicit consent [4].
TL;DR
1. ACR off
2. Ads + voice off
3. Smart devices on their own network
4. NextDNS filtering on the router
Sources:
[1] ACR study: https://t.co/S1IS8lXNbA
[2] Cost of US consumer goods: https://t.co/nclXELXcbd
[3] Vizio Q3 2024: https://t.co/CrVbwc9ZXk
[4] Texas v. Samsung: https://t.co/wFOUdeh1if
‼️ A bug bounty hunter says they rooted their 2025 Samsung TV with zero-days and found an AI model tracking what they watch and the ads they skip.
The TV also takes screenshots, categorises audio and can tap a soundbar's mic, they say.
Then OpenAI banned them for "Cyber Abuse".
El historial de versiones del documento. 214 revisiones. Cuatro horas y media de escritura repartidas en tres días, con sus borrados, sus frases a medias y sus pausas.
El profesor lo miró y me dijo que el sistema de detección es muy fiable.
Le pregunté qué margen de error tiene. No lo sabía.
Le pregunté quién había validado ese 97 %. Tampoco.
No denuncié a nadie. Presenté la revisión de la calificación por escrito y adjunté el historial.
Se la corrigieron a la semana siguiente.
Lo que me preocupa no es el cero. Es que a mi hija le dijeron delante de la clase que había hecho trampas, y la prueba de que no era así la tenía yo en una pestaña del navegador.
Están usando una máquina para acusar a adolescentes sin saber cómo funciona la máquina.
🚨 OUTRAGE: A man literally BEHEADED the historic Iwo Jima monument with a sledgehammer at Quantico. Hundreds of thousands in damage to honor our brave Marines! Is he here illegally? DEPORT HIM! The left attacks our history while we honor our heroes. Throw the book at him! 🇺🇸🔥
WTF, $3000 Samsung TV has an always-on mic, automatic content recognition, geo tracking, network mapping, and ships your data to Samsung + 400 partners.
Bro Rooted a brand-new 2025 Samsung TV after noticing absurdly targeted ads.
Firmware was locked down, so zero-days it was.
Got a root shell.
then found: always-on voice service, ACR, geo, full telemetry pipeline, and four separate DRM systems.
This isn’t a bug, It’s the product bro.
‼️ BREAKING: Trend Micro posted several unpatched Linux kernel flaws to public mailing lists.
Two are critical remote code execution bugs in the kernel's SMB server, and one includes proof-of-concept code.
Linux maintainer Greg told them to "fix your submission process."
Removed all of the samsung spyware from my TV with Codex (Claude refused to root the tv lol)
It's insane how much bloat samsung packs into their TVs to track you and sell your data. Here's just some of what I turned off that made my tv 3x faster:
- screenshot your screen a few times a second to see what you're streaming and fingerprint you to sell your data
- reading your hdmi inputs to do the same thing while you have a game console plugged in
- Voice assistants: Bixby wake-word detectors listening and tracking what you say in your house
Before and after speed of my TV:
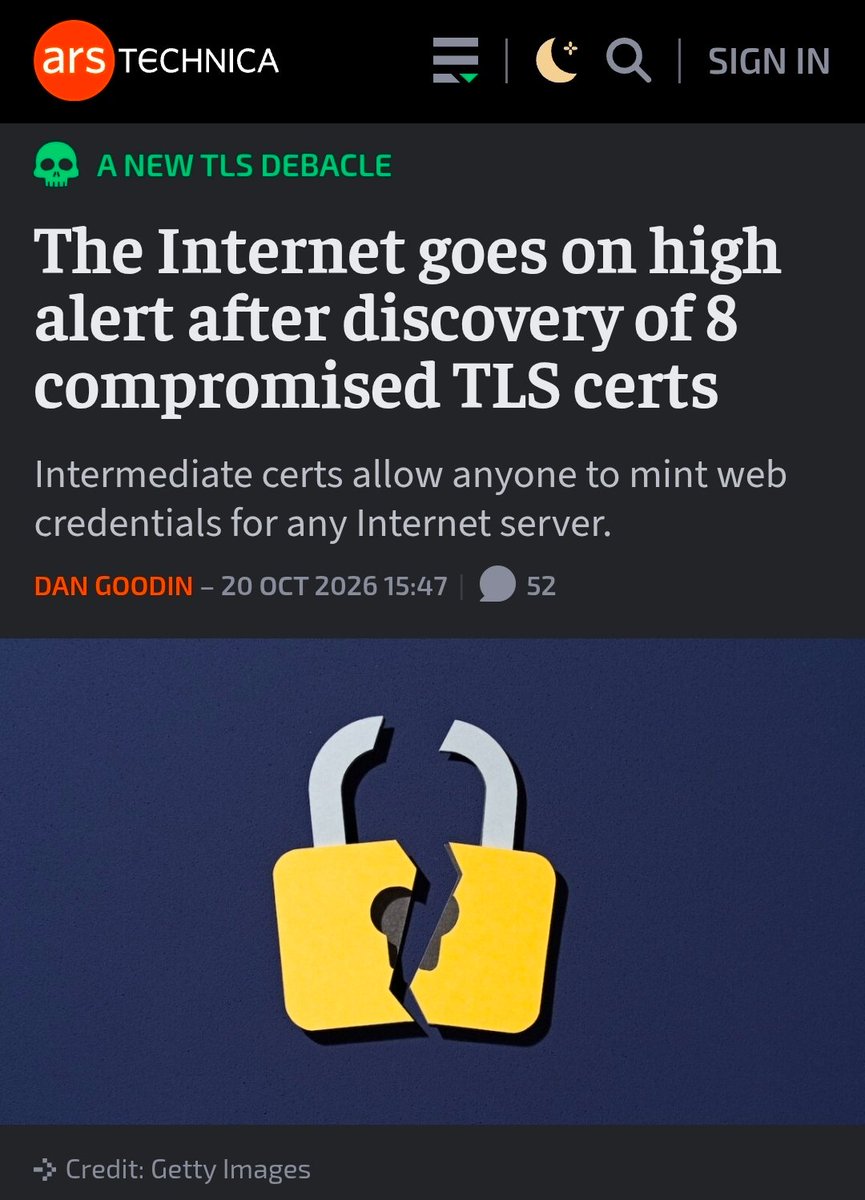
Internet encryption is currently having a nuclear meltdown.
Cryptographers are calling it "bigger than Heartbleed."
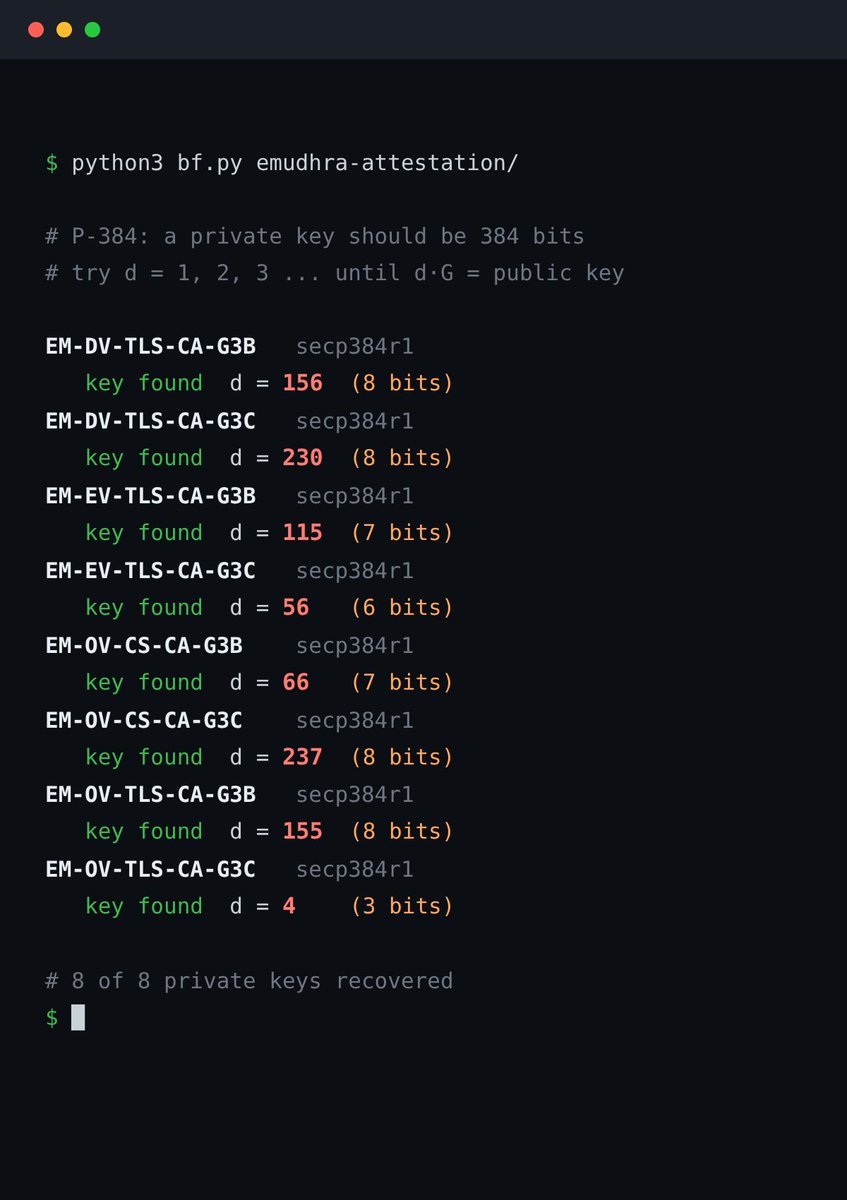
A global Certificate Authority just leaked 8 master private keys that allow anyone to impersonate any server on Earth (Google, banks, government sites).
A normal master key has 116 digits of entropy.
The actual leaked keys?
4. 56. 66. 115.
A toddler on a calculator could have cracked them.
While browsers patched it today, millions of IoT devices, Linux servers, and Docker containers will take years to clean up.
We bet global digital security on centralized human gatekeepers who forgot to check their math.
True security can't rely on trust cartels. It has to be governed by mathematical consensus.
See the signal. ♾️
‼️ BREAKING: Two leaked remote code execution flaws in PHP are real, watchTowr confirms.
PHP will ship fixes for two critical flaws, both rated CVSS 9.2, on Wednesday 21 October at 14:00 UTC, a day before the embargo was due to lift.
CVE-2026-109618 and CVE-2026-109619 first surfaced in a Hacker News post whose author admitted having no evidence beyond "source: trust me, bro".
Kevin Beaumont flagged the leak, and watchTowr confirmed it two hours later.
PHP says it may release sooner if details go public or exploitation appears. It has not named the CVEs or the affected versions.
> wake up
> take a shit
> get out of bed
> check beep boop
> everyone saying ooga booga PHP
> wtf why
> look inside
> ultra mega fuck off exploit coming
> php2shell
> so bad PHP devs begs nerds to patch tomorrow
> proof of concept video released
> pwn website easily
> video has dancing anime lady?
> nobody explains why dancing anime lady
> no one even asks why proof of concept has dancing anime lady
> ok
> cybersecurity nerds bamboozled
> some saying will be up there with Log4J in severity
> goopocalypse
pic unrelated
‼️ BREAKING: The private keys of 8 certificates from Indian certificate authority eMudhra were compromised, Mozilla says. Firefox blocked them within 3 hours.
Each key should be a 116-digit number, but one was just 4.
Anyone can guess them and forge HTTPS certs for any website.
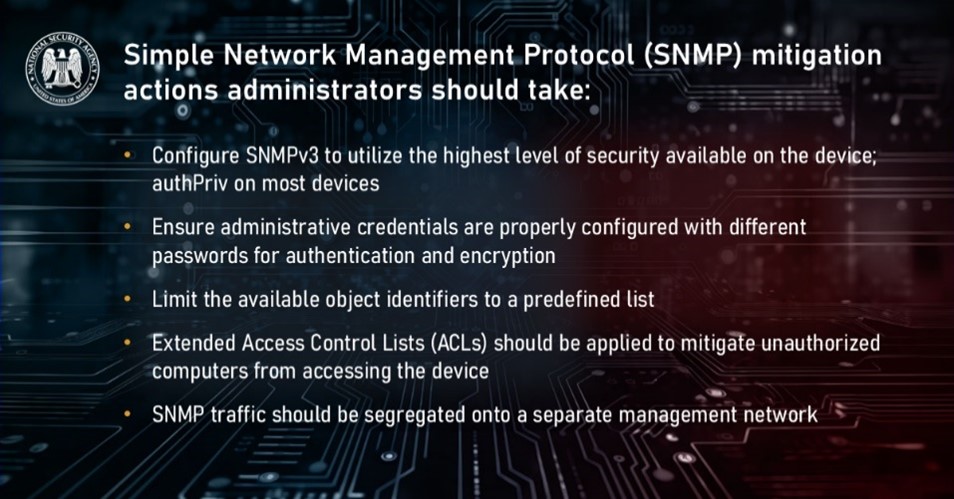
Stop Russian compromise of your network devices by hardening your SNMP. We urge NSS and DIB admins to move to SNMPv3 immediately to ensure payloads are authenticated and encrypted. Full hardening guidance here: https://t.co/dDj8IwwR3R
In Memory of Randolph “Randy” Mantooth
Randy Goes on one last run with his lifelong friend and co-star Kevin Tighe inside Squad 51.
On October 17th, a Flag Ceremony was held at Station 127 (Station 51) as Randy left the station for the last time.
Rest easy, Johnny.
📷:Los Angeles County Fire Museum