The security paradigm has significantly changed.
Moral panic and influencers won’t protect you. DYOR.
infosec will get a LOT worse before it gets better.
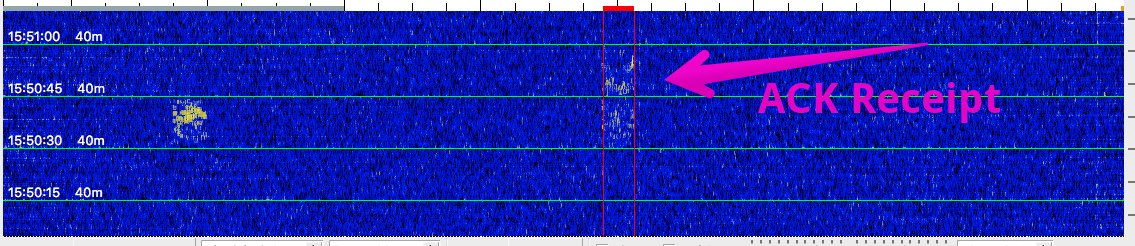
BAM! #Bitcoin sent over 7.077Mhz via #JS8Call to @SamuelPatt
Sweep: https://t.co/mLGREGXXN0
Toronto,CAN => Michigan,USA [40W:#SnowStorm]
Bcuz its a brainwallet made ahead of time, with bearer pk I don't require internet to broadcast this transaction at the time i'm sending
The only way out is through.
They're calling it the Bugpocalypse. LLMs are being used to find long-hidden cracks in the software infrastructure, and it's happening at a furious rate. 3% of all compromises in computing history happened in the last week, claims one source? I believe it.
There are people saying public access to the frontier models ought to be locked out, or heavily guardrailed, over this. The problem with that idea can be summed up in one sentence: when lockpicks are outlawed, only outlaws will have lockpicks.
The lockpicks will be Chinese open-weight models, if nothing else. There's no way to stop those from becoming ubiquitous.
There are two futures in front of us. One in which only the bad guys have lockpicks, and security holes go undiscovered until they're exploited. Another in which everybody has lockpicks and is aggressively red-teaming their own software so it gets fixed before the holes are exploited.
The corpus of human code is huge but finite. The number of defects in it has to be finite too. We can fix those defects now; we have a million friendly robots to do it with.
The only way out is through.
PSA: This week was kind of a turning point for AI and cybersecurity. Please take this weekend to do some simple cleanup for your family. Some suggestions:
- Set up a password manager like 1Password and give your spouse or partner access to a shared vault. Teach them how to use it.
- Update your passwords for critical stuff - your email account, your bank or financial stuff, etc. Store in your password manager and use the strongest password you can.
- Use two factor auth for everything you can. SMS is not ideal although better than nothing. Google Authenticator or a passkey is better. Hardware key is safest.)
- Add a sim pin to your phone. Makes it harder to sim jack.
- Update your phone and your computer to the newest releases. Turn auto-updates on.
- Freeze your credit - takes 5 minutes.
- Get an IRS Identity Protection PIN.
- If you’re using claude code or have AI agents that browse the web, they’re probably using Node.js. It’s also vulnerable. Update claude code, update node on your machine.
- If you’re building stuff on your computer, ask claude or grokbot (which is connected to twitter and likely has the most current info) to audit any of your repos for vulnerabilities. Ask grok to make it a scheduled task so it can do this daily - things are moving very quickly in the space right now.
- Consider some light resiliency stuff. This probably sounds silly, but it sounded silly at the beginning of covid too. Having printed out copies of important stuff - especially financial accounts. Having some cash on hand. Having some shelf-stable food and clean water or a water filter. Having a map. Having a generator that can at least power your fridge or some devices. Cheap insurance.
Again, I don’t want to alarm people, but I was taught that you should have a Secure plan, a Comfortable plan, and a Wealthy plan. And it seems pretty clear the secure plan needs to now factor cybersecurity risk as a legit threat. Take a weekend and shore yourself up.
🚨 LiteLLM reveals the root cause of its supply chain attack.
A master key leaked on GitHub in May was never revoked, allowing attackers to access its Agent Platform, steal a GitHub owner token, and publish a malicious PyPI release in October.
Read: https://t.co/KfE5QuX1Zs
New release: Electrum 4.8.3. This release fixes a critical security issue, so we urge all users to upgrade. A description of the vulnerability will be published later today. (note: Windows Defender may show a warning about ZXing.dll, ignore that, it is a false positive)
Emergency update to the Cloudflare Managed Ruleset on 2026-10-22 refines metadata for 7 rules targeting CVE-2026-109618 and CVE-2026-109619. Detection logic and block actions remain unchanged.
https://t.co/GuwGtO7EVt
BREAKING: OpenAI says it found a critical flaw in Brotli, a widely used compression library built into software like Node.js, Bun and Envoy.
The bug could let an attacker take over a system just by sending it malicious compressed data, with no login needed. That works both ways: a hacker could hijack an unpatched server, or a malicious server could hijack an unpatched user’s device.
The FBI continues to warn about two critical security flaws in PHP, a programming language used to build many websites and online services. Attackers could exploit these vulnerabilities to break into systems, putting sensitive information and business operations at risk. Security updates are available and should be applied immediately.
If you are a business owner or website operator, check whether your systems are affected. Contact your IT support team, website developer, or hosting provider for help identifying vulnerable systems and applying the necessary updates.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/JFOW6jG9Ws. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/ZWC7Se2YdU. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information on these vulnerabilities (CVE-2026-109618 and CVE-2026-109619), follow PHP’s announcements on https://t.co/JFOW6jG9Ws, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
‼️ Fortinet says AI helped find critical flaws in FortiOS and 4 more products, and thanked Anthropic, OpenAI, Google and SpaceX.
It urges an immediate upgrade but publishes no advisories until 10 November.
Kevin Beaumont says one is a path traversal in the management interface.
🚨 UPDATE: Railway says hackers targeted AI API keys to carry out model distillation attacks.
Up to 100,000 workspaces may have been exposed.
Attackers allegedly used uncensored AI models and massive compute resources to breach its infrastructure.
What we know: https://t.co/om4EQe9Q3q
Yahoo is still blocking emails from our newly assigned IP space. We've continued using it and aren't going to stop because Yahoo won't accept mails from it. It already has a great reputation elsewhere and there are 0 issues with anything else blocking it.
https://t.co/4Ml5I6Fijk
‼️ FOUR critical GitLab RCE flaws traced back to just THREE bugs in Ruby's regex engine.
Ruby has now fixed them, but this isn't just a GitLab issue.
Other Ruby apps that compile attacker-controlled regex patterns are also affected.
Details ➜ https://t.co/E4NxZyVZcq
I think we've discovered another critical vulnerability:
CVE-2026-BURNOUT: AppSec Professional Exhaustion
Severity: Critical (CVSS 10.0)
Description: A vulnerability affecting security professionals exposed to a continuous stream of critical RCEs, zero-days, emergency patches, and Friday afternoon disclosures.
Impact: Sleep deprivation, excessive caffeine consumption, and an inability to enjoy weekends.
Attack vector: Reading security advisories.
Affected versions: All AppSec professionals, regardless of experience.
Mitigation: No known patch. Air-gapping may delay the inevitable. Total system collapse remains a possibility. 🔥
as bad as things have gotten in the past 4 days, they are going to get a lot worse before they get better. security leaders, never let a crisis go to waste: please go to your boards and ask for help right now. not for ai, for the basics. (we need to hold on for ~18 months.)
The world is not prepared for when the hardware layers start getting attacked.
For example I can easily send a command to most Bitmain miners and completely fry all their hashboards.
No closed or open source firmware will save you from shitty engineering.
Attacking physical infrastructure (and especially zero sum infrastructure like bitcoin mining) will become lucrative for obvious reasons...
Software attacks are just the beginning, prepare accordingly...
Bitcoiners who've been through the Coldcard hack, Liquid drain, BTCPay Server incident, and Core Lightning vulnerability, now watching the rest of the world come to terms with the inevitable AI exploitation of the entire internet.