🚨 UNC6671 INFRASTRUCTURE UPDATE
Two more hostnames have appeared under myssologin[.]com:
⚖️ kelleydrye.myssologin[.]com
⚖️ willkie.myssologin[.]com
The apparent references are Kelley Drye and Willkie, expanding the cluster to four major law firms.
Tracking live. 👀
🚨 UNC6671 INFRASTRUCTURE UPDATE
Fresh legal-sector hostnames observed:
⚖️ cooley.myssologin[.]com
⚖️ paulweiss.myssologin[.]com
Both use the same Microsoft OAuth-style path:
🔗 /common/oauth2/v2.0/authorize/
Tracking live. 👀
#UNC6671#ThreatIntel
🚨 UNC6671 INFRASTRUCTURE UPDATE
A third hostname has appeared under login-options[.]com:
⚖️ bclplaw.login-options[.]com
The apparent reference is BCLP, adding legal services to the existing Carlyle and AEP finance/energy theme.
Tracking live. 👀
#UNC6671#ThreatIntel
🚨 UNC6671 INFRASTRUCTURE UPDATE
Newly observed under login-options[.]com:
💼 carlyle.login-options[.]com
⚡ aep.login-options[.]com
The apparent brand-impersonation theme now spans investment management and US energy infrastructure.
Tracking: ongoing 👀
🚨 UNC6671 INFRASTRUCTURE UPDATE ⚖️
Fresh legal-sector impersonation observed:
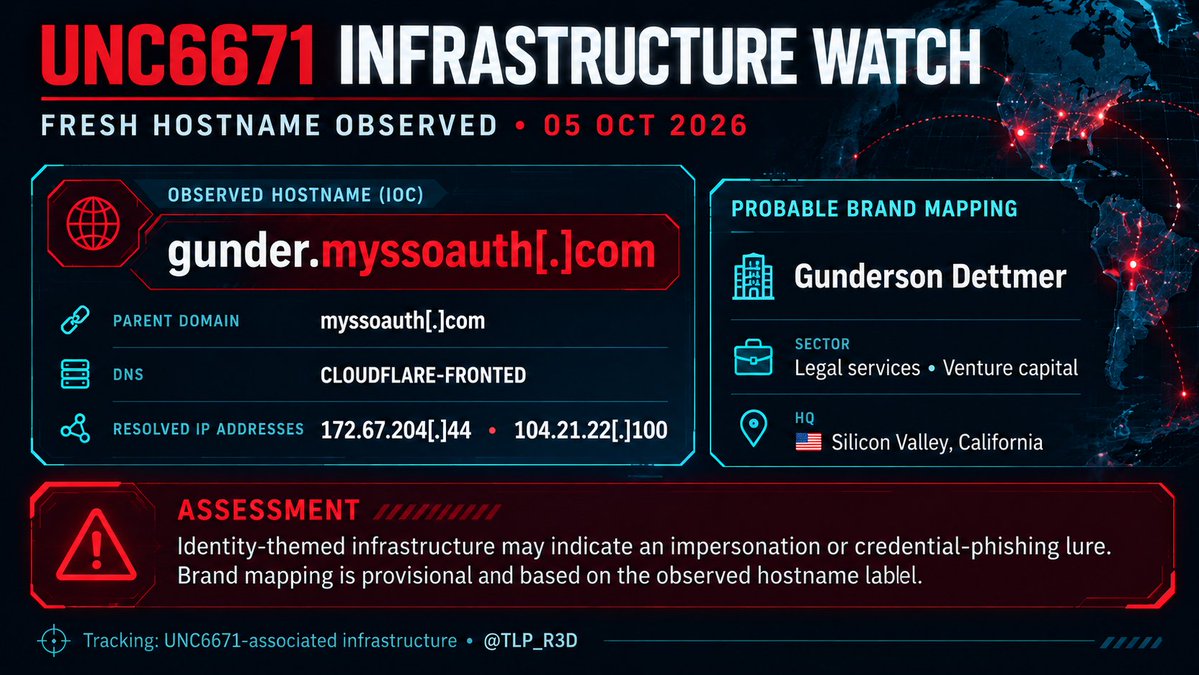
🔎 hollandhart.myssoauth[.]com
The hostname appears to spoof US law firm Holland & Hart and continues the cluster’s SSO/authentication theme.
Detection at observation: 0/92 👀
#UNC6671
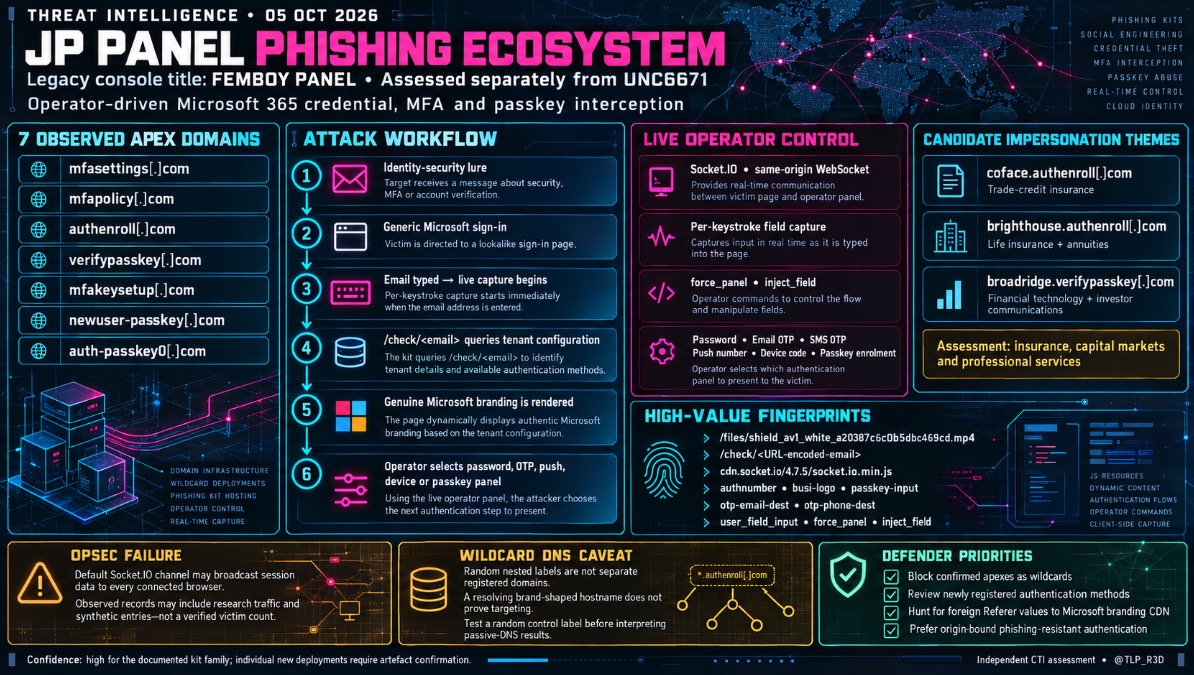
🎣 JP PANEL PHISHKIT 🔎
The kit renders genuine Microsoft tenant branding while operator controls target credentials, MFA and passkey flows.
Theme: insurance, capital markets & professional services.
Tracked separately from UNC6671. #ThreatIntel
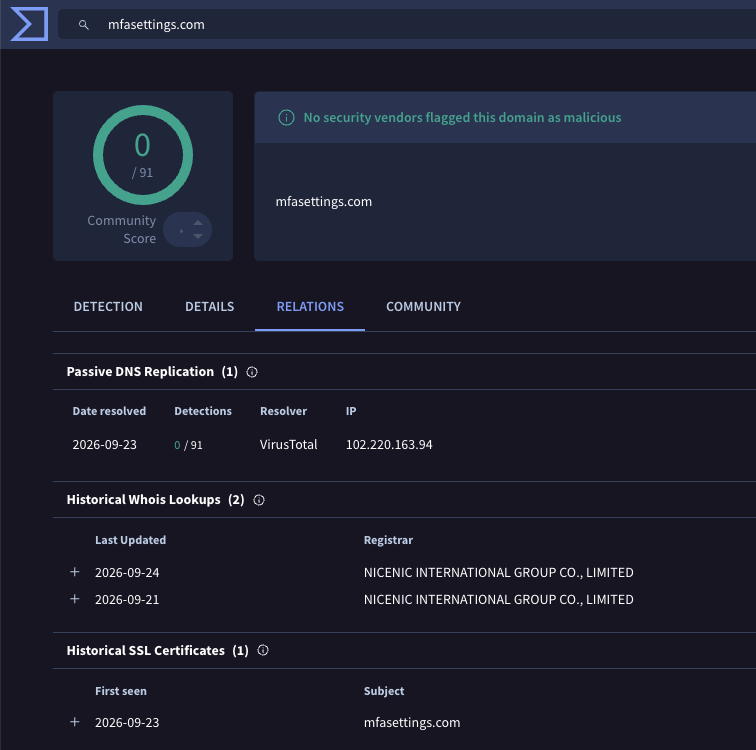
Another root domain: mfasettings[.]com , #UNC6671
Follows the same identity/MFA-themed naming pattern, no subdomain yet.
Registered on Sep 21 via NICENIC, uses Cloudflare NS, and currently resolves to 102.220.163[.]94 (VPS Dedicated LLC).
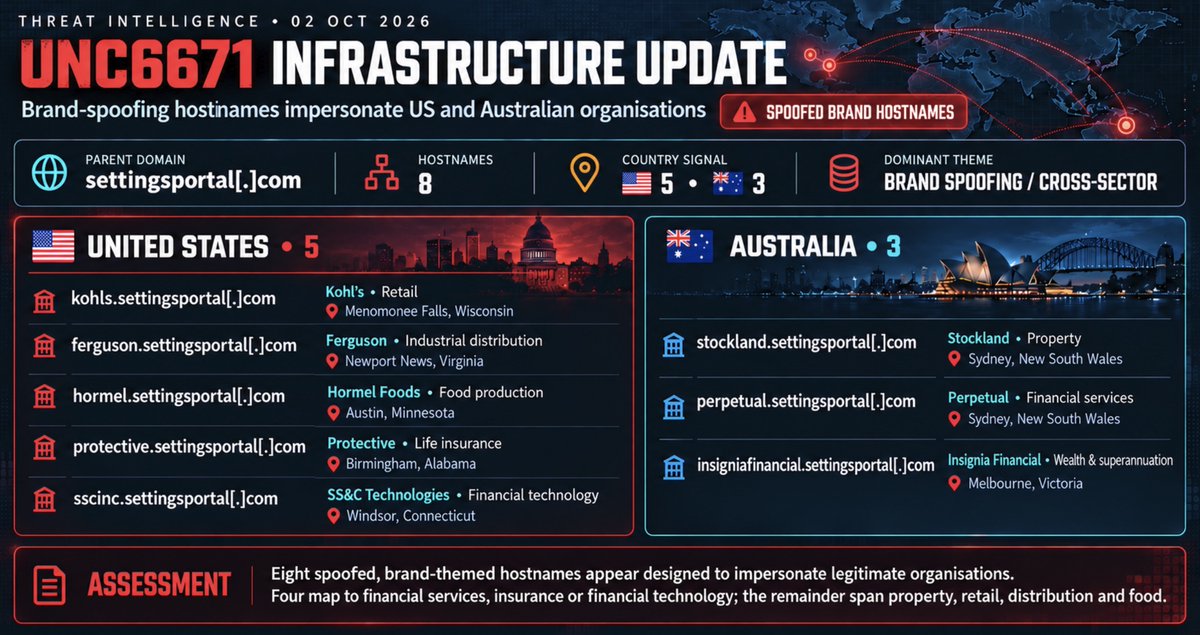
🚨 UNC6671 INFRASTRUCTURE UPDATE
New Domain: settingsportal[.]com
8 brand-themed hostnames across 🇺🇸 + 🇦🇺. Half map to finance, insurance or fintech; the rest span property, retail, distribution and food 👀
#UNC6671
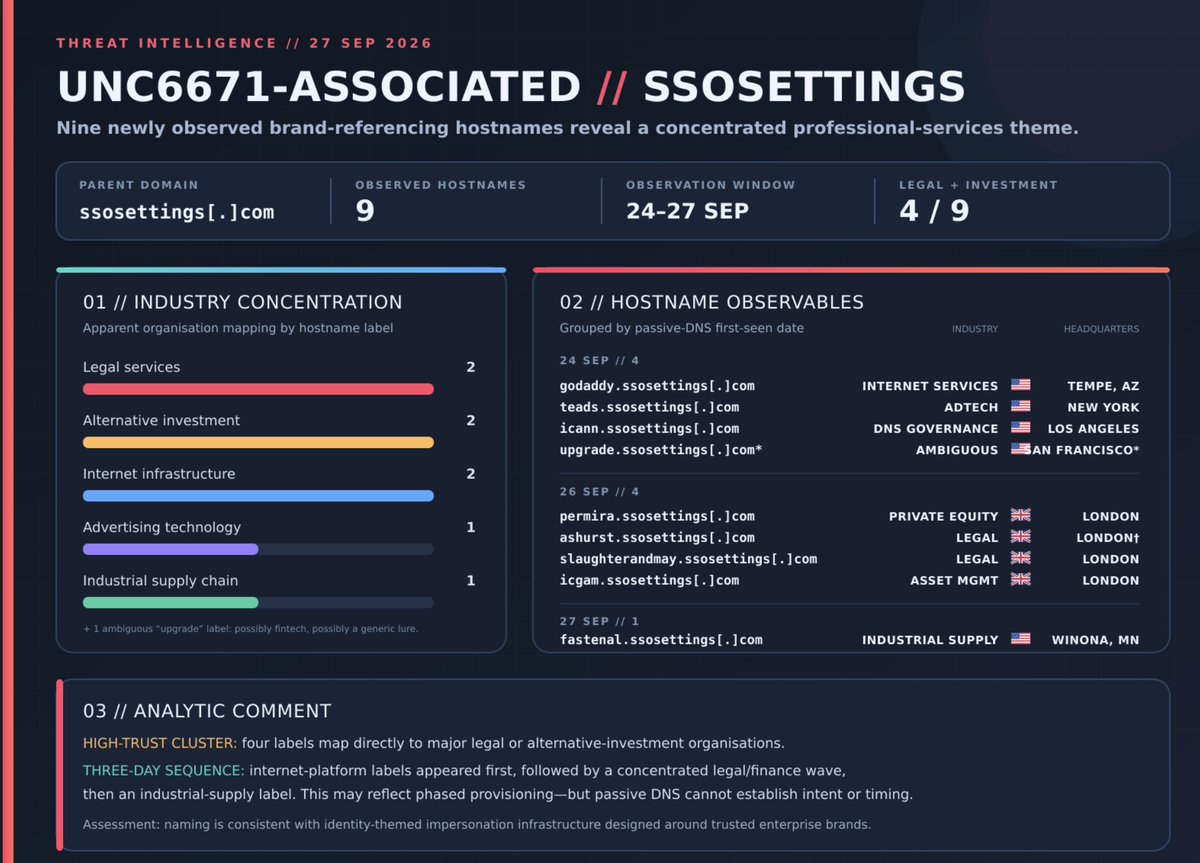
🚨 #UNC6671 WORKING ON THE WEEKEND 😀
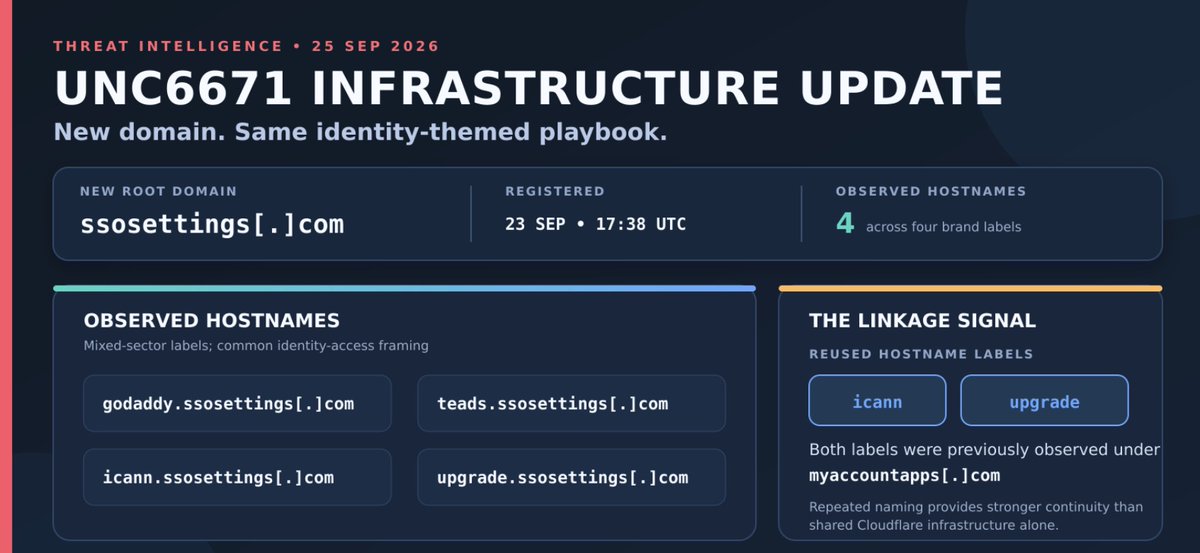
Nine brand-referencing hosts observed under ssosettings[.]com.
The standout: 4/9 reference legal or alternative-investment firms. The wider set spans internet infrastructure, adtech and industrial supply.
🚨 UNC6671 INFRASTRUCTURE ALERT
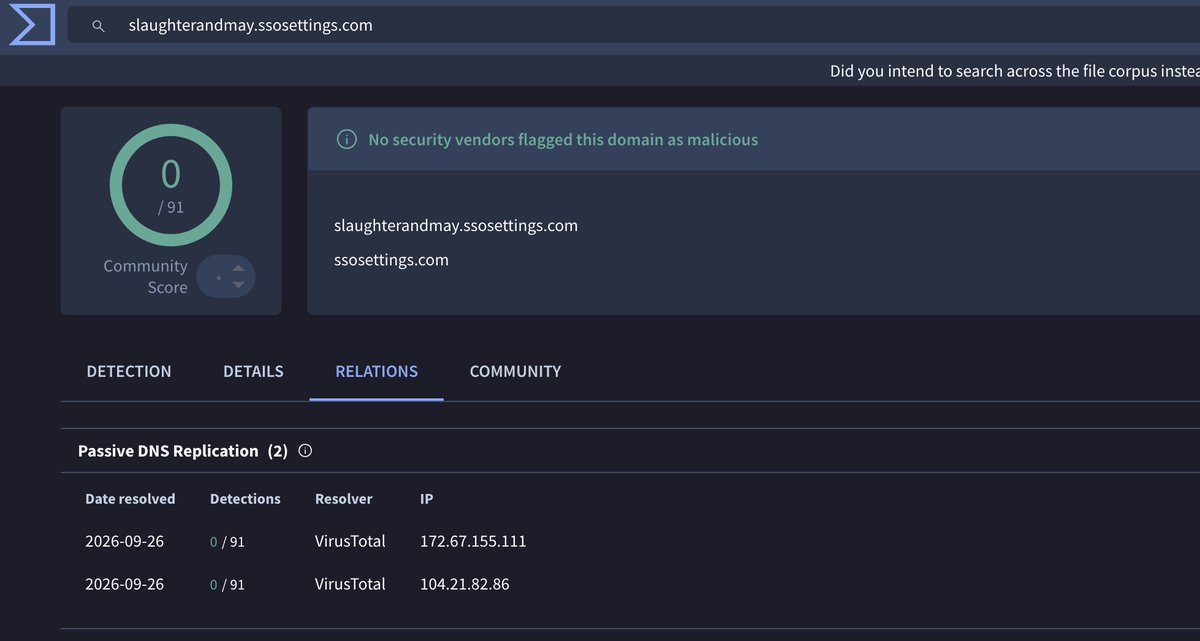
New apparent brand-impersonation host referencing @slaughterandmay:
slaughterandmay[.]ssosettings[.]com
Slaughter and May is a British law firm headquartered in London, England. Founded in 1889.
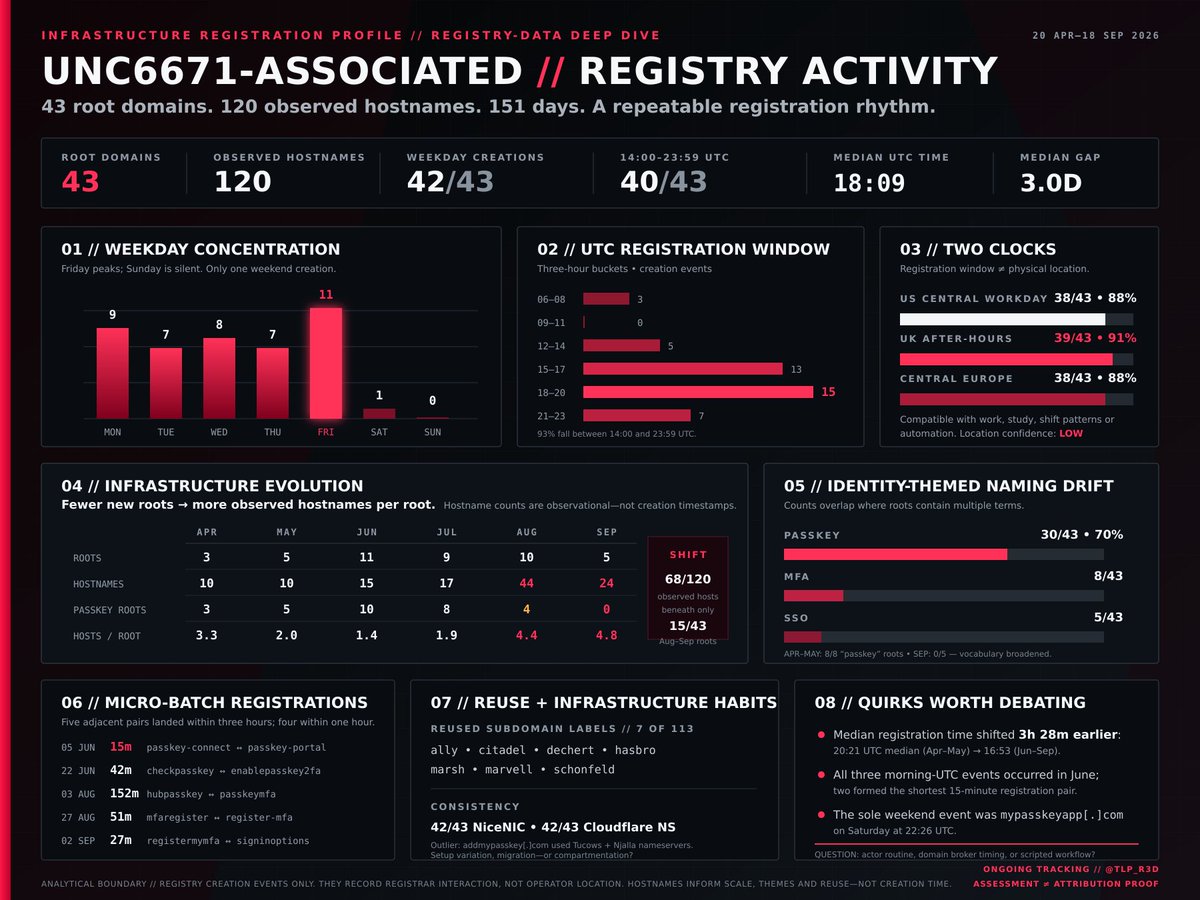
🕵️ I analysed 151 days of UNC6671 registry activity: 43 domains and 120 hostnames.
The pattern? 97.7% weekday provisioning, Friday peaks, micro-batches, recycled labels and a sharp pivot away from “passkey” naming.
US workday or European after-hours? 👀
#UNC6671
🔎 UNC6671 follow-up:
The exposed 46.19.136[.]147 sits in AS51852 / Private Layer—the same ASN Google previously reported hosting UNC6671 AiTM panel reverse proxies.
Strong infrastructure continuity, though this IP’s exact role remains unconfirmed. 👀
https://t.co/v5DR4sh2ir
🚨 Possible OPSEC slip in UNC6671 associated infrastructure?
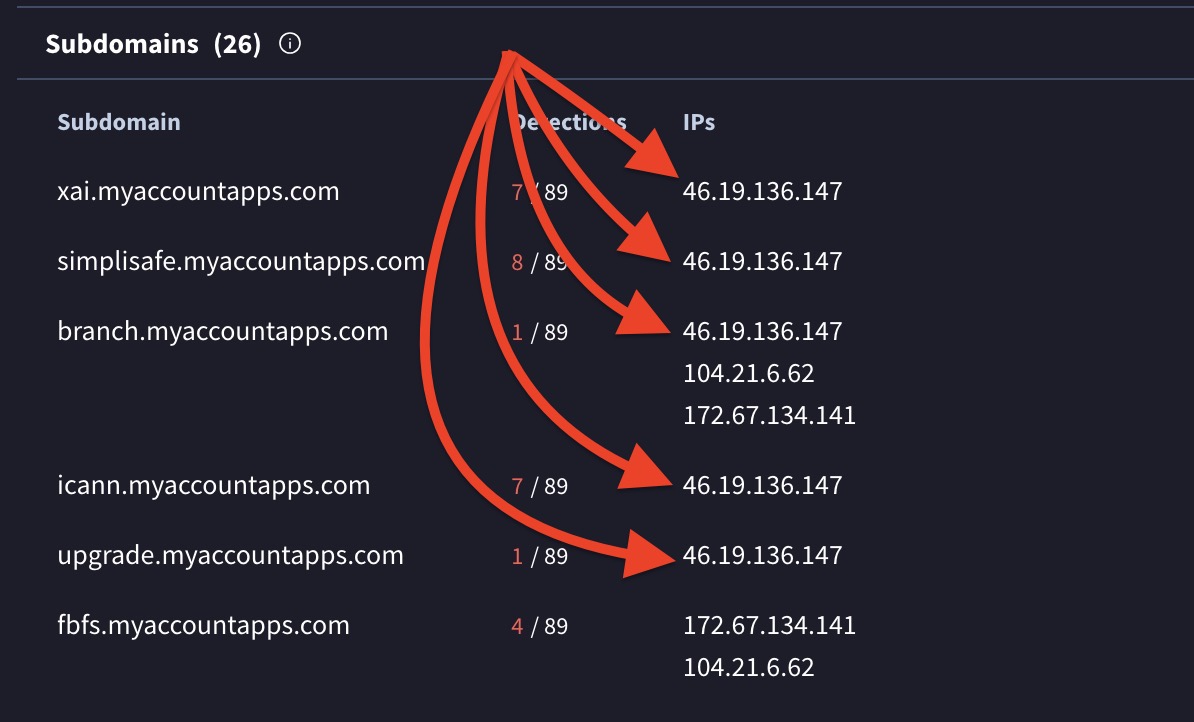
A DNS change appears to expose 46.19.136[.]147 (Private Layer INC ) behind numerous myaccountapps[.]com hostnames. 🔎
Misconfiguration or campaign teardown? Intent remains unclear—but the pivot is worth watching. 👀
🚨 Possible OPSEC slip in UNC6671 associated infrastructure?
A DNS change appears to expose 46.19.136[.]147 (Private Layer INC ) behind numerous myaccountapps[.]com hostnames. 🔎
Misconfiguration or campaign teardown? Intent remains unclear—but the pivot is worth watching. 👀
🔎 Useful supporting research from @Unit42_Intel.
They assess add-mfa[.]com and myaccountapps[.]com as likely Com-affiliated, both previously shared through my UNC6671 tracking.
I’ve also shared additional infrastructure in recent posts that is linked to this ongoing campaign .
Unit 42 continues to track network infrastructure that is likely associated with Com-affiliated threat actors. Two of these domains are likely being used to target organizations operating across a wide array of industries. Details at https://t.co/iKP9Sz54Uy
🏦 UNC6671 ACTIVITY UPDATE 🚨
New infrastructure continues to suggest possible phishing/vishing activity with an apparent focus on insurance and financial-services brands.
Time to refresh staff awareness around unsolicited calls, MFA requests and credential prompts.