🚨 A Next.js middleware flaw can let unauthenticated attackers bypass authorization checks; CVE-2025-29927
PoC: https://t.co/ui6L3jzXkM
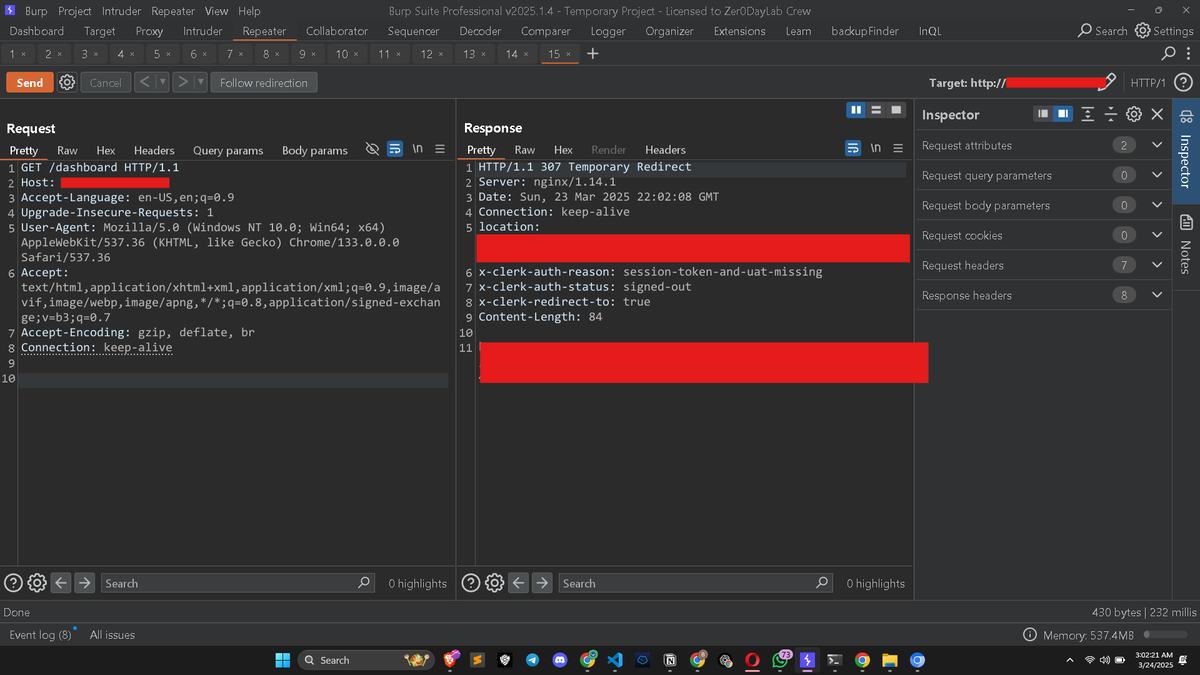
The vulnerability affects applications that rely on Next.js middleware for access control. By abusing the x-middleware-subrequest header, an attacker can cause middleware checks to be skipped and potentially reach protected routes without authentication.
Next.js Middleware | Authorization Bypass:
• CVSS: 9.1 Critical
• Attack: Remote, unauthenticated
• Affected: Next.js 11.1.4–12.3.4, 13.x < 13.5.9, 14.x < 14.2.25, 15.x < 15.2.3
• Fixed: 12.3.5, 13.5.9, 14.2.25, 15.2.3
• Impact: Bypass of middleware-based authorization controls
The repository demonstrates the header-based bypass against a protected route.