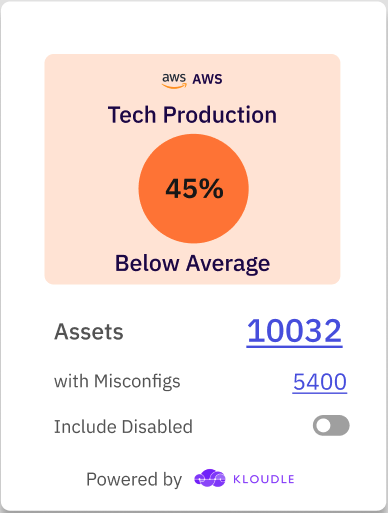
🌟 Users can now download our Security Scorecard to paste into their presentations. Comes with a Powered by Kloudle for some product awareness built in :)
DM @makash for a demo slot!
We are proud to be featured in @BessemerVP Venture Partner's ‘Developer platforms in India’ report. Can you spot us?!
cc @makash@riyazwalikar
https://t.co/6zDva9n2Xq
IMDSv1 can allows attackers to use vulnerabilities like SSRF to gain access to sensitive information from your instances on #AWS. Check out this article by @PragtiC to see how you can update IMDSv1 to the more secure IMDSv2.
https://t.co/jyINOdZrFD
#CloudSecurity
AWS Roles Anywhere allows non AWS workloads to obtain temporary security credentials in IAM instead of using long term credentials to perform actions on AWS.
In this detailed article by @riyazwalikar we take a look at how to use AWS IAM Roles Anywhere.
https://t.co/QROTuzdnia
Enabling the Password Prevent Reuse policy secures your #AWS in the event of password #breaches. This article by @PragtiC provides a walkthrough of how you can enable it, both in #video and text for your preferred medium of learning.
https://t.co/siu7pIiWJh
#cloudsecurity
Wondering How to enable prevent password reuse policy in AWS using CLI? Wonder no longer! Look at this @Kloudleinc video and answer all your questions!
https://t.co/1r6escZULm
@awscloud#AWS#Password#howto
Why read when you can watch instead? This @Kloudle video tells us How to enable prevent password reuse policy in AWS using the console
https://t.co/JJIk5KDBAf
@awscloud#AWS#Password#howto
Encrypting data at rest is a security best practice, for #AWS RDS instances too. If you have an existing unencrypted #RDS instance, this #Academy article by @DevSecOpsgirl_ will guide you on migrating it to an encrypted one.
https://t.co/0ce2xl7EGQ
#cloudsecurity@awscloud
If you have created a public AMI from your EC2 instance, be careful, you may be making sensitive or proprietary data accessible to any AWS user. @DevSecOpsgirl_ shares why and how to make them private in this #Academy article
https://t.co/3rJvi09Wj9
#cloudsecurity@awscloud
In this Academy article, @riyazwalikar shows us how to create users of various permission levels in an AWS EKS cluster and map the user to an AWS IAM user.
Check out this article here: https://t.co/YSRoY4BxUD
#SRE#devops#cloudsecurity#aws@awscloud#Kubernetes
Do you know the features provided by S3 to ensure our data is secure on the cloud? @riyazwalikar gives a comprehensive and detailed guide to securing your AWS #S3
https://t.co/cv4blVPxlC
@awscloud#cloudsecurity#SRE#devops
@ramimacisabird brings home the last in our #CloudVillage video series, #CloudSecurity Orienteering. Here he presents a methodology that can help one orient to the new cloud environment when tasked with its #security
Read @PragtiC's detailed #update now! https://t.co/9eX7ZmjsBz
Today @riyazwalikar writes the latest Academy article showing an exploitation scenario where an attacker, who has managed to gain SSRF or code execution capabilities, can leak tokens and escape to the Google Cloud platform
https://t.co/yz3GWMccl0
#gcp#pentesting@googlecloud
Pub/Subs are popularly used for asynchronous communication between applications. This #knowhow Academy article by @DevSecOpsgirl_ is a quick walkthrough of how you can create a Pub/Sub Topic on Google Cloud
https://t.co/Bbwso25fl3
#learning#SRE#devops#google@GoogleCloudTech