537 CVEs landed on 19 October 2026, above the typical 480. 27% arrived unscored, leaving 143 flaws you cannot triage on base severity yet. That is a heavy backlog to sort by hand. #CVE#VulnerabilityManagement https://t.co/fCmfsm1Iru
Krebs reports ShinyHunters breached https://t.co/u8Ku1j7Ldy via Oracle PeopleSoft flaw CVE-2026-35273 in Environment Management Hub. It has a 9.8 CVSS, 96.7% EPSS, and is on CISA KEV. #ThreatIntel#InfoSec https://t.co/Bap0RXkAup
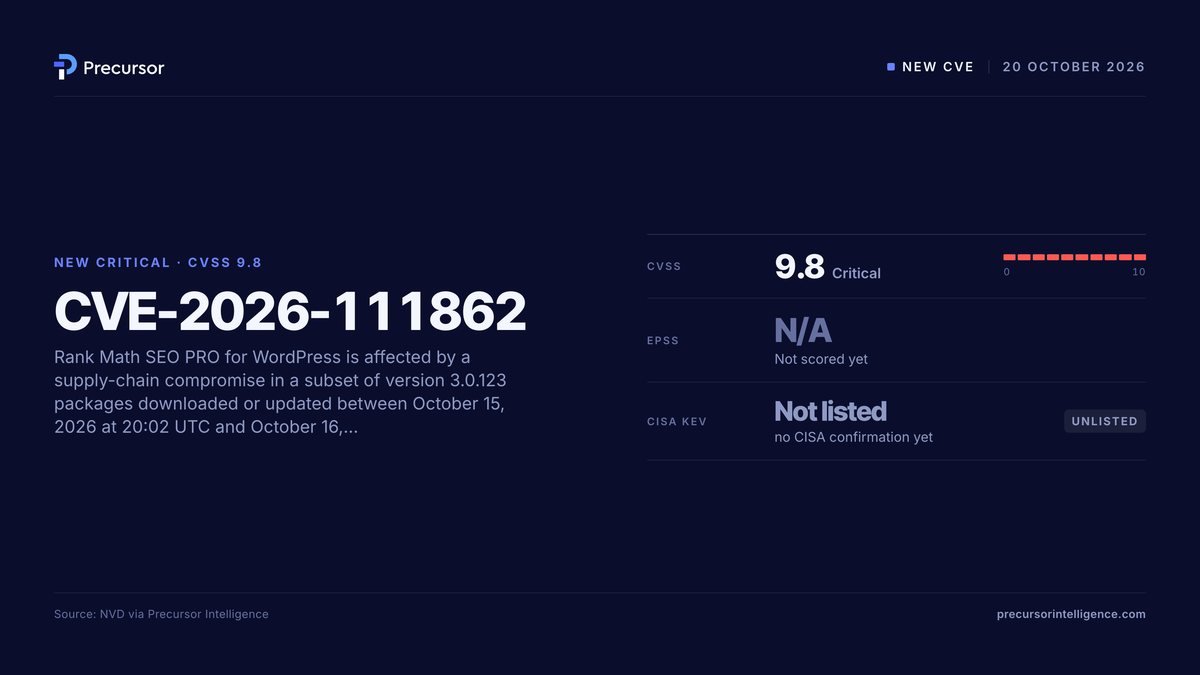
A supply-chain flaw in Rank Math SEO PRO version 3.0.123 carries a 9.8 CVSS. Poisoned packages installed on 15 or 16 October 2026 contain malware. No exploitation evidence yet: the quiet period is the cheapest time to patch. #CVE#Vulnerability https://t.co/xof45OE0d5
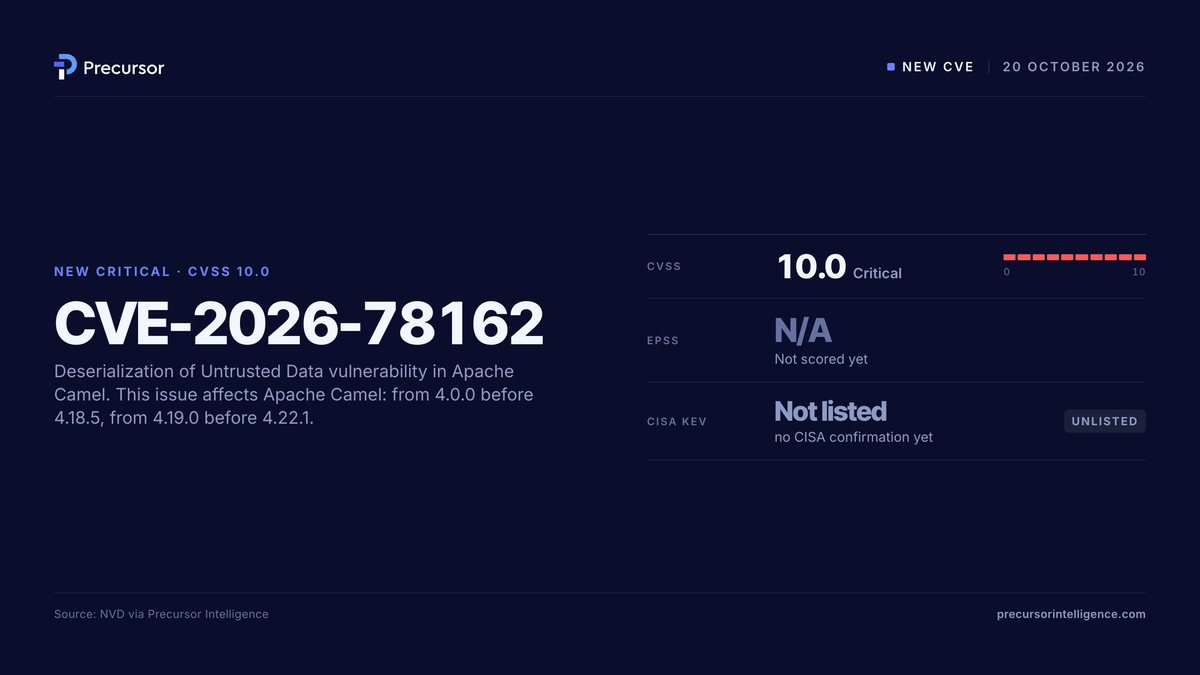
Apache Camel has a 10.0 CVSS deserialisation flaw, CVE-2026-78162, affecting versions from 4.0.0 before 4.18.5 and 4.19.0 before 4.22.1. There's no exploitation evidence yet, and the quiet period is the cheapest time to patch. #CVE#Vulnerability https://t.co/JwGTrLNA3V
Apache Answer carries a 9.8 CVSS flaw, CVE-2026-90910, affecting versions through 2.0.2 via its reaction API. Upgrading to 2.0.3 fixes it. With no exploitation evidence yet, this quiet period is the cheapest time to patch. #CVE#Vulnerability https://t.co/HKoE6dHKwS
RomPager's Misfortune Cookie bug moved from 63.7% to 74% EPSS in 2 days. The 2014 flaw lets attackers gain privileges via cookies on kit like Huawei Home Gateways. It isn't on CISA KEV, so check exposure now instead of waiting for a listing. #EPSS https://t.co/HzQ7gjj0qt
Genivia gSOAP flaw CVE-2017-9765 jumped from 24.6% to 42.1% EPSS in 2 days. It allows remote code execution on Axis cameras and other kit, and isn't on CISA KEV. Check exposure now, not after it's confirmed. #EPSS#VulnerabilityManagement https://t.co/fj3NYPxLPm
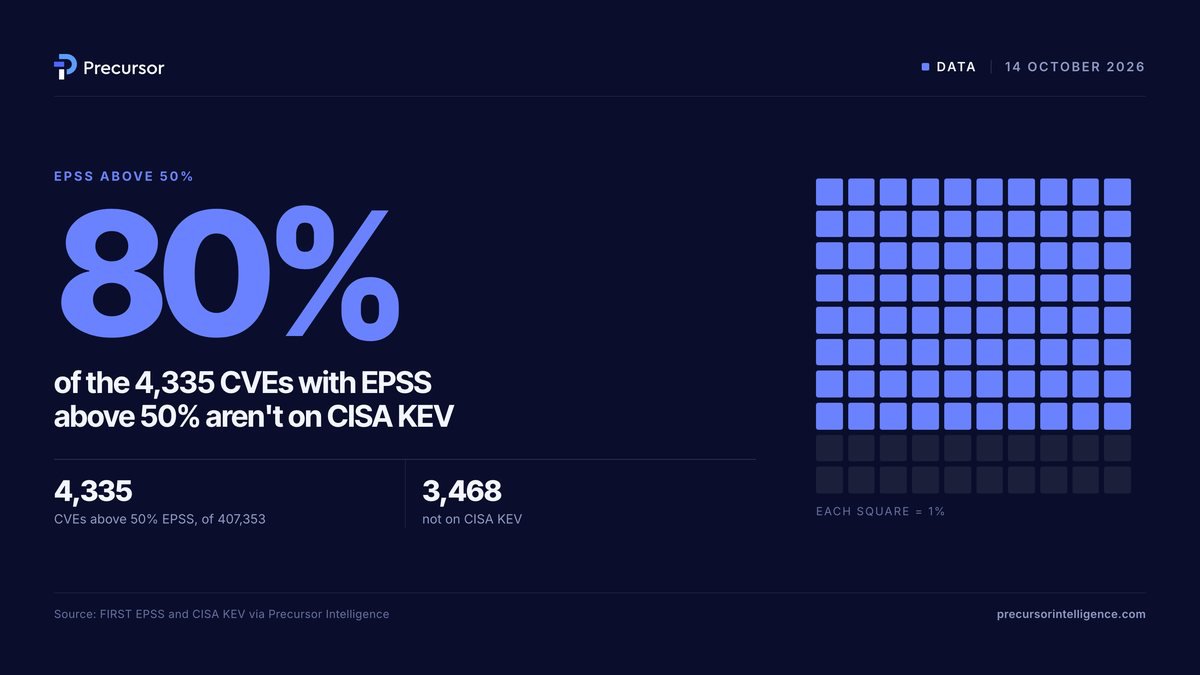
Just 4,335 of 407,353 CVEs sit at 50% EPSS or higher on 14 October 2026, which is 1.1% of them. 3,468 of those aren't in CISA KEV: that's an 80% blind spot if you only patch KEV bugs. Worth checking that short list against your estate. #ThreatIntel#CyberSecurity
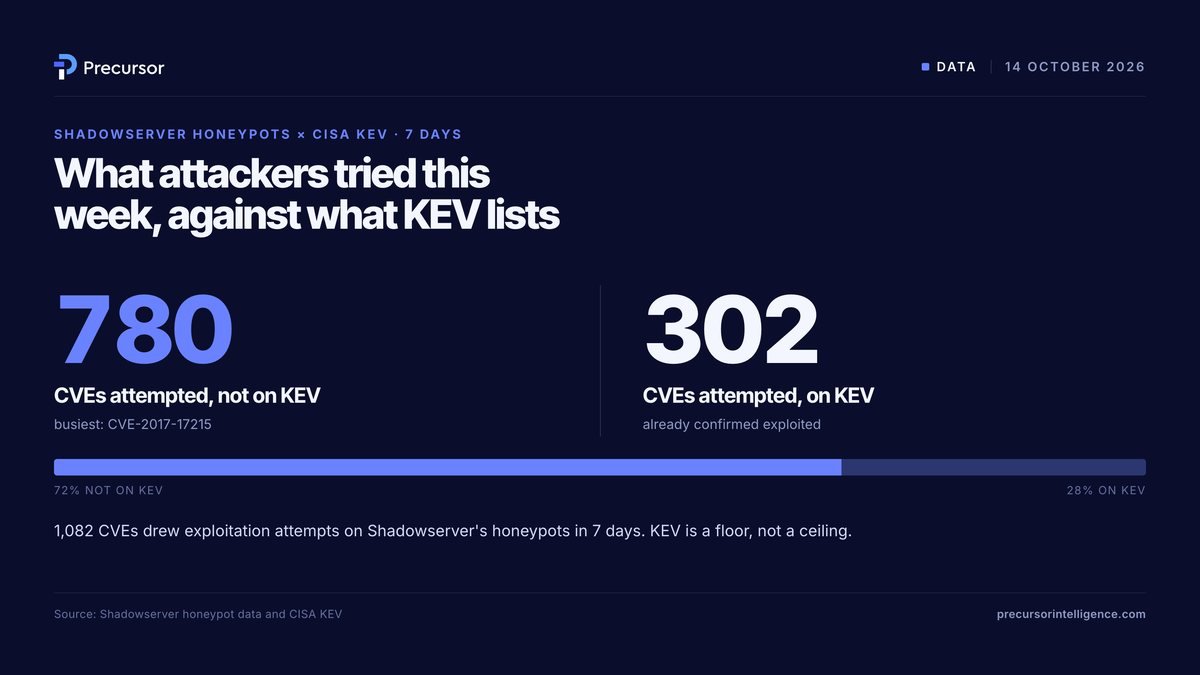
72% of the 1,082 CVEs with Shadowserver honeypot exploitation attempts in the last 7 days aren't in CISA KEV. That's 780 vulnerabilities being targeted right now, led by Huawei Home Gateway HG532 bug CVE-2017-17215 with 12,054 attempts. #ThreatIntel#CyberSecurity
Publishers saw 2,308 CVEs on 13 October 2026, above the 30 day average count of 479. The leading weakness was use-after-free with 382 flaws, while ColdFusion took three CVSS 10.0 flaws like CVE-2026-106624. #CVE#VulnerabilityManagement https://t.co/fCmfsm2gh2
Microsoft's October 2026 Patch Tuesday fixes a Windows Shell zero-day, Microsoft says. It also patches CVE-2026-108398, an untrusted search path flaw in .NET Framework (CVSS 8.8) that allows a local security feature bypass. #PatchTuesday https://t.co/AqokEIMi5l
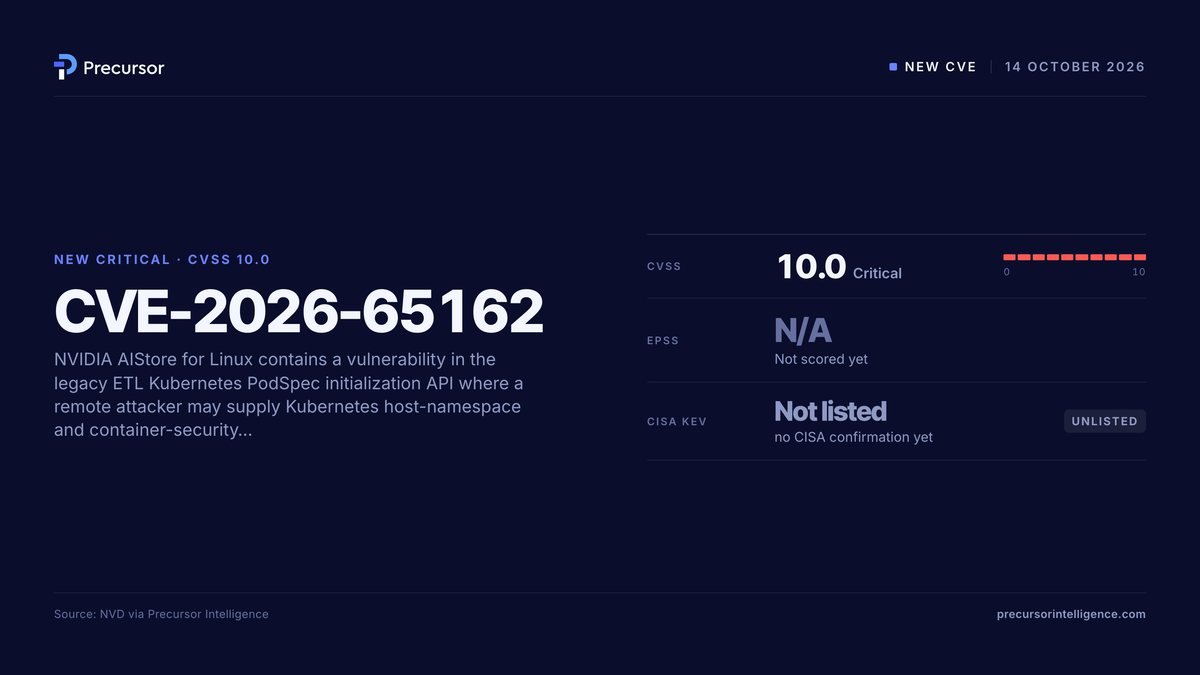
NVIDIA AIStore for Linux has a 10.0 CVSS bug in its ETL PodSpec API, letting remote attackers supply host-namespace settings. No exploitation evidence yet: the quiet period is the cheapest time to patch. #CVE#Vulnerability https://t.co/e8W6AkyXgO
CVE-2026-108971 is an 8.6 CVSS flaw in D-Link DCS-930L B1.08B4 devices. Remote attackers can bypass cryptographic signature checks via the Emergency HTTP Recovery Server. No exploitation evidence yet: the quiet period is the cheapest time to patch. #CVE https://t.co/ZMusYfyjNG
Wavlink WL-WN592AX6 250422 has a critical remote command injection flaw in its wmapd Daemon component. CVE-2026-109110 sits at 9.3 CVSS with public exploit code. No exploitation evidence yet: the quiet period is the cheapest time to patch. #CVE https://t.co/Qx1AOUEZpY
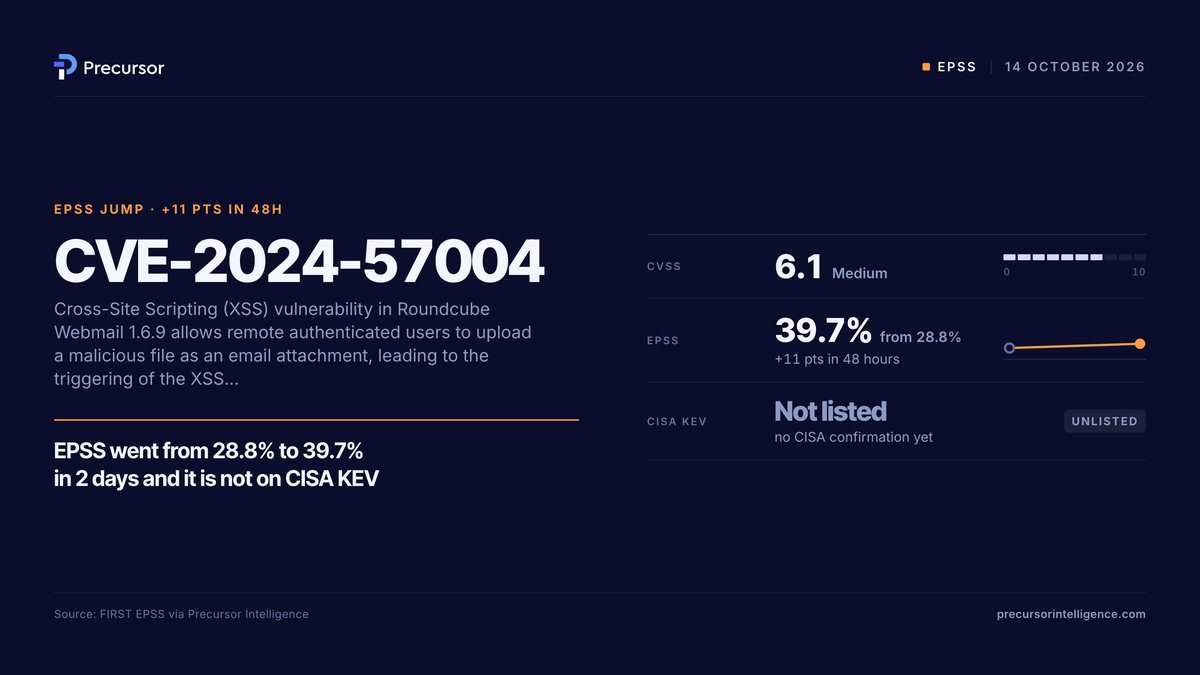
Roundcube Webmail 1.6.9's XSS bug went from 28.8% to 39.7% EPSS in 2 days. It isn't on CISA KEV, but authenticated users can trigger it via attachments. Check exposure now rather than waiting for a KEV listing. #EPSS#VulnerabilityManagement https://t.co/lJCrjBNRnT
MDaemon Email Server's webmail XSS bug, CVE-2024-11182, rose from 17.6% to 31.4% EPSS in two days. It's on CISA KEV and affects versions before 24.5.1c. Confirmed exploited and still climbing: top of the queue. #EPSS#MDaemon https://t.co/nSl4oZMz3q
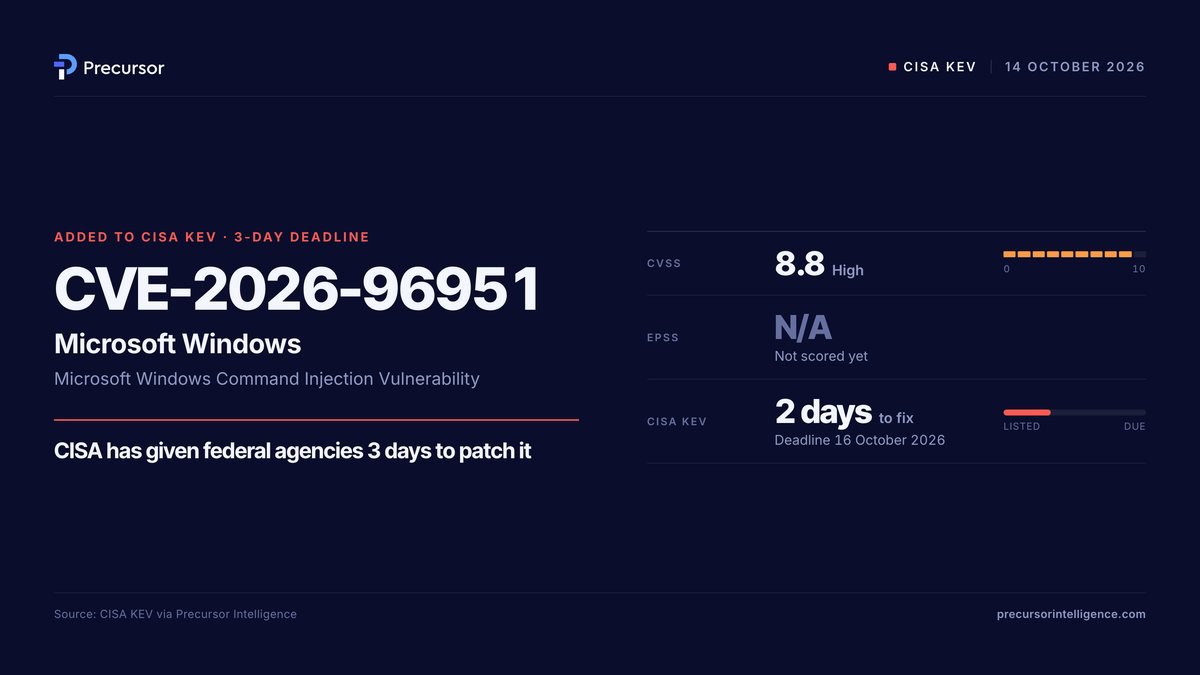
CISA added CVE-2026-96951 in Microsoft Windows Shell to KEV and gave agencies 3 days to patch it. It lets remote attackers bypass security features. CISA's patch deadline is a sensible benchmark for your own window on internet-facing kit. #CISAKEV https://t.co/jIUAt43sQO
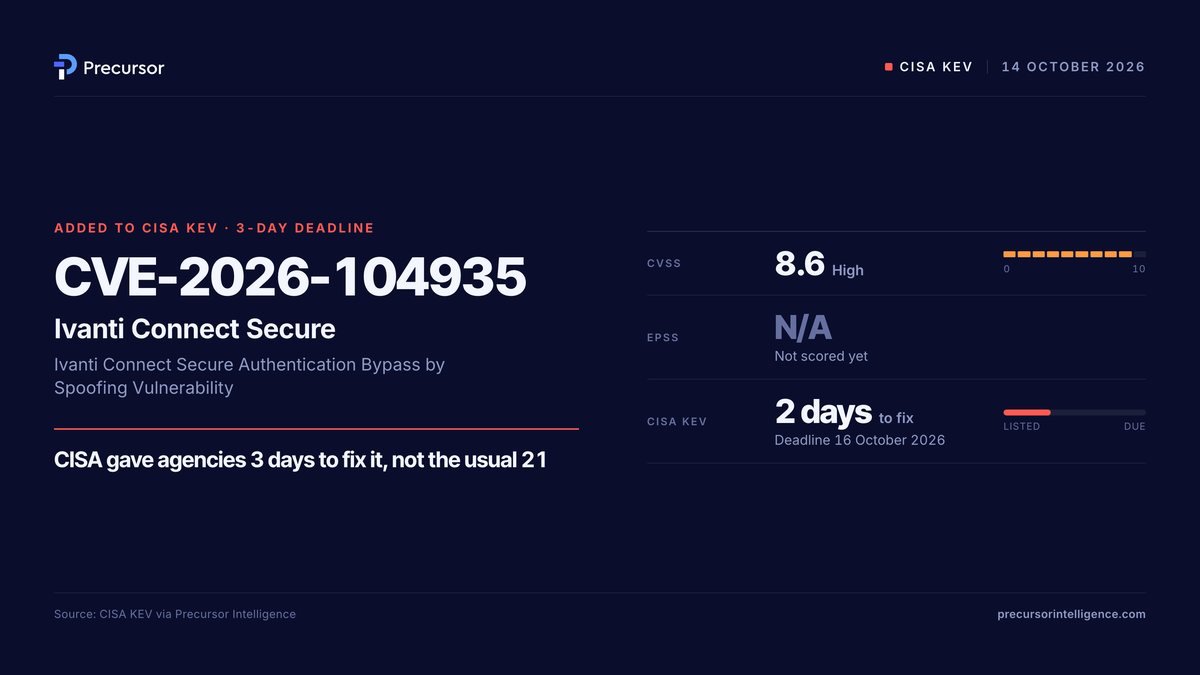
Ivanti Connect Secure bug CVE-2026-104935 is on CISA KEV, giving federal agencies 3 days to patch. It allows remote command execution before version 25.1.3.0. Use that deadline as a benchmark for your own internet-facing kit. #CISAKEV#Ivanti https://t.co/sI0wlcbYlx
465 of the 1,750 CVEs in the whole CISA KEV catalogue have an EPSS under 10% as of 13 October 2026. That is a 27% share. Review the list and keep patching what's on KEV. Tracked here: https://t.co/BYvTnr7MXe #ThreatIntel#CyberSecurity