🚨 CTI ALERT 🇦🇷 | TerroahOver CLAIMS ACCESS TO UNaM INFRASTRUCTURE / UNAM. EDU .AR — INTERNAL GITLAB
[STATUS: UNCONFIRMED / TYPE: UNIVERSITY INFRASTRUCTURE COMPROMISE · GITLAB ACCESS · SOURCE CODE / PROJECT EXPOSURE · POSSIBLE SUPABASE DATA EXTRACTION · CREDENTIAL / CONFIGURATION EXPOSURE / COUNTRY: 🇦🇷 ARGENTINA / ACTOR: TerroahOver / VICTIM: unam. edu .ar / SOURCE: DARKFORUMS]
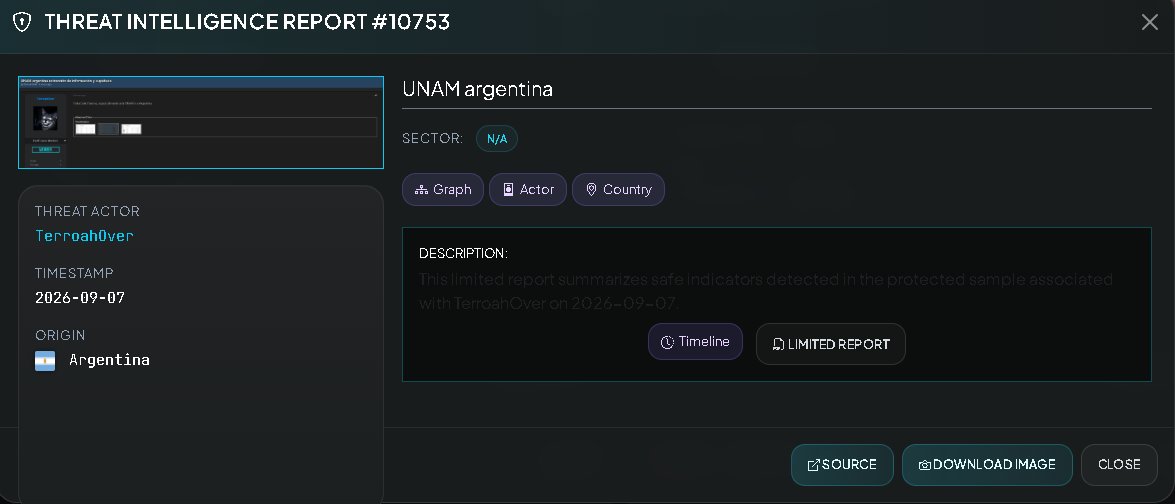
Cyber-intelligence monitoring has identified a new post attributed to the actor TerroahOver, who claims to have extracted information linked to an Argentine university's infrastructure and also mentions Supabase as part of the incident.
The provided screenshots show elements consistent with a GitLab environment.
⚠️ The incident remains UNCONFIRMED INDEPENDENTLY. Visual evidence shows screenshots of a GitLab platform and project-related content, but does not in itself prove the access vector, the actual scope of the compromise, or whether a full data extraction occurred.
🧩 POSSIBLE EXPOSURE OF CONFIGURATION FILES
Other evidence shows references to a path similar to:
demo/backend.env.dist
within a project hosted on GitLab.
.env or .env.dist files typically contain or document configuration variables.
Depending on the content, they could expose or reveal:
endpoints
service names
API keys
tokens
database credentials
internal URLs
project identifiers
Supabase configurations
⚠️ The screenshot does not allow confirmation that valid secrets are exposed. 📊 ASSESSMENT
Post observed: 🟢 YES
Actor: TerroahOver
Country: 🇦🇷 Argentina
GitLab access: 🟠 APPARENT / UNCONFIRMED
Project members visible: 🟢 YES
Roles visible: 🟢 YES
Source/config files: 🟢 APPARENTLY VISIBLE
.env.dist reference: 🟢 OBSERVED
Supabase involvement: 🔴 CLAIMED
Data extraction: 🔴 CLAIMED
Secrets exposed: ⚪ UNCONFIRMED
Database access: ⚪ UNCONFIRMED
CI/CD compromise: ⚪ NOT DEMONSTRATED
Initial vector: ⚪ UNKNOWN
Intrusion independently confirmed: 🔴 NO
🖥️ Centralized Threat Monitoring System:
https://t.co/wk9bZJ2Nli
Monitoring Console:
https://t.co/5LuqwzYuS6
#Argentina #UNAM #CyberSecurity #CyberCrime #ThreatIntel #CyberIntelligence #GitLab #Supabase #DataLeak #SourceCode #DevSecOps #UniversitySecurity #CredentialExposure #SOC #CSIRT #IncidentResponse #ThreatMonitoring #VECERT
🚨 CTI ALERT 🇵🇪🇦🇷 | cantpwn PUBLISHES ALLEGED PERUVIAN AIR FORCE LEAK — 13,037 IMAGES (~1.3 GB) AND ANNOUNCES ARGENTINA AS NEXT TARGET
[STATUS: UNCONFIRMED / TYPE: MILITARY DATA LEAK · DEFENSE-SECTOR TARGETING · IMAGE DATABASE EXPOSURE · POSSIBLE PERSONNEL/IDENTITY DATA · THREAT SIGNALING / AFFECTED COUNTRY: 🇵🇪 PERU / ACTOR: cantpwn / SOURCE: DARKFORUMS]
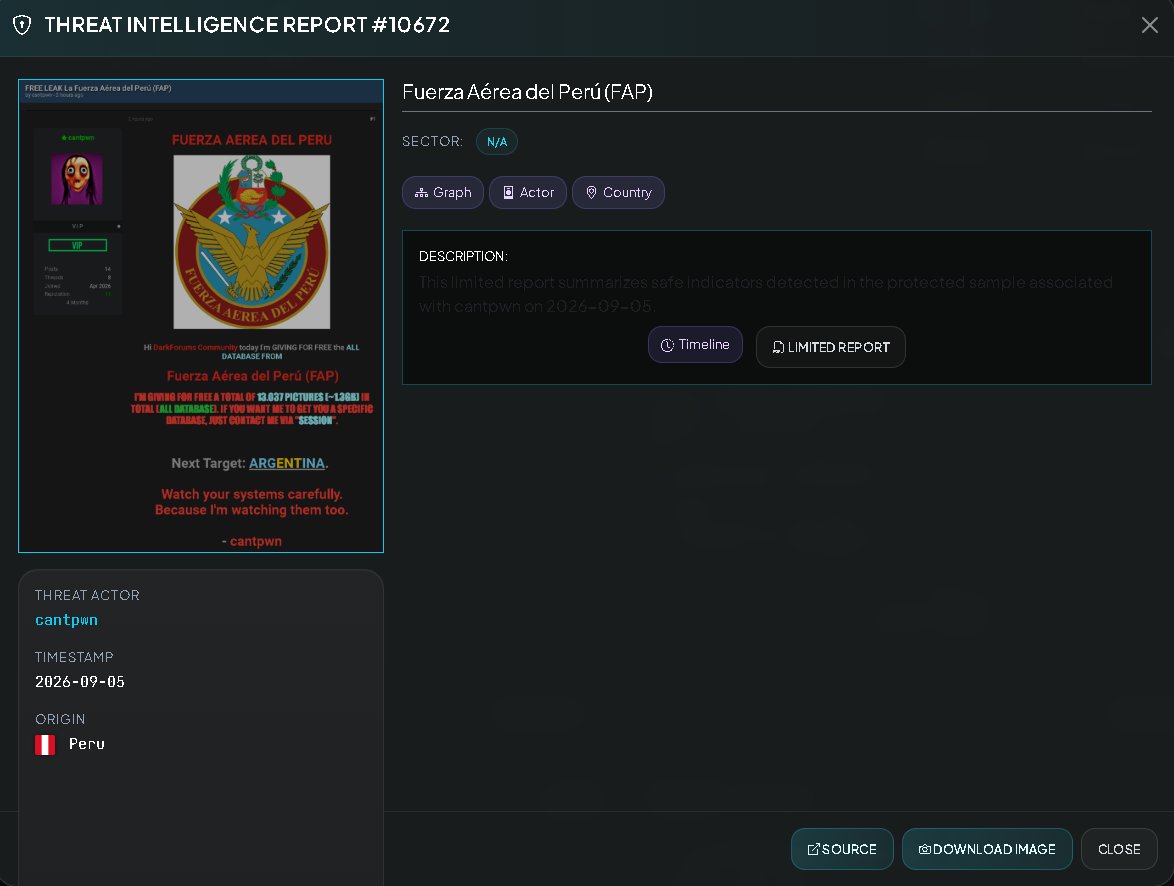
Cyber-intelligence monitoring has identified a new post attributed to the actor cantpwn, who claims to have obtained and released—free of charge—a database associated with the Peruvian Air Force (FAP).
The actor specifically announces the distribution of:
13,037 images
with an approximate volume of:
1.3 GB
and presents the material as part of the alleged "ALL DATABASE" of the Peruvian Air Force.
⚠️ The incident remains INDEPENDENTLY UNCONFIRMED. The post demonstrates the existence of the claim and a file advertised as a leak; however, it remains to be verified whether the 13,037 images actually originate from internal FAP systems, how old they are, and what categories of information they contain. 🛡️ RECOMMENDATIONS — SOC / CSIRT / DEFENSE
It is recommended to review:
image repositories
file servers
cloud storage
administrative systems
privileged accounts
bulk transfers
anomalous downloads
VPNs
remote access
reused credentials
vendor accounts
storage logs
activity from anomalous IPs/ASNs
tokens
APIs
accidentally exposed public repositories
buckets
backups
📊 PRELIMINARY ASSESSMENT
Publication observed: 🟢 YES
Actor: cantpwn
Claimed victim: Peruvian Air Force (FAP)
Country: 🇵🇪 Peru
Military sector: 🔴 YES
Claimed images: 13,037
Volume: ~1.3 GB
“All database”: 🔴 CLAIMED
Sample link: 🟢 YES
Overall authenticity: 🔴 UNCONFIRMED
Exact content: ⚪ TO BE VALIDATED
Military personnel: ⚪ TO BE VALIDATED
PII: ⚪ TO BE VALIDATED
Documents: ⚪ TO BE VALIDATED
Active access: ⚪ UNKNOWN
Initial vector: ⚪ UNKNOWN
Argentina announced as next target: 🔴 YES
Specific future threat: 🟠 GENERAL / NO SPECIFIC ENTITY
🖥️ Centralized Threat Monitoring System:
https://t.co/wk9bZJ2Nli
Monitoring Console:
https://t.co/5LuqwzYuS6
#Peru #FAP #PeruvianAirForce #Argentina #CyberSecurity #CyberCrime #ThreatIntel #CyberIntelligence #MilitarySecurity #DefenseSecurity #DataLeak #DataBreach #Doxxing #LATAM #DarkForums #SOC #CSIRT #IncidentResponse #ThreatMonitoring #VECERT
@impuestito_org Definitivamente voy por el silencio gil 2, ahora es personal
Respecto a la verdad incomoda, es un requisito para ser clasificado como "gamer" tener varios kilos de más y sufrir de sedentarismo.
🔥 SORTEO IMPUESTITO 🔥
🔑 Se sortea 1 SOLO de los dos (PC)
🔄 Difundí y toda lo de siempre
💬 Comentá por cuál participás
💬 Verdad gaming que nadie acepta
📀 Silent Hill 2 Remake
📀 Uncharted Legacy of Thieves Col.
@Saintiago11ii11 @impuestito_org Siendo realistas, la velocidad de los joysticks es adecuada para lo que tiene que hacer. Sería más incómodo posicionar un mouse y programar el seguimiento...
Y seguro no usó mouse porque estaba de oferta la twitch, juega COD primero y luego animal crossing.
@GooseworxMusic There's nothing wrong with the ads. Besides, you can always get rid of the ads by purchasing a monthly subscription starting at $99.99 that will "reduce" the amounts of ads you get...
@Unaplayable Realmente la única medida que me pareció extrema fue si por accidente eliminabas a un survi antes de llegar a la cantidad mínima de cuelgues.
Cuando jugué la PTB me tocaron puros rusheros cuando prove el nuevo killer.
Aun así un poco le gustó el resto de las medidas anti tuneleo
¿Tenés un comercio? ¿Querés que tus clientes sepan que pueden pagar con QR y encima recibir cashback?
Tenemos stickers para vos. Te los mandamos por correo para que los pegues en tu vidriera 😉
Respondé este tweet o mandanos DM con el nombre del local 👇
El QR que te devuelve Bitcoin llegó, y ahora vos también podés llevarte el famoso kit ⚡
¿Cómo participás?
👉 Seguinos
👉 Hacé RT a este post
📆 Sorteamos el 22/8