Hackers, bug hunters, researchers — we built our new home! Zero marketing fluff, just good stuff:
✅ @ptdbugs: 350K+ free vulns
✅ 0days & breach intel
✅ @StandoffBB: Bug bounties
✅ The world's cybersecurity calendar
👉 https://t.co/LY8ohhCCmj
One of our business cards had a busy three days at @GISECGlobal
It passed from hand to hand as we talked about what it takes to make digital sovereignty work.
The answer doesn’t fit on a business card. Watch the film.
#GISEC#GISEC2026
#GISEC is a wrap, but we’ve still got DeCode footage to drop 👀
@amoshkov teamed up with @GodfatherOrwa and @XHackerx007 to build a security token, rip into its firmware and trade bug bounty stories
Watch till the end to find out where we’re heading next https://t.co/70eU7cBOM6
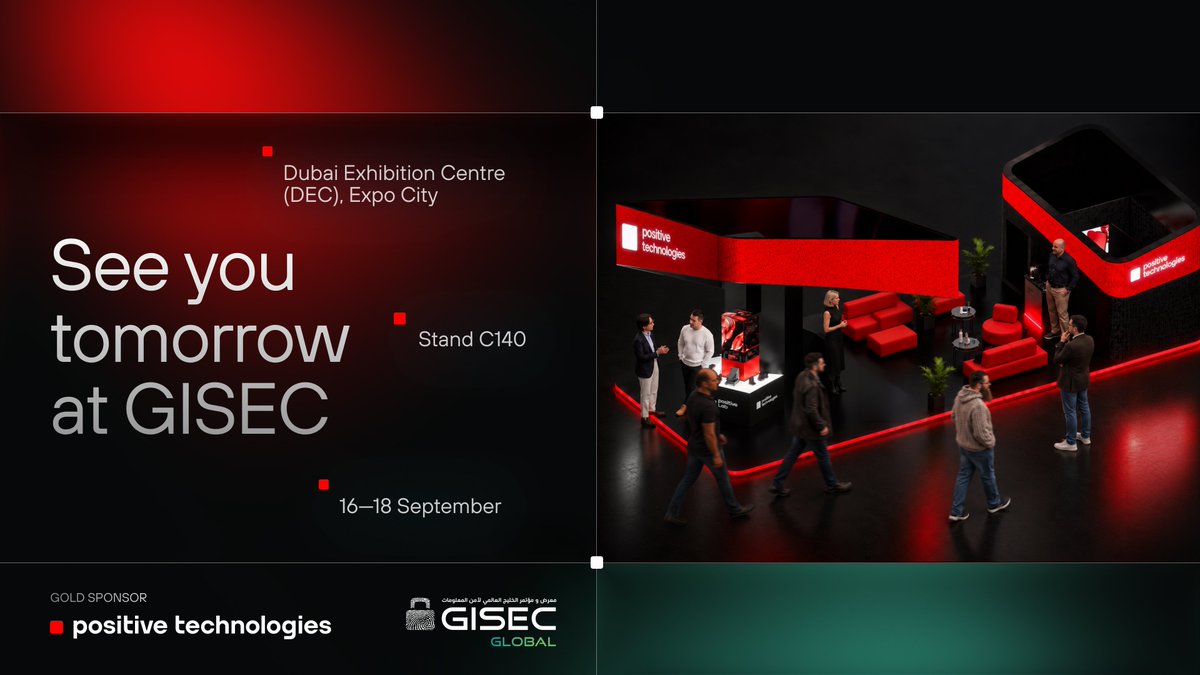
The Positive Technologies team will be at @GISECGlobal 2026 tomorrow!
📍 Dubai Exhibition Centre (DEC), Expo City
📢 Stand C140, Hall 5
Check out our full GISEC agenda below:
https://t.co/p76yF5kgXf
#GISEC#GISEC2026
QKS Group has ranked Positive Technologies among the leading vendors in its SPARK Matrix for XDR, highlighting MaxPatrol Endpoint Security and its integration with SIEM, VM, Sandbox, NAD and ISIM. Independent recognition is always welcome—especially when customers agree. 😎 #XDR
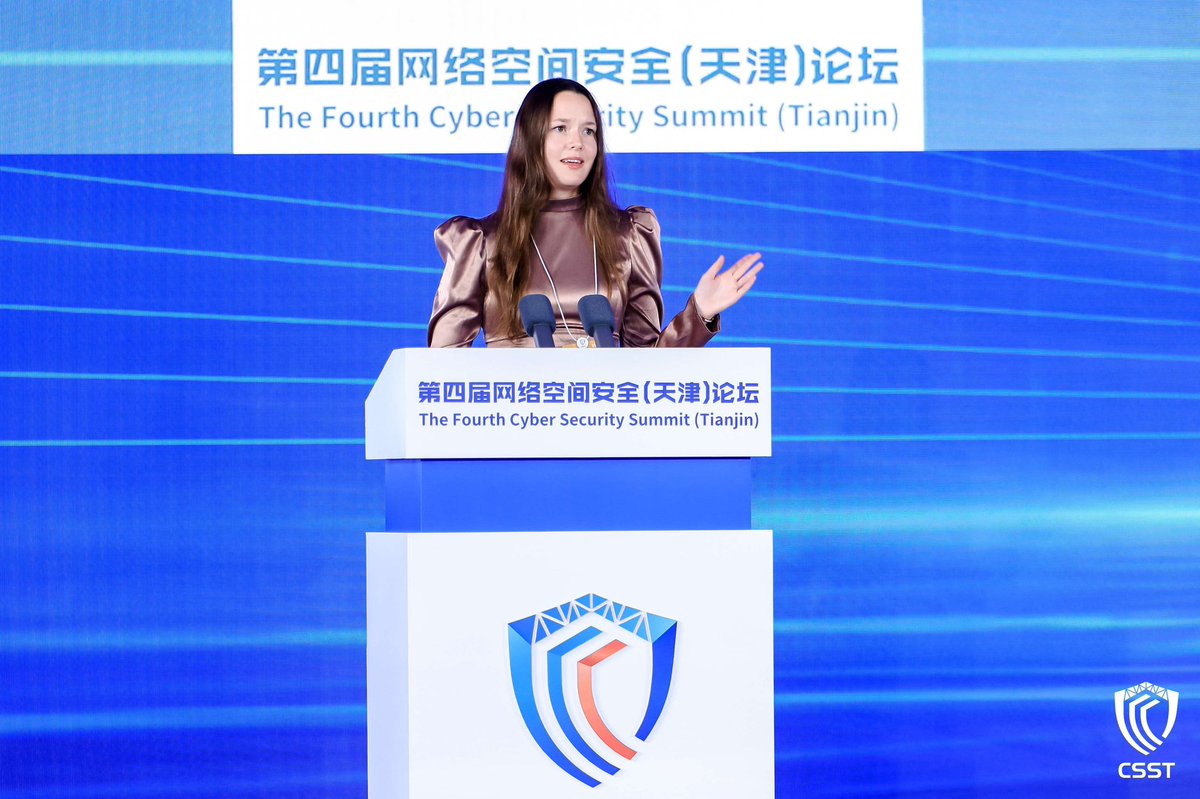
Long time no post! Back from CSST in Tianjin 🇨🇳
Was really happy to return to the International #AntiVirus#Conference for a 2nd year in a row!
Talked about "Navigating the Ocean of Network Dumps", basically how to triage terabytes of traffic & keep your sanity as an analyst 👩💻
What’s in Positive Technologies’ DeCode zone at @GISECGlobal?
⚙️ Positive Labs: build&hack an USB security token
🎭 DeepFake Reality: see how AI can replicate your identity
🎤 Stand-up talks with @GodfatherOrwa & @XHackerx007 for real-world insights and tips
C140, Hall 5 #GISEC
Emad Abu Jazar of Positive Technologies, highlights the evolving threat landscape and the need for organisations to strengthen their defences while securing AI systems, critical infrastructure and cloud environments - https://t.co/G7xwmjMLtk @PTsecurity_EN
🚨 New #FamousSparrow campaign: meet SquawkDoor
Our Threat Intelligence team at PT ESC has uncovered a new campaign by the East Asian APT group FamousSparrow. The group used a new backdoor we named SquawkDoor, along with an updated version of their known #SparrowDoor backdoor.
🎣 The group injected malicious JS into websites across multiple countries. Visitors saw a fake "certificate error" in their own language, urging them to download a "new certificate." In reality, the file was an MSI installer — and running it infected victims with the backdoors.
🔍 We took a close look at both tools: how SquawkDoor works, what's changed in SparrowDoor, and how they relate to #HemiGate, #TernDoor, and #CrowDoor. We also found several overlaps with other threat actors from East Asia.
🕵️ Separately, we identified a pentester linked to the group who was preparing attacks. Our Medium article reveals what kinds of applications this hacker had targeted before.
Read: https://t.co/YacJSOdcYU
#Malware #Backdoor #APT #ThreatActor #EarthEstries #SaltTyphoon #GhostEmperor
24M+ sites run PHP. We found where it breaks
@ptswarm found 2 flaws in PHP's core database components. SQL injection (PT-2026-39443, CVSS 8.1) and a null pointer deref that kills the process (PT-2025-52599, CVSS 8.2). SAST won't catch these.
Patch now
https://t.co/ZMU97HInvT
Movie Night is back at ROOTCON 20.
Featuring Russian Reverse by Positive Technologies!
Popcorn and beer on us, while supplies last!
September 23 - 2000HRS
See you there!
#ROOTCON20#MovieNight
What defines cyber threats in 2026? Major trends revealed by our latest research:
1️⃣ APT groups and hacktivists merging
2️⃣ Rapid AI weaponization
3️⃣ Exploitation of weak auth data
Full data: https://t.co/H4dalFGHZQ
#ThreatIntelligence#Cybersecurity#Hacktivism