📣 Discover how you can achieve #DevSecOps excellence with our comprehensive, hands-on training programs.
📣 #BlackFriday sales are here and we've got a great deal for you. Up to 15% Off on all courses site-wide: https://t.co/iIEKo3UKMc 🔴
#security#appsec#productsecurity
🚨 83% of organizations studied have had more than one data breach.
Read the full report to understand the recommendations in order to minimize financial impacts of a data breach: https://t.co/2ZehpSAplz
#devsecops#databreach#cyberattacks#infographic#ibmsecurity
🚨 83% of organizations studied have had more than one data breach.
Read the full report to understand the recommendations in order to minimize financial impacts of a data breach: https://t.co/duHPA3ATVf
#devsecops#databreach#cyberattacks#infographic#ibmsecurity
Are you facing issues in integrating Security in your DevOps?
One of the most important DevOps trends today is the ambition to include security aspects throughout the entire lifecycle of an application: https://t.co/Qvkn8cGzIf
#DevSecOps#CSA2022#AWIS2022#InfoSec#AppSec
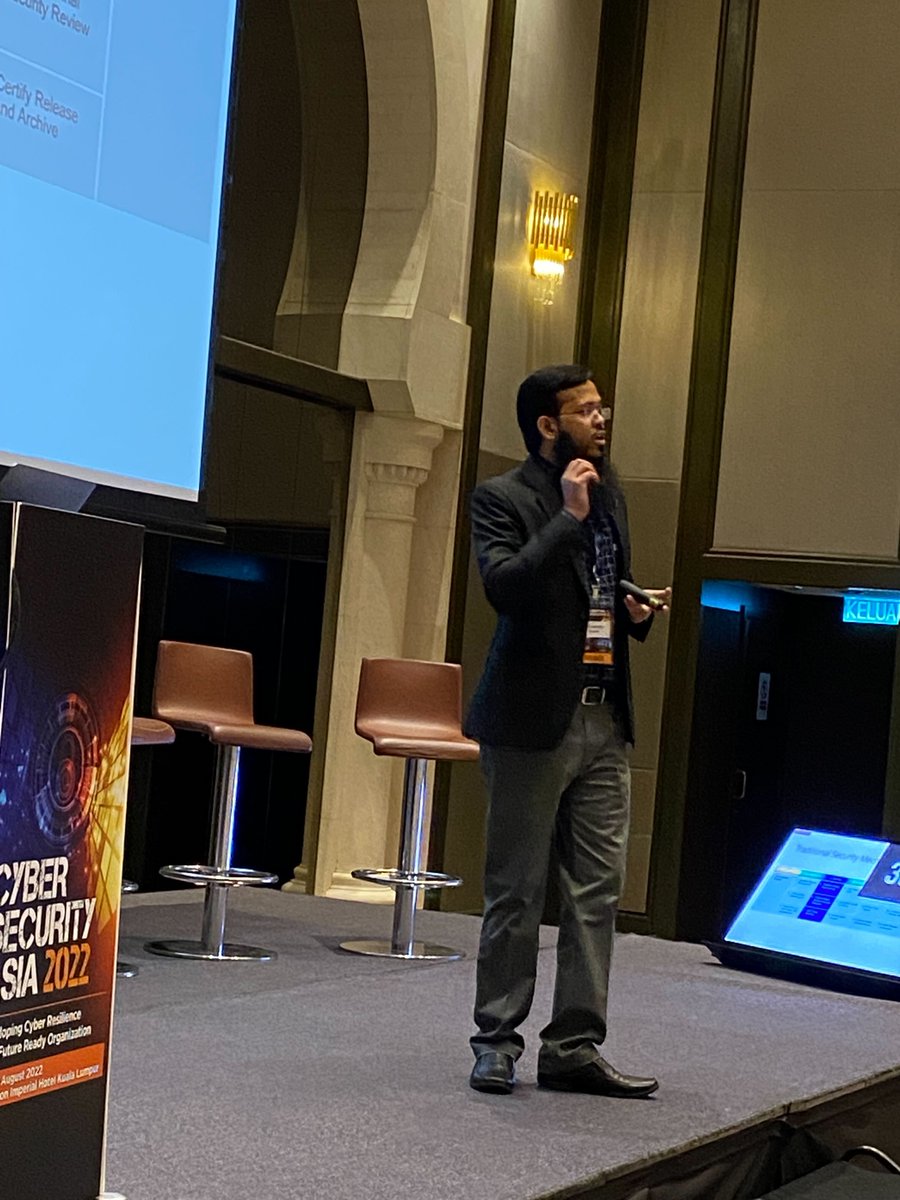
We're excited to speak at Cyber Security Asia 2022 about "DEVSECOPS BEST PRACTICES in 2022!
Learn about the latest in DevSecOps practices and how to apply them in their own organizations.
We hope to see you there: https://t.co/Qvkn8cGzIf
#DevSecOps#CSA2022#AWIS2022
🚨 In our latest blog "What is #ThreatModeling and How Does It Help?" , We explain what threat modeling is & how it can help you gain a practical understanding of threat modeling and the tools to automate it: https://t.co/ogvPpO5RHp
#devsecops#appsec#productsecurity#devops
Are you aiming to complete Practical DevSecOps Expert or Practical DevSecOps Professional? You can sign up for any Practical #DevSecOps Self-Paced Course between June 1st and June 30th 2022 and save 15%. https://t.co/tDXkENA6SW #CyberResilience
What a great #DevSecOpsLIVE it was! Did you know people have tried to organize & express Threat Modeling in many ways? We took a look at #ThreatModeling as Code, & explored its advantages & limitations. Missed it? Follow us for more upcoming #DevSecOps LIVE sessions!
What a great #DevSecOpsLIVE it was! Did you know people have tried to organize & express Threat Modeling in many ways? We took a look at #ThreatModeling as Code, & explored its advantages & limitations. Missed it? Follow us for more upcoming #DevSecOps LIVE sessions!
@PDevsecops Learn Container Security in a Vendor Agnostic way, check out the course curriculum at the below link
https://t.co/dK9cFz4p8C
#ContainerSecurity#DevSecOps
One of the questions we hear most often from our Students: “How can I become an expert in #DevSecOps tooling?”.
We answer that you have to find and learn 2-3 tools that can be widely used and play with other tools. 1/3
However, DevSecOps is not all about tooling. You need four things for DevSecOps Transformation in your organization: Culture, Automation, Measurement, and Sharing. Culture is probably the least appreciated aspect of DevOps/#DevSecOps but has the biggest impact on your org. 2/3