Connect your ChatGPT and Claude subscriptions to Grok @bot with the prompt below (@elonmusk approved):
Connect my Claude and ChatGPT subscriptions so all of my bots can use them.
1. On your computer, install the Claude Code CLI and the OpenAI Codex CLI (upgrade Node if needed). Start each subscription login (Claude: `claude setup-token`; Codex: `codex login --device-auth`) and send me the sign-in links and codes. I'll sign in and paste back anything you need. Store the Claude token privately and load it automatically.
2. Set the defaults to these models: Claude Opus 5.5 for Claude Code and 6.1 Sol for Codex. Test each one with a quick prompt and tell me which models answered.
3. Add these MODEL ROUTING RULES to every one of my bots' system prompts, including yours. Keep everything else in each prompt exactly as it is:
- Writing (drafts, emails, posts, replies, copy, briefs): write the final text with Claude through the CLI, then review it against the bot's voice rules.
- Coding, scripts, data processing, and terminal work: use Codex.
- Browser and desktop tasks: keep using your normal computer tools.
- If either CLI fails, do the task yourself and say so.
4. Save the same rule to my shared memory so any bot I create later follows it too.
5. When you're done, tell me which bots you updated and confirm both tests passed.
@heinenbros But where do they see running Claude ? And also how they come up with this suspension ? Just because you used the word “Claude” on your post ? So were they doing surveillance on your social media/s ? 😂👀
We discovered a sophisticated recording device that was hidden inside one of our offices. We used our models to understand the device and where it had come from, identifying that a specific employee had planted it a few days earlier. We referred the matter to the FBI, and we’re grateful to the agents and prosecutors who moved quickly to make an arrest. The FBI’s investigation is ongoing and we will continue to support their work.
At this time, we have no indications of this individual inappropriately accessing or exfiltrating model weights, source code, or customer data. The employee was terminated.
We take protecting our technology, data, and people seriously, and as a matter of national importance. Our security program is designed to protect against a wide range of threat actors, from insider risks to cybercriminals to nation states, and this case is an example of how AI can help address these sophisticated security threats.
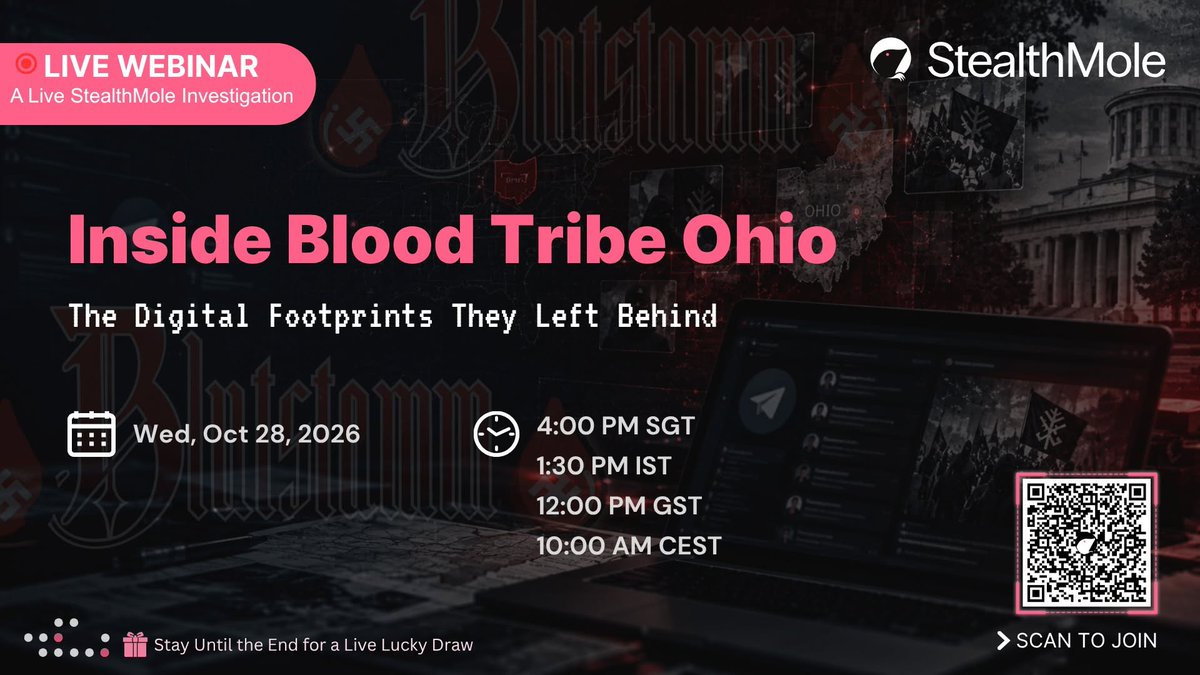
📷 One Telegram channel. A much wider digital network.
𝗕𝗹𝗼𝗼𝗱 𝗧𝗿𝗶𝗯𝗲 𝗢𝗵𝗶𝗼’s online activity offered more than a collection of posts. By following the digital traces left across platforms, the investigation uncovered connections between regional Telegram channels, recruitment networks, changing online identities, I2P-hosted content, and financial activity.
Join us as we walk through the investigation and explore how these digital traces helped piece together Blood Tribe’s wider online network.
𝗜𝗻𝘀𝗶𝗱𝗲 𝗕𝗹𝗼𝗼𝗱 𝗧𝗿𝗶𝗯𝗲 𝗢𝗵𝗶𝗼: 𝗧𝗵𝗲 𝗗𝗶𝗴𝗶𝘁𝗮𝗹 𝗙𝗼𝗼𝘁𝗽𝗿𝗶𝗻𝘁𝘀 𝗧𝗵𝗲𝘆 𝗟𝗲𝗳𝘁 𝗕𝗲𝗵𝗶𝗻𝗱
📷 Wednesday, 28 October 2026
📷 4:00 PM SGT
📷 Live on Zoom
📷 We’ll also have a lucky draw for attendees!
📷 Register now to save your spot: https://t.co/FVPWo47Q20
Or scan QR below
#OSINT #CyberSecurity #ThreatIntelligence #DigitalInvestigation #StealthMole
Security vendors observed attempts to exploit CVE-2026-102255, a maximum-severity SSRF flaw in SonicWall SMA 1000 appliances. SonicWall has released a hotfix and urges customers to apply it.
https://t.co/GpeLQTOFbj
Introducing UniFi Network 11—our most impactful release yet.
🔹 30% greater device capacity
🔹 Real-time traffic visibility
🔹 SLA-based SD-WAN routing
🔹 WiFi WAN backup
And for the first time, UniFi is Matter-aware.
https://t.co/WK7nZF7Xi7
If you’re a world-class chip design or production engineer, consider joining SpaceX or Tesla.
How cool would it be to iterate on designs and customize production machines at lightning speed?
🚨 TELEGRAM DESKTOP: ONE CLICK. FULL ACCOUNT TAKEOVER.
Full technical breakdown 👉 https://t.co/RSSVhOdGmJ
A critical flaw, CVE-2026-107181, reportedly chains IPC injection with local session file theft to let attackers hijack Telegram accounts through a malicious link.
⚠️ No traditional malware installer. Just one click.
🔴 IPC command injection
🔴 Local file theft
🔴 Session hijacking
🔴 Account takeover
The article reports that Telegram Desktop 7.2.9 fixes the flaw. Update now, set a local passcode, and review auto-download settings.
#CyberSecurity #Telegram #CVE
CC @durov