So it's up to you to fight for the righteous, destroy the evil
#United we shall stand, #united we shall fall
But if we stick #together and #conquer them, it was worth it all
It's time to spark a #revolution through the #underground sound
So get the fuck up, #people throw your fist up
Refuse to be treated like cattle, by forces with blind trust
The power of the #nation lies in it's #people.
This week has been quite a shitshow already, and there are still 2 days to go
Here’s a quick recap of the security mess we’ve seen in just the last few days:
1. PHP Core RCE (CVSS 9.2)
Two critical vulnerabilities (CVE-2026-109618/109619) allowing unauthenticated RCE. A huge number of PHP installations potentially affected, and there are already reports of reliable exploitation against patched versions. Great…
Useful links:
Official PHP advisory and patches:
https://t.co/XOos2fsRoy
Practical hardening and mitigation guide by Vincent Schmalbach. nginx/Apache configurations, PHP settings, patch verification and compromise checks:
https://t.co/30YfHmqIcR
Huntress analysis. What to monitor, suspicious child processes, webshells and post-exploitation activity:
https://t.co/XLx8za50cZ
Wiz technical deep dive. Exploit mechanics, memory disclosure, affected applications and the role of AI:
https://t.co/5HdgI3aM0f
Corelight’s open-source Zeek and Suricata detection rules:
https://t.co/eQdkc3vIpM
2. GitLab RCE (CVSS 10.0)
CVE-2026-110264. An integer overflow in the regex compiler leading to unauthenticated RCE. Apparently affects around 12 years(!) of GitLab releases.
https://t.co/APW5ihIOZ0
3. Node.js / Brotli RCE
CVE-2026-111497. An out-of-bounds write in the Brotli decoder that can lead to RCE when processing malicious compressed data. Node.js 22, 24 and 26 affected.
https://t.co/RUFjjKtfPE
4. DNS-over-QUIC DoS
CVE-2026-97206. A use-after-free in Unbound’s DNS-over-QUIC implementation. Remote attackers can crash affected multi-threaded DNS resolvers.
https://t.co/DxaIsMF2ZP
5. eMudhra CA disaster
And then there’s this absolute PKI clusterfuck. Eight intermediate CA private keys turned out to be ridiculously easy to reconstruct.
Browser vendors have started blocking the affected CAs, but outdated clients and applications with their own trust stores could keep accepting certificates from them. Cleaning up this mess is a lot harder than just patching a server.
Google’s analysis and response:
https://t.co/gvfGdOBibg
Mozilla’s public incident investigation, including the technical findings, timeline and eMudhra’s explanations:
https://t.co/K2wxEOneGJ
—
And I can’t help wondering how much of this sudden wave of discoveries has to do with the latest AI models getting better at code review and vulnerability research.
We now have models that can dig through massive codebases and potentially find bugs that have been sitting there for years.
I’m not saying these particular vulnerabilities were discovered using AI. I haven’t seen evidence for that. But I do wonder whether we’re starting to see some of the effects.
The eMudhra case is obviously a different story. That’s a spectacular failure of key management and quality control.
Anyway, quite a week. And it’s only Thursday…
“Who’s a good boy?!”
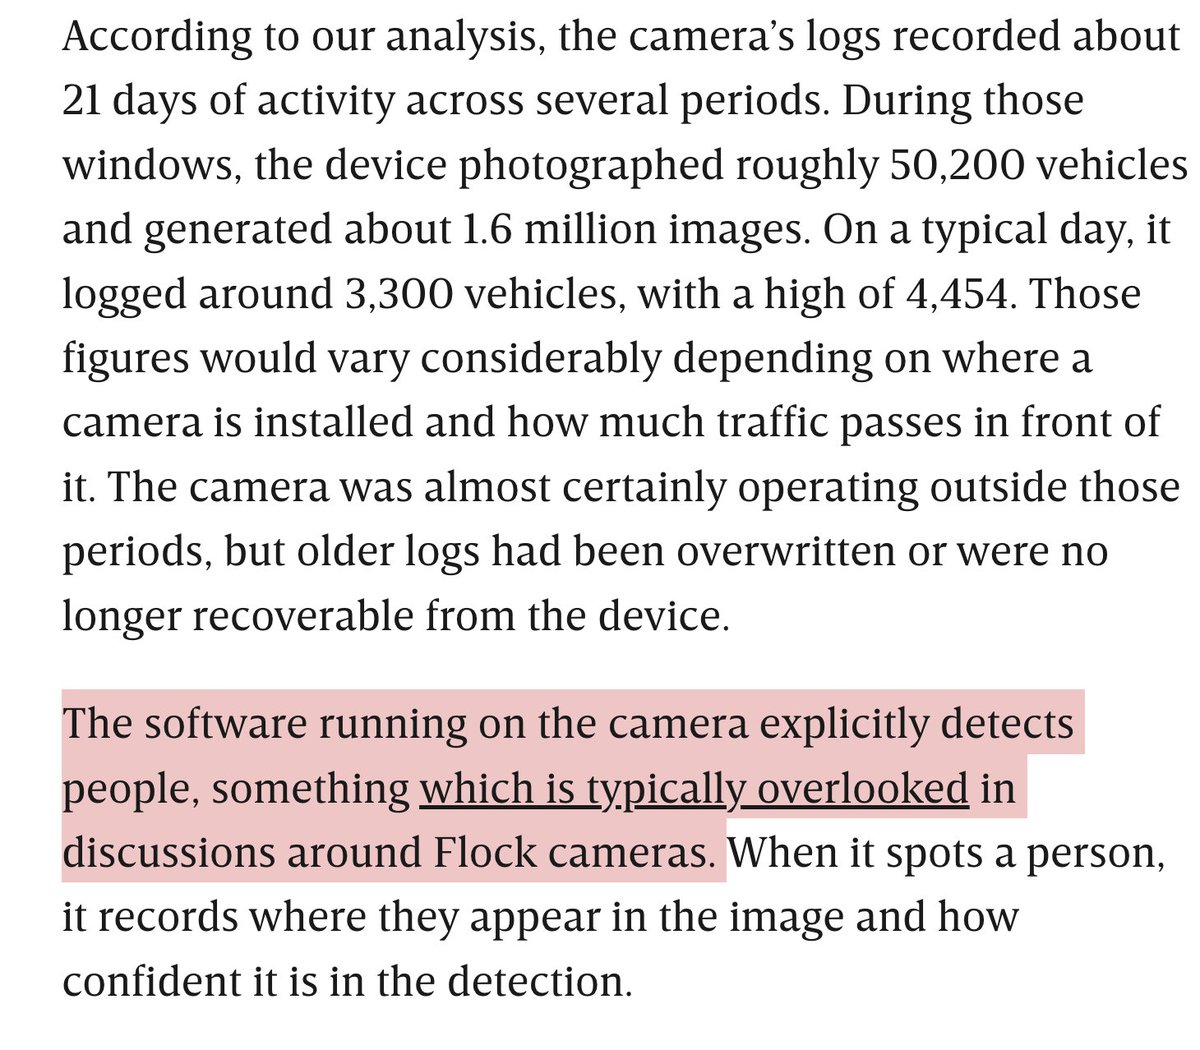
Hackers just dumped the contents of a Flock camera.
They found:
🔴Software explicitly detecting people, not just plates
🔴1.6 million images logged in 21 days
🔴Key to decrypt files stored on the device itself.
Finds directly contradict Flock, which claims someone with physical access can't access images.
Making it worse,@GainSec warned about the physical access issue more than a year ago & Flock downplayed it.
And yeah, the Flock camera logged “Who’s a good boy?!” about every 2 minutes, all while plagued with errors, crashes & reboots.
By @dmehro & @josephfcox
https://t.co/5a91FwVrPf
I resigned from Anthropic today. I spent the last three years doing pretraining research at both OpenAI and Anthropic. Neither company is acting responsibly. They are racing straight to self-improving superintelligence and gambling with our lives. More thoughts below.
Or… what if we gave you $100 in Codex credits if you tell us what you love about GPT-5.6 Sol or why you switched?
Tweet it, claim your gift, enjoy more usage. First 10k get the free tokens!
https://t.co/8mU93eA13i
🚨 BREAKING: Jamie Raskin confirms that calling Donald Trump a “pedophile protector” is factually grounded in the public record.
So don’t let them gaslight you.
President Pedophile Protector.
Say it louder.
DONALD TRUMP IS A PEDOPHILE
DONALD TRUMP IS A PEDOPHILE
DONALD TRUMP IS A PEDOPHILE DONALD TRUMP IS A PEDOPHILE
DONALD TRUMP IS A PEDOPHILE
DONALD TRUMP IS A PEDOPHILE DONALD TRUMP IS A PEDOPHILE
DONALD TRUMP IS A PEDOPHILE
DONALD TRUMP IS A PEDOPHILE
Obama: As for the president, he has been focused on critical issues like paving over the rose garden so folks don't get mud on their shoes and gold plating the Oval Office and building a ballroom… If you can't visit a doctor, don't worry. He will save you a dance. And if you don't get an invitation to the next white house shindig, you can always watch the festivities and all the beautiful people on Truth social.
Sen. Brian Schatz nails it:
“There’s enough money to bail out Argentina for $20 billion.
Enough money for Kristi Noem’s $173 million jet.
Enough money to renovate Trump’s White House ballroom.
What there isn’t enough money for—under this Republican government — is you.”
They never run out of cash for corruption, only compassion.
My 10 year-old daughter asked:
"Dad, are we going to get shot if we go to the march?"
THIS is exactly what Donald Trump wants our innocent kids to fear.
We refuse to be scared.
WE WILL SEE YOU THERE!!!!!
#NoKingsDayOct18th
If I were to call Pam Bondi a vile, lying, fascist, pedophile-protecting CUNT who belongs in prison for the rest of her natural life, would I get more followers or just more Russian bots flooding my timeline?