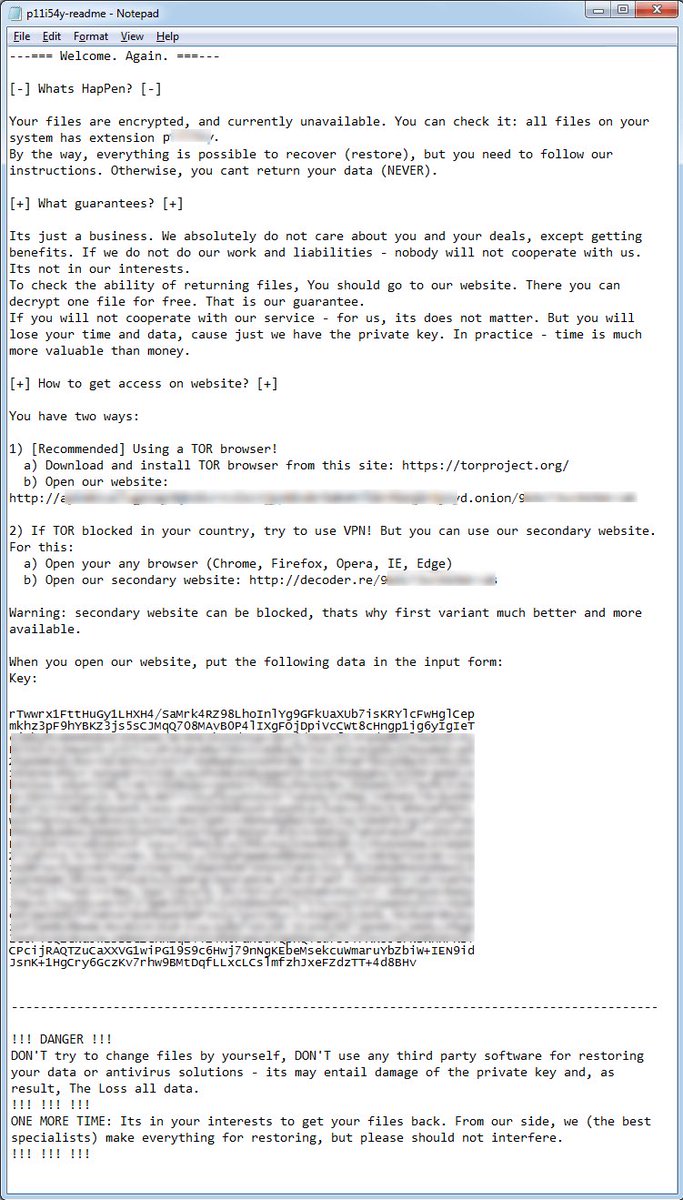
My teammates' insight into the previously undisclosed tooling, MDeployer and MS4Killer, used by #Embargo, one of the newly emerged RaaS #ransomware groups.
#ESETresearch analyzed new Rust-based tools, MDeployer and MS4Killer, used for deploying #Embargo ransomware and discovered when investigating attacks targeting US companies in July 2024. https://t.co/TUIIah9j1e 1/6
#ESETresearch You may have heard about #Grandoreiro resurrection after its disruption in January. This is not entirely true. In short: the disrupted Grandoreiro is different from the currently active Grandoreiro strain. Read further to learn more. 1/9
Following up, Spain’s @policia stated that over the course of 2 years they arrested a total of 133 mules in 🇪🇸 tied to #Grandoreiro. Their operation is directly linked to the one by Brazil’s @policiafederal where #ESETresearch played a crucial role. https://t.co/OofhL7Tm5d 1/4
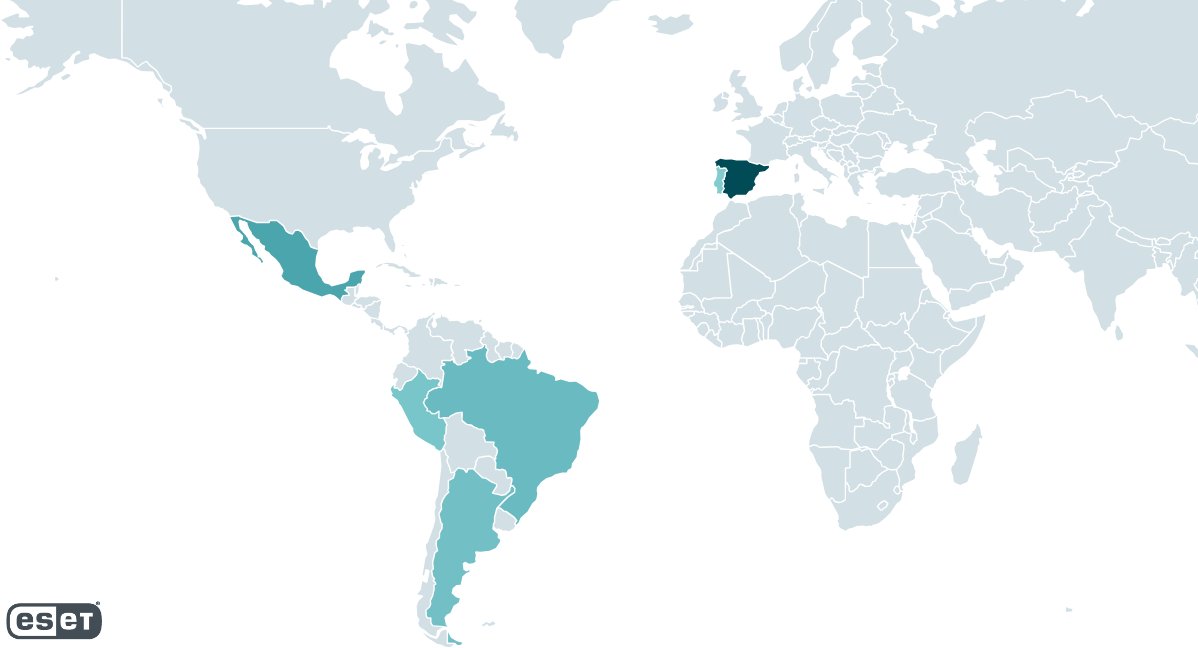
#ESETresearch aided in an operation to disrupt #Grandoreiro, a banking trojan targeting the general public in 🇧🇷, 🇲🇽, 🇪🇸 and 🇦🇷. ESET provided technical analysis, stats, and C&C addresses. https://t.co/4BdWV8hfui 1/4
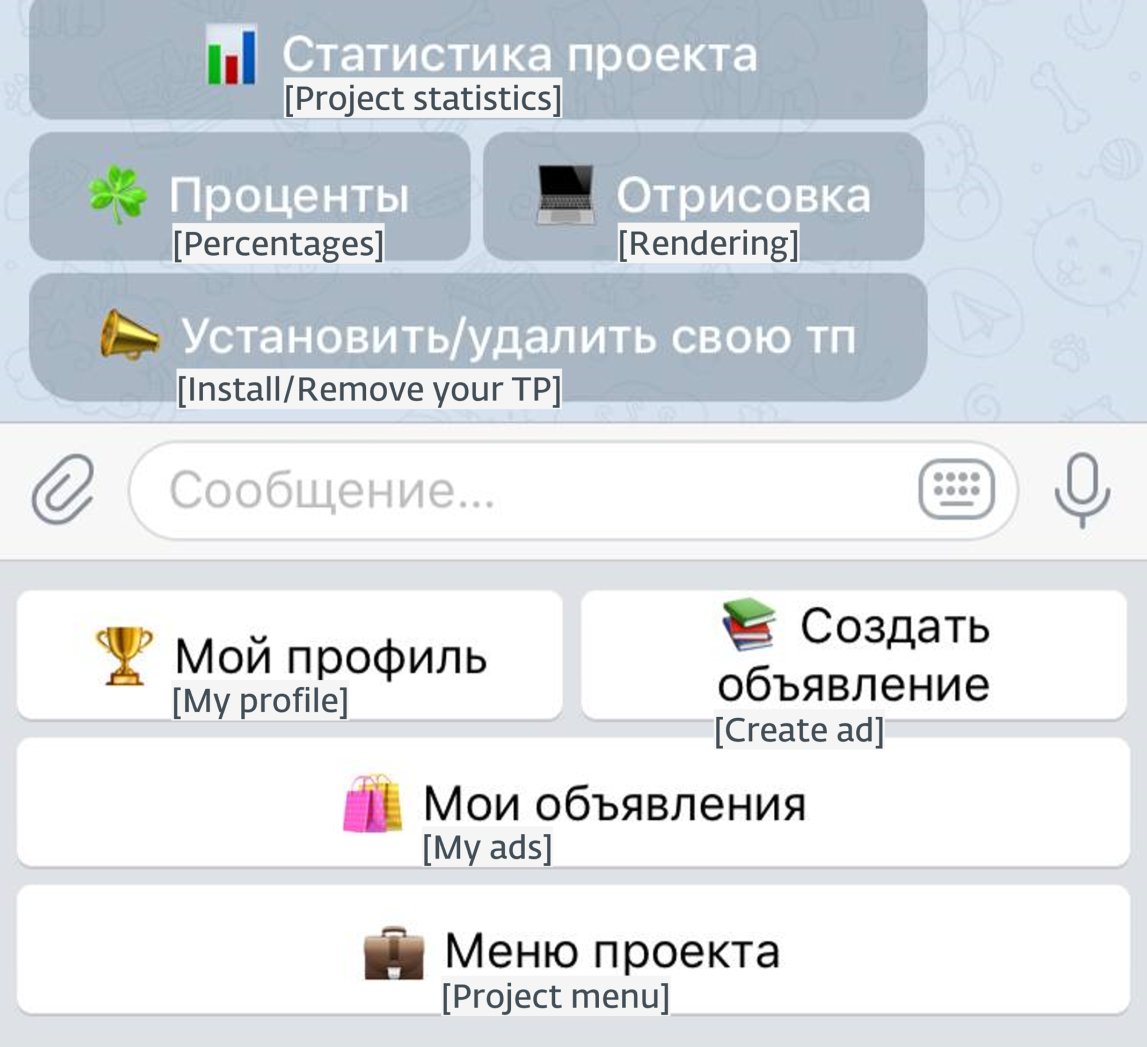
#ESETresearch discovered a toolkit that we have named #Telekopye. This malware is implemented as a Telegram bot that, when activated, provides easy-to-navigate menus that make scamming easier. 1/4
https://t.co/EtNWj8zUqf
#ESETResearch is hiring malware researchers for our 🇨🇦 🇨🇿 🇸🇰 offices. If you’d like to track some of the most impactful APTs/cybercrime campaigns, don’t wait and apply here 👇
🇨🇦: https://t.co/HLOAkkZNB7
🇨🇿: https://t.co/AbhB3Pi1oK
🇸🇰: https://t.co/1cKeEdAyBk
#infosecjobs 1/4
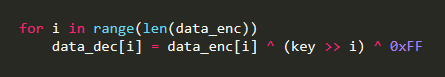
@dodo_sec@ESETresearch This is #Grandoreiro. Decryption key is 5658, algorithm pseudocode attached. Execution via DLL Side-loading. C&C http://ldaztag1sjthtjg.freedynamicdns[.]org, version (V12)(DNKL01PIX)1804. https://t.co/cRMJyAcqiH
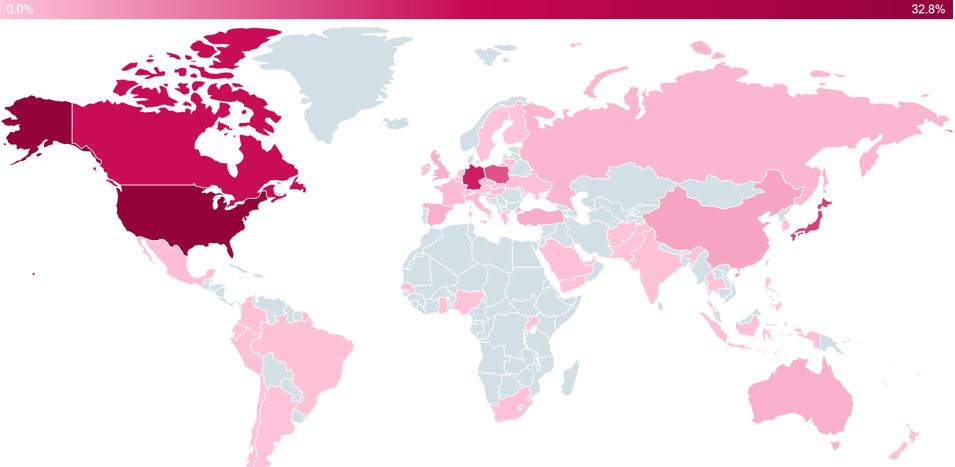
#ESETresearch participated in the action to disrupt the #Zloader botnets along with many partners. Our historical telemetry shows Zloader being distributed mostly in North America and Europe. https://t.co/2tNxFK7ixr @0xE9FBFFFFFF@jiboutin 1/3
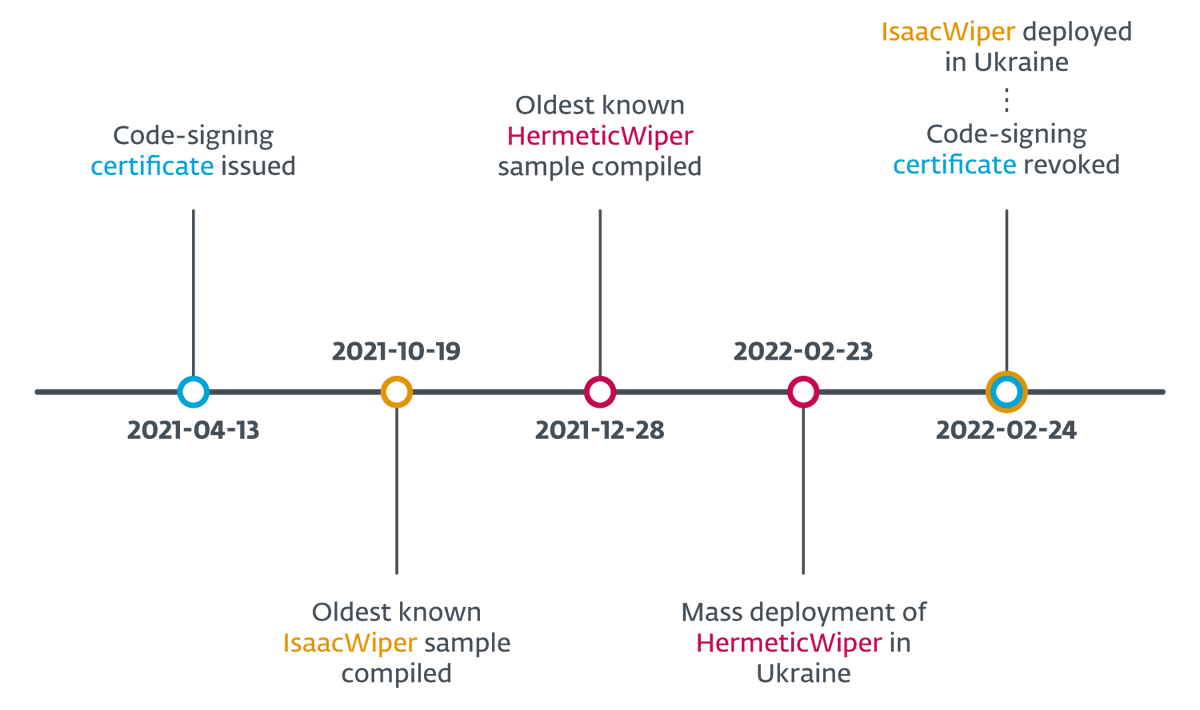
Breaking. #ESETResearch discovered a new data wiper malware used in Ukraine today. ESET telemetry shows that it was installed on hundreds of machines in the country. This follows the DDoS attacks against several Ukrainian websites earlier today 1/n
#ESETresearch identified a new non-prevalent variant of #Grandoreiro. The two most crucial changes are string table obfuscation and new targets from LATAM and EU 🇪🇺 countries, US 🇺🇸, Canada 🇨🇦, Australia 🇦🇺 and United Arab Emirates 🇦🇪. The DGA is slightly changed as well. 1/3
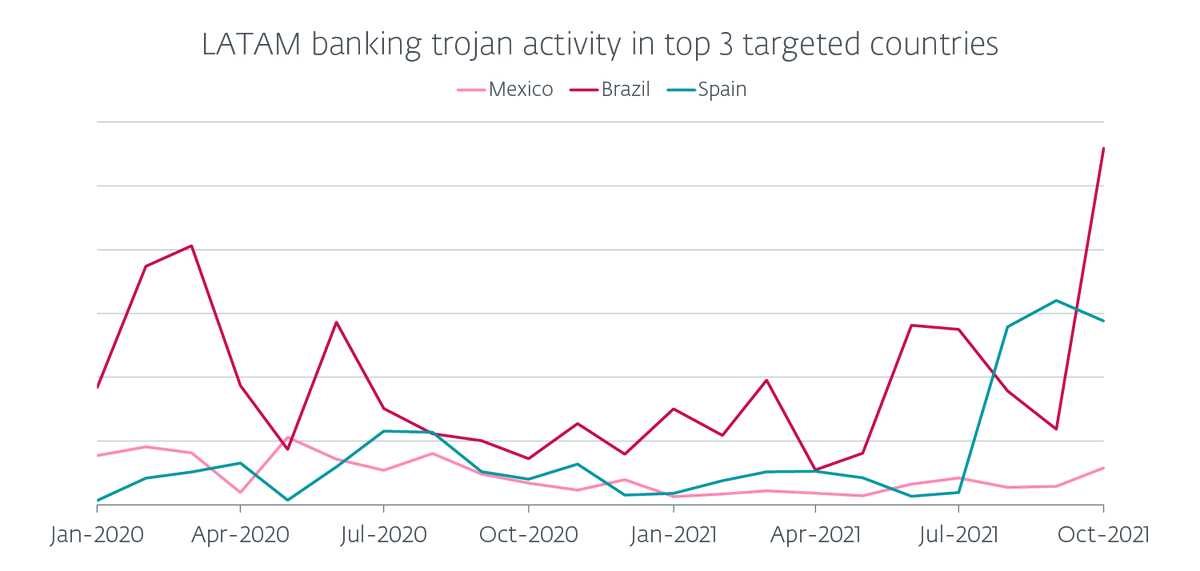
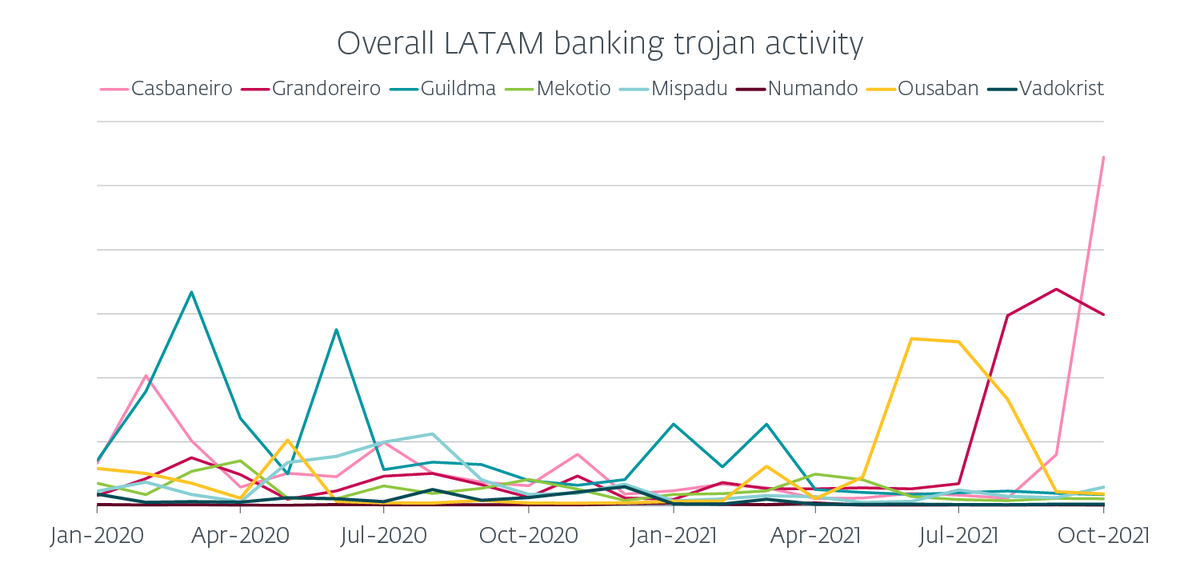
#ESETresearch concludes its LATAM banking trojan series. We look at how the scene changed in the last 2y, briefly describe Lokorrito, Krachulka and Zumanek, which became dormant before getting their own piece & hypothesize what the future might bring. https://t.co/BkWuMYekqV 1/3
#ESETresearch continues its series about Latin American banking trojans, this time featuring #Numando, a malware family targeting almost exclusively Brazil 🇧🇷 since at least 2018. @RoboSuman https://t.co/hl2MVTrdSI 1/3
16 people arrested in 🇪🇸 Spain due to connections to #Mekotio and #Grandoreiro, two LATAM banking trojans operating in Europe since 2020. https://t.co/tKOT1IhVJd #ESETresearch@SCrow357 1/5
#ESETresearch responded to ransomware deployed as supply-chain attack against #Kaseya VSA users attributed to #REvil beginning Friday afternoon EDT (US)/evening CEST (Europe). Detection was added for Win32/Filecoder.Sodinokibi.N on Friday shortly after.https://t.co/O6ESZMUMmQ 1/3
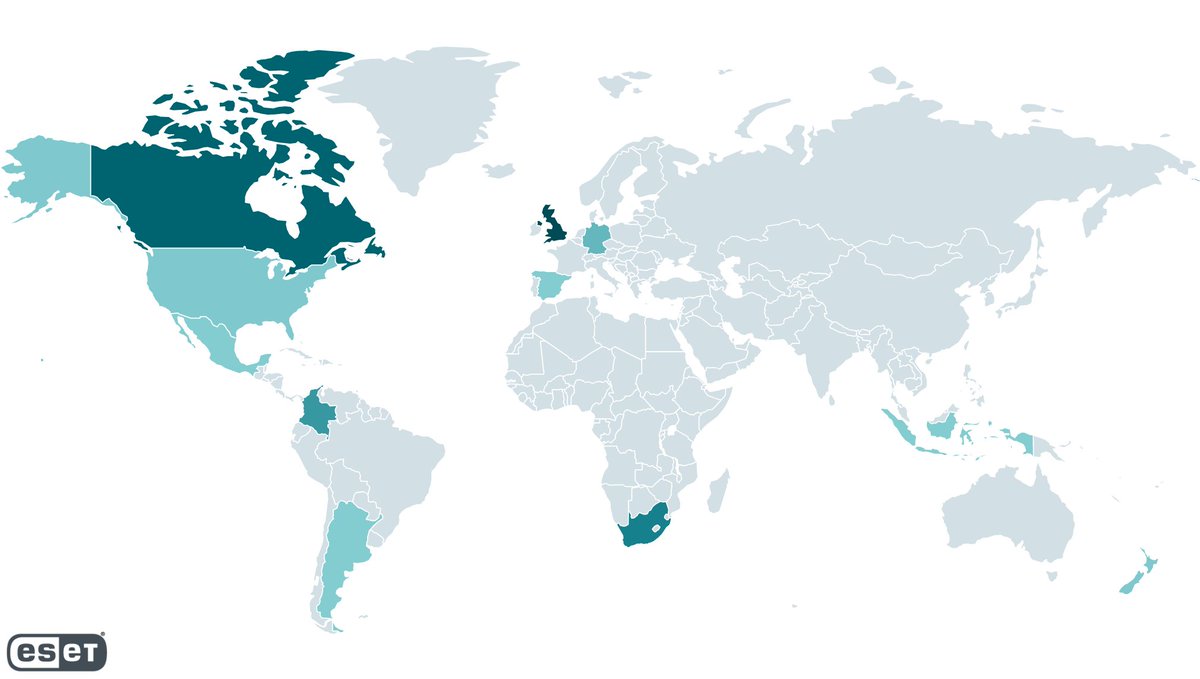
#ESETresearch telemetry shows majority of reports of Win32/Filecoder.Sodinokibi.N (#REvil) coming from 🇬🇧UK, 🇨🇦CA, 🇿🇦ZA, 🇨🇴CO and 🇩🇪 DE, followed by 🇳🇿NZ, 🇺🇸US, 🇦🇷AR, 🇮🇩 ID, 🇲🇽MX and 🇪🇸ES in decreasing order. @goretsky 1/2
#ESETresearch discovered a campaign distributing #Grandoreiro banking trojan targeting the US 🇺🇸. This is the first campaign of a LATAM banking trojan outside of LATAM and Europe we have observed. It is spreading via malicious ads leading to https://spotifyannounce[.]com. 1/4
#ESETresearch continues its series about Latin American banking trojans, this time focusing on #Ousaban, a malware family targeting Brazil 🇧🇷 since at least 2018. @RoboSuman https://t.co/qkJ0xz7H4e 1/4