Happy #BloodhoundBasics from @ScoubiMtl!
Want to map more of your environment in #BloodHound? The new in-app Marketplace links to:
• OpenGraph extensions
• Integrations that push or pull data
• Extensions and integrations in development
What happens when signing protections don’t stop NTLM relay?
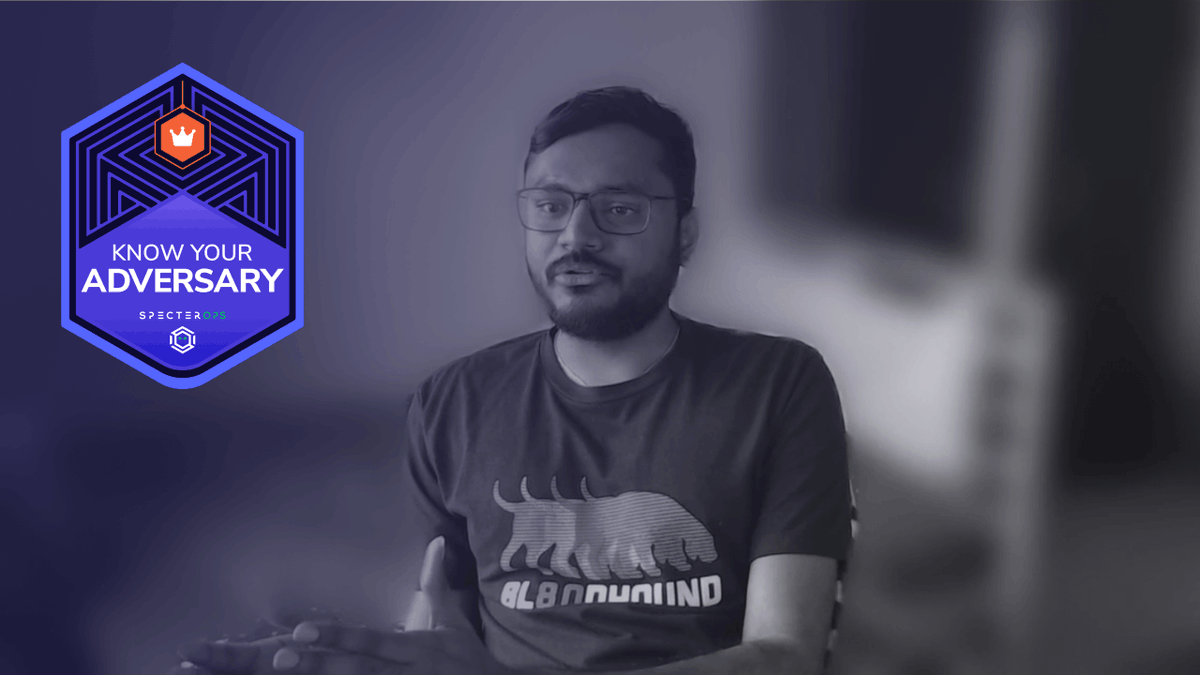
@GrayHatKiller joins #KnowYourAdversary to explain his SMB and LDAP signing bypass research, how Codex supported the process, and the lessons for defenders.
👀: https://t.co/77KyCb5acu
The FBI warns that some ARTEX-enabled intrusions reached privileged access in under three hours. We look at how mapping identity attack paths helps teams decide what to fix first:
https://t.co/Zg9lUIBO3m
Explore our #SOCON2027 training lineup: LLM Tradecraft, Identity-driven Offensive Tradecraft, Red Team Operations, and Azure.
Build practical skills through hands-on labs, with in-person and virtual options.
Browse the courses & register: https://t.co/hnVbhWcF3m
Go beyond Domain Admin.
Our Red Team Operations training at #BHEU explores lateral movement, persistence, and adapting to defensive responses.
Train with us in London, 7–10 December. Register: https://t.co/odSxiN5v6u
New in Tradecraft Academy: AWS for Red Teamers.
Get hands-on with AWS privilege escalation and lateral movement. Work through vulnerable labs and learn to chain techniques into cross-account attack paths.
Explore the on-demand course: https://t.co/YZJeUKaspi
We're heading to Las Vegas for #GartnerIAM, December 7–9!
Stop by Booth 227 to meet our team and learn how BloodHound Enterprise helps uncover identity attack paths and prioritize security risks.
Register: https://t.co/GxfSre0RUp
Tomorrow: Join @Ne0nd0g and @robwinchester3 along with @OpenAI’s Jack Lockhart and Hunter Reh as they explore frontier AI, security testing, and attack path validation.
➡️ https://t.co/ICBMbbfq8f
What happens when an everyday app becomes a SOCKS proxy? 🤔
Senior Security Consultant @skylerknecht joins @ScoubiMtl for our latest SO:Brief to discuss how attackers use apps to route traffic through enterprise networks.
Give it a watch! ⤵️
Gartner recommends measuring security performance by attack paths eliminated, rather than vulnerability counts.
Our take: Attack Path Management belongs in the work security teams are doing now.
@JustinKohler10 explains why: https://t.co/nqsfeaGw8C
Tomorrow: Join @Ne0nd0g and @robwinchester3 along with @OpenAI’s Jack Lockhart and Hunter Reh as they explore frontier AI, security testing, and attack path validation.
➡️ https://t.co/ICBMbbfq8f
Registration for #SOCON2027 is OPEN! 🙌
Join us April 26–May 1 for the conference, hands-on training, or both.
Learn more and start planning your week with us: https://t.co/hnVbhWcF3m
There's still time to submit a talk for #SOCON2027! ⏰
Share your research or practical lessons on identity security, adversary tradecraft, or attack paths before the CFP closes TOMORROW 11:59PM EST.
Submit 👉 https://t.co/1acXOkfTdZ
Happy #BloodHoundBasics from @StephenHinck!
BloodHound includes simple and complex edges. Our latest release keeps complex edges stable during graph analysis for both CE and Enterprise users.
Query with confidence, no matter your environment's status!
How can frontier AI and adversary tradecraft work together to uncover security gaps?
Explore security testing and vulnerability research with experts from SpecterOps and @OpenAI November 18, at noon ET / 9 AM PT.
Register: https://t.co/ICBMbbfq8f
BloodHound Enterprise is featured in Microsoft's Ignite Sentinel connector announcement!
Our integration brings identity attack path insights into Sentinel, helping security teams investigate identity risks and prioritize remediation.
Read more ⤵️ https://t.co/hI40aRd9W6
Our #SOCON2027 CFP closes this week! Have research or practical lessons on identity security, adversary tradecraft, or attack paths? We want to hear them.
Submit 👉 https://t.co/1acXOkfTdZ
Meet Sage: open-source AI for assumed-breach operations, built into Mythic. State your objective; Sage prepares commands for your approval in supervised mode.
@Ne0nd0g breaks it down in his new blog ⤵️ https://t.co/haYwfjObTc
What happens in the gaps between your security tools?
Join @Ne0nd0g, @robwinchester3 and @OpenAI's Jack Lockhart & Hunter Reh as they explore frontier AI, security testing, and attack path validation.
📆 November 18 | Noon ET / 9 AM PT
Register: https://t.co/ICBMbbfq8f