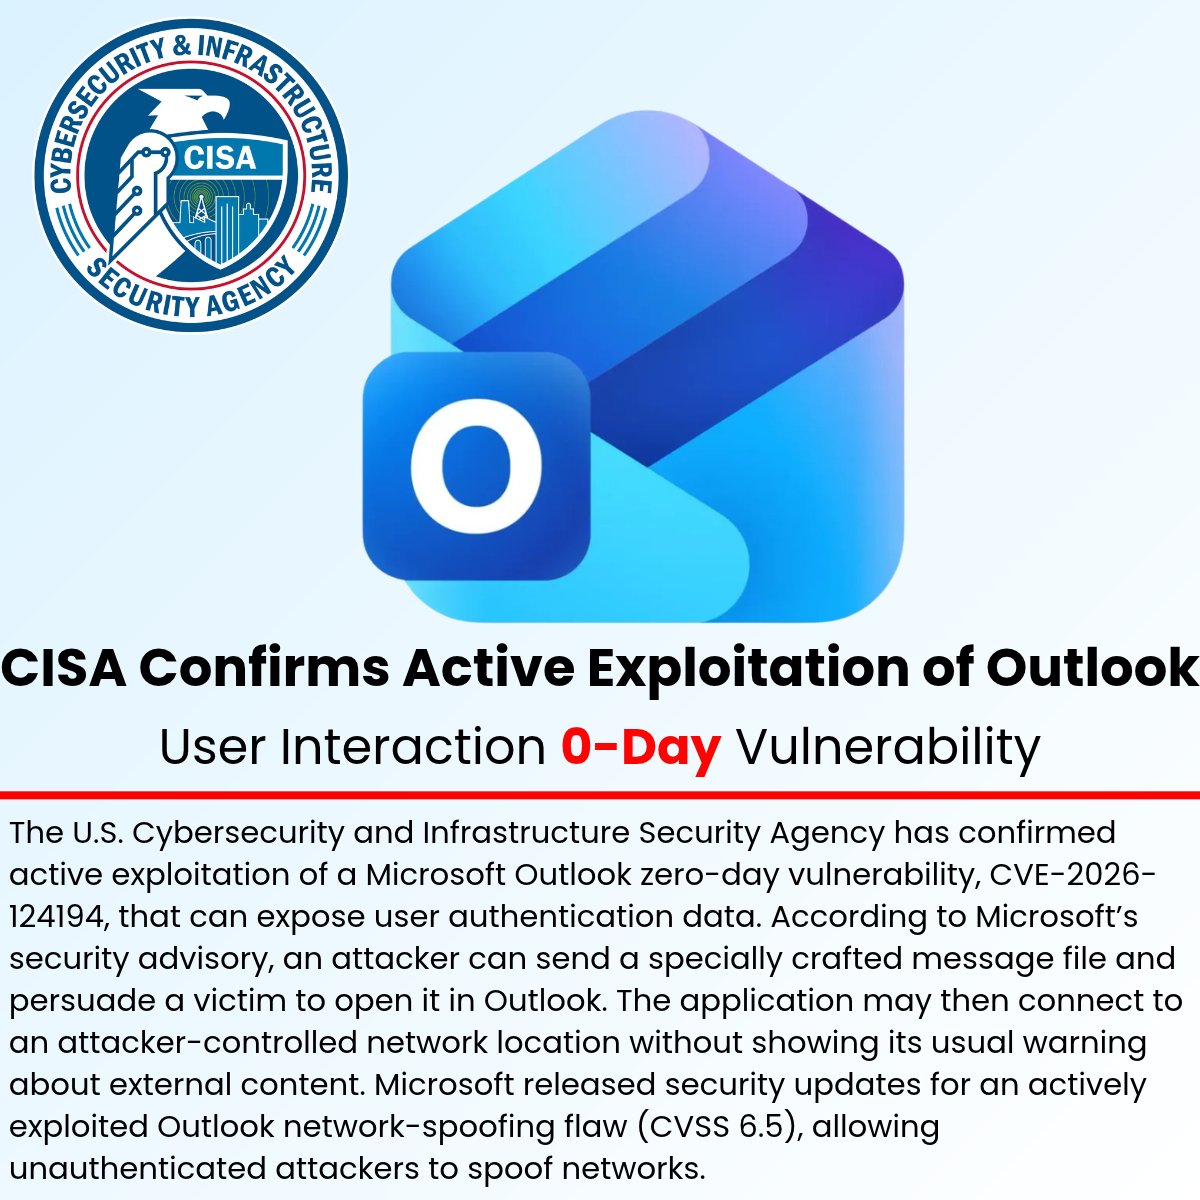
‼️ CISA Confirms Active Exploitation of Outlook User Interaction 0-Day Vulnerability
Details: https://t.co/9hqn7XHeqI
The U.S. Cybersecurity and Infrastructure Security Agency has confirmed active exploitation of a Microsoft Outlook zero-day vulnerability, CVE-2026-124194, that can expose user authentication data.
According to Microsoft’s security advisory, an attacker can send a specially crafted message file and persuade a victim to open it in Outlook.
The application may then connect to an attacker-controlled network location without showing its usual warning about external content. Microsoft released security updates for an actively exploited Outlook network-spoofing flaw (CVSS 6.5) that allows unauthenticated attackers to spoof networks.
#CybersecurityNews
Rust 1.100.0 has been released! 🦀💯🌈🎈
This bigger-than-usual Rust release adds the never type (`!`), the Allocator api, DropGuard, Box::map, Vec::from_fn, and more! Cargo now warns for unused dependencies, rebuilds less often, and adds the min-publish-age setting!