Your AI wrote the code. We check it before it ships
Weekly AI news, vibe-coding security tips & "Aster sits down with…" episodes.
First repo audit free 👇
I went live on launch day.
A viewer changed the 7 in his order link to an 8 and saw Sarah's name and address.
The login worked fine. Nothing checked whose order it was. ChatGPT explains 👇
Source: Tea's own statement, reported by Engadget (Jul 25, 2025).
2-minute check for your app: open your storage bucket's rules. If uploads can be read without logging in, fix that before anything else.
A dating-safety app asked women for a selfie and a photo ID to keep them safe.
In July 2025, about 72,000 of their images, including roughly 13,000 selfies and IDs, were sitting in a storage bucket anyone could open.
Nobody broke in. The door was never locked.
The full breakdown: how the crew walked in, the role trap, and the 3 locks with copy-paste code for Next.js, Express and Supabase:
https://t.co/OCuRzfPJXj
We hired a crew to rob our own app. It took 4 seconds: the admin button was hidden, but the API never checked who was calling.
The full breakdown: how the crew got in, the role trap, and the 3 locks with copy-paste code for Next.js and Supabase 👇 https://t.co/6ytF7lrC0y
We hired a crew to rob our own app.
The plan took three weeks. The heist took four seconds.
The admin button was hidden. The API never checked who was calling. Gemini explains 👇
We hired a crew to rob our own app. It took 4 seconds: the admin button was hidden, but the API never checked who was calling.
The full breakdown: how the crew got in, the role trap, and the 3 locks with copy-paste code for Next.js and Supabase 👇 https://t.co/6ytF7lrC0y
The full breakdown: what the fake looks like, why the signature check "keeps failing", and the 3-step fix with copy-paste code for Next.js and Express:
https://t.co/TkTEsF60Rf
Anyone can send an unverified Stripe webhook a fake "payment succeeded" and get your paid plan for free.
How it happens, why the signature check "keeps failing", and the 3-step fix with copy-paste code 👇 https://t.co/y7cDEoejzY
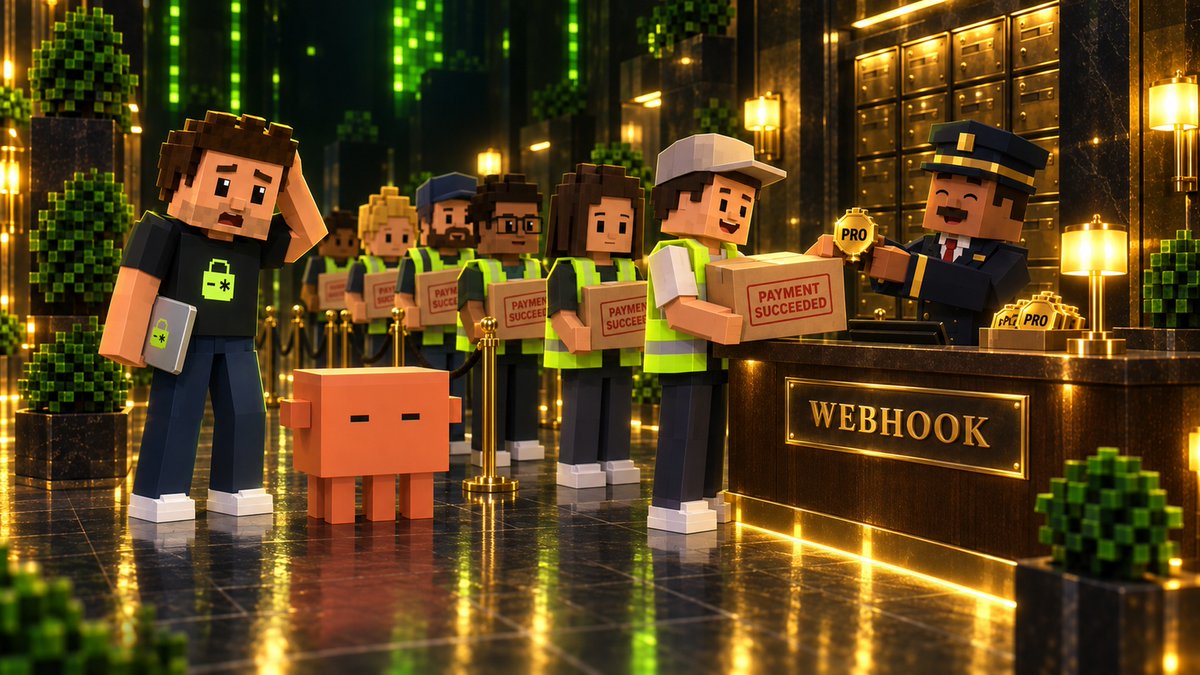
Your Stripe webhook is a doorman.
If it never checks the signature, it signs for anyone in a delivery vest, and one fake "payment succeeded" gets them Pro.
Aster asked Claude how it happens. Under 3 min 👇
Anyone can send an unverified Stripe webhook a fake "payment succeeded" and get your paid plan for free.
How it happens, why the signature check "keeps failing", and the 3-step fix with copy-paste code 👇 https://t.co/y7cDEoejzY
A URL isn't a password.
If your Stripe webhook skips the signature check, anyone can POST a fake "checkout.session.completed" to your server, and your app hands out Pro.
How it happens + the 3-step fix 🧵
Save this:
1. Verify the signature (constructEvent)
2. Use the raw body
3. Handle each event ID once
4. Give Pro only for verified events
5. Test with stripe listen + stripe trigger
Which one did your app skip?