🚨 ShinyHunters / SLSH: New Activity Observed — reported by #Team_D4rkn3ttz@jzzzz1qw
SLSH has publicly disavowed Aegis/Reyswap, claiming he is not affiliated with ShinyHunters or SLSH and accusing him of using the ShinyHunters name in a scam.
SLSH describes itself as an alliance comprising ShinyHunters, Scattered Spider, Lapsus$, and UNC6783.
The SLSH name was previously used by an alliance comprising ShinyHunters, Scattered Spider, and Lapsus$ that was active in 2025.
The SLSH-branded operation is promoting IntelForums and has announced plans to redesign its DLS.
The site features a claim of a breach targeting the Florida DMV on October 10, 2026. Posted filenames appear consistent with naming conventions previously observed in ShinyHunters DLS listings.
SLSH also claims to have seized control of an existing ShinyHunters account with approximately 13K followers. Since then, the account has been observed in a mutual-follow relationship with SLSH’s account and is being used to promote the SLSH identity.
#CTI #ThreatIntelligence #Cybercrime #DarkWeb
⚠️ 🌐 🕵️♂️ 🗄️ PREVENTION ALERT - NEW CLANDESTINE CYBERCRIME FORUM (INTELFORUMS)
[STATUS: ALLEGED / ACTIVE / PLATFORM DETECTED: INTELFORUMS / DATE: NOVEMBER 10, 2026]
Centralized cyber-intelligence systems have intercepted the registration and launch of a new exchange platform within the underground economy (registered on November 10, 2026). The clandestine portal, identified as IntelForums (intelforums(.)cc), has begun operating as a meeting point and discussion forum for individuals involved in the trade of data and breach-related intelligence.
The forum’s user interface, navigation sections (Forums, Archive, Resources, Upgrades, Shoutbox, Online), and active user profiles���operating under aliases linked to the coordination of massive data leaks—have been identified.
#IntelForums #CyberCrime #UndergroundForum #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
This is obviously fake/scam. Anyone who has private keys won't "sell the data", they will move the funds. Saw it yesterday, thought it was obvious, but still many media went with it for the headlines.
This is obviously fake/scam. Anyone who has private keys won't "sell the data", they will move the funds. Saw it yesterday, thought it was obvious, but still many media went with it for the headlines.
UPDATE: Binance dismisses ShinyHunters’ alleged 335M-user data breach as a likely scam
A Binance spokesperson has told https://t.co/wdIuaMxgOm that the exchange's preliminary investigation found no evidence of compromised systems or customer data, questioning claims that the dataset contains passwords, KYC documents and private keys; Binance suspects the information may come from infostealer malware targeting individual devices.
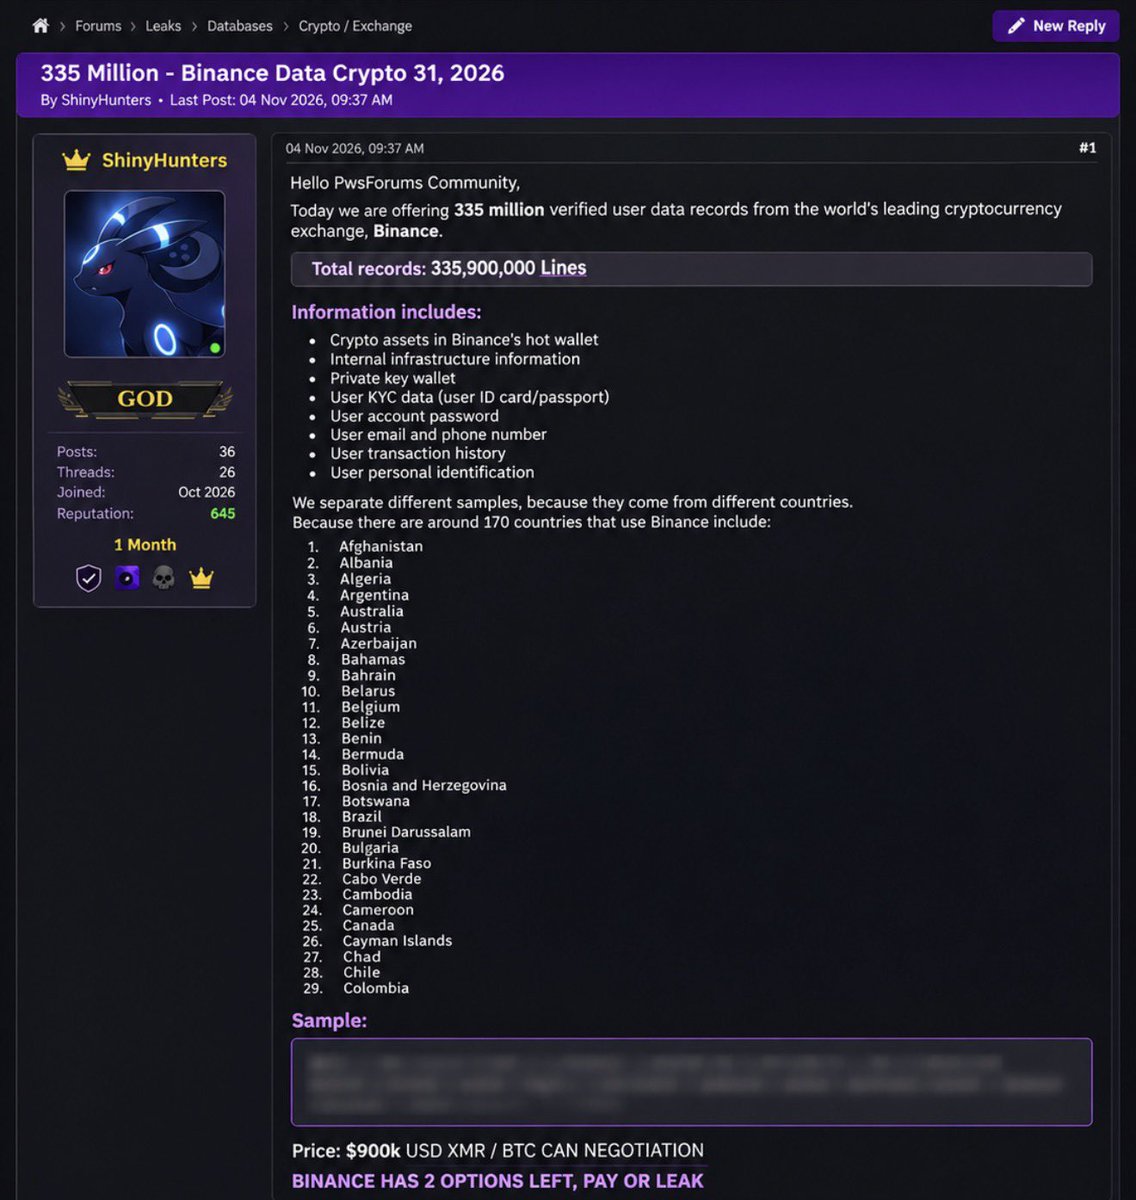
⚡️UPDATE: Binance says a $900,000 listing claiming to offer 335.9 MILLION user records is likely a SCAM.
The listing, attributed to ShinyHunters, claims to include readable passwords and external wallet keys.
Binance says it stores neither and has found NO evidence its systems, customer IDs, logins or wallet keys were compromised.
The probe continues. Binance says similar listings have used data stolen from users’ devices by malware.
.@binance has responded to ShinyHunters’ alleged 335M-user data breach, calling it a likely scam.
A group calling itself ShinyHunters claims to be selling 335,900,000 lines of data allegedly linked to Binance!
They claim the dataset includes KYC documents, passwords, transaction histories, and even wallet private keys.
Several versions of the listing have surfaced, asking between $500,000 and $900,000.
They even gave Binance an ultimatum: “PAY OR LEAK.”
If they really had access to private keys controlling significant amounts of crypto, why would they sell everything for just $900,000? 🤔