Another party in Moscow 🇷🇺 sponsored by cybercrime ZELENKA / LOLZ forum, featuring their LOLZTEAM marketplace for stolen accounts. A party for Halloween 🎃
Allegedly “attended by over 5,000 people” and with famous rappers like “Fortuna 812” on stage
And allegedly a safe place to meet between threat actors, discuss about gray and black activities and advice newcomers into the criminal field
NCTV: de capaciteiten en activiteiten van statelijke actoren en cybercriminelen nemen toe. De cyberdreiging vormt een ‘ernstig risico voor de nationale veiligheid’
https://t.co/0dEV6I4x6I
I am looking for my next role in cybersecurity!
If your team is hiring, or you know someone who is, please feel free to contact me.
DMs are open and any reposts or leads are appreciated!
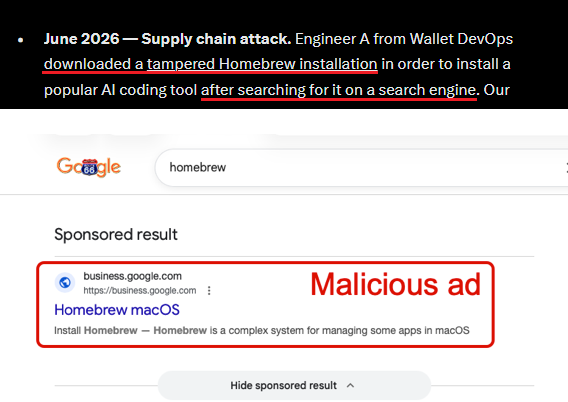
We at @MacHomebrew been warning @Google about this for years. Sadly, they are too addicted to making money selling malware ads.
If someone senior enough at @Google wants to talk about this or, ideally, just fix the fucking problem: I'm easily contactable online.
RTs welcome.
The domino that caused the Binance $6 Billion hack was a malicious Google ad.
1) Google has been getting away with profiting from ads for literal malware and phishing sites for far too long
2) Engineer A is retarded
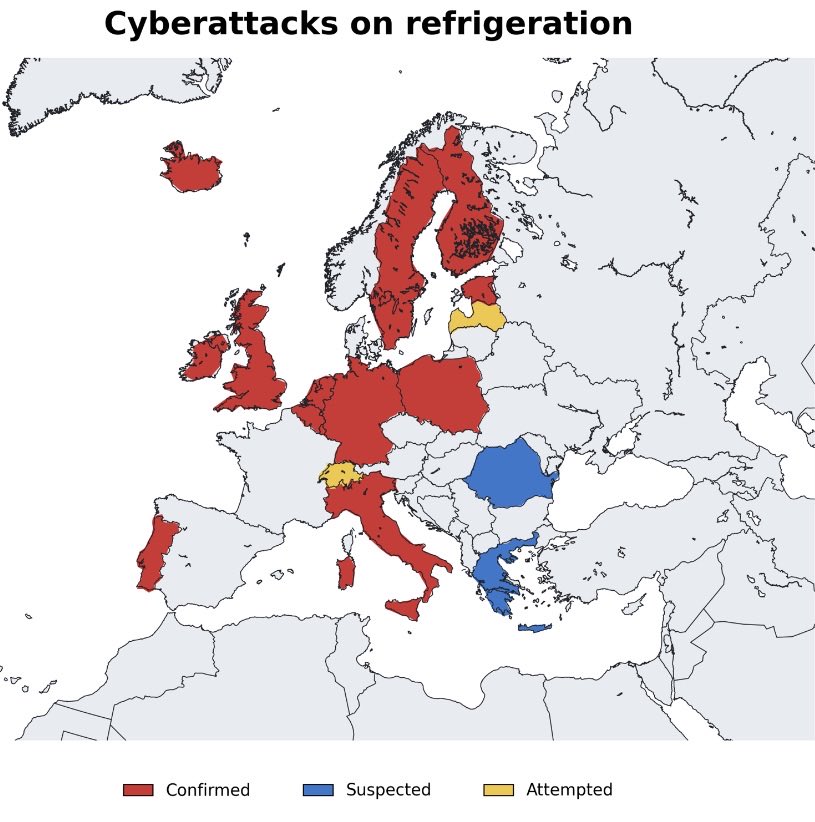
Dug into the freezer hacks for SentinelLABS: the timeline, how they work, and who might be behind them.
Russian-aligned groups have relevant history here. That’s not enough to say they did these attacks. Read more here:
https://t.co/oWycYl8OCj
I'm super curious as to who is behind all these. The only threat actor I could think of who'd be motivated to just randomly break fridges across Europe is Russia. They've funded a lot of sabotage operations that don't really seem to accomplish much, but they keep doing it.
Attacks will accelerate from here on - We are there: Six months ago I said Mythos like capability will be widely available. It's happening. A critical vulnerability, a social engineering attack that looks innocuous, or daisy chaining publicly available vulnerabilities and conducting a sniper strike is all being witnessed in the wild. Incident responders have never been busier.
Some key points:
- attacks are not becoming more sophisticated, it's the same attacks, faster and by a lot more people.
- attack path discovery which took trial and error and multiple attempts is now trivial, open source LLMs are here to help
- you are as secure as your supply chain, insecure down or upstream players who have access to your infrastructure could be the next attack path, marketplaces and supply chain is an easier vector
The increase in activity is a result of more people becoming better at hacking due to the ease of being able to attack. Had not contemplated that in my calculus.
Please:
1. Test your infrastructure for accessible vulnerabilities and misconfigurations
2. Fix your code and demand your vendors do.
3. Old infra, or insecure infra at the perimeter needs to be updated first
4. New AI tools, especially coding need a security framework. Your developers will do more with code, new skills, and more automation. Don't forget the coding models have trained on human code.
Stay safe this Halloween :)