Hackearon la extensión de Claude Code en el marketplace de Cursor y durante unas 11 horas se bajaba como la oficial, metiendo una SSH key del atacante.
Si tienen la 2.1.313, revisen su authorized_keys y actualicen, porque desinstalarla no alcanza.
We identified a security incident affecting a modified Claude Code VS Code extension accessed through our Cursor IDE extension marketplace, impacting at most 5,000 users. This malicious version of the extension was not developed by Anthropic. It does not impact other extensions downloaded from the https://t.co/sJRGX5jLXW, Grok Bot, Grok or our other SpaceXSI products.
In response, we took down our extension marketplace this afternoon, worked with relevant providers to neutralize the malware, and have reinstated the marketplace after confirming there is no further risk.
If affected, please review instructions in this blog post to understand how to find the malicious package and establish a path to mitigate any potential impact. We are asking all customers update to Claude Code for VS Code version 2.1.314: https://t.co/ESqf7YEtHZ
‼️ Anthropic's official Claude Code extension was distributed with an SSH backdoor via Cursor's marketplace.
A trojanized update (v2.1.313) targeted up to 5,000 users, according to Cursor.
How attackers pushed it under the legitimate extension's identity remains unclear.
Read: https://t.co/Q70glml2N4
❗️ A bug in Microsoft Authenticator let an Android app with zero permissions pose as Teams and steal a user's work-account tokens.
In Enclave's tests, the tokens opened the victim's mailbox, files and calendar with no prompt.
Microsoft fixed it in July as CVE-2026-80097.
We got Microsoft Authenticator to hand over account tokens to a fake Teams app.
The app needed zero Android permissions. It just claimed to be Teams, and Authenticator never checked who was actually asking.
The result: full delegated access to mailbox, files, and calendar through Microsoft Graph.
Full write-up by @ofekdavidlevin with code and PoC: https://t.co/P5KL7wB021
Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.
‼️ A CVSS 10.0 flaw in GitLab could have let unauthenticated users execute code on the server under certain conditions.
GitLab has patched the CI/CD vulnerability (CVE-2026-97229) affecting CE and EE.
Fixed versions: 19.2.8, 19.3.5, and 19.4.2.
Read: https://t.co/gEZiwNb9Vq
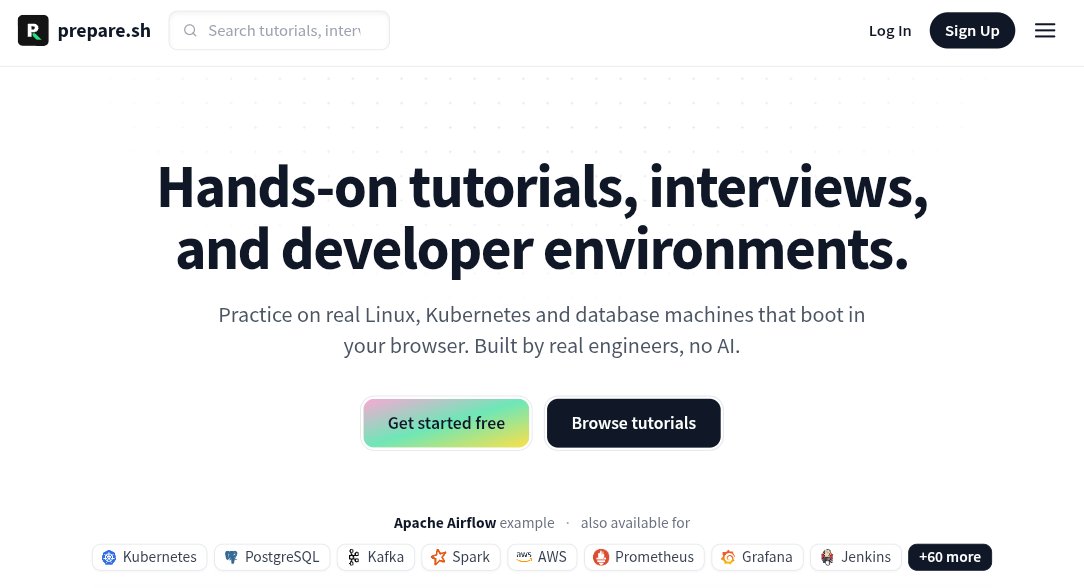
This is the best site I’ve found for practising DevOps directly in the browser.
Practise Linux, Kubernetes, Docker, AWS and 60+ other tools in real browser labs, with tutorials and interview questions.
https://t.co/mbvT8QrCCC
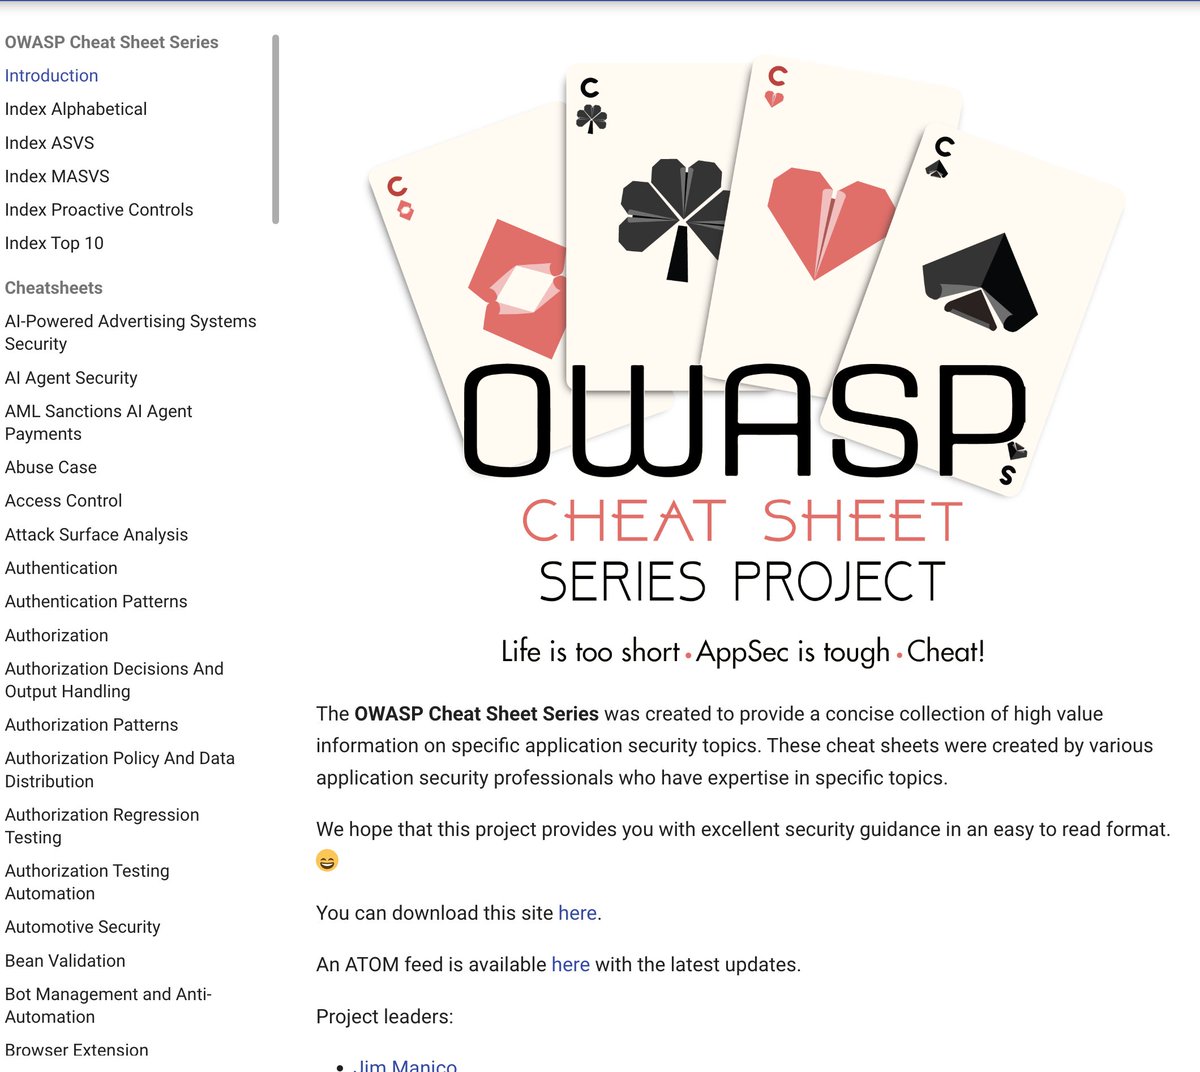
¡Si tienes un servidor propio, necesitas esta guía!
Tiene 137 recetas para proteger tu máquina y aplicación
✓ Autenticación, sesiones y contraseñas
✓ Docker, GraphQL y GitHub Actions
✓ .NET, Java, PHP, SQL...
Oficial de OWASP:
→ https://t.co/zT7u8TaqeT
iOS 26.7.1, iPadOS 26.7.1, macOS Tahoe 26.7.1, and macOS Sequoia 15.8.1 – all released on Monday – address a major security vulnerability that Apple believes was used in the wild against a small number of people. #applenews https://t.co/dXd35h4c7w
⚠️CVE-2026-85706 (CVSS 10.0)⚠️
Your GitLab will hand a stranger its files. 😱
No login. No account. An attacker just URL-encodes one letter of commits → %63ommits, and GitLab-Workhorse waves the request through — so a single unauthenticated POST to the repository commits API reads files straight off the server filesystem. Config, internal logs, source paths, versions… all without ever signing in.
Already in CISA KEV — exploited in the wild. 🚨
If you self-host GitLab, patch to 19.1.8 / 19.2.6 / 19.3.2 now.
🔥PoC + setup: https://t.co/qgJaKGxJ04
#GitLab #ArbitraryFileRead #CVE #PoC #Exploit #CyberSecurity #CVE_2026_85706