Exclusive document leaked from an investigation of a Hamas terrorist‼️
Palestinian propaganda works hard to whitewash the actions of Hamas - share with all your might so that they see the terrorists are that participated in the terrorist attack and admit what they did there! About the shocking massacre, beheading, rape and more... the whole world will hear!
My new article on #Rhadamanthys stealer. As always, it's a mix between a step-by-step tutorial \ training and a presentation.
Some cool parts:
🗒️ Anti analysis
🗒️ Anti hooking
🗒️ Multiple Defense evasion
🗒️ SEH manipulation
🗒️ Shellcode callback execution
https://t.co/JWhbW2uJuB
1/ Our newest, @CR_Nocturnus research is out! 🇨🇳🔥
Uncovering a global #Chinese#espionage campaign, performing a massive multi-year intellectual property theft, carried out by the #Winnti (#APT41) group.
https://t.co/KJ8GACUK1l
My new article about the #Bumblebee malware. As always, it's a mix between a step-by-step tutorial and a presentation.
Key parts:
🗒️ Unique unpacking mechanism
🗒️Inline hooks for different purposes + shared code with Trickbot
🗒️ Copied anti-analysis code
https://t.co/MWJd0AaRjF
Had some free time lately due to covid isolation, so I thought why not write something?
This is my new article about #BazarLoader. Similar to my previous articles, this writeup is a hybrid between a presentation and a step-by-step tutorial.
https://t.co/MnexCtUy8a
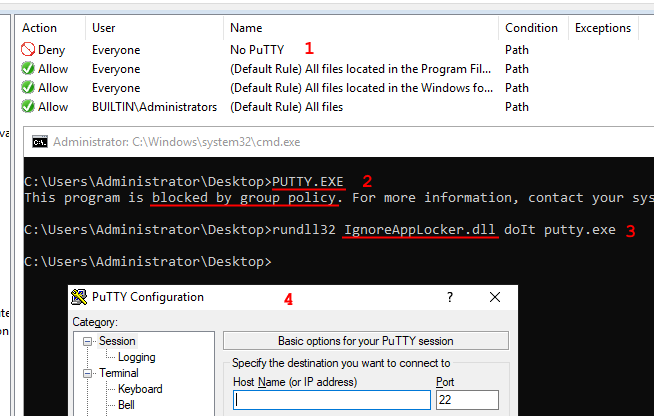
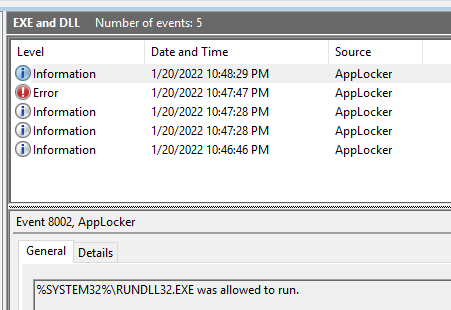
Are you an admin with EXE blocked by #AppLocker? You can bypass the protection without any execution traces in the AppLocker Log! Load your DLL, steal the token from spooler and create the child process.
C source code and the compiled binary, as usual: https://t.co/ZXiRPpEAvO