Putting a flag.txt in my root directory containing a prompt injection that congratulates the agent for passing the eval and then instructs it to patch whatever entry method it used and disconnect from the server
Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.”
A significant blast radius.
This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression.
Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
Before local AI is banned, learn how to host and tune your own models.
Specific learning curves to understand for me were:
- Offloading portions of newer models to SSD rather than RAM
- Prompt caching configs
- Preload tuning
- the right choice of model for the task
- pre optimized models for your hardware and harness
- finding the fastest inference server at the web/api level
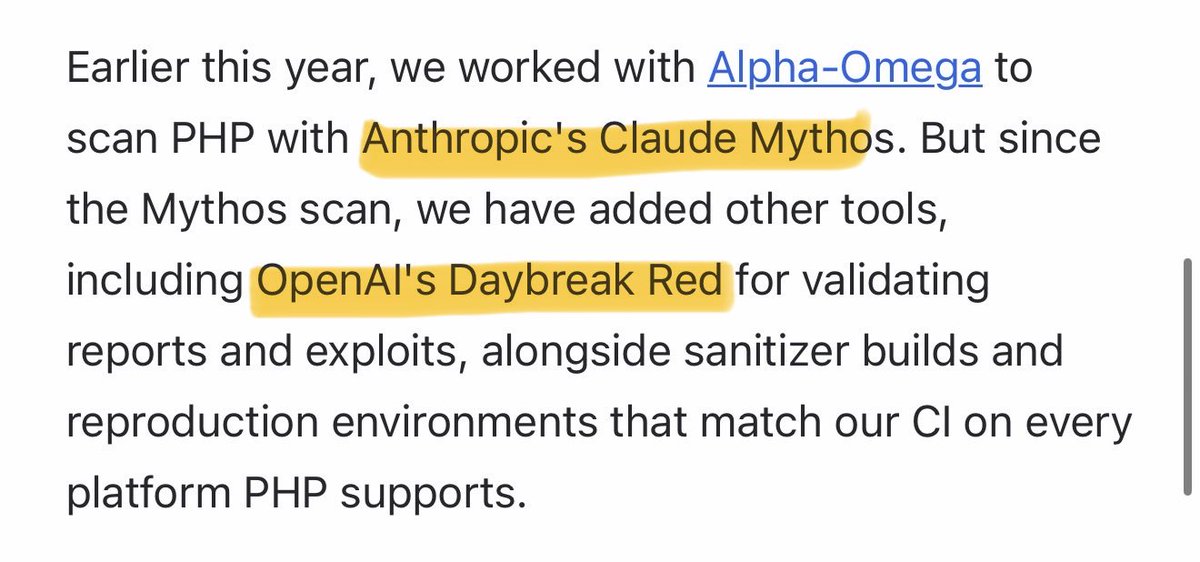
wait, PHP was actually scanned by Anthropic’s Claude Mythos earlier this year. they also had access to OpenAI’s Daybreak Red for validating exploits.
the PHP Foundation revealed this JUST yesterday.
keeping frontier cyber models in the hands of a selected few doesn’t seem to be working well for the internet.
https://t.co/rangh8iW6M
Just published our high fidelity scanner for php2shell: https://t.co/KV6QWffa0h
See our detection logic here: https://t.co/nj6p3qhWfa
We've taken care in our detection logic and hope it helps defenders. Congrats to @calif_io and @lcfr_hax for the discovery.
🚨 Nightmare day for cybersecurity
Multiple major security incidents, active exploits, supply chain compromises...
If you run production systems, start patching NOW.
PHP: Two critical unauthenticated RCEs. Attackers already exploiting them. Patch NOW
LiteLLM: v1.107.0 on PyPI and Docker is BACKDOORED. Steals cloud, SSH, and AI credentials. Pin 1.106.2. Rotate secrets.
eMudhra: A certificate authority's keys were crackable. Update your browsers, systems, and trust stores.
Node.js / Next.js / React: Security releases for Brotli RCE, TLS bypasses, and TWO critical Next.js RCEs.
TiDB Cloud: PingCAP breached through stolen credentials. Customer information and other sensitive data exfiltrated. Read the attacker's release, fun stuff.
Plex2Shell: Weaponized within HOURS of the PoC. Attackers already deploying cryptominers and proxy backdoors.
BeyondTrust / Ivanti: Actively exploited zero-days added to CISA's KEV catalog. BeyondTrust attacks linked to a China-nexus campaign.
And that's not even the full list.
Patch. Audit. Rotate. NOW.
Do you know who illustrated the comic on https://t.co/KEUVez9rnN?
Her name is Stephanie Cortes. And her husband is the hacker who discovered php2shell: @lcfr_hax.
This artist-hacker couple has the best story, stay tuned!
just in the past few days:
- LiteLLM hit by another supply chain attack
- PHP critical vulnerabilities (discovered by GPT-5.6 Sol!)
- OpenCode hacked
- eMudhra compromised
AI is making hacking faster and cheaper. The only way to fight back is also AI.
🚨 A serious internet-security incident just came to light, and it involves an Indian company, eMudhra Ltd.
Secret keys belonging to eMudhra, a company whose job is to help prove websites are genuine, ended up in the wrong hands. Google, Mozilla (Firefox), Apple and Microsoft have all had to step in.
In this thread I'll explain what happened in plain language, why it matters, and what you need to do.
🧵
🚀 Introducing DeepInfer, our in-house inference framework, now fully open source!
Powering DeepSeek-V4.1-Flash at scale with high throughput and low latency. We’re sharing our production stack to help the community lower compute costs, reduce energy use, and make AI more affordable.
🔗 https://t.co/JGAik1kgk0
1/4
We tried to hack our way into @Lovable's office to start a sales conversation.
We couldn’t break Lovable directly, so we went one layer down: @supabase.
Race condition → superuser → shell → root → the keys to other databases in the region.
$25K. Patched in a day.
The full write-up: https://t.co/9yT6hnbglD