I just published JWTs Explained: From Basics to Security 🔐. I documented the concepts in simple language.
In this write-up: JWT basics & structure, attack. Next, I’ll cover the practical JWT attacks and labs separately.
read it 👇
https://t.co/IqxhL8BLr0
@tryhackme Complete my first THM challange! 🏴☠️ Learned a lot about image OSINT, pivoting and following digital clues. Looking forward to the next room. 🚀
@tryhackme I'm learning VAPT and web penetration testing on @tryhackme . My dream is to become a Red Team Penetration Tester. A Premium subscription would help me continue building practical skills. 💜 #WomenInCyber
Cybersecurity is for everyone. 💚
Great opportunity for women who want to start, switch careers, or grow their skills in cybersecurity.
Free TryHackMe access available through this initiative. 🚀
Share with someone who might benefit.
#WomenInCyber#CyberSecurity#TryHackMe
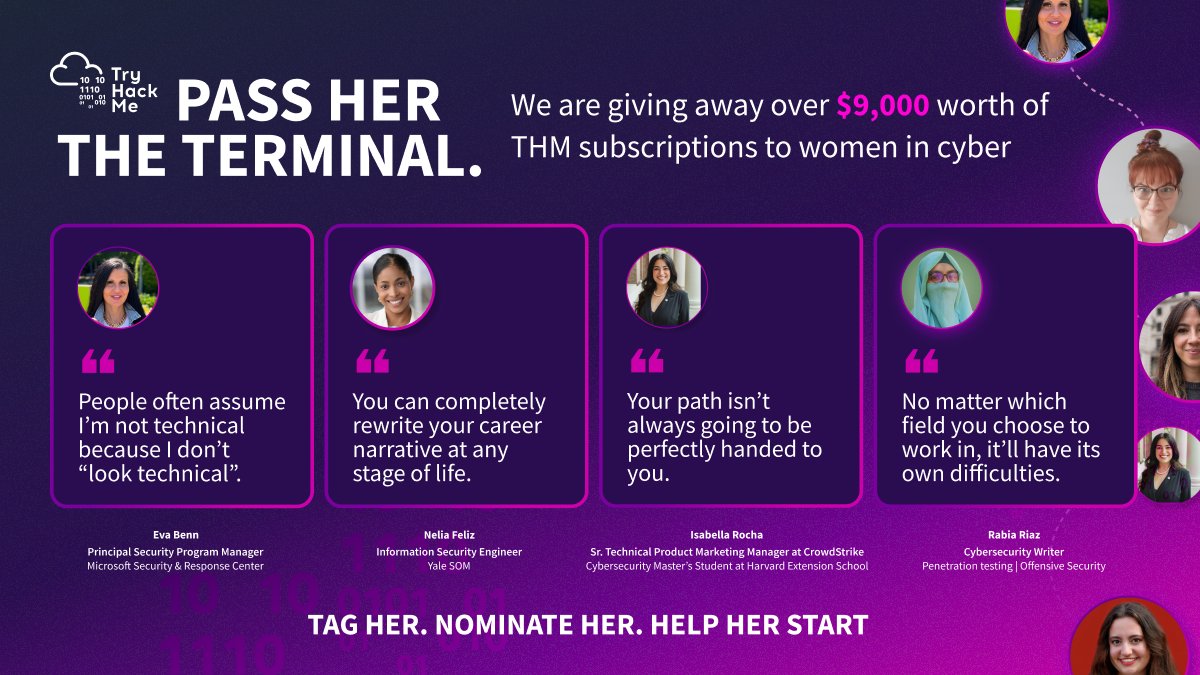
For the women ready to start, switch careers, learn, or keep going. 💜 Fill in the form to nominate yourself or another woman for free TryHackMe access.
To enter: ✨ Fill in the form ✨ Sign up to TryHackMe ✨ Share this post
▶️ https://t.co/Tf2iKOTjM4
You belong in cyber. 💚
For the women ready to start, switch careers, learn, or keep going. 💜 Fill in the form to nominate yourself or another woman for free TryHackMe access.
To enter: ✨ Fill in the form ✨ Sign up to TryHackMe ✨ Share this post
▶️ https://t.co/Tf2iKOTjM4
You belong in cyber. 💚
Just published a full LazyAdmin Walkthrough (TryHackMe)
Covered:
🔍 Web enumeration
🗂️ Sensitive data exposure
🔑 MD5 cracking
💥 Privilege escalation (sudo perl exploit) → ROOT
Read here 👇
https://t.co/UxHln1KGGJ
#pentesting#tryhackme#ethicalhacking#redteam#lazyadmin