4300 requests done through MCP so far.
And that's with the closed beta users only.
How many vulnerabilities are you finding with @immunefi Studio MCP?? 🤯
Banned from Immunefi? Now there's a way back in.
A run of invalid reports can lock your account out of submissions.
The new Immunefi Studio Academy gives you a path back: pass a short skills assessment and your access is restored automatically.
Enrolled → Pass → Reinstated ✅
Invite-only for now. DM me for access 💬
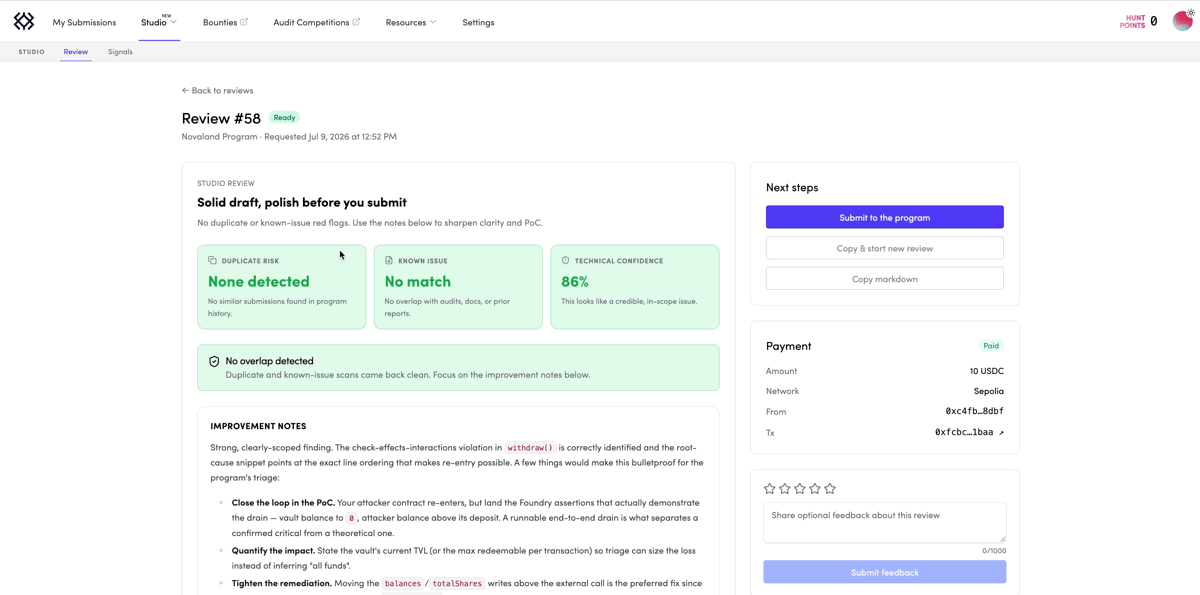
Studio tells you what's wrong with your bug bounty draft. Now your agent can fix it.
Shipped a copy-as-markdown button. One click grabs the whole review: dupe scans and the weak spots. Paste it into your agent, it patches the draft, rerun until the review comes back clean.
The review used to be stuck on the page. Now it goes where you actually work.
What's your daily driver? Reply "Claude", "Cursor" or "Codex"
You spot something odd on Monday, and by Thursday you've lost the thread.
So we built notes into Immunefi Studio: log your progress and tag the targets right on the program.
Scope, Signals, and your intel all in one place.
Reply "notes" and I'll get you in.
Bounty scopes change, catch every change the moment it happens.
We added scope tracking to Immunefi Studio, right beside Signals. Review how scope and rewards moved.
New target added? Time to hunt.
A few spots remain. Reply "scope" and I'll get you in.
We just published the fairest comparison of audits vs. audit competitions ever done.
Contests win hands down.
Help us make sure every founder reads it.
Contests will become the new standard.
Friday I said 10 retweets and I ship it by Monday, and you delivered.
Duplicate detection is live in Studio. It checks the program's history for overlap before you submit.
Retweeters get first access. Ping me.
I’m an engineer at Immunefi.
My advice to any researcher: don't submit cold.
Run it through Immunefi Studio first. It catches the weak spots that get reports closed. 65% of beta runs last month came from newer researchers. They checked before they sent.
Reply "studio" if you want in 🛠️
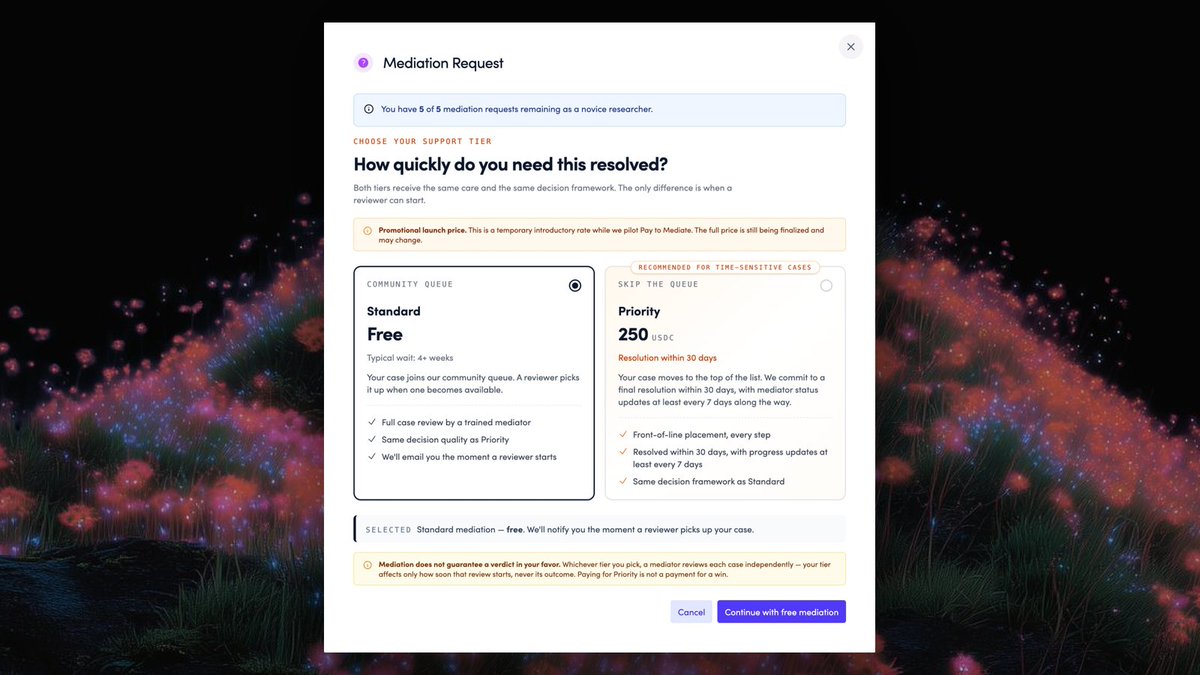
Just shipped on Immunefi: Priority Mediation.
For a while now, security researchers have been telling us the same thing: when you've put real work into a report and you believe in it, waiting weeks for a mediator to pick it up is brutal.
Priority Mediation now lets researchers who are confident in their submission pay to get faster resolution with a hard commitment: resolution within 30 business days, mediator status updates at least every 7 business days along the way.
A couple things I want to be explicit about, because they matter:
1) Free mediation requests are reviewed by the same trained mediators, using the exact same decision framework.
2) The tier you choose affects the queue, not the verdict. A paid mediation does not buy you a favorable outcome. It buys you speed and additional hands-on activity. Every case gets the same impartial review, full stop. If we ever blurred that line, the whole system would be worthless.
This is one of several changes we're shipping based on direct researcher feedback.
Keep it coming so we can usher in SR Summer.
Today, we're announcing that Immunefi is partnering with @code4rena to onboard their bug bounty customers to our platform following Code4rena's decision to wind down operations.
Code4rena played a huge role in shaping crypto security, and they deserve real recognition. As they wind down, our focus is to make sure every protocol continues to receive top-tier security.
We're working hand-in-hand with the Code4rena team to make the transition as smooth as possible.
Protocol teams onboarding to Immunefi will get:
* Access to the largest and most elite whitehat community in crypto
* Professional triage and mediation, battle-tested across $135M in bounties paid
* Dedicated migration support to port over scope, rules, and reward structures
And to every C4 warden: we want you here. You've been the backbone of one of the most respected security communities in crypto, and your work has made this industry materially safer. Come join us in continuing that mission. We're committed to picking up the banner Code4rena raised around improving the whitehat experience.
A sincere thank you to the Code4rena team for trusting us to carry this forward, and for putting their customers' security first throughout this process. The industry is better for what they built.
Onward.
That's more payouts and more hacks prevented than every other security platform combined.
So many more Whitehat wins coming. If you're not using Immunefi, you're not taking security seriously.
After almost five years, I'm no longer at @immunefi
I built and led the Managed Triage Service from the ground up. Hired the team. Wrote the playbooks. Triaged thousands of vulnerability reports and helped mediate one of the largest payouts in the history of Web3 security, and plenty more behind closed doors.
I'm proud of what we built and grateful to everyone I worked with.
Now I'm looking for what's next.
I'm looking for a leadership position in security. Joining an existing team, or building one from zero. Triage, bug bounties, Web3 security, or anything that helps secure a project or the wider org.
I'm also open to consulting. Helping teams spin-up an internal security function, or advising on what a project actually needs, especially on the internal side. I know how to run triage that's operationally efficient and doesn't miss the false negatives that matter.
If you're hiring or know someone who is, I'd like to hear from you.
My DMs are open
The @base Azul Audit Competition is live! ⚡️
A $250,000 scaling reward pool is up for grabs for finding bugs in the Base Azul, Base's first independent upgrade.
📅 Ends May 4, 2026
💰 Scaling reward pool of $250,000
⌨️ Language: Solidity & Rust
✅ KYC required
Get hunting: https://t.co/CxVYnD8Twr