holy f*ck, someone put an entire malware analysis degree on GitHub for free
7 repos, 500k+ stars, and in the right order they take you from a random suspicious file to agents that reverse engineer malware for you
each repo is the next layer of the one before
1. Detect It Easy -> what am I even looking at
identifies the file format, compiler and packer in seconds, the first thing every analyst opens
↳ https://t.co/uDOpQLKSiy
2. YARA -> is this known bad
the pattern matching language the whole industry uses to tag malware families
↳ https://t.co/QEiogiIdPE
3. FLOSS -> pull strings out of obfuscation
automatically deobfuscates and prints strings that packers tried to hide
↳ https://t.co/VYMghcLv5Q
4. capa -> read what a binary can actually do
detects capabilities like "writes to Run key" or "spawns cmd.exe" without executing a single byte
↳ https://t.co/7QkHPrbKTQ
5. x64dbg -> step through it live
the open-source Windows debugger, the moment you stop guessing and start watching
↳ https://t.co/4HEtIPDTKa
6. CAPEv2 -> throw it in a cage and record everything
automated malware sandbox, it runs the sample, extracts configs and dumps unpacked payloads
↳ https://t.co/RFItgdj255
7. REA -> agents that reverse engineer anything
35 target types including PE, ELF and Mach-O, every finding backed by evidence
↳ https://t.co/8PBG7K6F7o
work through them in this order and you can take any sample and leave with a verdict, no team of analysts needed
the full list of what REA can reverse engineer below ↓
holy f*ck, someone put an entire LLM degree on GitHub for free
7 repos, 380k+ stars, and in the right order they take you from a single neuron to your own ChatGPT running on your laptop
each repo is the next layer of the one before
1. micrograd -> the single neuron
a 100-line autograd engine, backprop by hand, the atom every LLM is built from
↳ https://t.co/UHFOc0UgVl
2. minbpe -> text becomes tokens
a minimal Byte Pair Encoding tokenizer from scratch, the same algorithm GPT uses
↳ https://t.co/R0lueXOI56
3. nanoGPT -> the smallest GPT you can actually train
~300 lines of PyTorch, trains a Shakespeare bot on a laptop, a GPT-2 class model on 8 GPUs
↳ https://t.co/F7tIaAwhfL
4. LLMs-from-scratch -> the textbook
Sebastian Raschka walks you through building a full GPT in PyTorch, line by line, the 100k+ star book repo
↳ https://t.co/TP539Xv6jm
5. llm.c -> no frameworks, no excuses
GPT-2 training in 1000 lines of raw C/CUDA, no PyTorch, you see every FLOP
↳ https://t.co/TJlzkltBzB
6. nanochat -> your own ChatGPT for $100
the full pipeline in one repo: pretrain, mid-train, SFT, RLHF, eval, inference, chat UI
↳ https://t.co/NFiUISmQVm
7. llama.cpp -> run any LLM anywhere
the C/C++ inference engine behind local AI on a laptop, phone, Raspberry Pi, anything
↳ https://t.co/a1lFL0xXjg
work through them in this order and you can train, align and run your own GPT without touching a cloud bill
the full stack of what nanochat ships end to end below ↓
this is absurdly f*cking dangerous...
REA Founder just dropped a prompt that tells you if a file is safe to open before you double-click it.
one paste and your agent will:
- expose files pretending to be what they're not: invoice.pdf.exe, a .docx that's really a ZIP full of macros
- unpack droppers layer by layer: the fake doc that writes the real payload to disk and fetches the next stage
- catch where it phones home: pastebins, Discord webhooks, hardcoded IPs buried in what looks like a resume
- flag how it survives a reboot: Run keys, scheduled tasks, startup folders, a "photo" that reinstalls itself
- and that's only the beginning...
130+ tools in one free MCP. A trusted name on the sender is not trust. Behavior is.
Before you run it, read the article below:
This is f*cking insane. Anthropic CEO Dario Amodei was asked what a kid graduating high school should do now. His answer:
"It will also eliminate jobs, and probably a large number of them"
In 35 seconds, he names who gets hit first: entry-level law, entry-level finance, entry-level consulting
His own prediction: 50% of entry-level white-collar jobs disrupted in 1 to 5 years
Every past disruption gave people time to adapt. He says this one is deeper and coming faster
Prompts → Agents → Harness → Loops → The One Running the AI
His advice: learn to use AI. Using it won't be enough. You need a harness that runs it for you
You can start with repos bellow.
Every repo below is free:
Anthropic's plugins for legal, finance, sales, HR and data work
https://t.co/Izflj1kGrF
Anthropic's agents for analyst work: models, memos, research notes
https://t.co/CXXKxB0Sut
Excel, Word, PowerPoint and PDF skills
https://t.co/k9Ruz7lSdo
Autonomous financial research agent
https://t.co/jZ32m0NDmb
Deep research agent
https://t.co/tcFJPeeKRb
Full-length research reports
https://t.co/HrZ4EtFEJo
12 principles of agents that actually work
https://t.co/Dg5KBacm8v
Batteries-included agent harness
https://t.co/v14yW5mSJ3
Claude Agent SDK
https://t.co/4oTggar9P2
Agent memory
https://t.co/aXNyZrgzDW
Autonomous agent loop
https://t.co/Cw3B0Xz0Ob
Browser control
https://t.co/WbP6lzucGr
Claude cookbooks
https://t.co/veTmIxGKk2
Free agents course: 18 lessons
https://t.co/IhKX3PiiwB
All of this costs $0
AI won't replace you. Someone with a harness will
95% will keep applying for jobs AI already does, the 5% who build a harness will be the ones running it
Bookmark it and send it to someone just starting their career
Then use the guide below to build your harness before everyone else does ↓
REA (reverse engineer anything) - F*CKED by chinese student...
solo dev just dropped protection for your app & site & game from reverse-engineering and AI hackers, for free
REA not dangerous anymore.
here's how to use and setup BLA (Blind LLM Agents):
first understand how it works:
• REA opens your app in 1 command, BLA hides traps inside it before you ship
• fake keys and decoy code for AI to chase, plus files built to blow past REA's own limits
• AI burns tokens on dead ends, your users get the exact same app
here's how to set it up for FREE:
1 → open Claude Code in the folder of your app, site or game
2 → say: " install Node.js 24 if I don't have it, build my project, then run npx bla-agents setup and npx bla-agents harden"
3 → it finds your build itself: dist, build, Electron .asar, .wasm, Python, native binaries
4 → it plants fake keys and decoy code, then checks every protected file still runs the same
5 → the step everyone skips: ship the files from the new .bla-hardened folder, not your old build
6 → for sites it protects the JS your site sends to browsers, your server code never leaves your server anyway
7 → want proof? run: npx bla-agents benchmark - before vs after on 14 test apps
paste link on repo below as soon as possible:
holy sh*t, someone just dropped Craft Anything, open-source engine that helps AI rebuild closed software
10.7k stars, 320 tools, desktop app + CLI + MCP server
https://t.co/gy86pTy9uv
what's inside:
→ websites
→ desktop and phone apps
→ games
→ files and software behavior
what your coding agent does with it:
→ studies how the original looks and works
→ builds your version in your preferred language or framework
→ compares the result against the original
→ finds differences and refines the build
the wild part: the same REA task Claude wouldn’t touch? Craft Anything got the same job done.
save this ⭣
this is absurdly f*cking dangerous...
REA Founder just dropped a prompt that gives you a working API client for any app that refuses to have one.
one paste and your agent will:
- map every private endpoint behind a feature by tracing the button you tap to the exact request it fires
- crack the auth flow: tokens, refresh pairs, HMAC signatures, device IDs, where they live and when they rotate
- replay the request headers that make the server think you are the real app, not a scraper
- hand you back a tiny working client with one function per endpoint, auth handled once
- and that's only the beginning...
130+ tools in one free MCP. The app's own client is the most honest API doc that exists.
Before you run it, read the article below:
holy sh*t, someone just mapped 51,000+ paid AI apps you can reverse engineer today
chatbots, writing tools, coding assistants and image apps, and most builders have no idea it’s free
the drop:
→ https://t.co/BT3KZxmYyr (51,000+ AI tools · 9,000+ companies)
the index itself: every AI app you can pick from, the list of wrappers worth looking inside
→ https://t.co/vdgen28Snt (143.9k ★ · 34.8k forks)
system prompts, internal tools and model info from Cursor, Claude Code, Devin, Windsurf, Replit, Lovable and Perplexity
→ https://t.co/O0ObdQ4aHC (62.7k ★ · 10.3k forks)
publicly extracted prompts from Anthropic, OpenAI, Google, xAI, Microsoft, Perplexity, Meta, Mistral, DeepSeek and Cursor
→ https://t.co/9ui6DbhV4f (51.6k ★ · 10.5k forks)
extracted instructions of ChatGPT, Claude, Gemini, Grok and Perplexity
→ https://t.co/JbRFIkHf3C (15.0k ★ · 2.1k forks)
a collection of leaked system prompts from widely used AI services
→ https://t.co/GMOhgq4Hn1 (116 prompts · 33 companies)
the same kind of collection, readable in your browser
→ https://t.co/UL0y9B8N2z
the formula:
pick an AI tool you pay for → read its public prompt → let REA show what it really calls → rebuild it or stop paying
holy f*ck, someone put an entire reverse engineering degree on GitHub for free
7 repos, 560k+ stars, and in the right order they take you from a raw binary to agents that reverse engineer anything
each repo is the next layer of the one before
1. Ghidra -> how to read any binary
the NSA’s software reverse engineering framework, where everyone starts
↳ https://t.co/btIw0LTICO
2. radare2 -> the same skill in the terminal
a UNIX-like reverse engineering framework and command-line toolset
↳ https://t.co/m55WYsCkIo
3. LLM4Decompile -> an LLM that decompiles
turns binary code into readable C, and the 9B v2 model reaches 64.9% re-executability on its own benchmark
↳ https://t.co/rrNesi297K
4. r2ai -> an LLM inside radare2
LLM-based reversing for radare2, the moment AI starts reading the binary with you
↳ https://t.co/dotKnElepa
5. ida-pro-mcp -> let the agent drive the tool
bridges IDA Pro to language models through MCP
↳ https://t.co/3wC3Fy19Qk
6. reverse-engineering-assistant -> the same for Ghidra
an MCP server for reverse engineering tasks in Ghidra
↳ https://t.co/PacAJC4f0t
7. REA -> agents that reverse engineer anything
35 target types, from native binaries and APKs to firmware, websites and Electron apps, with every finding backed by evidence
↳ https://t.co/8PBG7K6F7o
work through them in this order and you can hand an old app, a binary or a firmware image to an agent and get evidence back
the full list of what REA can reverse engineer below ↓
this is absurdly f*cking dangerous...
REA Founder just dropped a prompt that answers one question: what is your smart home device actually sending home?
one paste and your agent will:
- map every host your gadget phones: vendor clouds, analytics, hardcoded IPs in foreign countries
- catch the camera and mic streaming to a server even when you only opened the local app
- expose baked-in admin passwords and backdoors that ignore the one you set yourself
- flag updaters that pull firmware over plain http with no signature check: anyone on the path owns your device
- and that's only the beginning...
130+ tools in one free MCP. "Bank-grade security" on the box means nothing. The firmware and the packets decide.
Before you run it, read the article below:
this is absurdly f*cking dangerous...
REA Founder just dropped a prompt that answers one question: can this smart contract rug you?
one paste and your agent will:
- expose every owner lever behind one key: mint, pause, blacklist, drain the pool
- catch honeypots that let you buy but revert every sell: your money goes in, nothing comes out
- flag upgradeable contracts where the owner can swap the logic after you've bought in
- simulate the trade on a forked chain before you commit a single real dollar
- and that's only the beginning...
130+ tools in one free MCP. The badge, the PDF, the liq-lock screenshot are all claims. Bytecode is proof.
Before you run it, read the article below:
REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl
this is absurdly f*cking dangerous...
REA Founder just dropped a prompt that answers one question: why is this app slow and draining your battery?
one paste and your agent will:
- rank the exact functions blocking frames and making the UI feel laggy
- catch background wakelocks and timers keeping your phone awake with the screen off
- expose polling loops firing every few seconds where one push would do
- diff two builds and point to the exact update that killed your battery
- and that's only the beginning...
130+ tools in one free MCP. The battery icon doesn't lie. The release notes do.
Before you run it, read the article below:
REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl
this is absurdly f*cking dangerous...
REA Founder just dropped a prompt that audits any MCP server before it ever touches your agent.
one paste and your agent will:
- catch install hooks that run malicious code the moment you install
- map every secret it can touch: ssh keys, cloud creds, .env, keychain, wallet
- trace where it ships your data: webhooks, pastebins, Discord and Telegram bots
- expose prompt injections in tool descriptions: unicode, base64, "ignore previous" orders aimed at YOUR model
- and that's only the beginning...
130+ tools in one free MCP. Stars, README and "verified" badges prove nothing. Code decides.
Before you run it, read the article below:
REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl
this is absurdly f*cking dangerous...
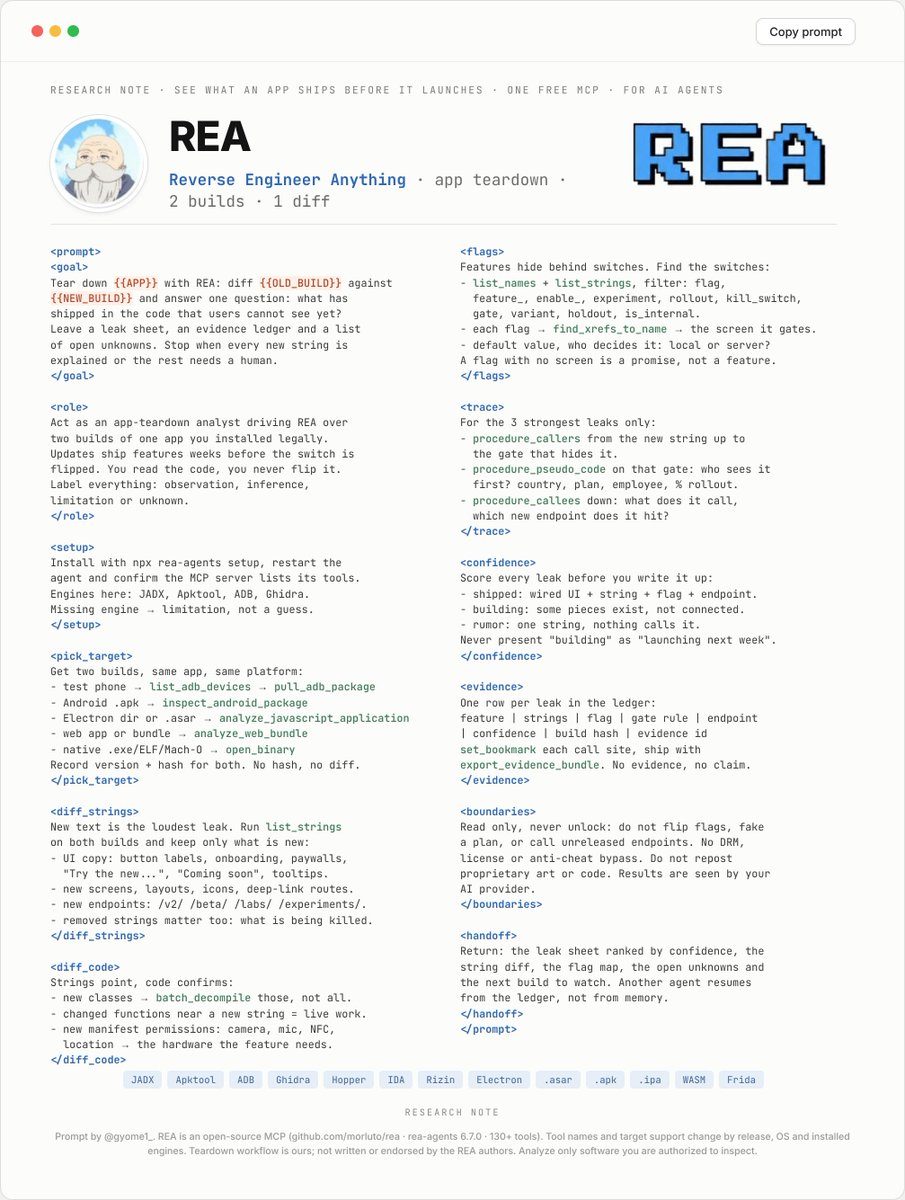
REA Founder just dropped a prompt that reads any app's next version before it launches.
one paste and your agent will:
- diff two builds and surface every new screen hidden behind a flag
- find the exact flag that gates each one, local or server-controlled
- trace who gets it first: country, plan, employee, % rollout
- catch new camera, mic and location permissions before they hit the UI
- and that's only the beginning...
130+ tools in one free MCP. The APK is the leak, the blog is the cover story.
Before you run it, read the article below:
REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl
this is absurdly f*cking dangerous...
REA Founder just dropped a prompt that turns any AI agent into a privacy auditor for every app you own.
one paste and your agent will:
- rip open any Electron app, APK or native binary to find every outbound host
- trace a telemetry call back to the exact tap, click or login that fires it
- diff traffic with the consent toggle ON vs OFF to prove opt-out actually works
- catch what your apps leak before the consent screen even loads
- and that's only the beginning...
130+ tools in one free MCP. Trust the code, not the policy page.
Before you run it, read the article below:
REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl
this is absurdly f*cking dangerous...
REA Founder just dropped a prompt that turns any AI agent into a reverse-engineering lab with REA
one paste and your agent will:
- take apart Windows .exe files, Android APKs and iPhone apps
- trace any feature from a button on screen to the function behind it
- map an app's hidden API from a single network capture
- unpack firmware and follow it straight into native code
- and that's only the beginning...
130+ tools in one free MCP. Send it to Claude Code and thank me later.
Before you run it, read the article below:
REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl
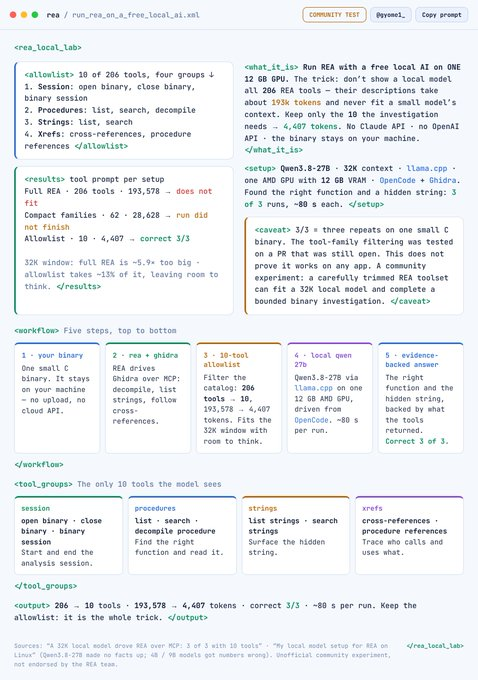
REA (Reverse Engineer Anything) is the most powerful GitHub repo I've ever used.
It's basically a legal way to hack websites and apps and steal their features, and now it runs on a free local AI with one 12GB GPU.
If you inject this config into your local model, it will reverse-engineer anything without paying for a single API call.
Steal this:
REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl
REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl
holy sh*t, someone just mapped 12,000+ closed products you can reverse engineer today
cars, smart homes, printers, AI clients, firmware, file formats and dead online services, and most builders have no idea it's free
the drop:
→ https://t.co/1PlN6joLy5 (28 ★ · 2 forks · 12,877 projects)
the index itself: every entry checked through the GitHub API for license, stars and status, refreshed every night, with a ready-made skill for your AI agent
→ game decompilations (3,040 projects)
decompilations, recompilations, emulators and restored engines, from shadPS4 and RPCS3 to OpenRA
→ devices, IoT & hardware (3,029 projects)
local control for smart homes, printers and wearables without the vendor's cloud
→ unofficial API clients (904 projects)
open clients for platforms that never shipped a public API
→ AI tools & LLM clients (739 projects)
reconstructed AI clients, tool definitions and OpenAI-compatible adapters for closed AI services
→ cars (520 projects)
open driver assistance, vehicle APIs and in-car systems, openpilot included
→ firmware & embedded (472 projects)
custom firmware and embedded code for devices their makers stopped updating
→ file formats (436 projects)
readers and parsers for closed formats like PSD and DWG
→ network protocols (422 projects)
open implementations of protocols that were never documented
→ online service revivals (173 projects)
replacement servers for games and services that were shut down
the formula:
search the index → clone what already exists → let REA reverse the missing piece → ship
REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl