Improper access Control can be P1 Critical
Bypass 403 /wp-admin adding in your wordlists /wp-admin/setup-config.php?step=1
It allows an attacker can create a new database.
#bugbounty#bugbountytips
Bug Bounty Tip
You can use this payload
for finding XSS & SQLi
qwe'"<x</
🔸 qwe - easy to type & find in HTML
🔸 '" - JS/HTML breakout & SQLi
🔸 <x - HTML injection test
🔸 </ - <script> breakout
extra for SSTI/CSTI
{{[7*7]}}${7*7}qwe'"<x</
Cheers!
If you want to find third parties domains for your target.
Go to @securitytrails and on the search write your keyword.
Example your target is indeed .com
Just write indeed and hit search,
Copy all results ,sort it and scan it to find vulnerabilities.
Good luck.
#bugbountytip
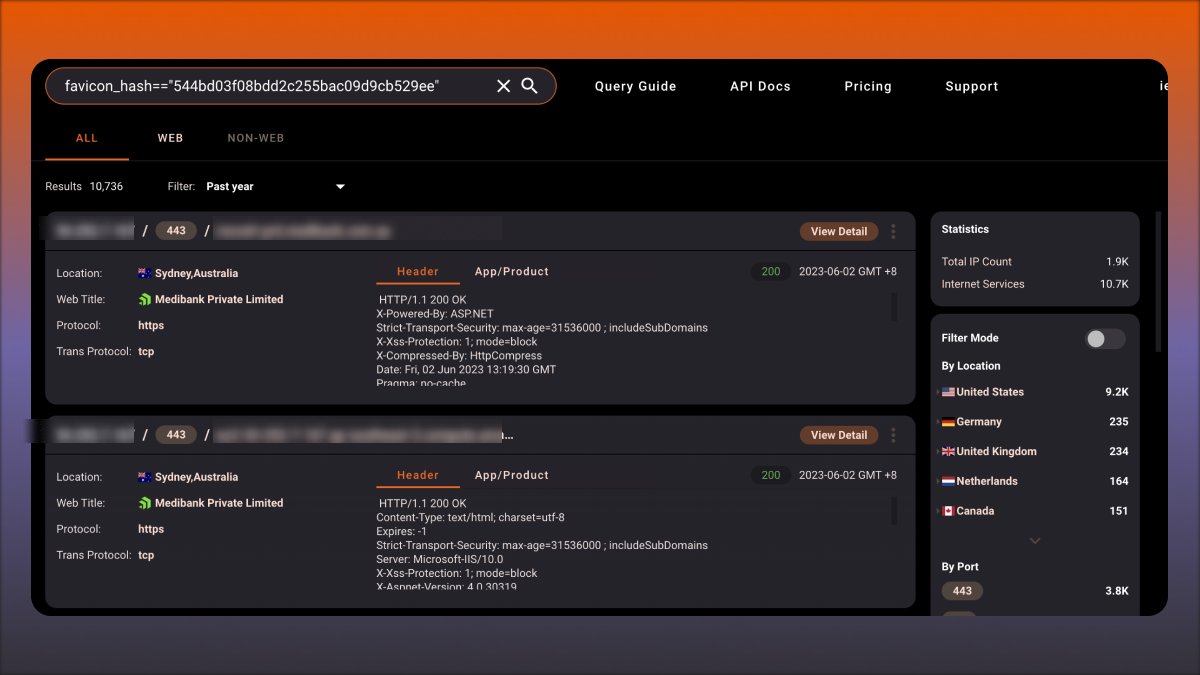
⚠️Warning CVE-2023-34362 #MOVEIt Transfer #0day-day vulnerability. ⚠️
Take immediate action as noted here https://t.co/pGAlO0Gd1q
Search Link 💡:https://t.co/WYNVBTCzzn
Dorks on other platforms:
1⃣Shodan: http.favicon.hash:989289239
2⃣FOFA: icon_hash="989289239"
The 30 burp suite extensions every hacker should know about:
SQLiPy SQL Injection Scanner: Injects SQL payloads into all parameters and looks for evidence of an SQL injection.
J2EEScan: Useful for testing J2EE applications. It extends Burp's scanning capabilities to identify J2EE vulnerabilities.
Burp Bounty (Scan Check Builder): It improves the active and passive scanner capabilities by allowing you to customize payloads and scan checks.
Autorize: Automatically detects authorization enforcement by tagging requests and responses.
Logger++: Logs requests and responses for all Burp tools in a sortable table.
JSON Decoder: Beautifies and simplifies complex JSON responses.
Wsdler: Parses WSDL files for web service testing.
EsPReSSO: Enhances handling of client-side stored data like cookies and HTML5 local storage.
Retire.js: Identifies JavaScript libraries with known vulnerabilities.
Backslash Powered Scanner: Actively scans for parameter-based vulnerabilities.
Software Vulnerability Scanner: Integrates with Burp to identify software that is outdated and potentially vulnerable.
BurpHash: Helps to decrypt hash values or make a comparison between two or more hash values quickly.
Paramalyzer: Helps in the identification of hidden, unlinked parameters.
HUNT Methodology Scanner: Allows for easier identification of common parameters vulnerable to certain vulnerability classes (SQLi, XSS, command injection, etc.)
Turbo Intruder: Allows you to perform high speed, reliable HTTP requests.
Upload Scanner: Scans file uploads to find client-side and server-side vulnerabilities.
Brida: Integrates Burp Suite with the Frida Tool, useful for mobile app testing.
J2EEScan: Improves the test coverage of J2EE applications.
Request Timer: Measures the time taken for HTTP responses.
Reflected Parameters: Monitors and logs all reflected parameters within the HTTP response.
CO2: A collection of various tools including Payload encoding/decoding, SQL helpers, and command shortcuts.
Collaborator Everywhere: Injects Burp Collaborator payloads into almost every parameter.
Flow: Provides a sortable and filterable view of all Burp Suite tools' HTTP traffic.
CSRF Scanner: Scans for potential CSRF vulnerabilities.
InQL (Introspection GraphQL): A Burp Suite extension for handling GraphQL.
Content Type Converter: Converts JSON to XML, XML to JSON, etc., for ease of viewing.
Reissue Request Scripter: A tool for scripting the reissue of requests.
HTML5 Auditor: Audits HTML5 web storage data, useful for checking local and session storage.
Same Origin Policy Bypass: Helps find SOP bypasses.
Shellshock Scanner: Actively scans for the shellshock vulnerability.
If you found an injection point but can't get an XSS because a WAF is blocking you
Leverage loaded technologies to still execute XSS:
BLOCKED: "><a href=javascript:alert(1)>accept</a>
ALLOWED: xyz"/ng-click="constructor.constructor('alert(1)')()
#bugbounty#bugbountytip