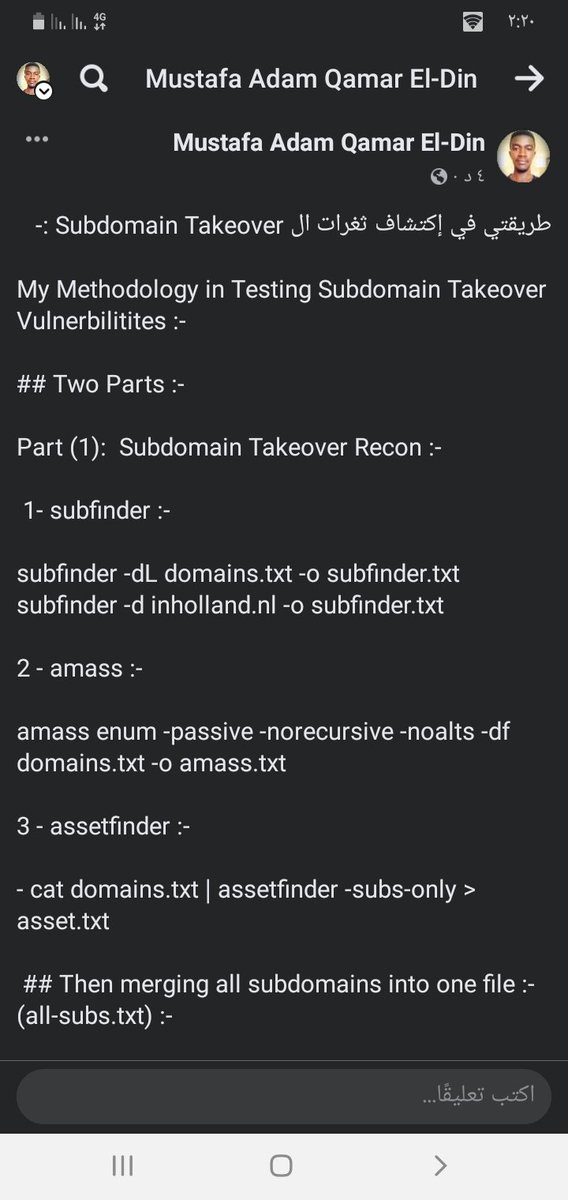
My Methodology in Testing for Subdomain Takeover Vulnerabilities
## Useful Writeups and Disclosured Reports in the first comment (:
#bugbountytips#cybersecurity#security
Do you want to attend a live class on API hacking? Can you bare going to London for a day 😉? Do you want insiderphd swag? Check out this free workshop with @LHS_LON
كرر هذا الدعاء عظيم جدا
" اللهُم إني أشهِدُك بأني قد رضيتُ بكل ما أردتَه من، عطاء وحِرمان، ومن جبرٍ، ومن كسرٍ، ومن فرح، ومن ألم، ومن نجاح ومن فشل، فأرضِنى بفرح وجبر من حيث لا احتسِب يا الله."
Tip - 1⃣0⃣
How can you find CRLF Injection in just 10 Mins.
1- Collect all subdomains with amass, subfinder, assetfinder, etc. & save it.
2- Run Nuclei on sub.txt
cat sub.txt | nuclei -tags cves,osint,tech
3- and BOOM 🎉
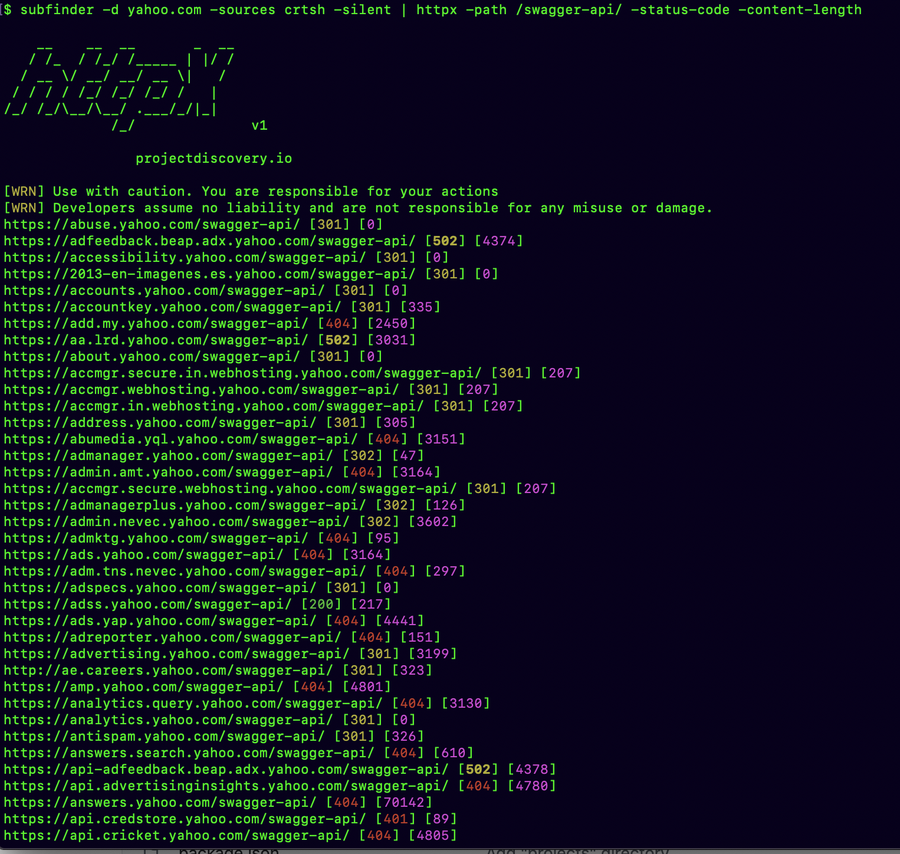
You can use #httpx to request any path and see the status code and other details on the go, filter, or matcher flags if you want to be more specific.
httpx -path /swagger-api/ -status-code -content-length
credit:@pdnuclei#hackwithautomation#recon#bugbountytips#infosec
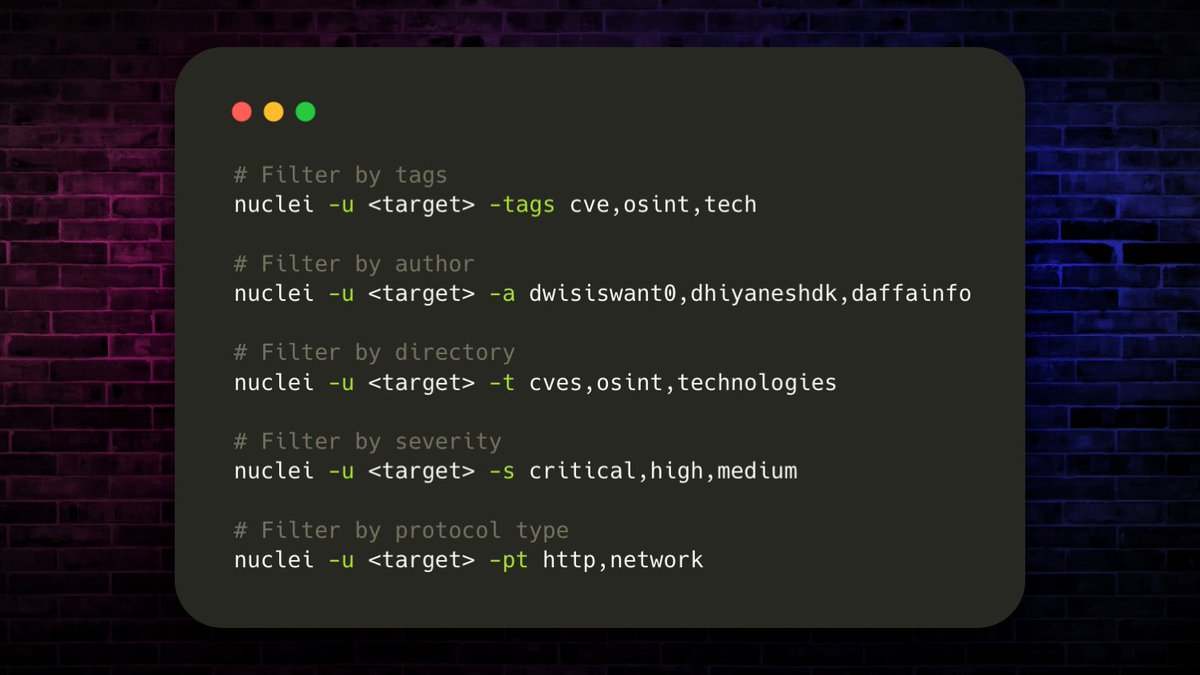
Improve your filtering game with this list of tags, authors, directories, severities and types!
Filter by:
⚛️ Tags: -tags
⚛️ Author: -a
⚛️ Severity: -s
⚛️ Type: -pt
⚛️ Template/Directory: -t
Bookmark this list:
👉🔗 https://t.co/bnVoqW363C #hackwithautomation#nuclei101
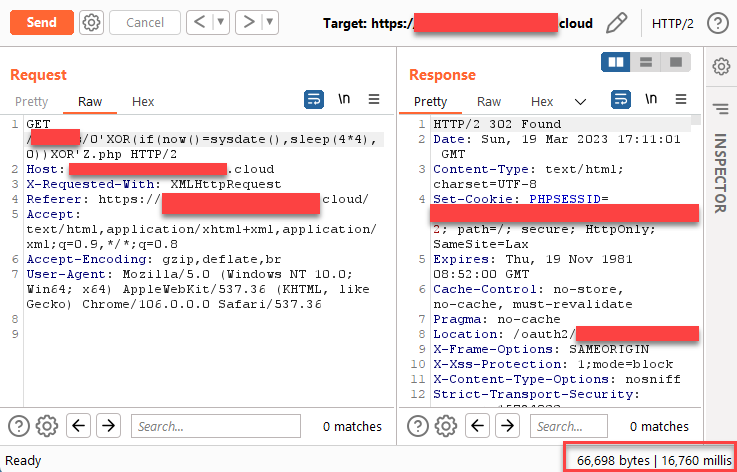
I was testing an app's #oauth2 today and randomly inject the payload "0'XOR(if(now()=sysdate(),sleep(6-2),0))XOR'Z", with php extension, and booom it was blind #SQLinjection...wt**, never knew SQLi payloads can be sent using .php. #BugBounty#bugbountytips
" This is how i got my first bounty "
1. Tools :
- Naabu, Httpx, Katana , Nuclei from @pdiscoveryio
- Waymore , xnLinkfinder from @xnl_h4ck3r
2. How to exploit :
- https://t.co/TcRpQVy55t
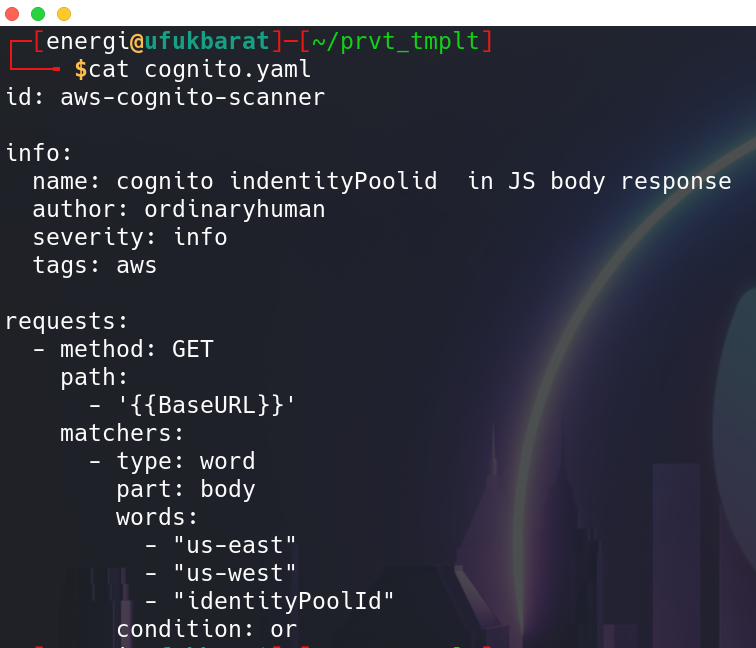
Nahamcon 2022 AWS Cognito